remove-ai-watermarks

Remove visible and invisible AI watermarks from images and video, and AI provenance metadata from images, video, and audio. Python library, CLI, and…

Remove visible and invisible AI watermarks from images and video, and AI provenance metadata from images, video, and audio. Python library, CLI, and…

Use to copy a file from an NTFS partitioned volume by reading the raw volume and parsing the NTFS structures.

GUI forensic tool for acquiring and analyzing Telegram data from Android devices. Parses messages, media, and metadata; generates integrity-verified…

Recovers lost partitions and repairs boot sectors; carves 480+ file formats from damaged disks and filesystems for data recovery and forensic use.

Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…

Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…

Extract files from any kind of container formats

Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…

📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…

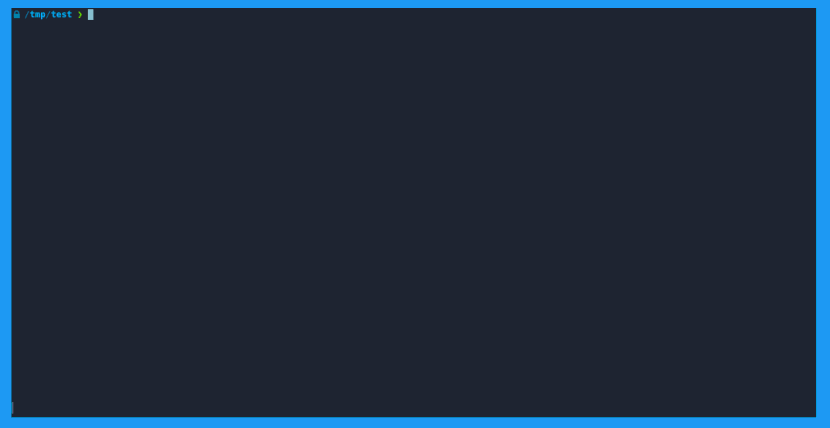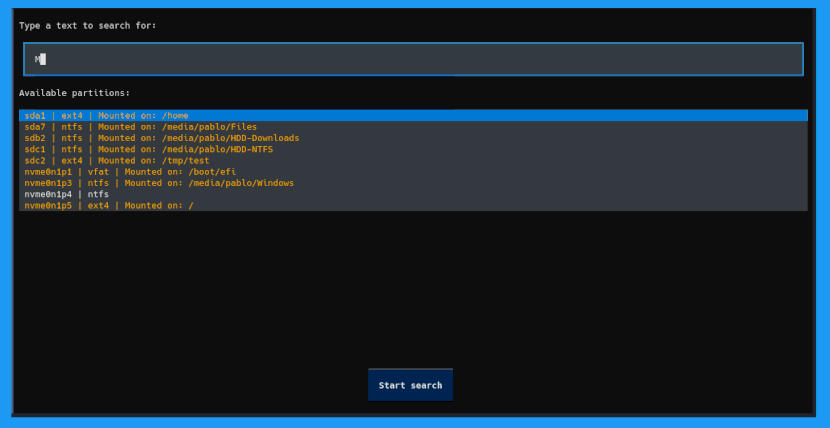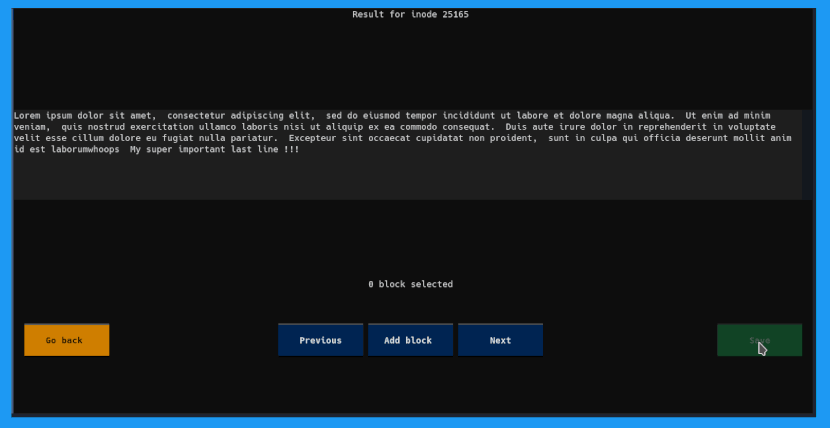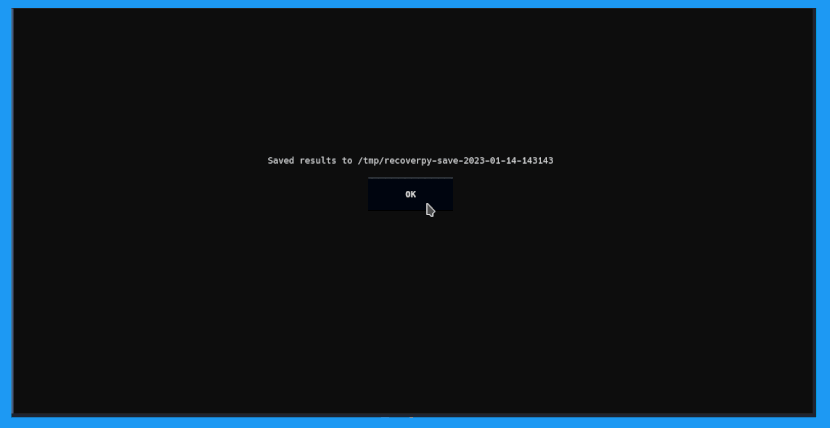
Interactively find and recover deleted or :point_right: overwritten :point_left: files from your terminal

File carving and indexing tool for digital forensics, recovering files from disk images based on header/footer pattern matching, regular expressions,…

Turn any collection of documents into a knowledge graph. Extract entities and relationships via LLM, deduplicate with your approval. Map domains,…

androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…

analyzeMFT.py is designed to fully parse the MFT file from an NTFS filesystem and present the results as accurately as possible in multiple formats.

File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…

'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files

Wipe, reinstall or restore your system from running GNU/Linux distribution. Via SSH, without rebooting.

Tool to extract the $UsnJrnl from an NTFS volume