

ImHex
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
ai-assisted-reversingbinary-analysisbinary-exploitation+10
55.7k22 days ago
werwolv/imhex🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 a-poc/blueteam-tools
Tools and Techniques for Blue Team / Incident Response

 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 simsong/bulk_extractor
This is the development tree. Production downloads are at:

 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 cristianzsh/forensictools
Collection of forensic tools
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
 0xpoly/centry
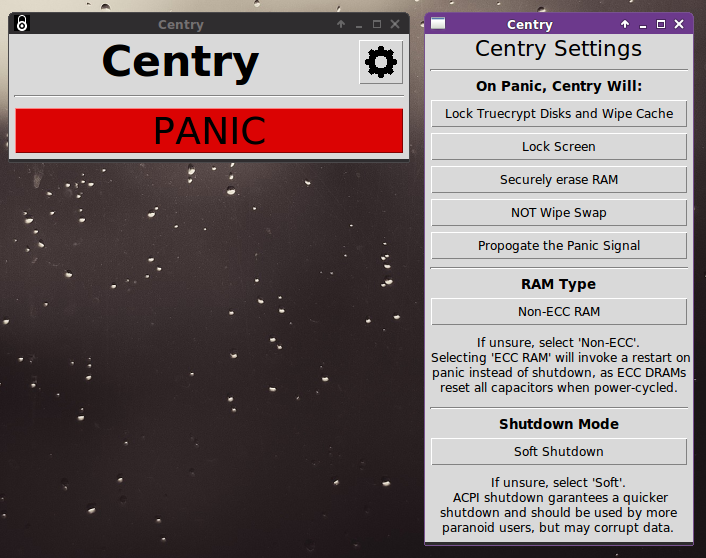
Panic button for protection against cold boot attacks
 packetlss/android-locdump
android location service cache dumper
 piat0n/baremetal-ram-dumper
A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
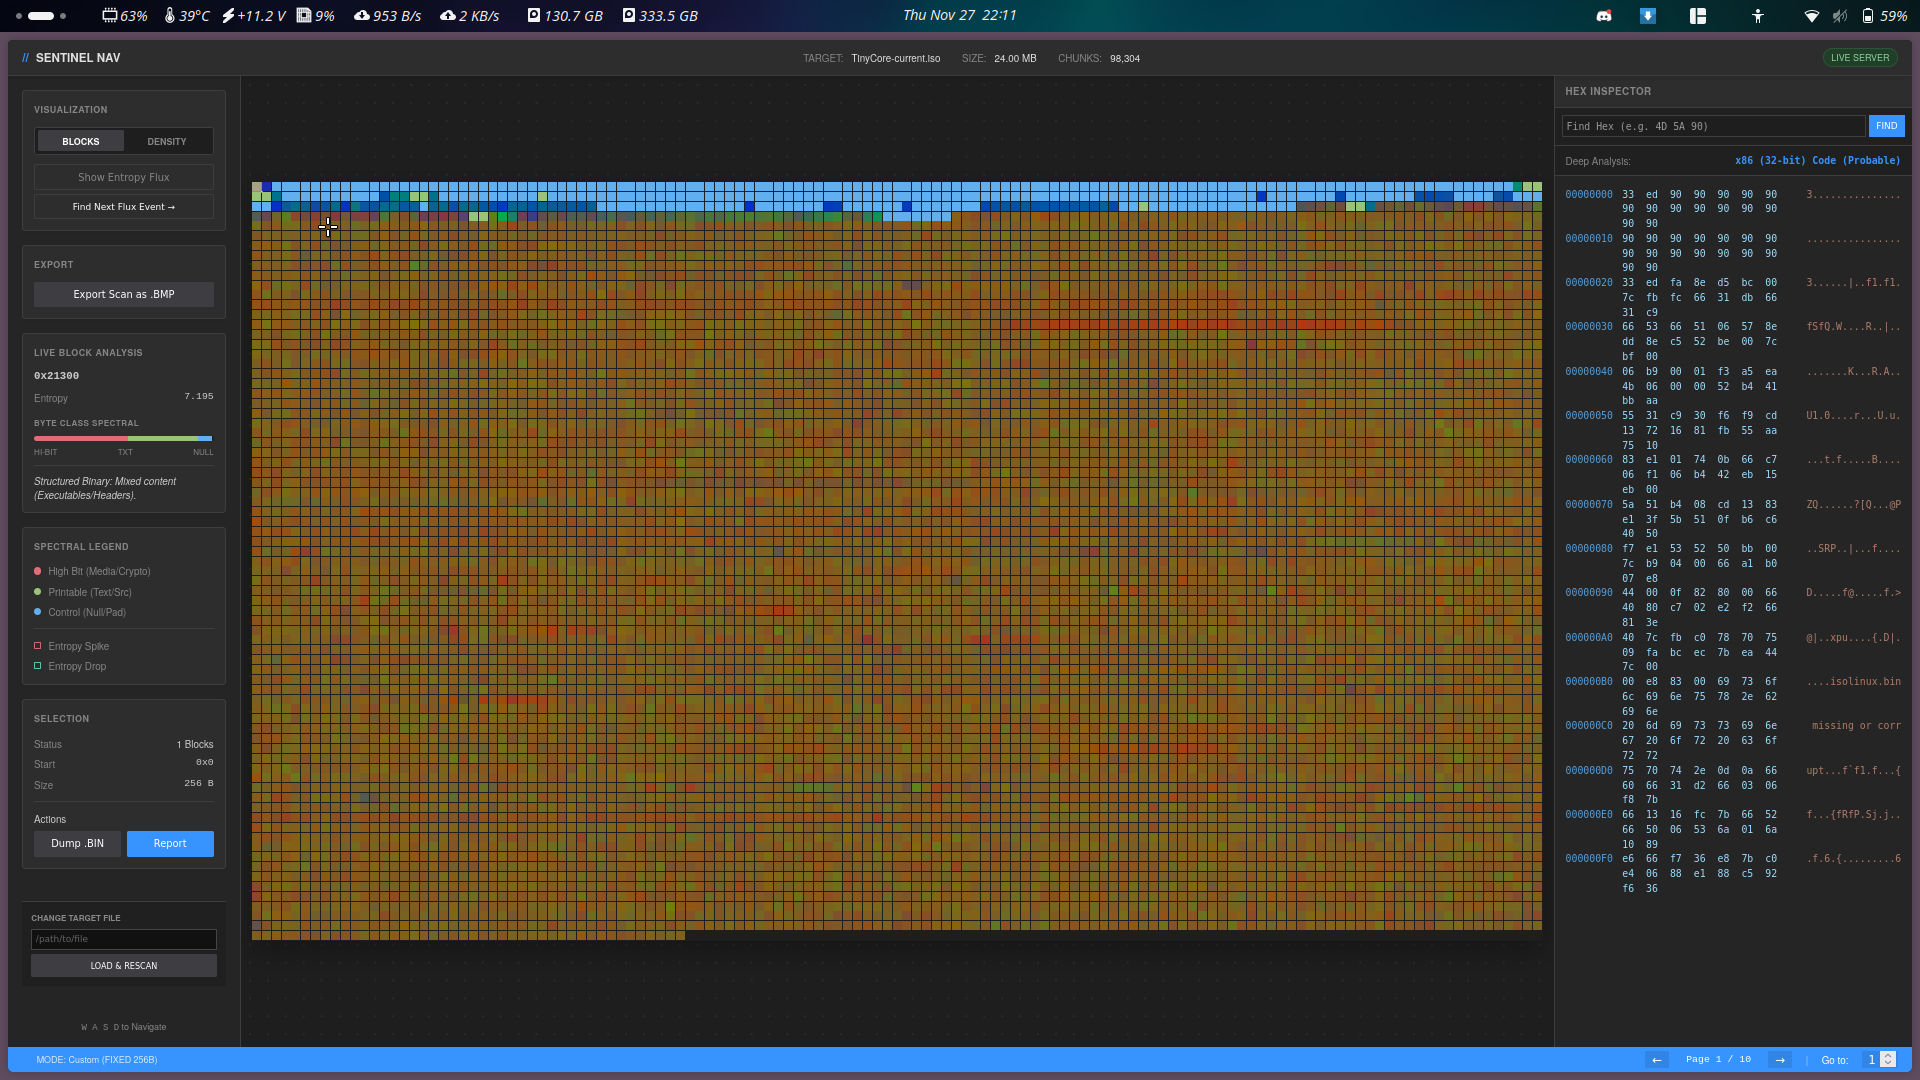 smolfiddle/sentinelnav
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.
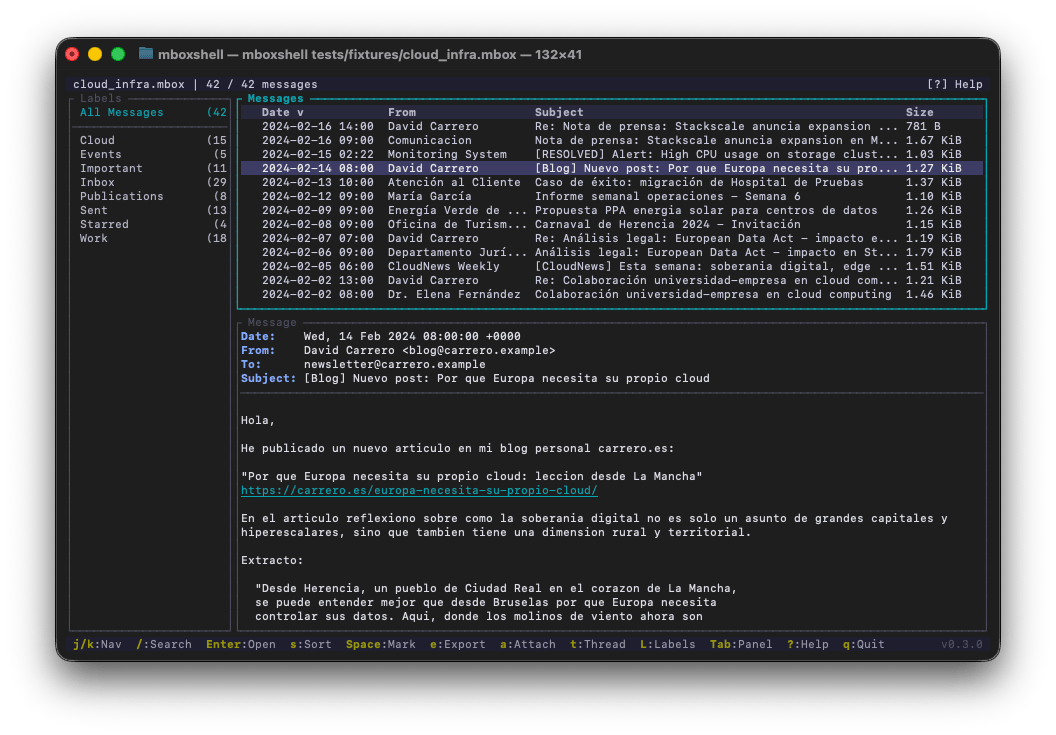 dcarrero/mboxshell
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 carmaa/interrogate
Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…