YellowKey-BitLocker-CVE-2026-45585

YellowKey BitLocker recovery audits CVE-2026-45585: yellowkey github, TPM, recovery key backup. Windows 10/11 CLI GUI, portable audit tool for…

YellowKey BitLocker recovery audits CVE-2026-45585: yellowkey github, TPM, recovery key backup. Windows 10/11 CLI GUI, portable audit tool for…

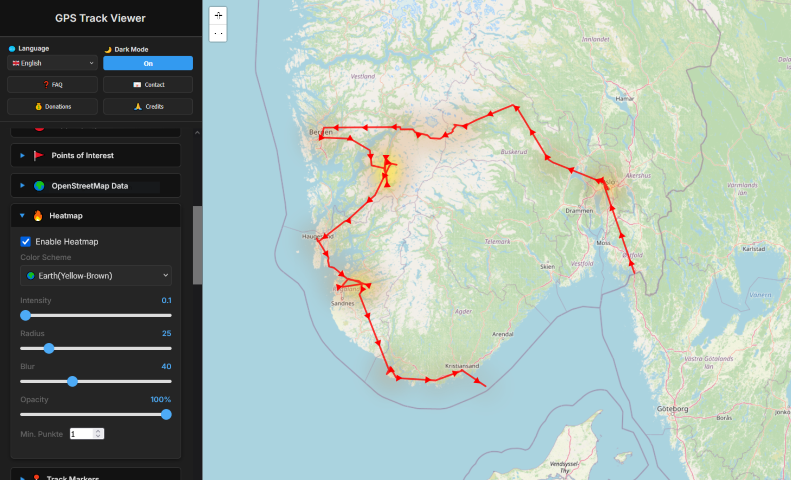
A powerful, privacy-focused, browser-based tool to visualize and analyze GPS data from your photos. Simply drag and drop images to generate…


Tools and Techniques for Blue Team / Incident Response

Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…

Turn any collection of documents into a knowledge graph. Extract entities and relationships via LLM, deduplicate with your approval. Map domains,…

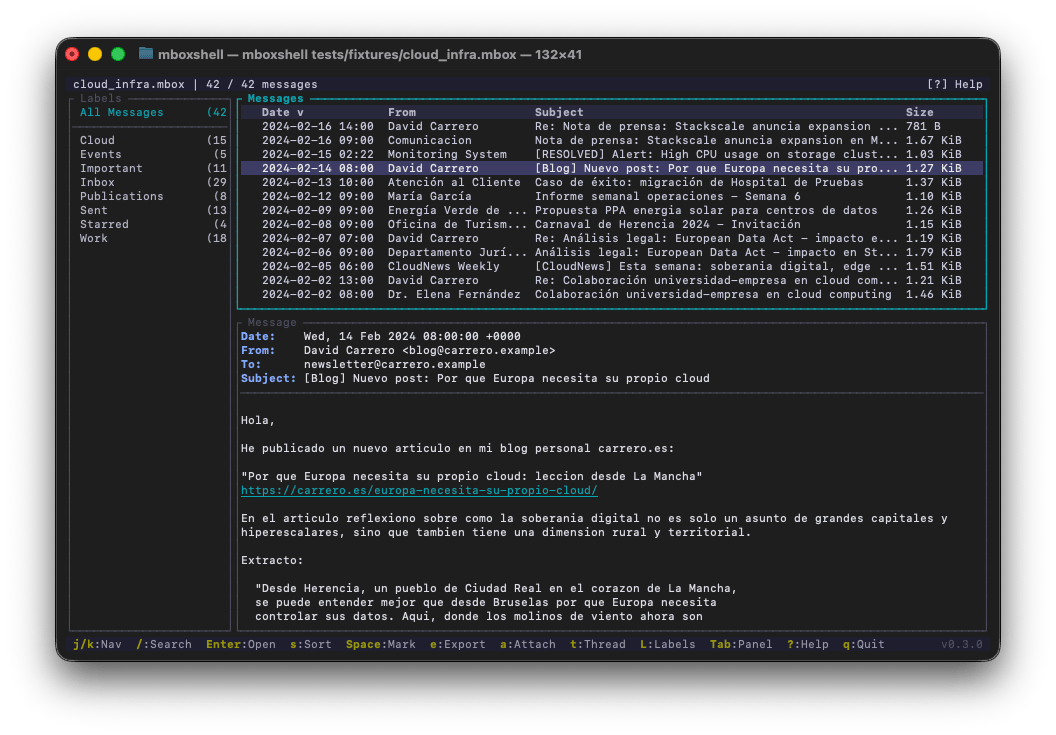
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…

An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.

Forensic Analysis for Mobile Apps (FAMA) -- module for the Autopsy Forensic Browser

android location service cache dumper

Acquires the EBS disks of an AWS AMI you can launch, streaming snapshots via EBS direct APIs to a private S3 bucket with sha256 manifests and…

Kvasir: Penetration Test Data Management

Search and extract blob files on the Ethereum Blockchain network

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.

This is the development tree. Production downloads are at:

A python tool that will extract exif data from picture with two methods