

androidqf
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
android-securitydata-recoverydigital-forensics+4
321
mvt-project/androidqfandroidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 gregwar/fatcat
FAT filesystems explore, extract, repair, and forensic tool
 iqbaalilmii/acropalypse-reconstructor
A lightweight CLI tool to detect and reconstruct cropped images vulnerable to Acropalypse (CVE-2023-21036 and CVE-2023-28303) written in Python.
 msedek/btrfs_fixes
Custom BTRFS repair tools for severe extent tree corruption where btrfs check --repair fails (segfault, loop, or deadlock)
 rowingdude/analyzemft
analyzeMFT.py is designed to fully parse the MFT file from an NTFS filesystem and present the results as accurately as possible in multiple formats.

 politoinc/xwfacropalypse
X-Ways Acropalypse extension detects CVE-2023-21036 in common images
 reecdeep/hivev5_file_decryptor
Hive v5 file decryption algorithm
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
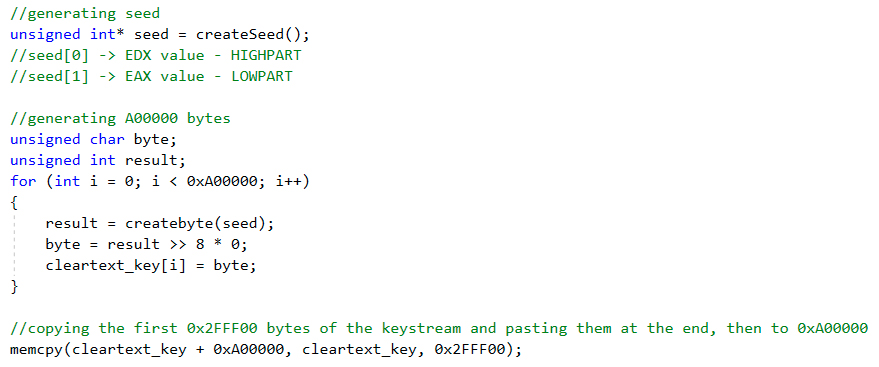 reecdeep/hivev5_keystream_decryptor
bad stuffs by bad guys
 fran314/secrets-manager-rs
A command-line tool for securely backing up, restoring, and verifying secrets using interoperable standards like age encryption and coreutils,…

 notaswe/gocropalypse
CVE-2023-21036 detection in Go
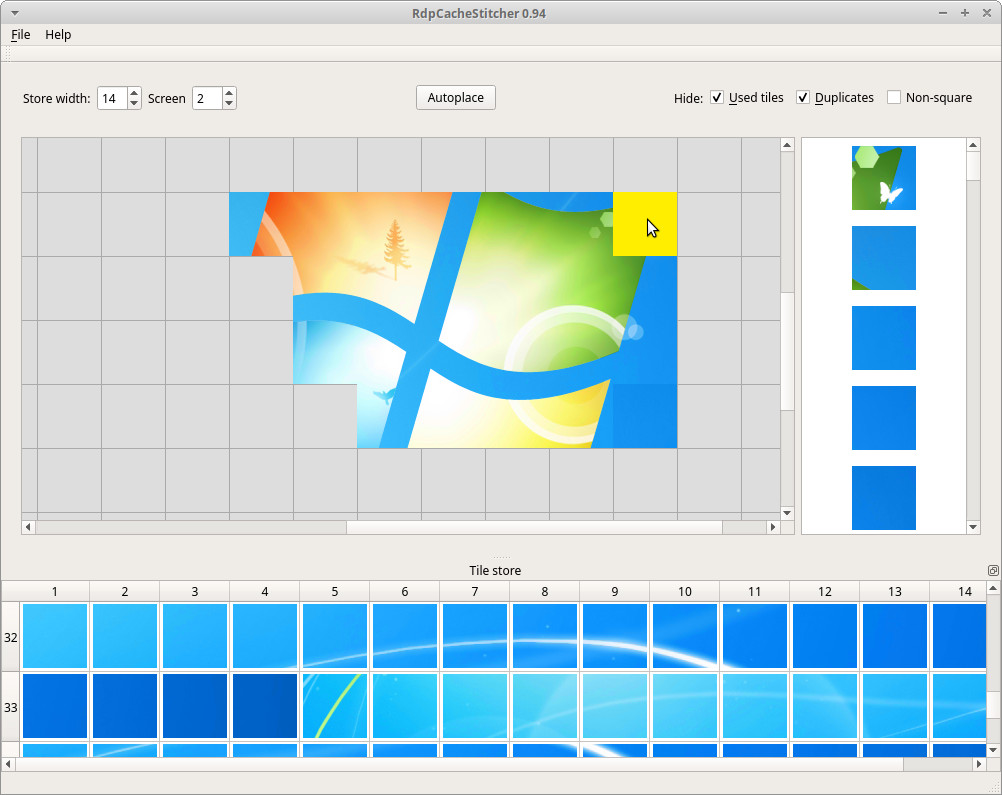 bsi-bund/rdpcachestitcher
RdpCacheStitcher is a tool that supports forensic analysts in reconstructing useful images out of RDP cache bitmaps.
 quantika14/guasap-whatsapp-foresincs-tool
WhatsApp Forensic Tool
 landw-hub/cve-2025-50422
Proof-of-concept for CVE-2025-50422: demonstrates heap memory disclosure in Poppler's pdftocairo, allowing local attackers to recover clear-text PDF…
 carmaa/interrogate
Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…