
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
35 results
pcapfex preview

pcapfex

GitHubvikwin/pcapfex

'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
data-recoverydigital-forensicsforensics+2
2306 years ago
BlueTeam-Tools preview

BlueTeam-Tools

GitHuba-poc/blueteam-tools

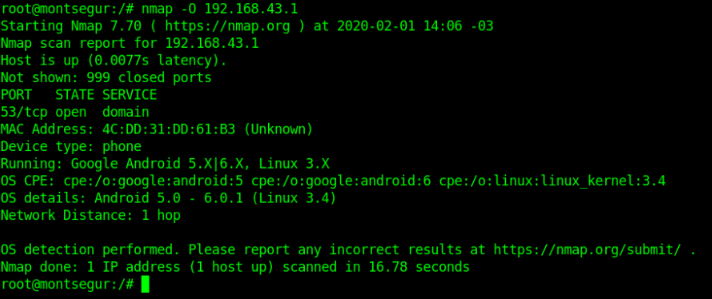
Tools and Techniques for Blue Team / Incident Response
curated-resourcesdata-recoverydefensive-tools+8
4.5k2 months ago
etherblob-explorer preview

etherblob-explorer

GitHublitneet64/etherblob-explorer

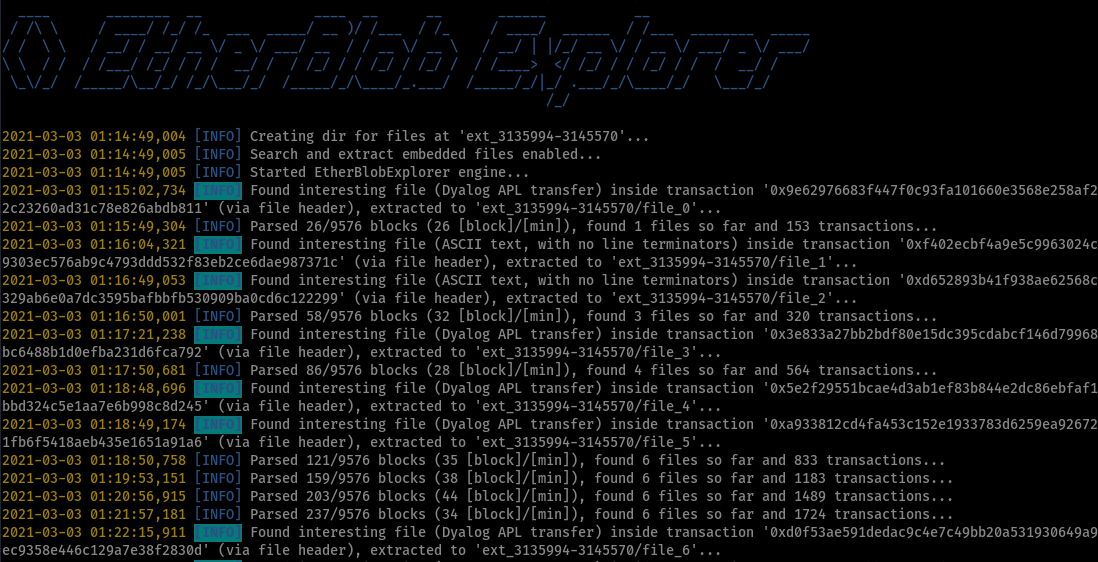
Search and extract blob files on the Ethereum Blockchain network
ctfdata-recoveryforensics+2
435 years ago
LocalExifGeoMap preview

LocalExifGeoMap

GitHublukawe/localexifgeomap

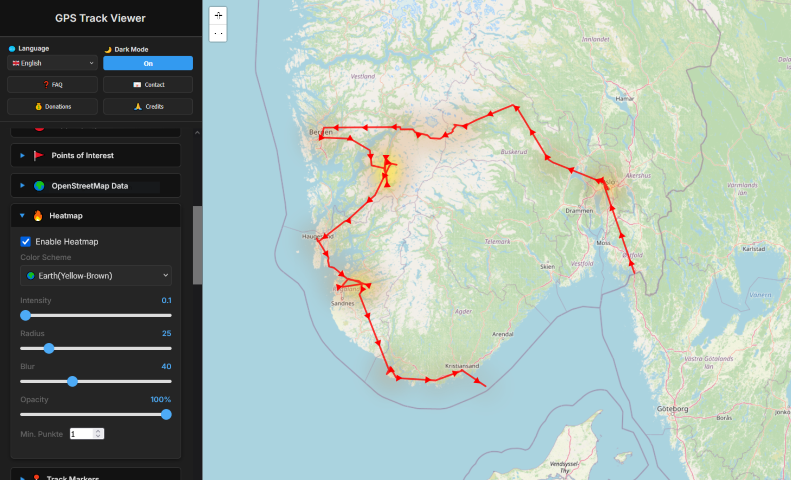
A powerful, privacy-focused, browser-based tool to visualize and analyze GPS data from your photos. Simply drag and drop images to generate…

data-recoveryforensicsgeneral-purpose-utilities+3
18 months ago
forensictools preview

forensictools

GitHubcristianzsh/forensictools

Collection of forensic tools

binary-analysisdata-recoverydigital-forensics+7
7072 months ago
ImHex preview

ImHex

GitHubwerwolv/imhex

🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
ai-assisted-reversingbinary-analysisbinary-exploitation+10
55.6k18 days ago
SentinelNav preview

SentinelNav

GitHubsmolfiddle/sentinelnav

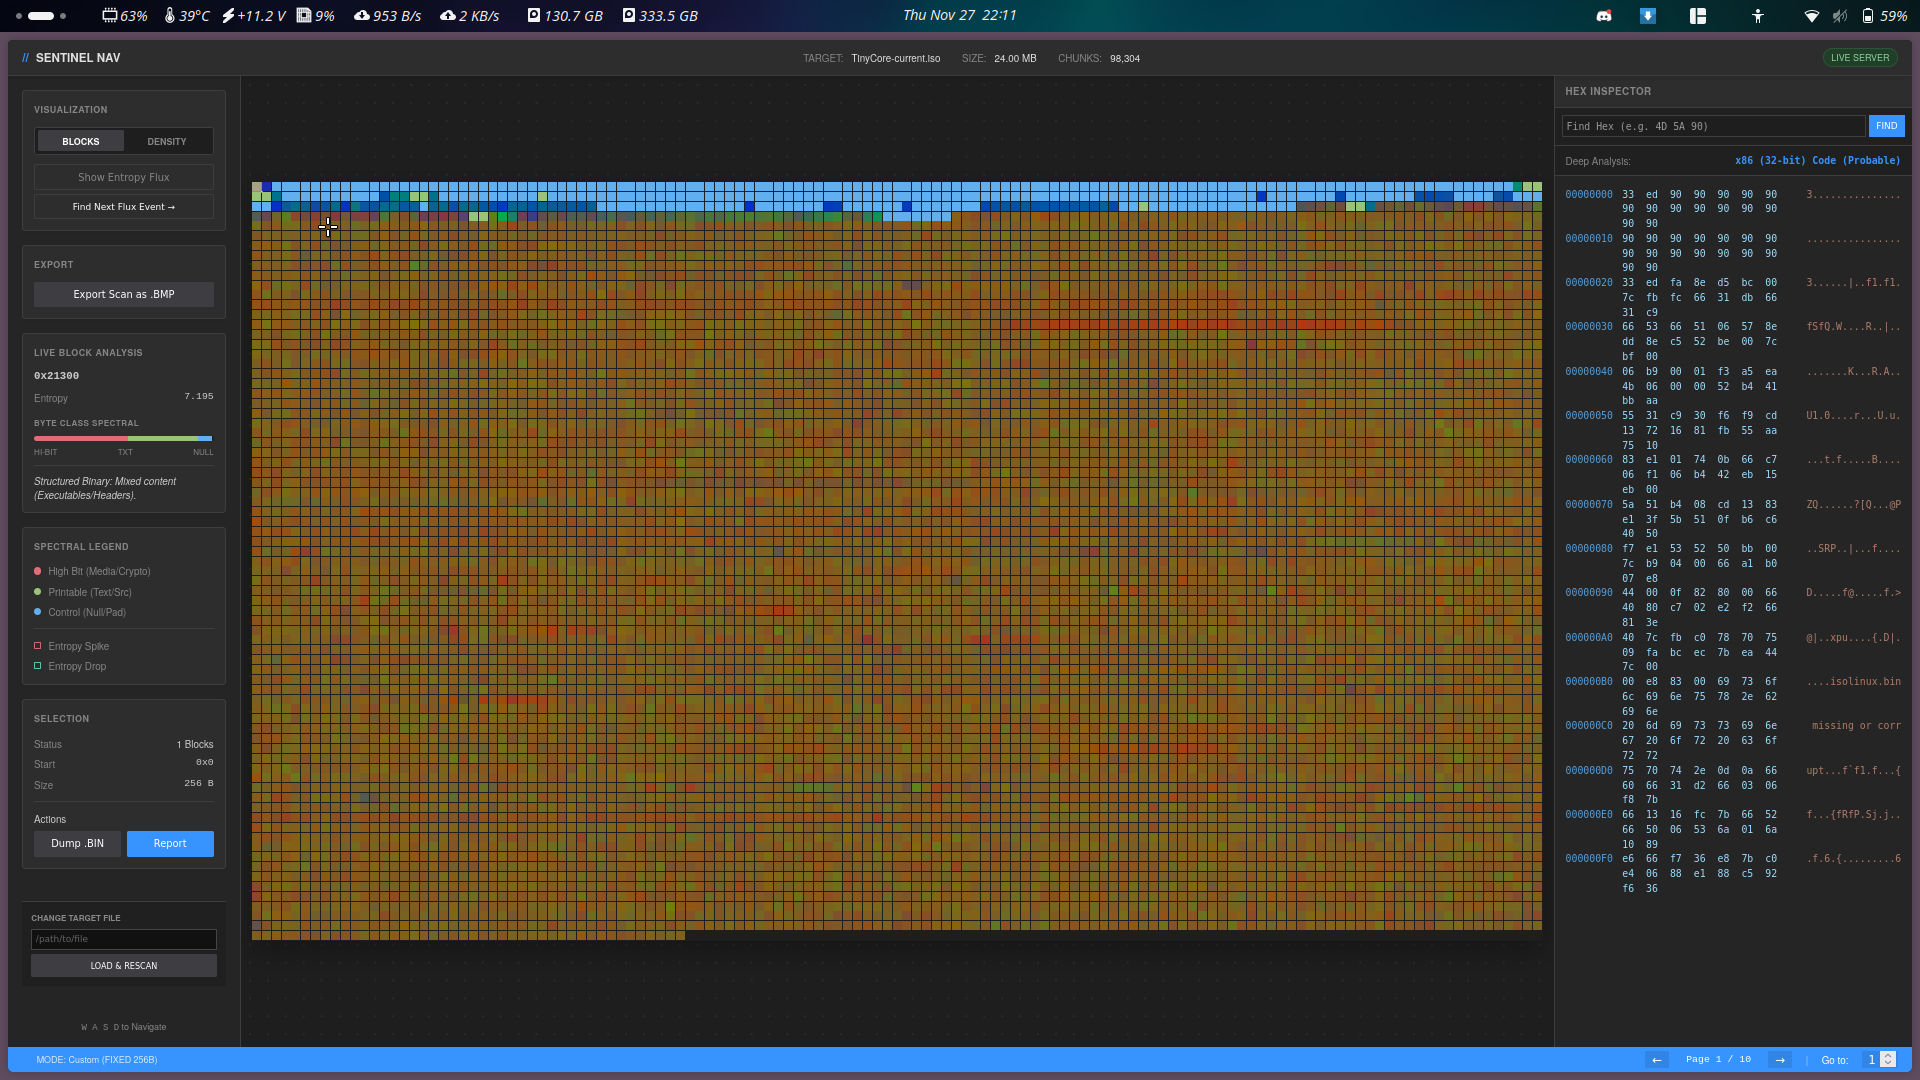
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.
binary-analysisdata-recoverydigital-forensics+4
15111 months ago
interrogate preview

interrogate

GitHubcarmaa/interrogate

Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…

binary-analysiscryptographydata-recovery+4
777 years ago
magic-extractor preview

magic-extractor

GitHubxchwarze/magic-extractor

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
binary-analysisdata-recoverydigital-forensics+8
432 months ago
memory-forensic preview

memory-forensic

GitHubsecurityronin/memory-forensic

Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.


binary-analysiscontainer-escapedata-recovery+7
122 months ago
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

binary-analysisdata-recoverydefensive-tools+14
1.3k11h 9m ago
timesketch preview

timesketch

GitHubgoogle/timesketch

Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

data-recoverydigital-forensicsdisk-forensics+7
3.4k18h 32m ago
IPED preview

IPED

GitHubsepinf-inc/iped

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…

data-recoverydigital-forensicsdisk-forensics+9
3.1k3 days ago
dissect preview

dissect

GitHubfox-it/dissect

Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
data-recoverydigital-forensicsdisk-forensics+5
1.2k4 days ago
sift-kg preview

sift-kg

GitHubjuanceresa/sift-kg

Turn any collection of documents into a knowledge graph. Extract entities and relationships via LLM, deduplicate with your approval. Map domains,…
data-recoverydigital-forensicseducation+4
8025 months ago
BareMetal-RAM-Dumper preview

BareMetal-RAM-Dumper

GitHubpiat0n/baremetal-ram-dumper

A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
data-recoverydigital-forensicsexploitation+3
1043 months ago
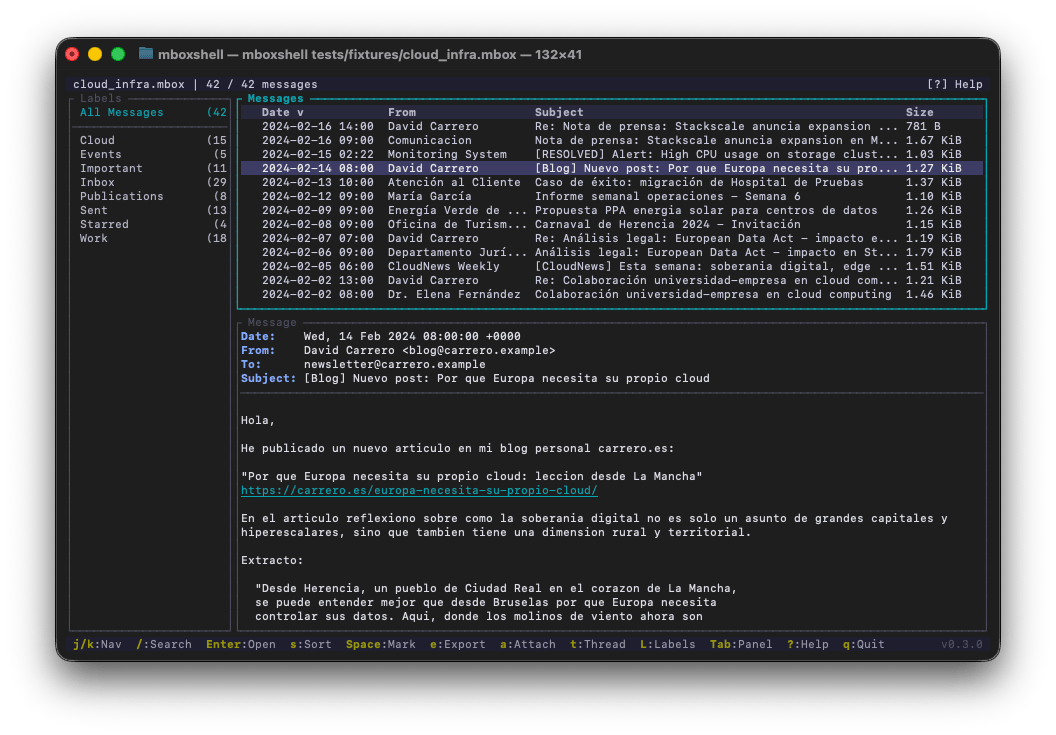
mboxshell preview

mboxshell

GitHubdcarrero/mboxshell

mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…

data-recoverydigital-forensicsemail-security+4
568 days ago
OsintCase preview

OsintCase

GitHubemrekybs/osintcase

An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.

curated-resourcesdata-recoverydigital-forensics+6
77 days ago
Previous12Next