
andriller
 den4uk/andriller
📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…
android-securitydata-recoverydigital-forensics+4
1.6k
den4uk/andriller📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…
 cristianzsh/forensictools
Collection of forensic tools
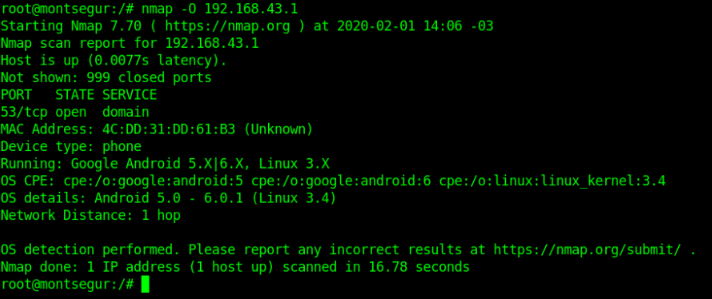 a-poc/blueteam-tools
Tools and Techniques for Blue Team / Incident Response
 juanceresa/sift-kg
Turn any collection of documents into a knowledge graph. Extract entities and relationships via LLM, deduplicate with your approval. Map domains,…
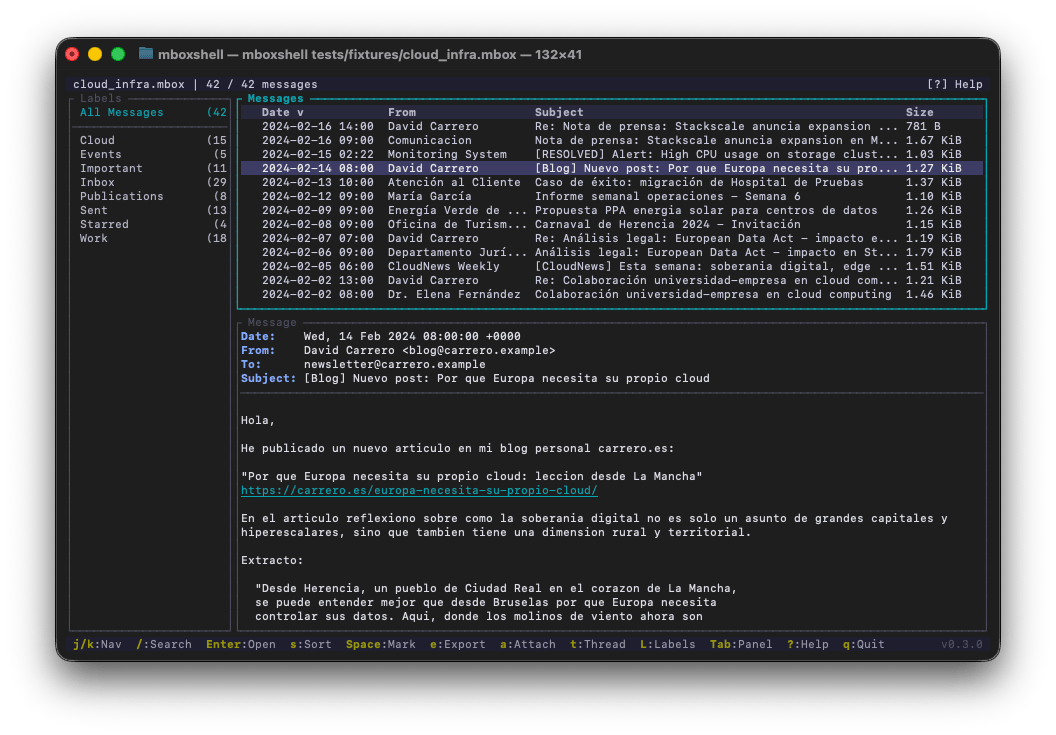 dcarrero/mboxshell
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
 jessek/hashdeep
Cross-platform hashing toolset for computing message digests (MD5, SHA-1, SHA-256, Tiger, Whirlpool) with recursive directory traversal and file…
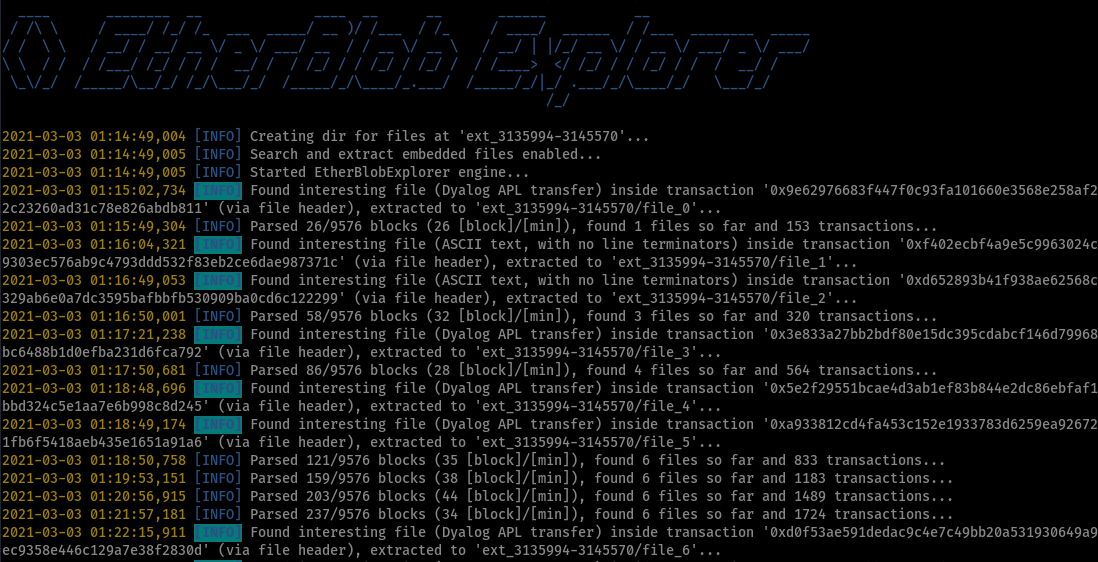 litneet64/etherblob-explorer
Search and extract blob files on the Ethereum Blockchain network
 politoinc/xwfacropalypse
X-Ways Acropalypse extension detects CVE-2023-21036 in common images
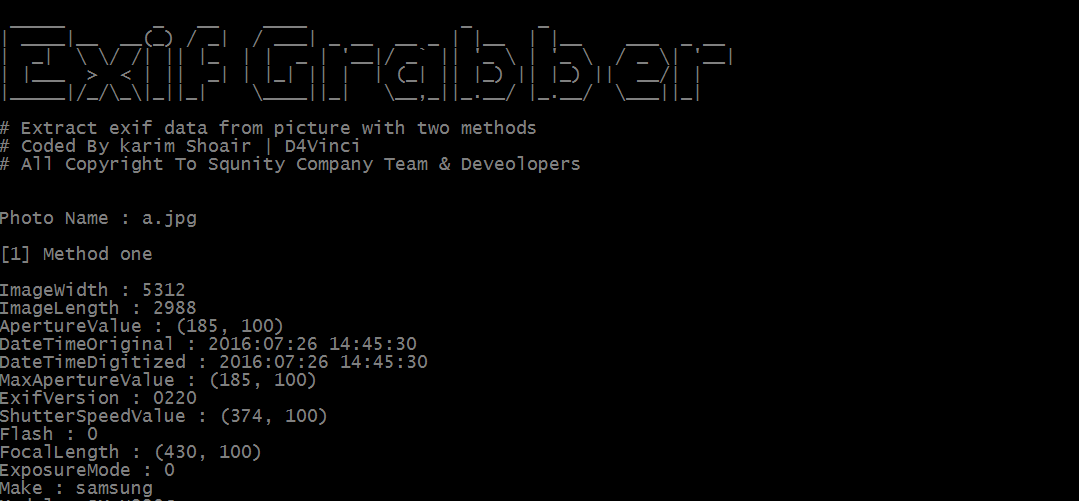 d4vinci/exif-grabber
A python tool that will extract exif data from picture with two methods
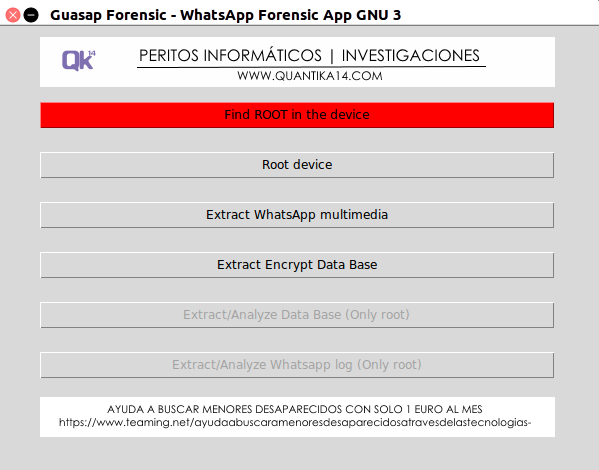 quantika14/guasap-whatsapp-foresincs-tool
WhatsApp Forensic Tool
 qixils/anticropalypse
Discord bot for mitigating the aCropalypse vulnerability (CVE-2023-21036, CVE-2023-28303) by retroactively deleting vulnerable images
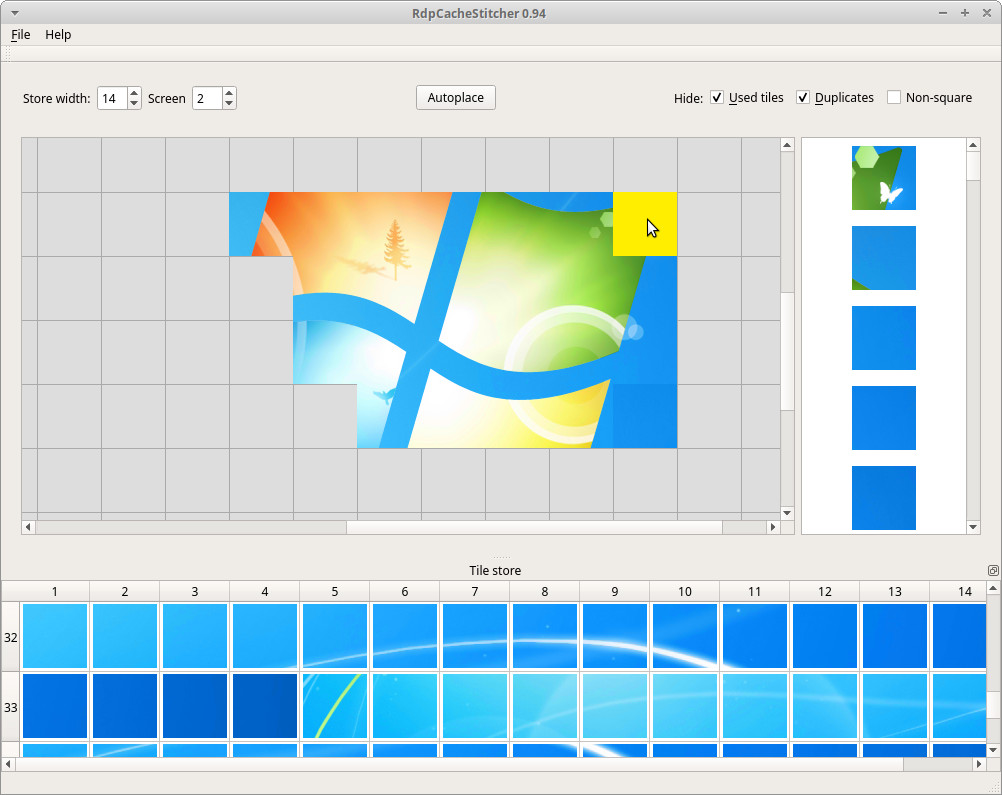 bsi-bund/rdpcachestitcher
RdpCacheStitcher is a tool that supports forensic analysts in reconstructing useful images out of RDP cache bitmaps.
 jfarley248/meat
This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices
 matank001/asclepius
Asclepius validates backup integrity by restoring files and actively testing their recoverability. Instead of trusting metadata, it attempts to parse…
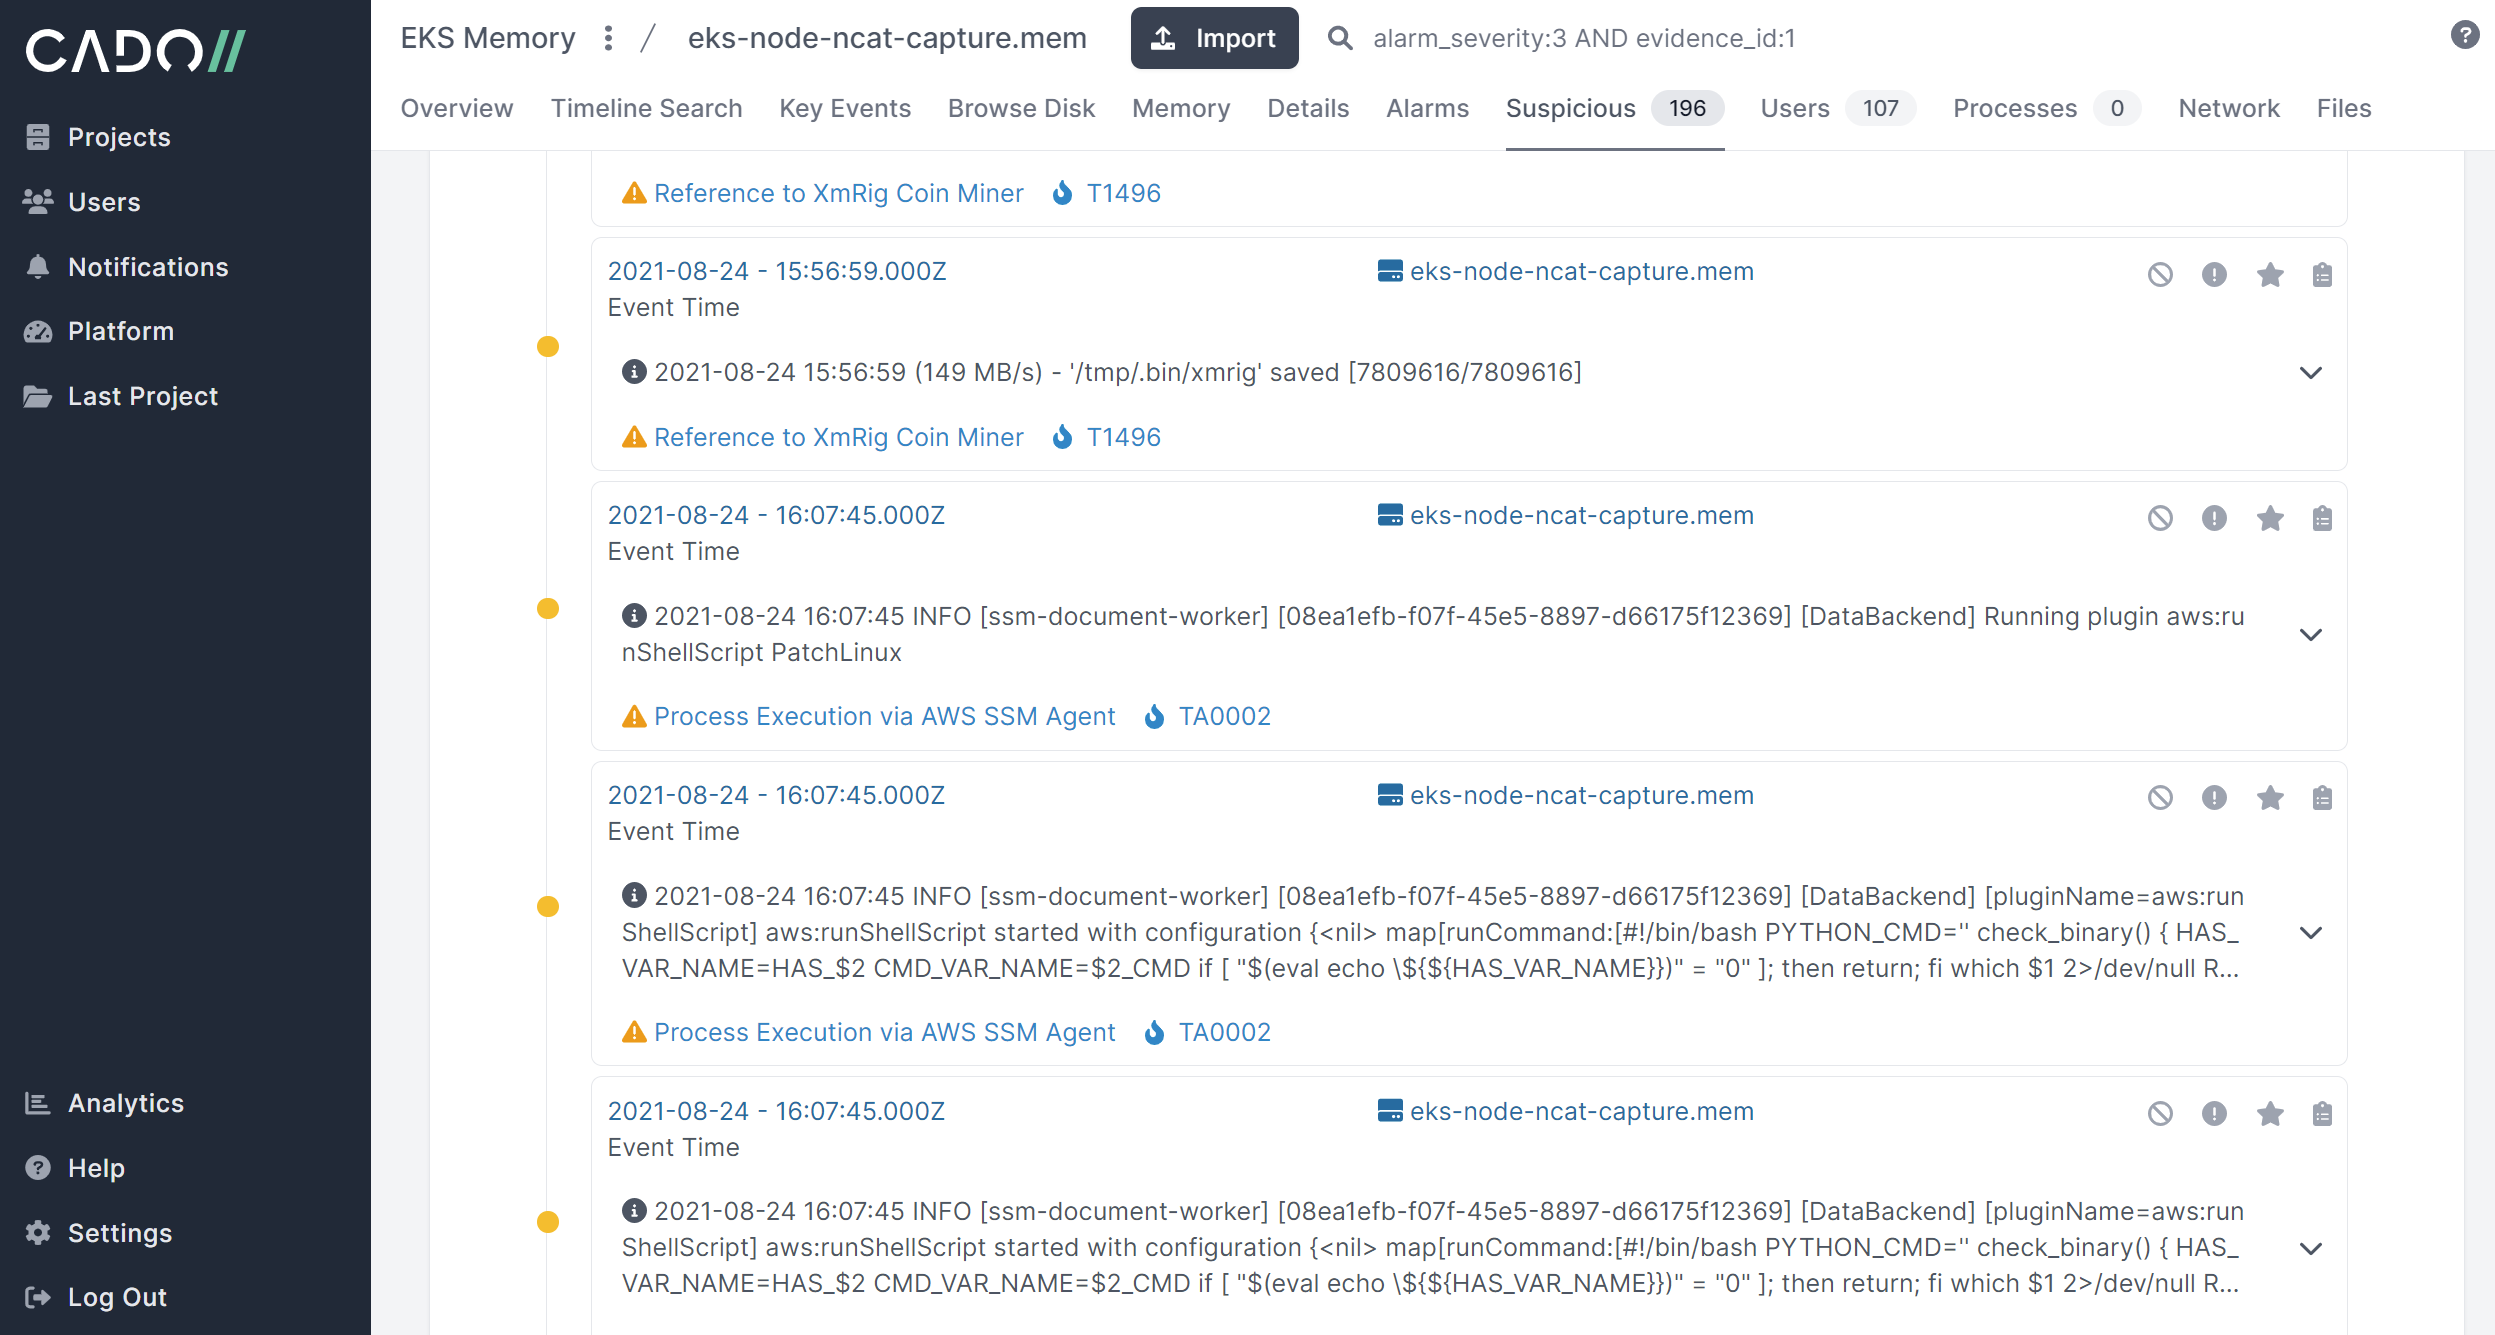 cado-security/rip_raw
Rip Raw is a small tool to analyse the memory of compromised Linux systems.
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 cisagov/esxiargs-recover
A tool to recover from ESXiArgs ransomware