

iCloudKitExtractor
 giordanosconti/icloudkitextractor
Experimental .NET/WPF forensic toolkit for iCloud auth, CloudKit/MMCS backup download, and Octagon/PCS recovery (ADP, Recovery Key, Lockdown Mode).…
authenticationcloud-securitydata-recovery+6
18
giordanosconti/icloudkitextractorExperimental .NET/WPF forensic toolkit for iCloud auth, CloudKit/MMCS backup download, and Octagon/PCS recovery (ADP, Recovery Key, Lockdown Mode).…

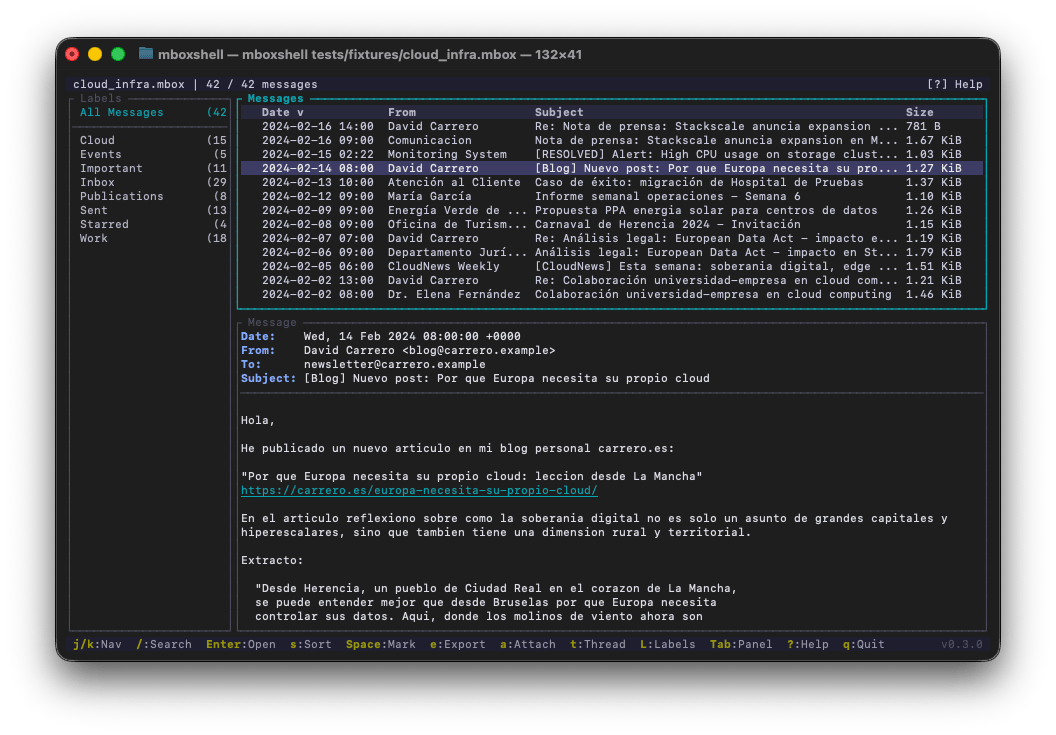 dcarrero/mboxshell
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 piotr-kniaz/eslockdecryptor
Tool for recovering and decrypting ES File Explorer encrypted files (.eslock)
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…

 tchuin2609/yellowkey-bitlocker
Manage BitLocker encrypted drives on Windows. Extract recovery keys, check encryption status, and apply security mitigations for CVE-2026-45585.
 desireeontrial76/yellowkey-bitlocker
Manage and recover BitLocker encrypted drives with this tool for Windows 11 recovery key management and educational study of CVE-2026-45585.
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
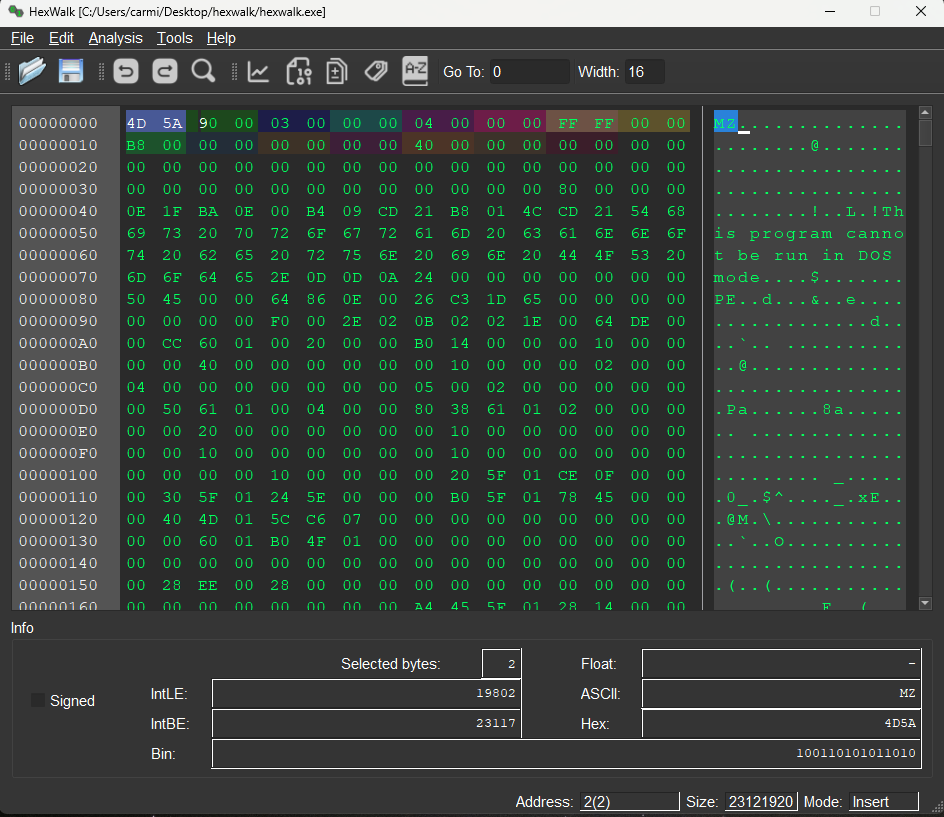 gcarmix/hexwalk
Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 cristianzsh/forensictools
Collection of forensic tools
 neccie/yellowkey-bitlocker-cve-2026-45585
Manage BitLocker recovery keys, unlock encrypted drives, and monitor encryption status with this lightweight Windows utility.
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 x-cmd-build/xz
Portable binary distribution of xz-utils 5.8.3 with CVE-2024-3094 verification. Provides static builds for Linux, macOS, and Windows for compression…
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files