
yellowkey-bitlocker
Manage and recover BitLocker encrypted drives with this tool for Windows 11 recovery key management and educational study of CVE-2026-45585.

Manage and recover BitLocker encrypted drives with this tool for Windows 11 recovery key management and educational study of CVE-2026-45585.

Extract files from any kind of container formats

Tools developed by the Zscaler ThreatLabz Threat Intelligence team

Manage BitLocker encrypted drives on Windows. Extract recovery keys, check encryption status, and apply security mitigations for CVE-2026-45585.

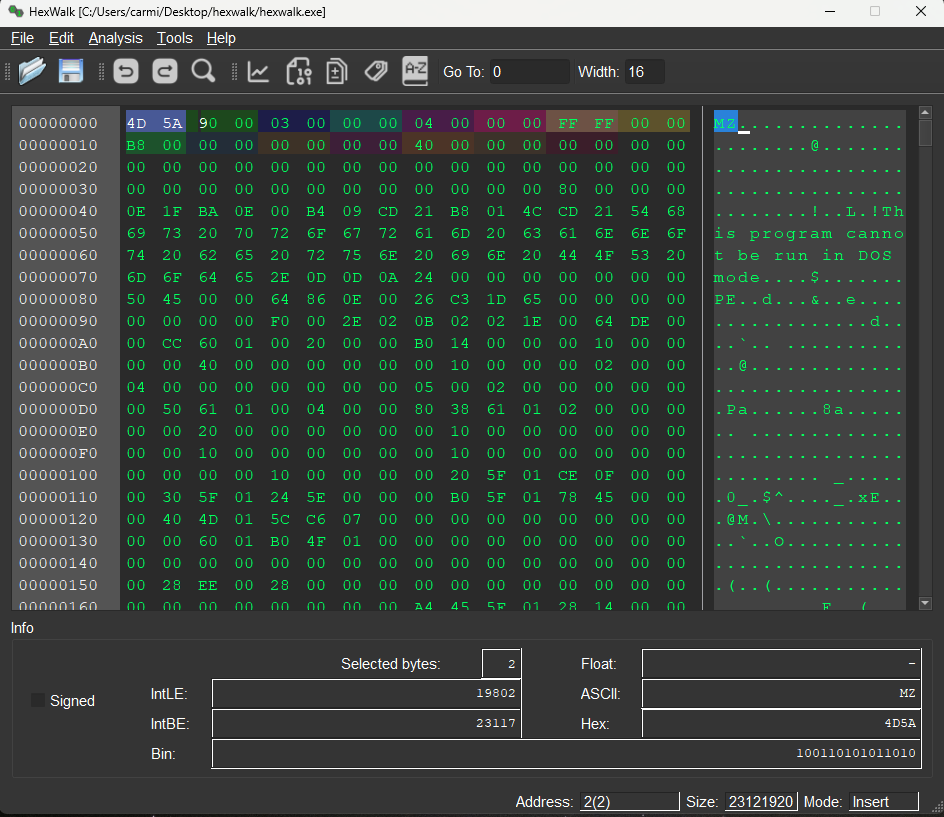
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.

YellowKey BitLocker recovery audits CVE-2026-45585: yellowkey github, TPM, recovery key backup. Windows 10/11 CLI GUI, portable audit tool for…

Find your device and control it remotely. Works over SMS, instant messengers, or FMD Server's web interface. A secure open source alternative to…

Production-grade Security Baseline & Hardening Guide for Ubuntu 24.04/26.04 LTS. Kernel isolation, Emergency Panic Button, custom AppArmor/Firejail…

Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS

Mediatek Flash and Repair Utility

This is the development tree. Production downloads are at:

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.

Tools and Techniques for Blue Team / Incident Response

Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.

Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.

A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.

BitLocker full-disk encryption bypass research using CVE-2023-21563 (BitPixie). Methodology, exploit chain, and defensive recommendations.