
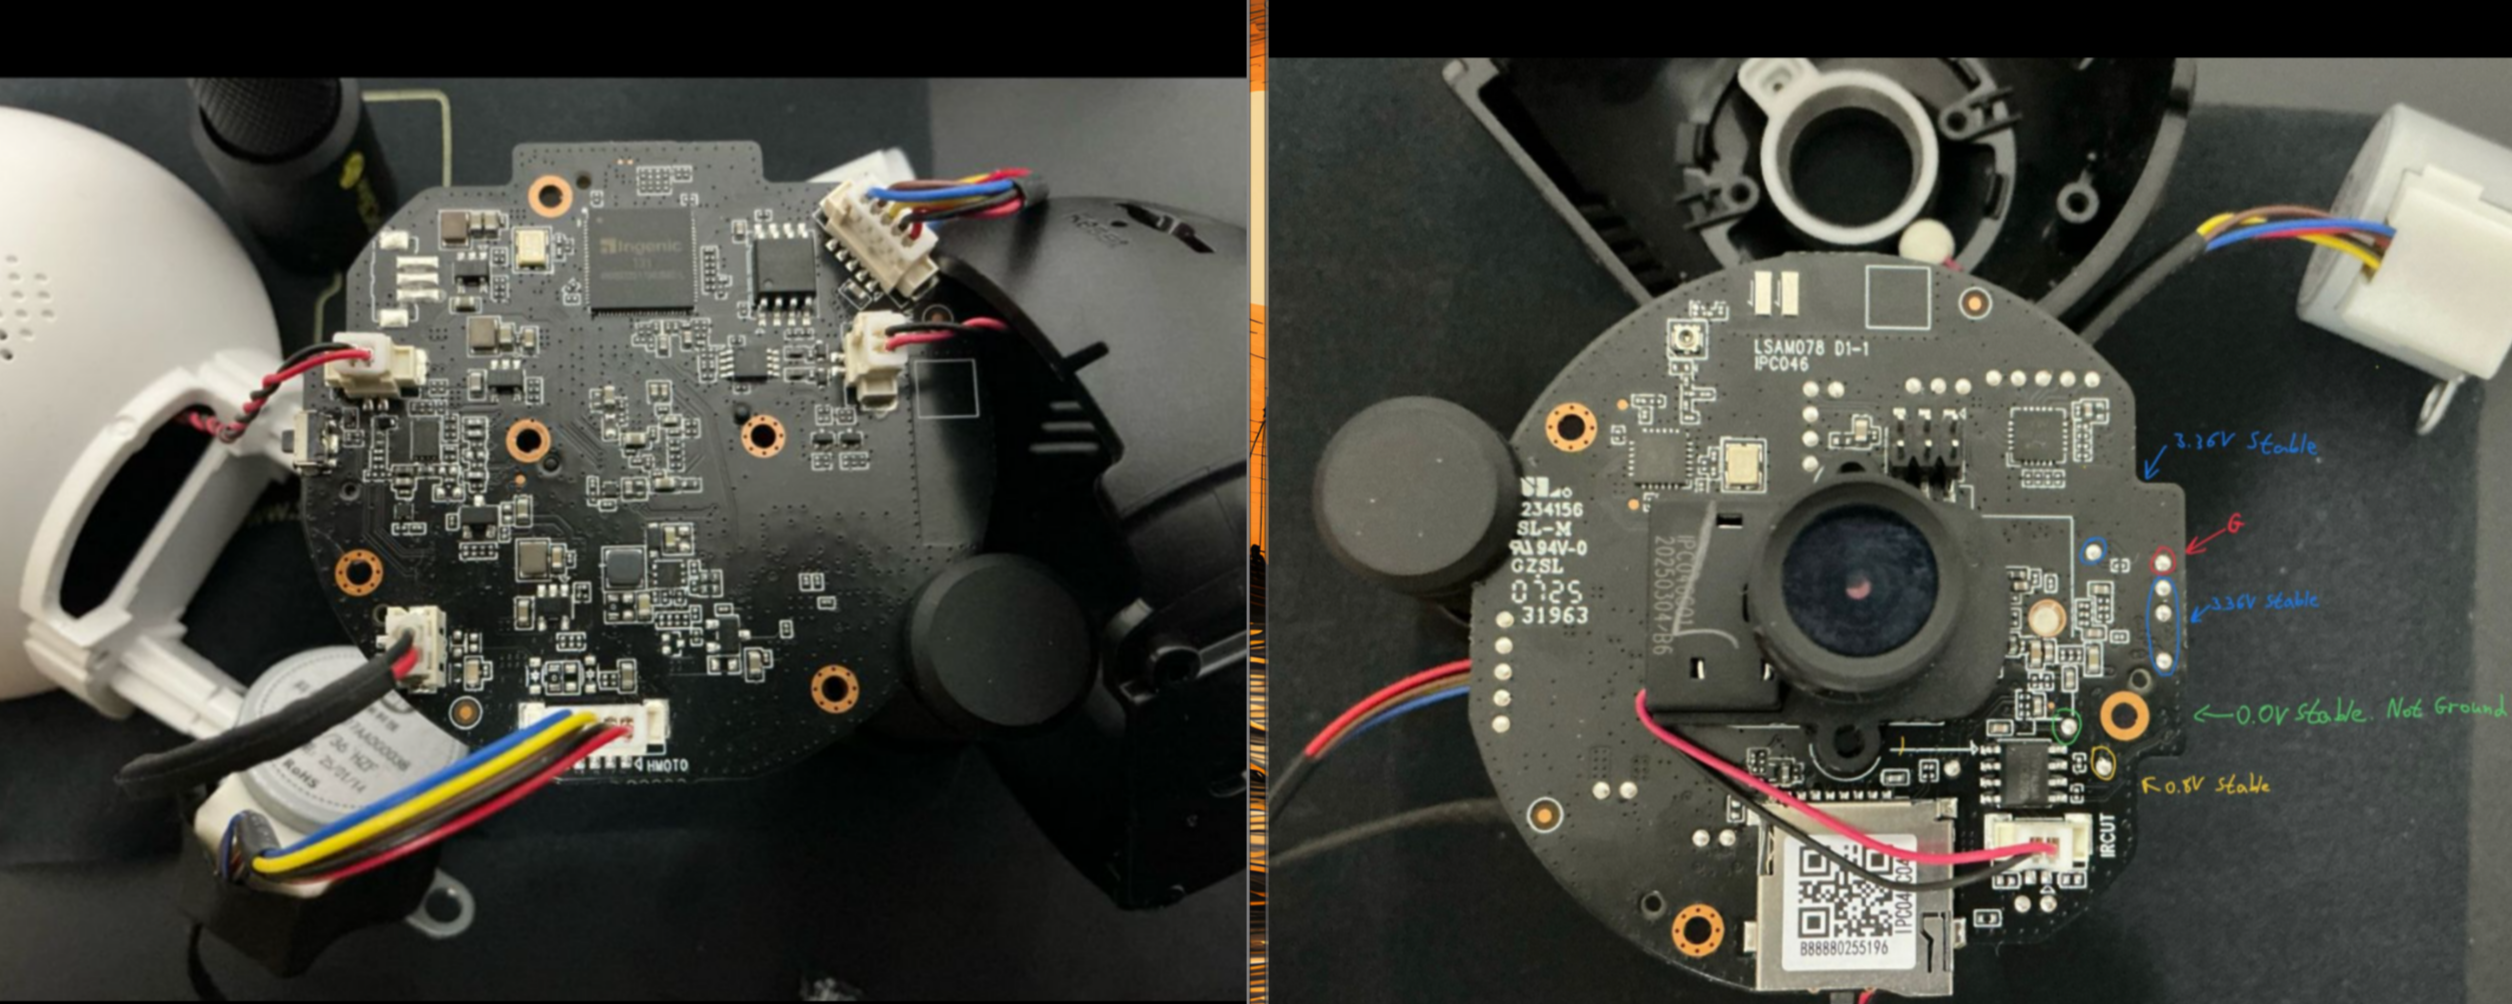
Xiaomi-C200-Firmware-Analysis
 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
data-recoveryembedded-systems-securityexploitation+6
h3xdum/xiaomi-c200-firmware-analysisFrom UART to Root: Breaking Into the Xiaomi C200 via U-Boot
 kfallahi/underlaycopy
PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 grishinpv/poc_cve-2021-36934
POC experiments with Volume Shadow copy Service (VSS)
 3gstudent/ntfsdump
Use to copy a file from an NTFS partitioned volume by reading the raw volume and parsing the NTFS structures.
 kvasirsecurity/kvasir
Kvasir: Penetration Test Data Management