security-baseline-ubuntu

Production-grade Security Baseline & Hardening Guide for Ubuntu 24.04/26.04 LTS. Kernel isolation, Emergency Panic Button, custom AppArmor/Firejail…

Production-grade Security Baseline & Hardening Guide for Ubuntu 24.04/26.04 LTS. Kernel isolation, Emergency Panic Button, custom AppArmor/Firejail…

Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…

Library and tools to access the Windows New Technology File System (NTFS)

Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…

PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads

Manage BitLocker encrypted drives on Windows. Extract recovery keys, check encryption status, and apply security mitigations for CVE-2026-45585.

A Mac OS X forensic utility which manages file system mounting in support of forensic procedures.

Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…

F*ck file system - cli file search tool that bypasses OS kernel and reads your disc directlry

KeePass 2.53.1 with removed ECAS Trigger System Remediating CVE-2023-24055

Cryptanalysis of a proprietary 1999 video DRM system. Recovers 61 encrypted wrestling videos from the WCW Internet Powerdisk CD-ROM through static…

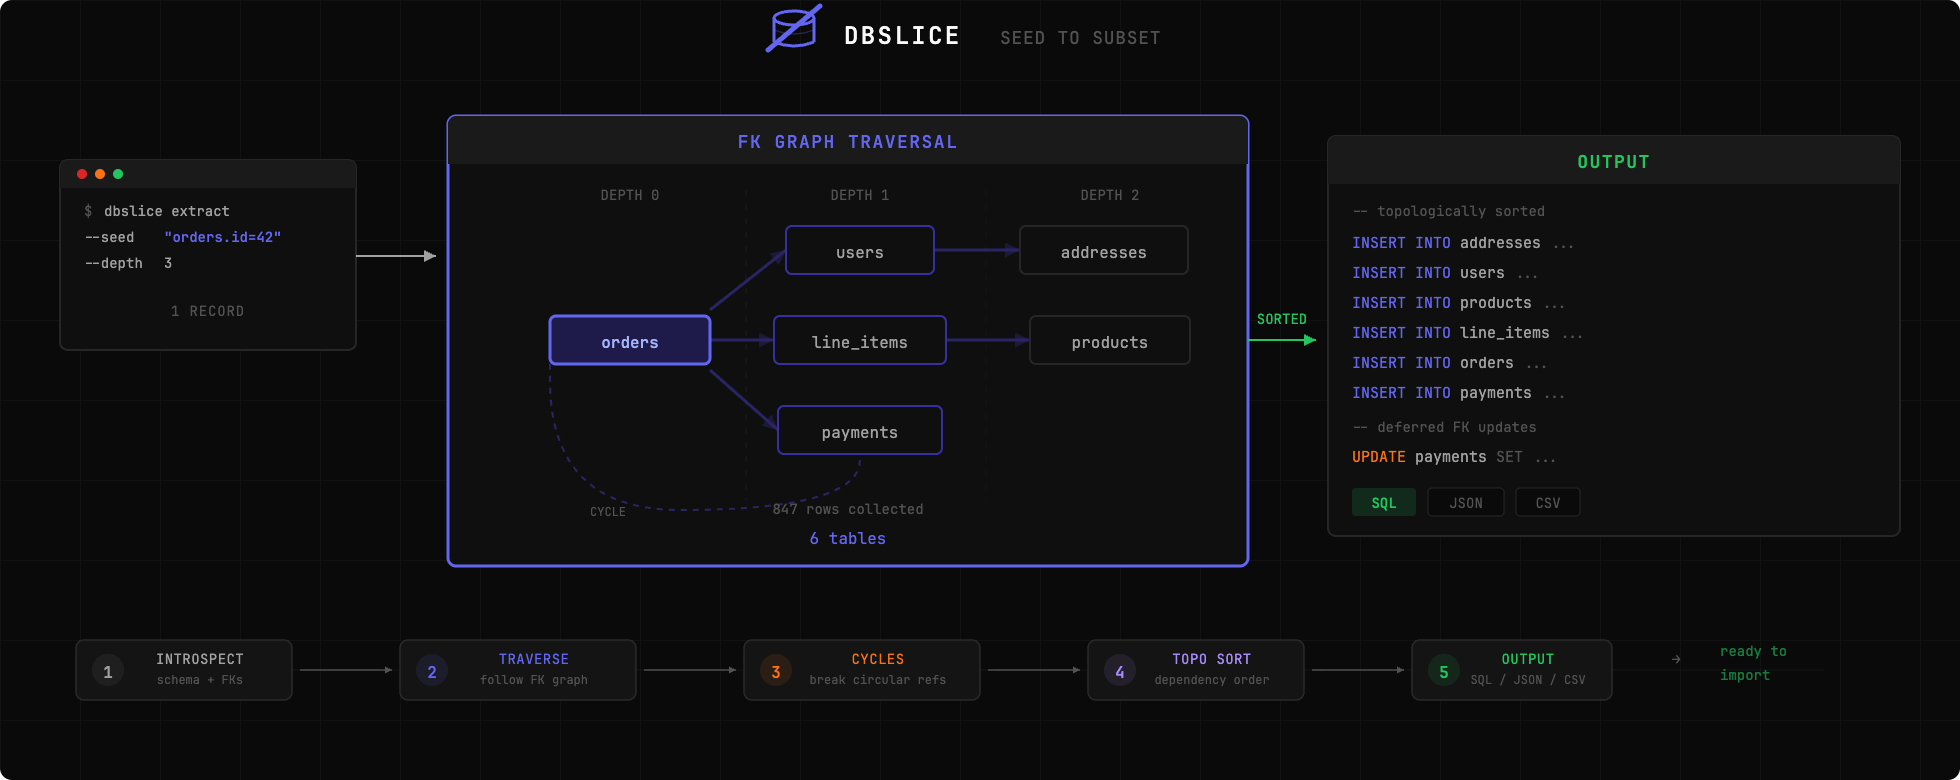
Extract a slice of your production database to reproduce bugs locally. Point dbslice at a record, it follows foreign keys and gives you a complete,…

Parallel backup and restore solution for PostgreSQL with encryption, delta restore, and multi-cloud object store support for enterprise disaster…

A tool for forensic file system reconstruction.

FAT filesystems explore, extract, repair, and forensic tool

Crack ios Restriction PassCode in Python

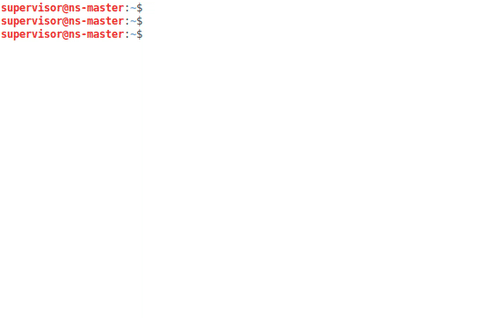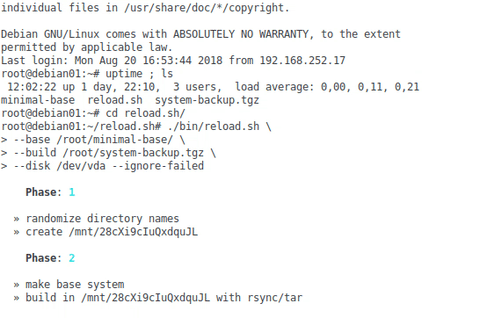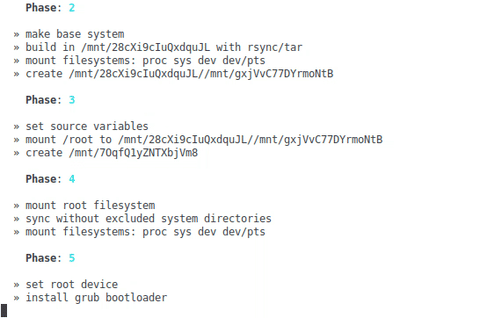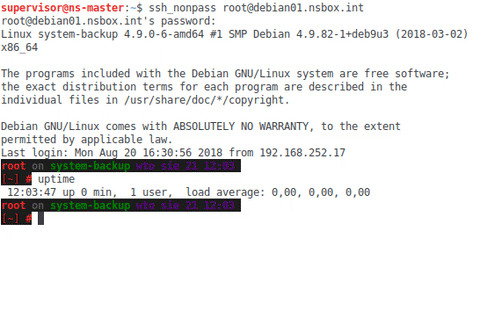
Wipe, reinstall or restore your system from running GNU/Linux distribution. Via SSH, without rebooting.

This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices