

DeadMatter
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
data-recoverydigital-forensicsforensics+7
qsecure-labs/deadmatterOffset Independent Credential Extraction Tool
 disqualifier/psa-2026-00043-recovery
Recovery notes for proxmox advisory ID: PSA-2026-00043-1 (CVE-2023-54391)
 neccie/yellowkey-bitlocker-cve-2026-45585
Manage BitLocker recovery keys, unlock encrypted drives, and monitor encryption status with this lightweight Windows utility.
 s4larie/walletool
A utility for extracting cryptocurrency wallet data from wallet.dat files.
 korczis/foremost
File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…
 sleuthkit/scalpel
File carving and indexing tool for digital forensics, recovering files from disk images based on header/footer pattern matching, regular expressions,…
 cgsecurity/testdisk
Recovers lost partitions and repairs boot sectors; carves 480+ file formats from damaged disks and filesystems for data recovery and forensic use.
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 cherojeong/extundelete
Undelete and recover accidentally erased files from ext3 and ext4 filesystems, using inode scanning and block recovery for forensic and data-loss…
 gnu-mirror-unofficial/ddrescue
Copies data from damaged or failing storage devices, handles read errors, and performs efficient rescue operations to recover as much data as…
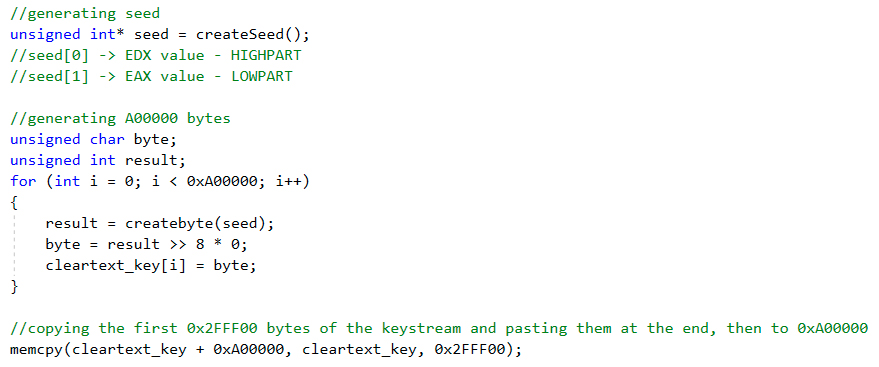 reecdeep/hivev5_keystream_decryptor
bad stuffs by bad guys
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
 3gstudent/ntfsdump
Use to copy a file from an NTFS partitioned volume by reading the raw volume and parsing the NTFS structures.
 enferex/pdfresurrect
Analyze and help extract older "hidden" versions of a pdf from the current pdf.

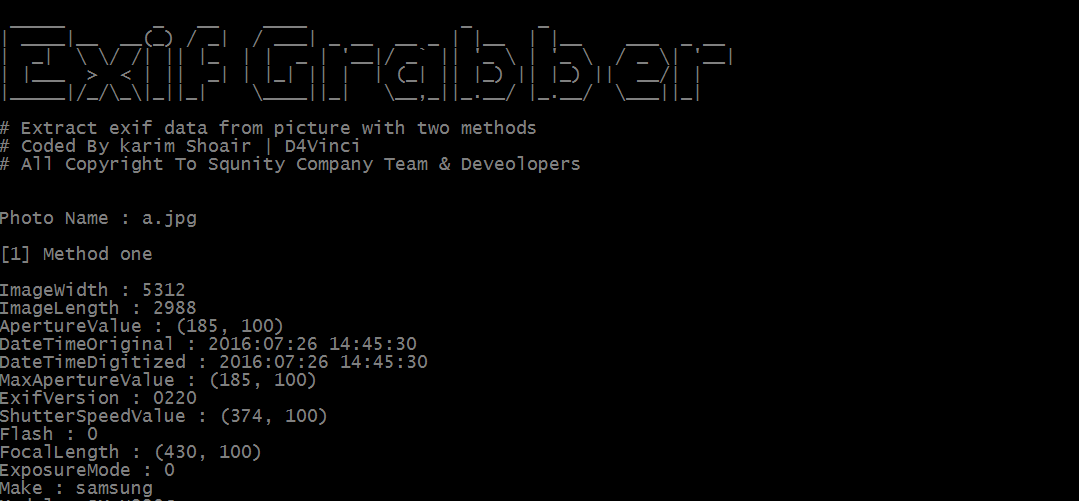 d4vinci/exif-grabber
A python tool that will extract exif data from picture with two methods
 elevenpaths/iphonerestrictionspasscodebf
Extracts and decrypts the 4-digit restriction passcode from iPhone backups on Windows machines, enabling recovery of device access controls.
 elevenpaths/metashield-clean-up-sdk-python
Python SDK for removing hidden metadata from files (PDF, Office, images) to protect privacy and prevent data leakage via automated cleaning workflows.