YellowKey-BitLocker-CVE-2026-45585

YellowKey BitLocker recovery audits CVE-2026-45585: yellowkey github, TPM, recovery key backup. Windows 10/11 CLI GUI, portable audit tool for…

YellowKey BitLocker recovery audits CVE-2026-45585: yellowkey github, TPM, recovery key backup. Windows 10/11 CLI GUI, portable audit tool for…

Offset Independent Credential Extraction Tool

An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.

Total Commander FTP Password Recovery Tool for Python allows you to decrypt the FTP account password information for all Total Commander versions…

Manage BitLocker recovery keys, unlock encrypted drives, and monitor encryption status with this lightweight Windows utility.

Extracts cryptocurrency private keys and addresses from wallet.dat files for Bitcoin and Litecoin, enabling wallet recovery and forensic analysis.

A utility for extracting cryptocurrency wallet data from wallet.dat files.

File carving and indexing tool for digital forensics, recovering files from disk images based on header/footer pattern matching, regular expressions,…

Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

Tools developed by the Zscaler ThreatLabz Threat Intelligence team

Hive v5 file decryption algorithm

Tool for checking passwords against TrueCrypt encrypted volumes and disks, and/or decrypting the data.

Analyze and help extract older "hidden" versions of a pdf from the current pdf.

Utility for recovering ES File Explorer encrypted files (.eslock)

Binary and Directory tree comparison tool using Fuzzy Hashing

This is the development tree. Production downloads are at:

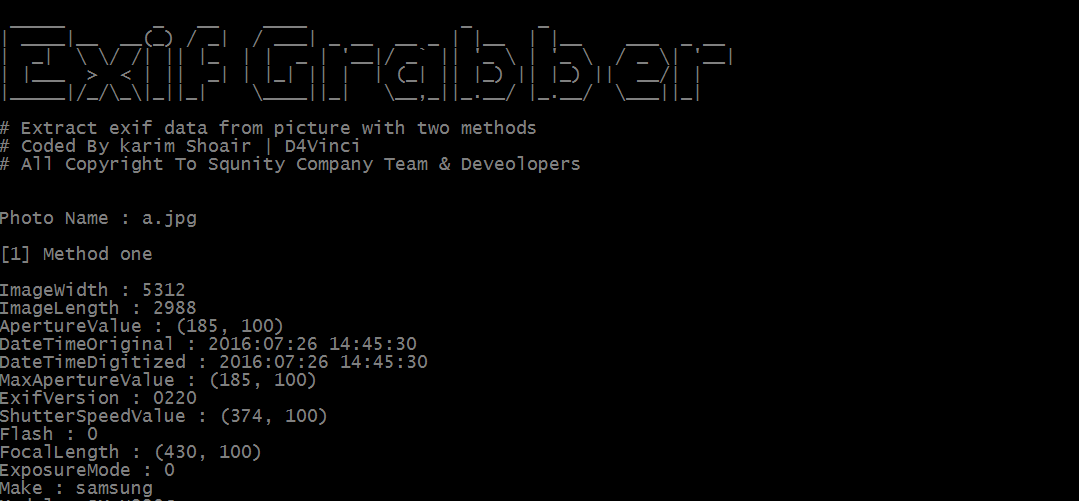
A python tool that will extract exif data from picture with two methods