

mtkclient
 bkerler/mtkclient
Mediatek Flash and Repair Utility
android-securitydata-recoveryembedded-systems-security+5
bkerler/mtkclientMediatek Flash and Repair Utility
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 dimareverse/nuitka-static-unpacker
Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.
 roxanne_ardary/nullify
Automated, policy-driven data retention and deletion system with immutable audit trails, RBAC/ABAC, multi-jurisdiction compliance, and AI/ML…
 qg5casz/walletool
Extracts cryptocurrency private keys and addresses from wallet.dat files for Bitcoin and Litecoin, enabling wallet recovery and forensic analysis.

 emrekybs/osintcase
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
 filosottile/age
A simple, modern and secure encryption tool (and Go library) with small explicit keys, no config options, and UNIX-style composability.
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 elevenpaths/iphonerestrictionspasscodebf
Extracts and decrypts the 4-digit restriction passcode from iPhone backups on Windows machines, enabling recovery of device access controls.
 gregwar/fatcat
FAT filesystems explore, extract, repair, and forensic tool
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
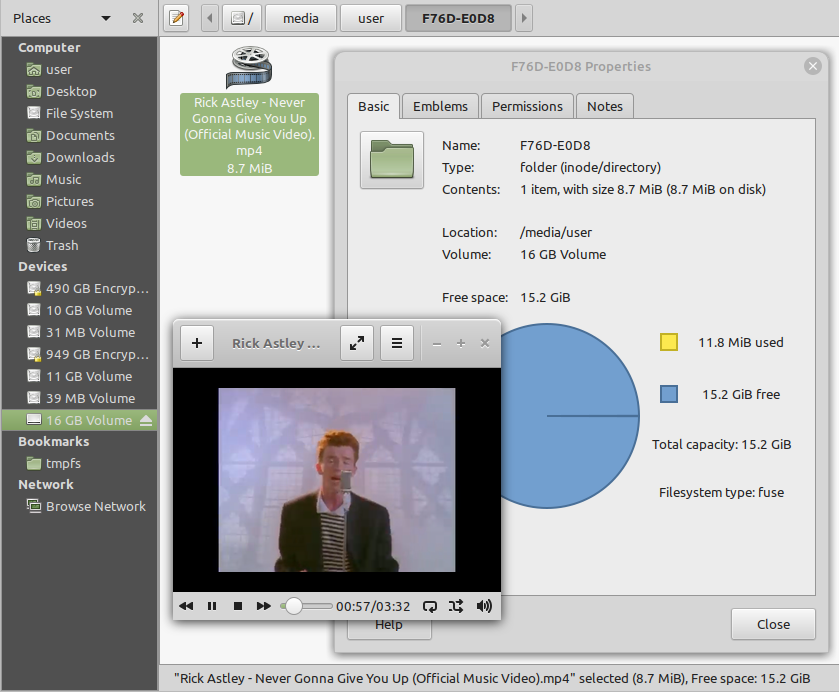 hakavlad/tird
Steganographic storage & File encryption tool
 sleuthkit/scalpel
File carving and indexing tool for digital forensics, recovering files from disk images based on header/footer pattern matching, regular expressions,…
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
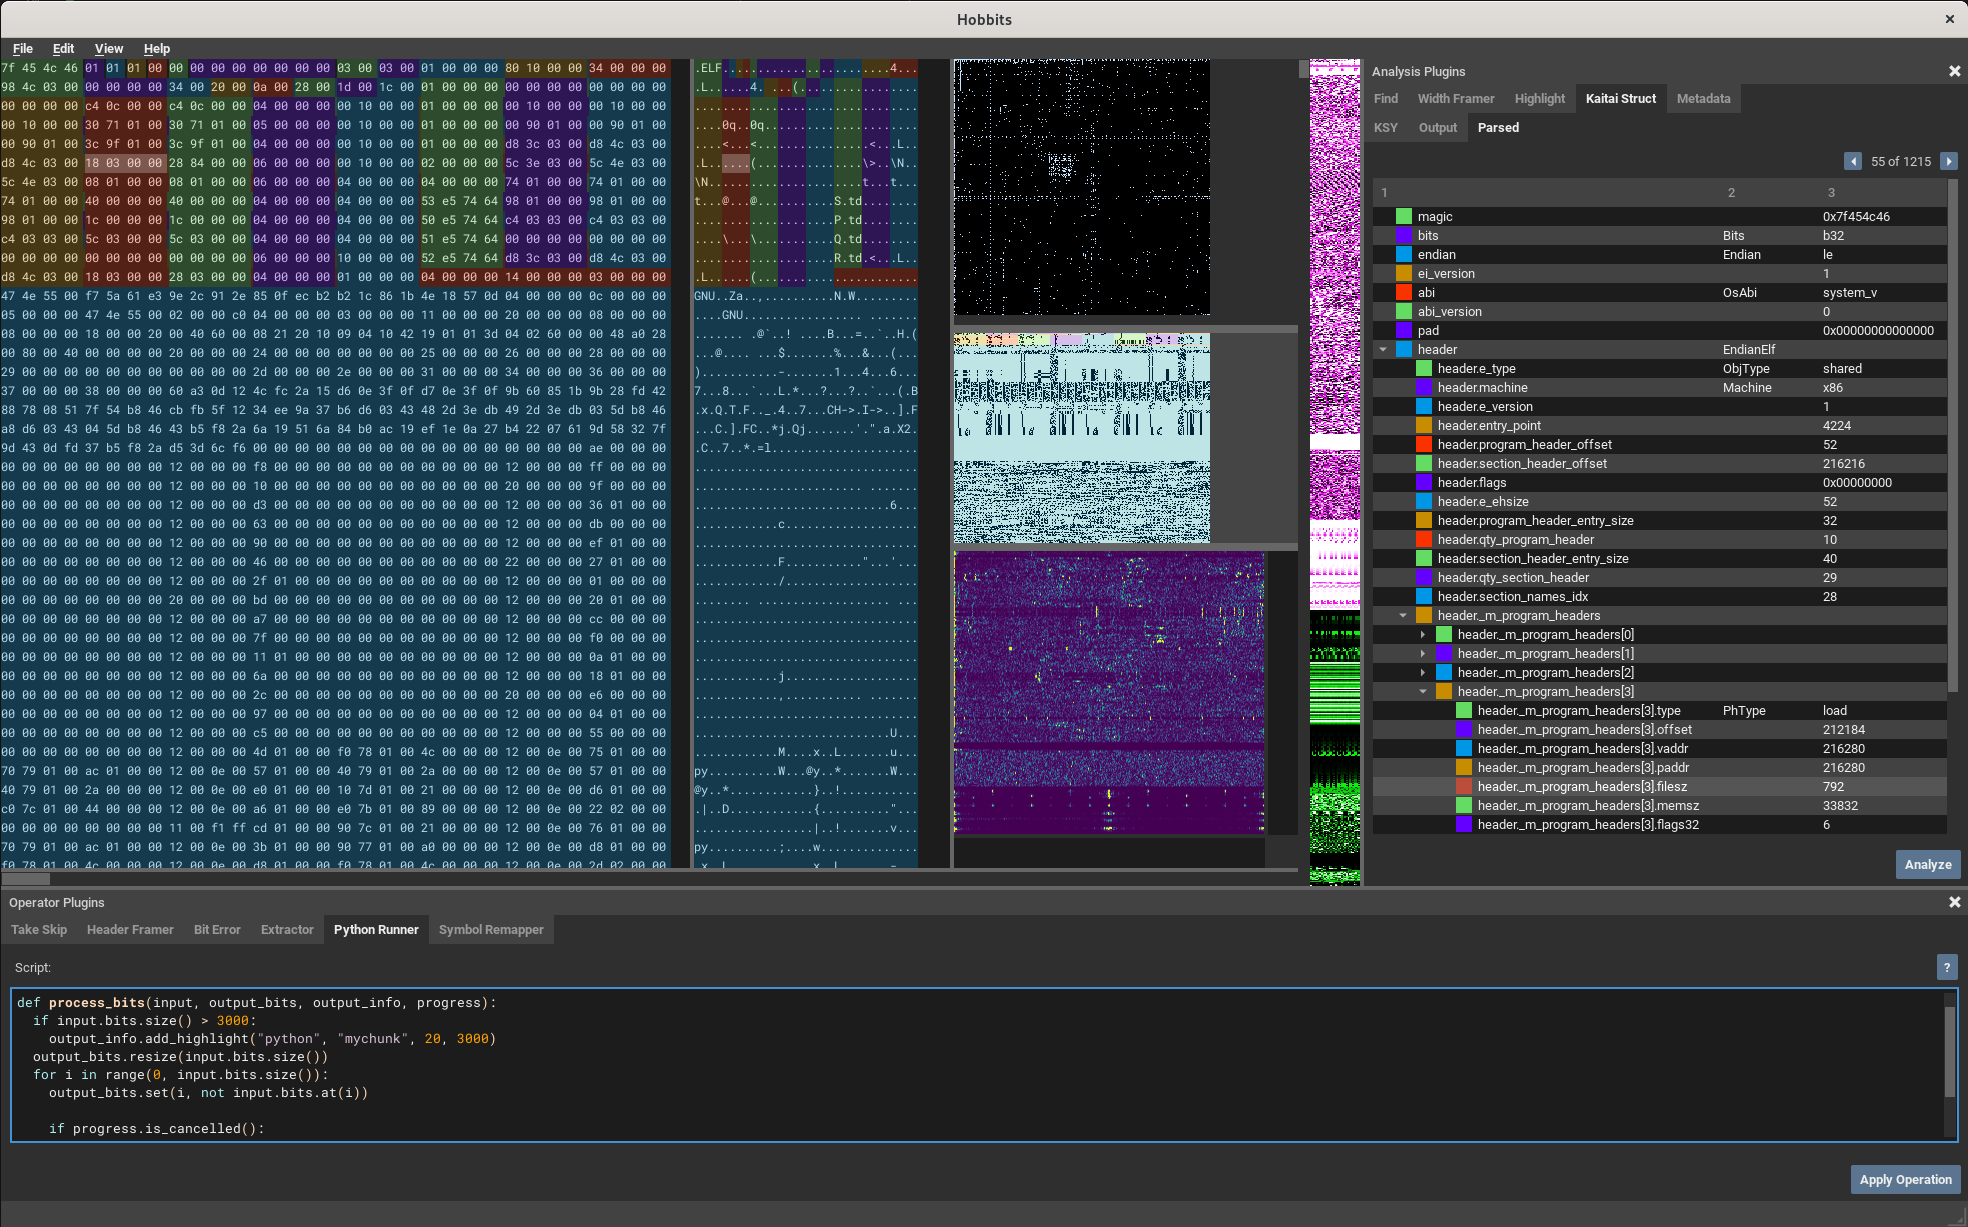 mahlet-inc/hobbits
A multi-platform GUI for bit-based analysis, processing, and visualization
 piotr-kniaz/eslockdecryptor
Tool for recovering and decrypting ES File Explorer encrypted files (.eslock)
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…