

whapa
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
android-securitydata-recoverydigital-forensics+5
1.5k
b16f00t/whapaGraphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
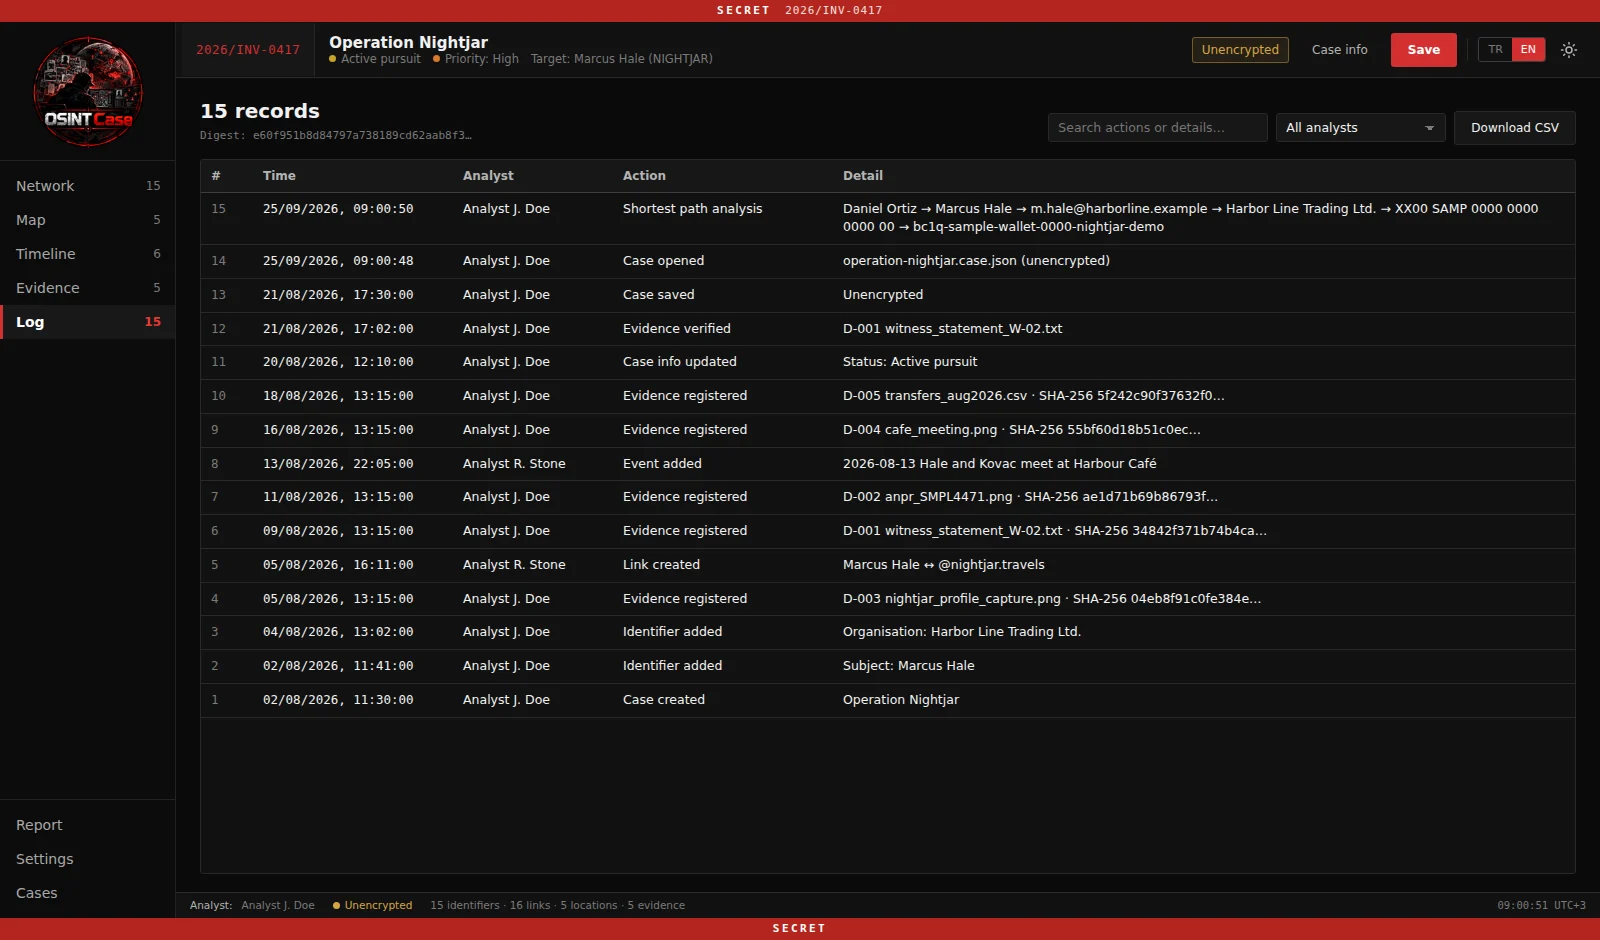 emrekybs/osintcase
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 a-poc/blueteam-tools
Tools and Techniques for Blue Team / Incident Response
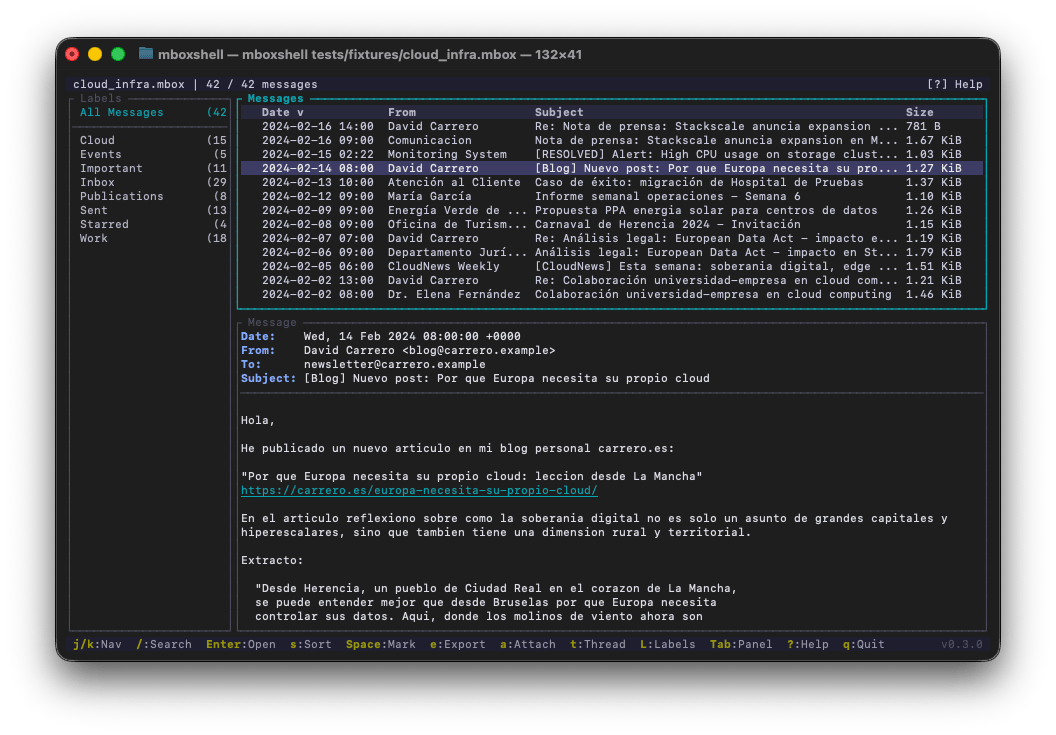 dcarrero/mboxshell
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…

 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 cristianzsh/forensictools
Collection of forensic tools
 kvasirsecurity/kvasir
Kvasir: Penetration Test Data Management
 juanceresa/sift-kg
Turn any collection of documents into a knowledge graph. Extract entities and relationships via LLM, deduplicate with your approval. Map domains,…
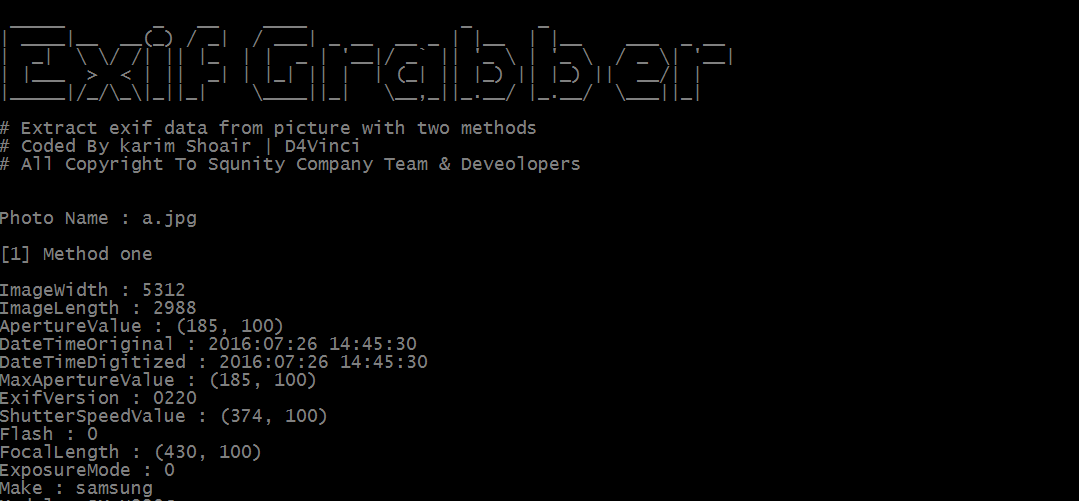 d4vinci/exif-grabber
A python tool that will extract exif data from picture with two methods
 radkawar/aws-firmware-dump
Acquires the EBS disks of an AWS AMI you can launch, streaming snapshots via EBS direct APIs to a private S3 bucket with sha256 manifests and…
 carmaa/interrogate
Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…
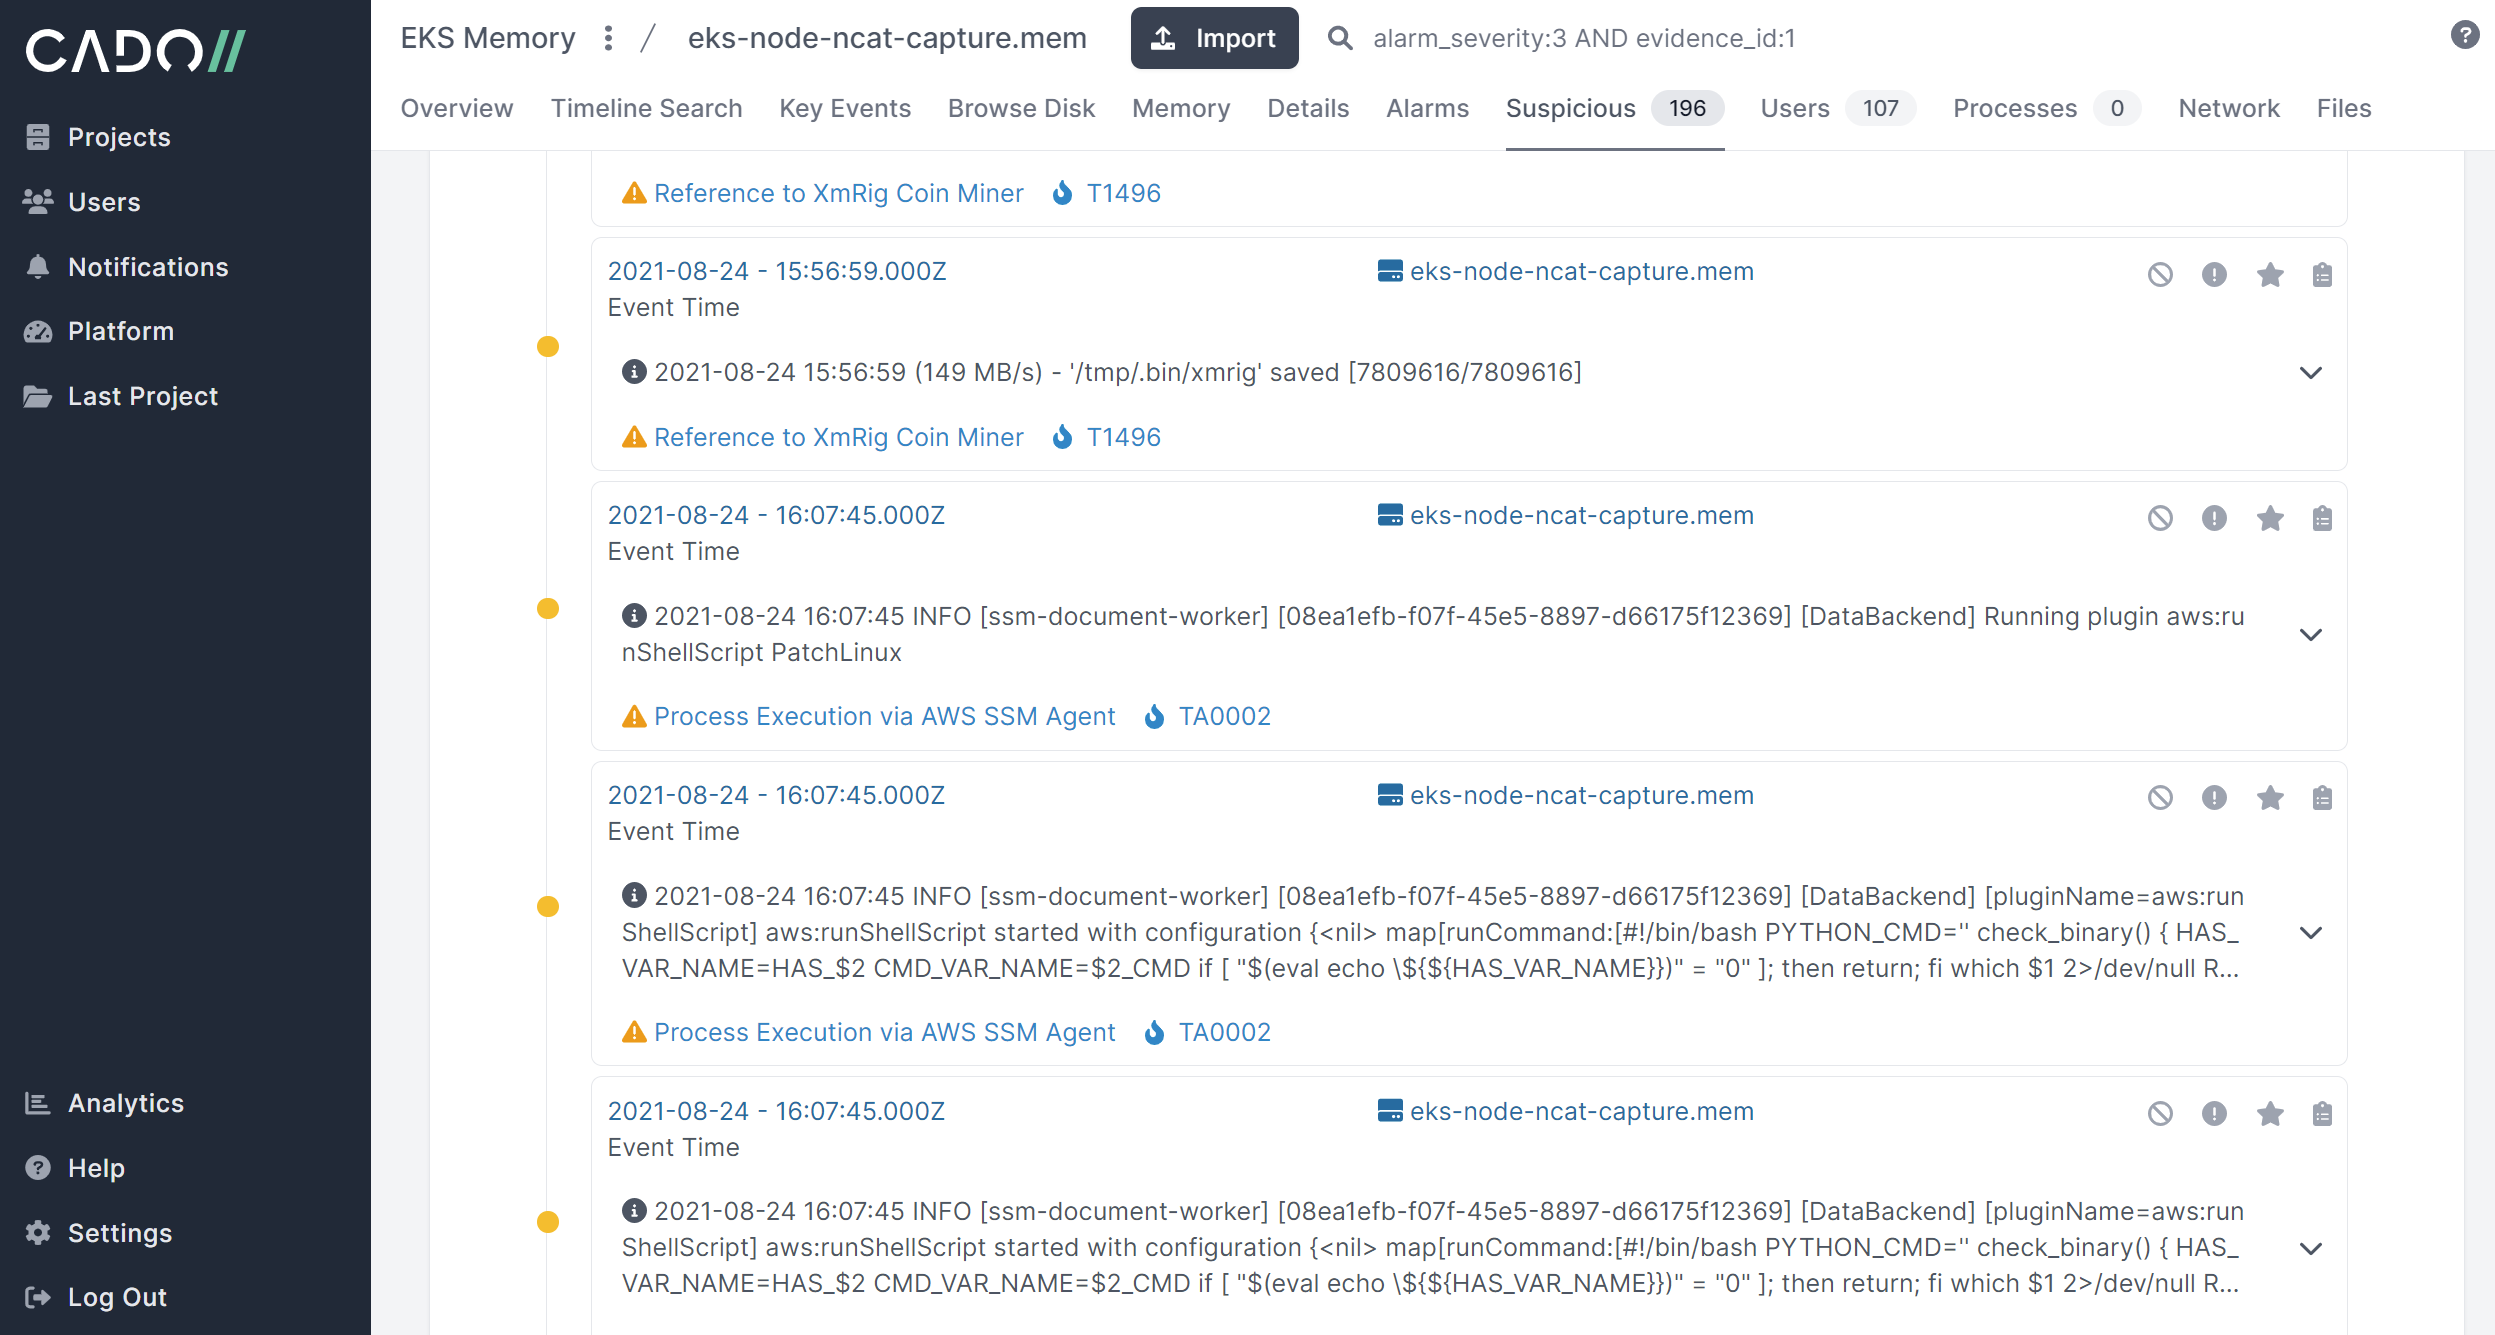 cado-security/rip_raw
Rip Raw is a small tool to analyse the memory of compromised Linux systems.
 litneet64/etherblob-explorer
Search and extract blob files on the Ethereum Blockchain network
 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys