

androidqf
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
android-securitydata-recoverydigital-forensics+4
341
mvt-project/androidqfandroidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…

 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 gregwar/fatcat
FAT filesystems explore, extract, repair, and forensic tool
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 sleuthkit/scalpel
File carving and indexing tool for digital forensics, recovering files from disk images based on header/footer pattern matching, regular expressions,…
 neccie/yellowkey-bitlocker-cve-2026-45585
Manage BitLocker recovery keys, unlock encrypted drives, and monitor encryption status with this lightweight Windows utility.

 pelock/total-commander-ftp-password-recovery-tool-python
Total Commander FTP Password Recovery Tool for Python allows you to decrypt the FTP account password information for all Total Commander versions…
 lazza/recuperabit
A tool for forensic file system reconstruction.
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 rejithregi-group/securityproject
Python Security Project that implements a file encryption and decryption tool
 thewhiteninja/ntfstool
Forensics tool for NTFS (parser, mft, bitlocker, deleted files)
 desireeontrial76/yellowkey-bitlocker
Manage and recover BitLocker encrypted drives with this tool for Windows 11 recovery key management and educational study of CVE-2026-45585.
 dmtrkovalenko/ffs
F*ck file system - cli file search tool that bypasses OS kernel and reads your disc directlry
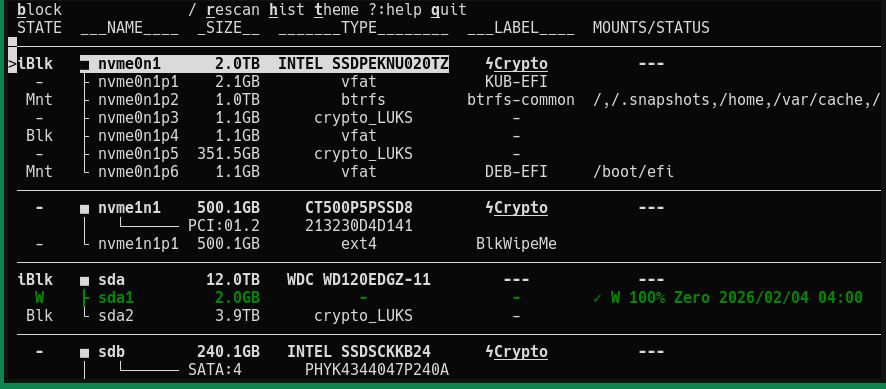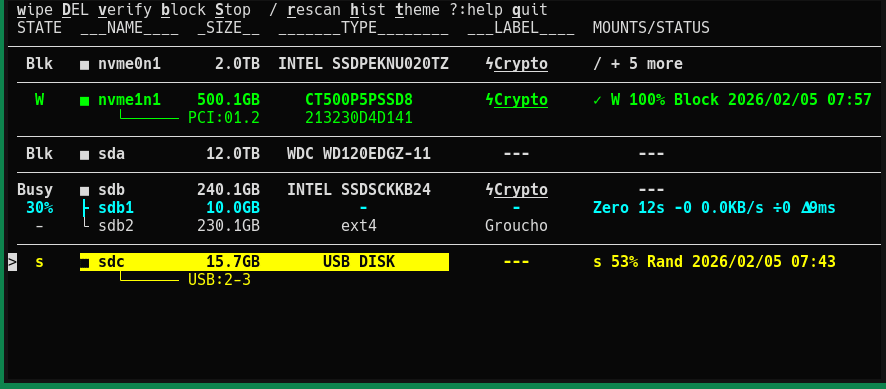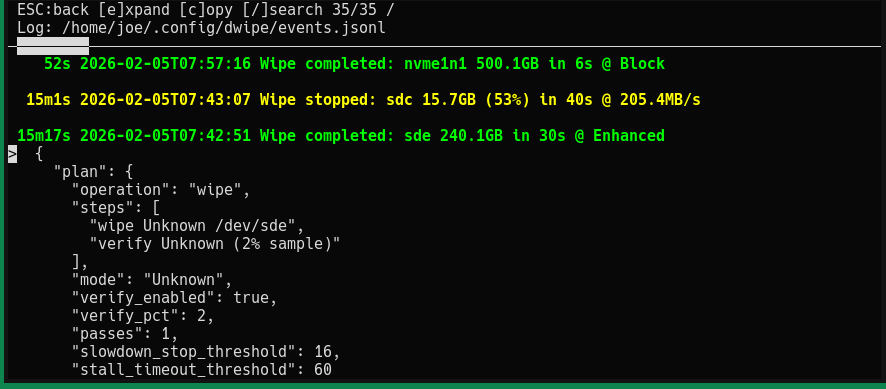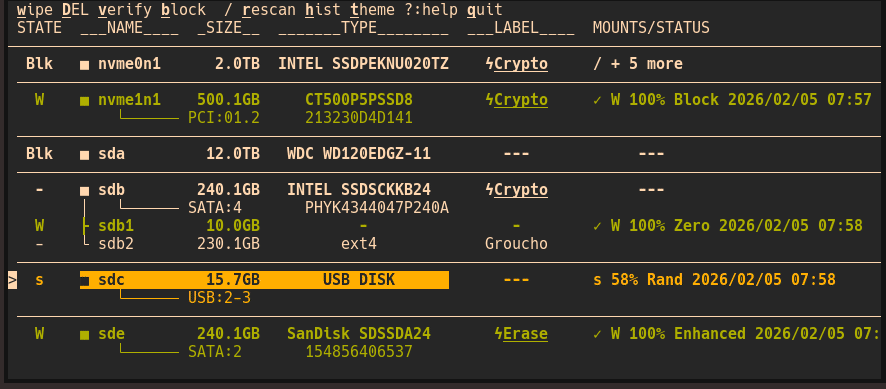 joedefen/dwipe
Tool to securely and efficiently wipe devices and partiitions for Linux