nuitka-static-unpacker

Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.

Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.

Extracts cryptocurrency private keys and addresses from wallet.dat files for Bitcoin and Litecoin, enabling wallet recovery and forensic analysis.

Offset Independent Credential Extraction Tool

Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

Tools and Techniques for Blue Team / Incident Response

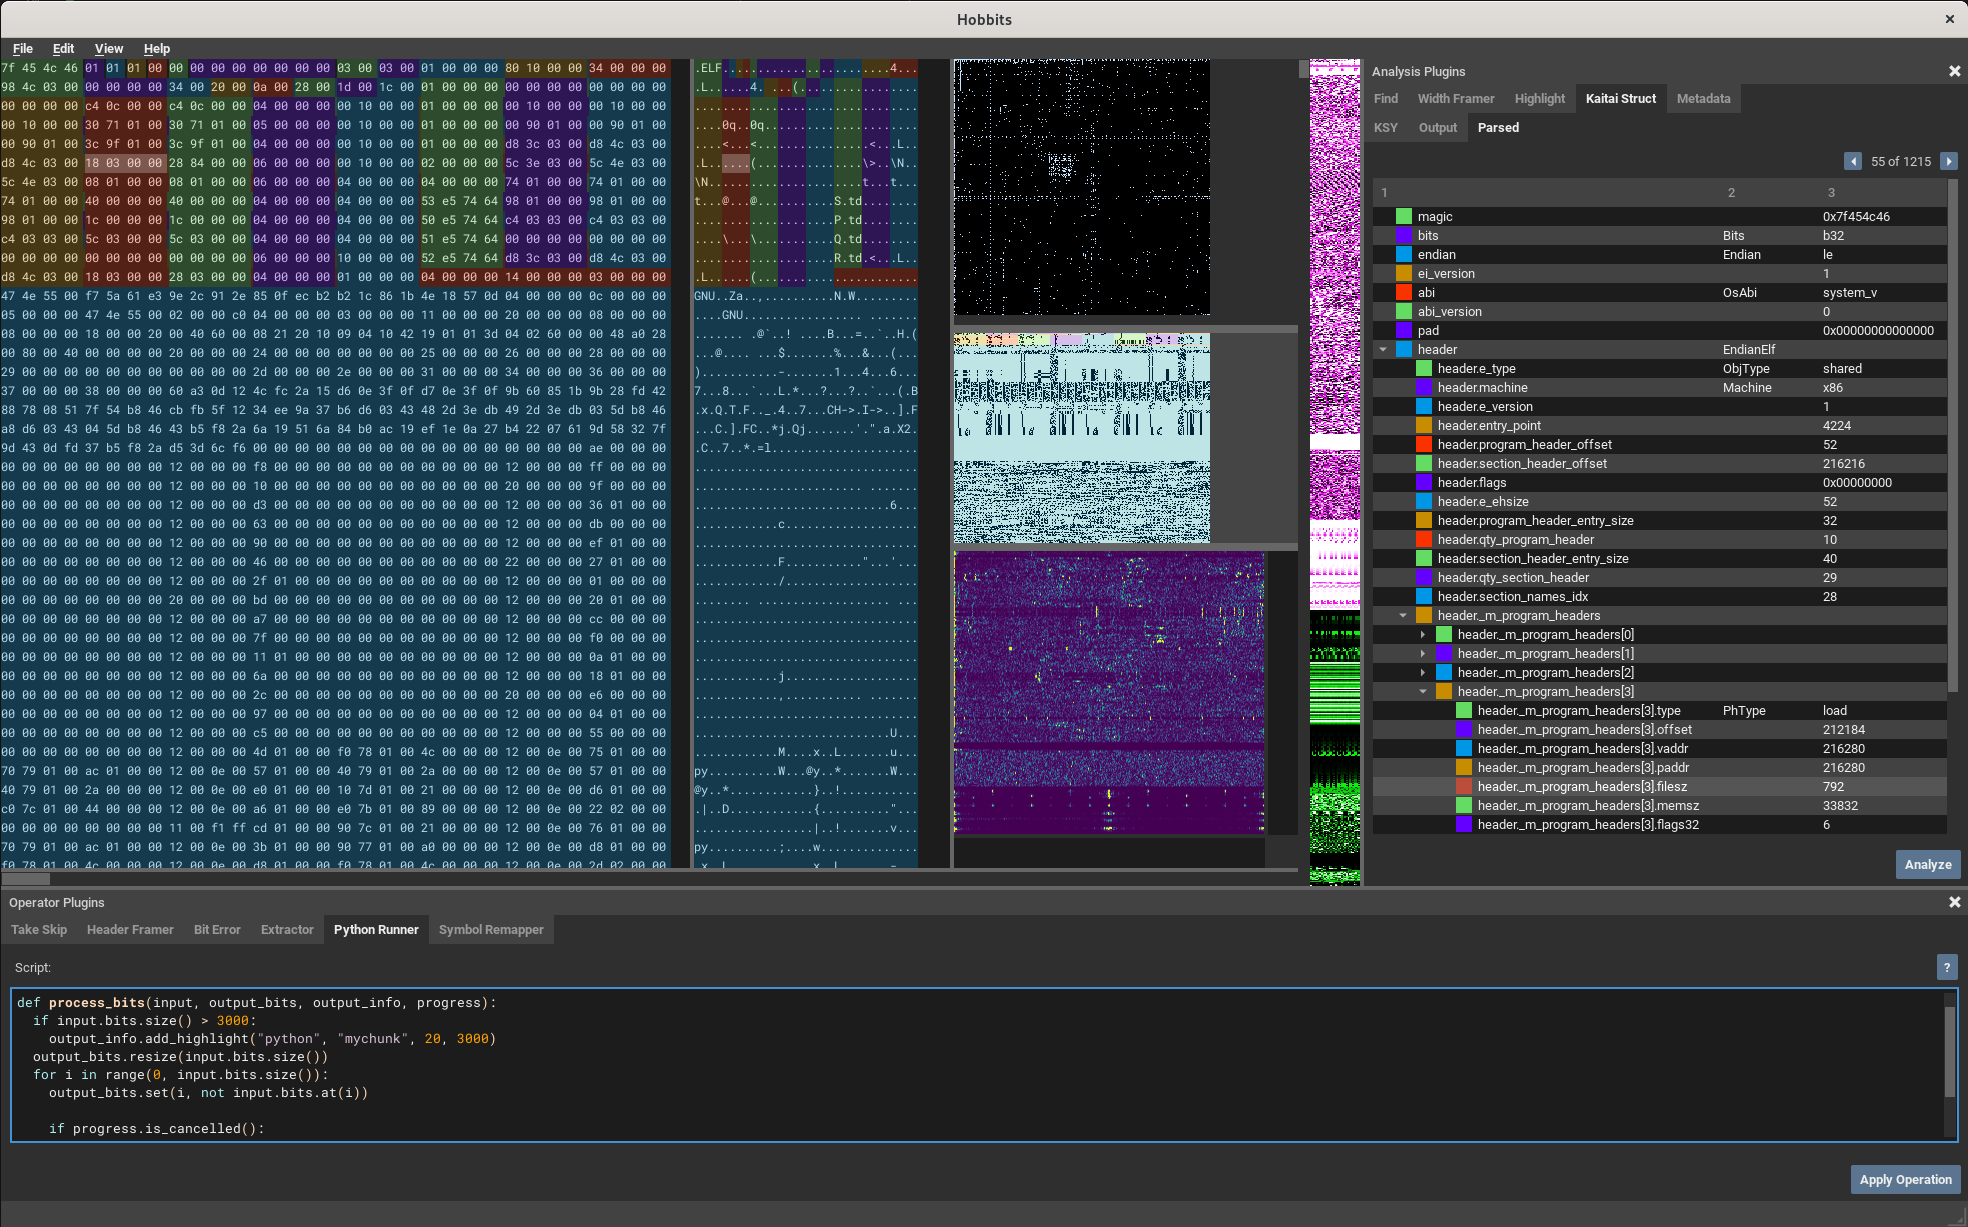
A multi-platform GUI for bit-based analysis, processing, and visualization


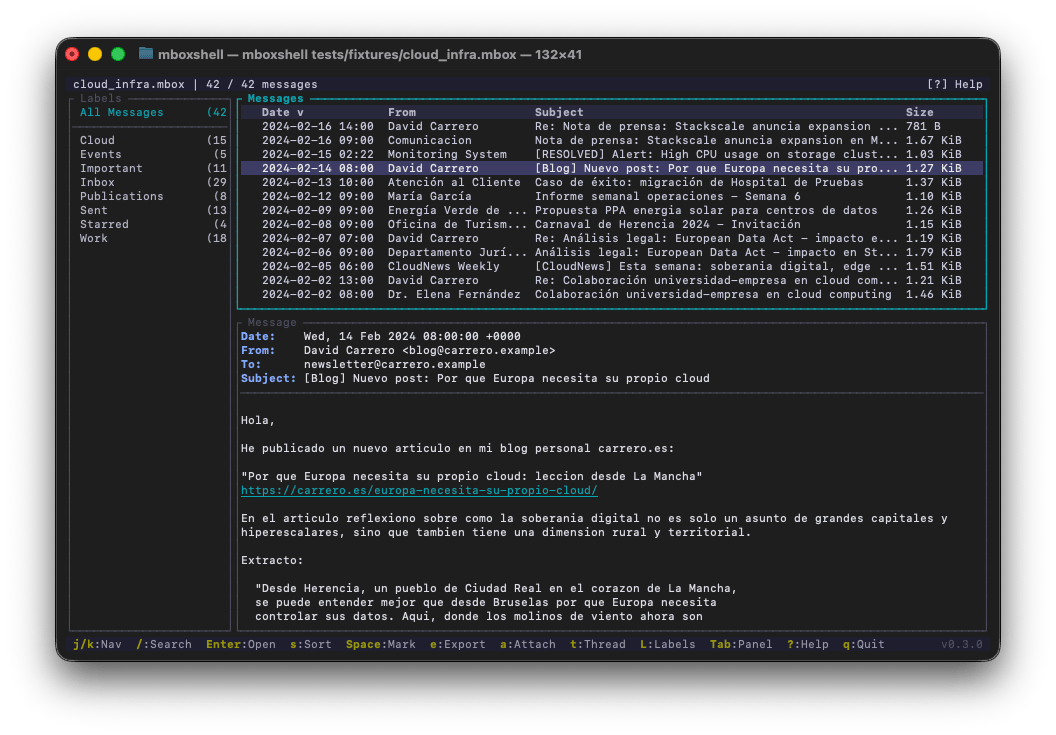
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…

Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…

Cellebrite Physical Analyzer python scripts to aid analysts with extended functionality

This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices

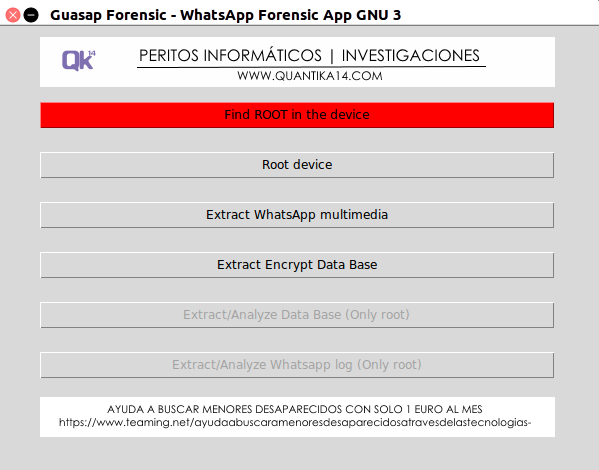
WhatsApp Forensic Tool

Cross-platform hashing toolset for computing message digests (MD5, SHA-1, SHA-256, Tiger, Whirlpool) with recursive directory traversal and file…

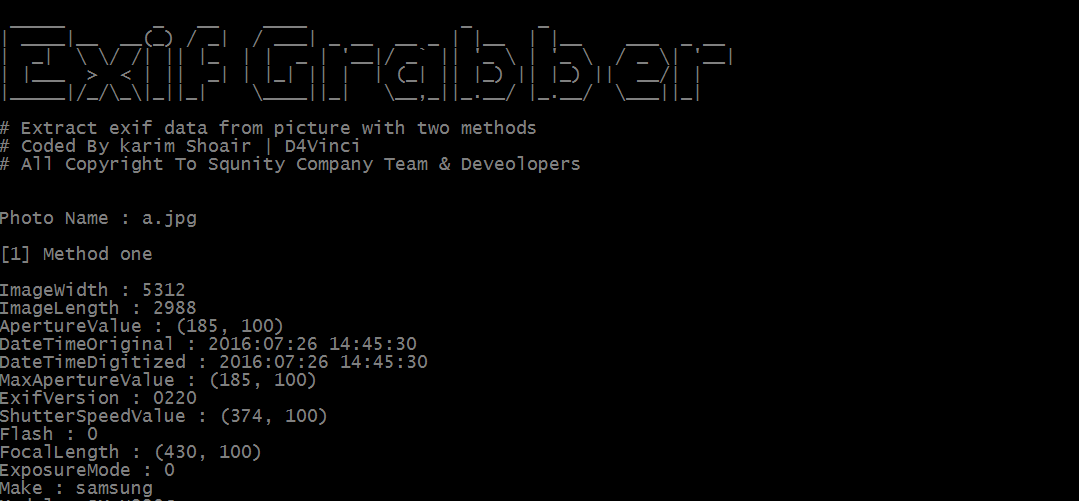
A python tool that will extract exif data from picture with two methods

'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files

A tool to recover from ESXiArgs ransomware

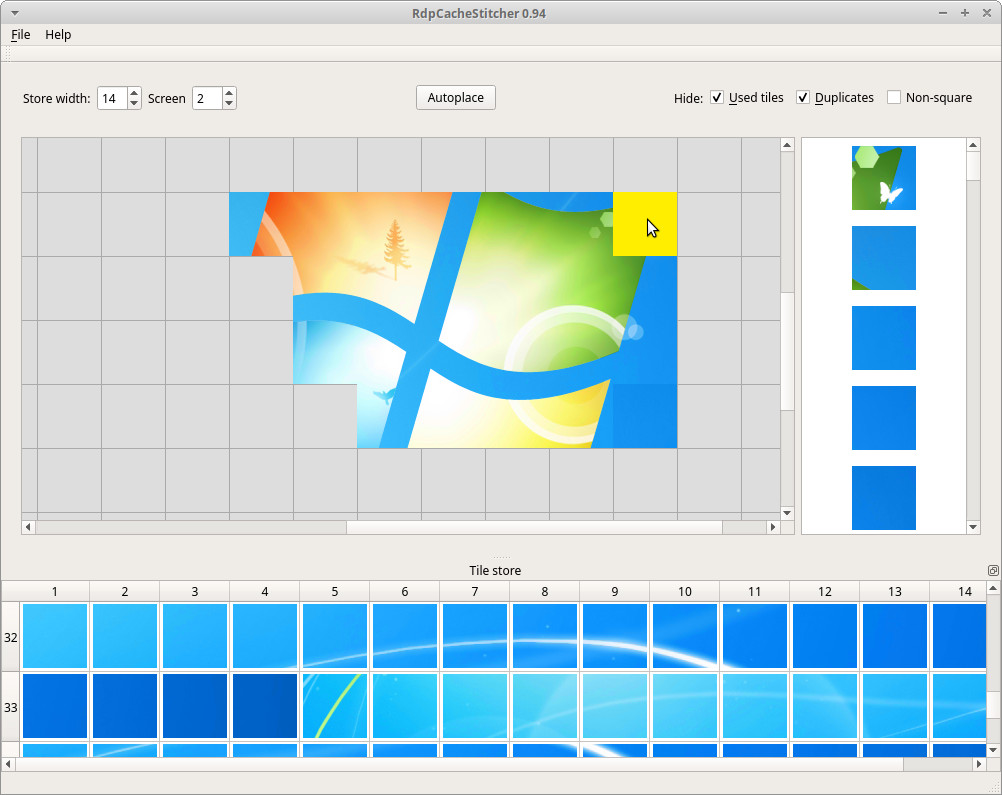
RdpCacheStitcher is a tool that supports forensic analysts in reconstructing useful images out of RDP cache bitmaps.

Crack ios Restriction PassCode in Python