

NtDumpBOF
 deh00ni/ntdumpbof
Cobalt Strike BOF that creates an LSASS minidump in memory and exfiltrates it over the C2 callback for offline credential parsing with Mimikatz or…
data-exfiltrationpost-exploitationred-teaming
deh00ni/ntdumpbofCobalt Strike BOF that creates an LSASS minidump in memory and exfiltrates it over the C2 callback for offline credential parsing with Mimikatz or…
 osintbuddy/web
Entity graphs, OSINT data mining, and plugins. Connect unstructured and public data for transformative insights 🌐 (Web version)
 thestingr/cve-2024-36991-tool
This binary POC automates the exploitation of CVE-2024-36991 by sending crafted curl requests to a vulnerable Splunk instance. It retrieves sensitive…
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 dagowda/notrdp
Havoc C2 plugin that creates a hidden Windows desktop, streams it to a browser viewer, and injects mouse/keyboard input for covert remote control.
 de3vil/stealing
The SteaLinG is an open-source penetration testing framework designed for social engineering
 albertrg99/redditosint
Reddit OSINT by username. Discover indexed posts, comments, deleted and live content, activity patterns, exposed identifiers, and an overall exposure…
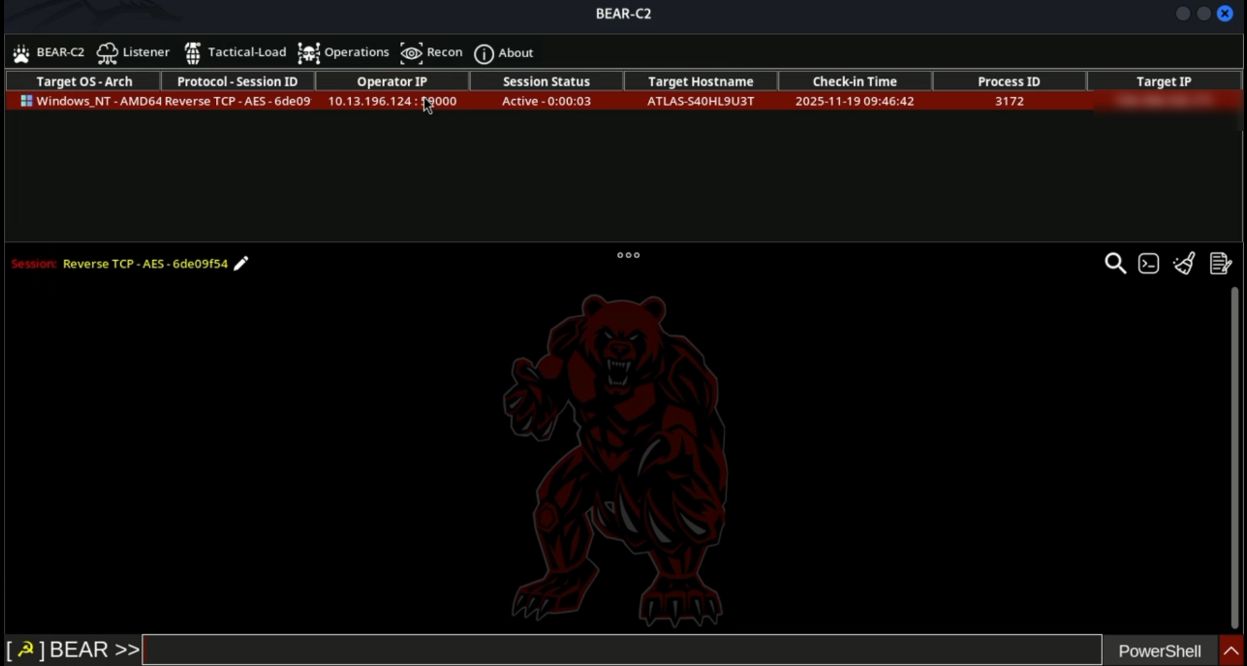
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 s3n4t0r-0x0/pixelcode-attack
Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…
 zolderio/token-proxy
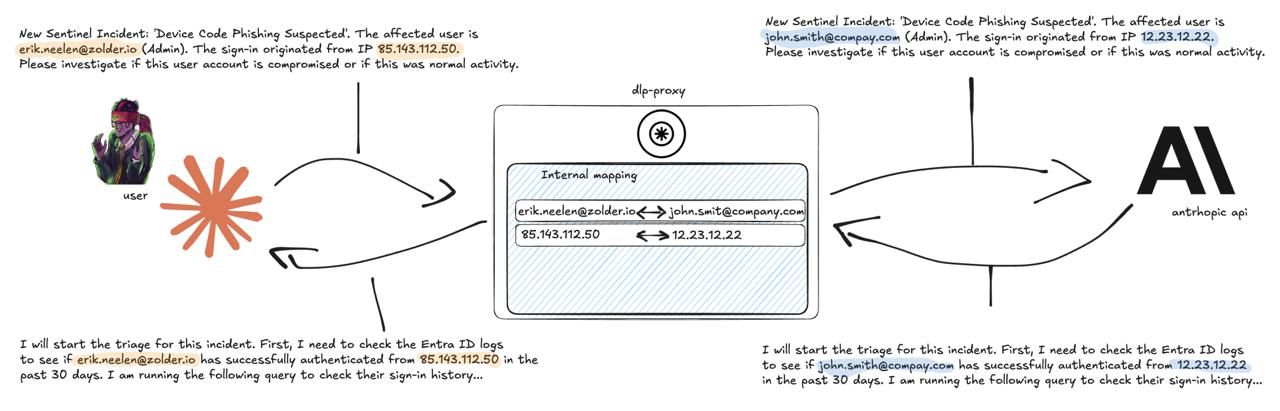
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…
 microsoft/ethr
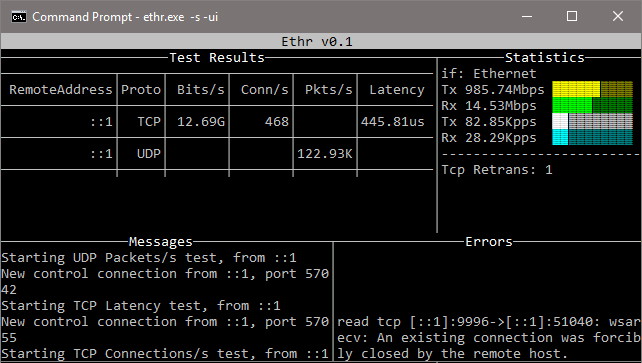
Cross-platform CLI for network performance testing over TCP, UDP, HTTP, HTTPS, and ICMP: bandwidth, connections/s, packets/s, latency, loss, jitter,…
 mustafadalga/wildlogger
This is a keylogger that collects all the data and e-mail it in a set time with system information which includes device S/N and hardware specs,…
 6mile/gimmepatz
Personal Access Token (PAT) recon tool for bug bounty hunters, pentesters & red teams
 abubakarsiddik31/zdr
Curated guide to zero-data-retention configurations for LLM APIs. Covers provider-specific ZDR endpoints, threat models, compliance mappings, and…
 solivaquaant/cve-2026-85706
Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
 graysignal/cve-2024-23897-jenkins-arbitrary-read-file-vulnerability
Unauthenticated Jenkins CLI exploit scanner for CVE-2024-23897 that detects vulnerable versions and reads arbitrary files from the controller through…
 george0papasotiriou/cve-2026-11111-toctou-in-file-permission-check-before-open
Educational CVE PoC for a TOCTOU file-permission race in Flask; uses symlink replacement during the check-open window to disclose sensitive files.
 solivaquaant/cve-2026-85706-poc
PoC for CVE-2026-85706: GitLab CE/EE unauthenticated arbitrary local file read