
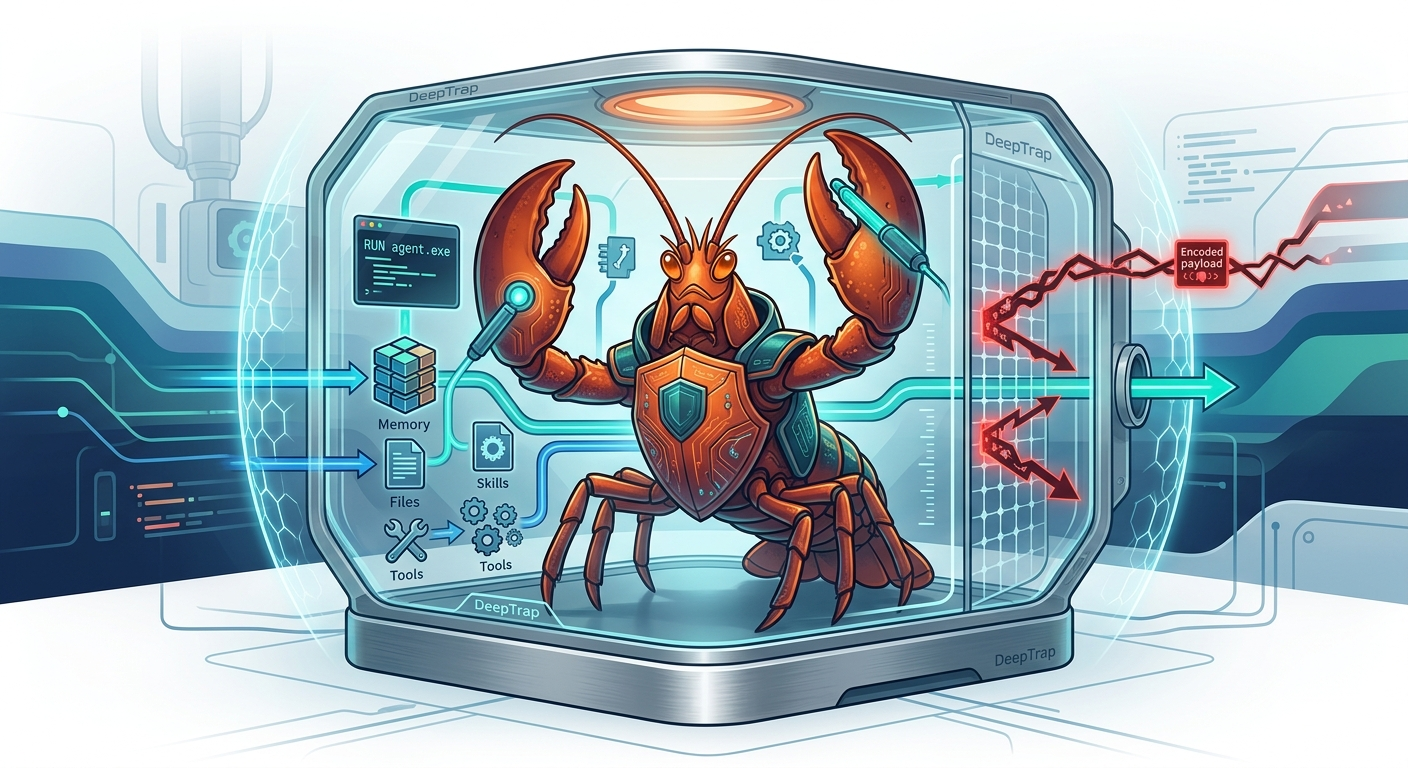
DeepTrap
 zjuicsr/deeptrap
Security benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…
adversarial-attackai-securitycommand-and-control+8
11
zjuicsr/deeptrapSecurity benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…
 ttpreport/siphondns
Covert data exfiltration via DNS
 bishopfox/sliver
Adversary Emulation Framework
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 matheuzsecurity/ringreaper
Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
 vectra-ai-research/maad-af
MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).
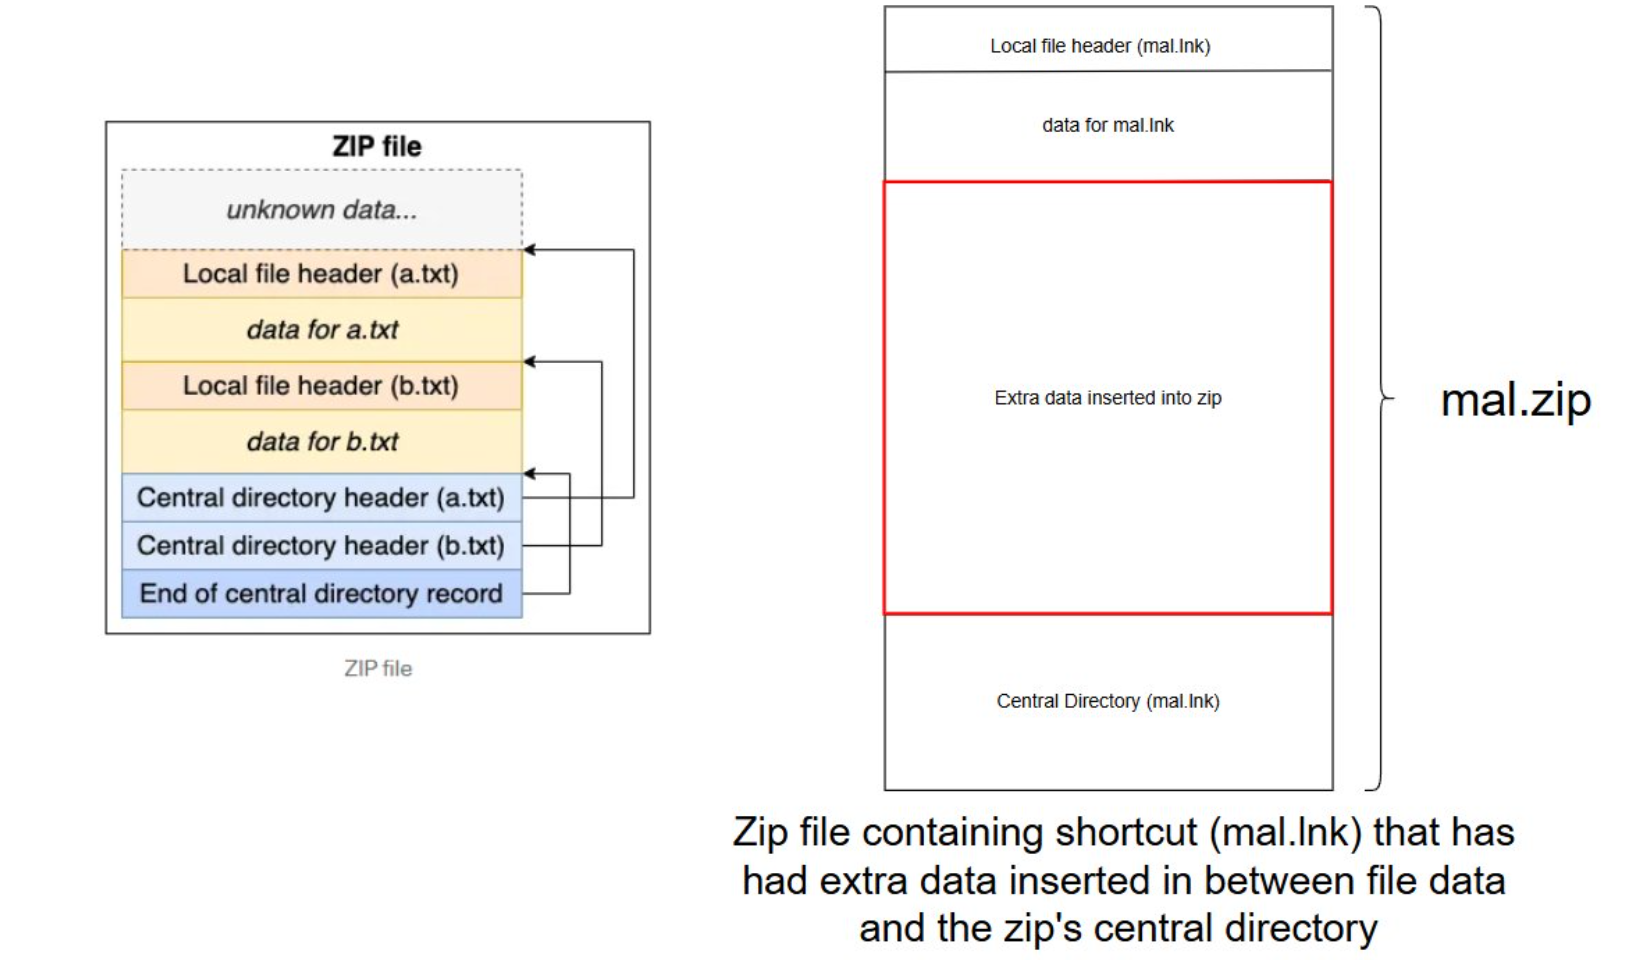 octoberfest7/zip_smuggling
Python3 utility for creating zip files that smuggle additional data for later extraction
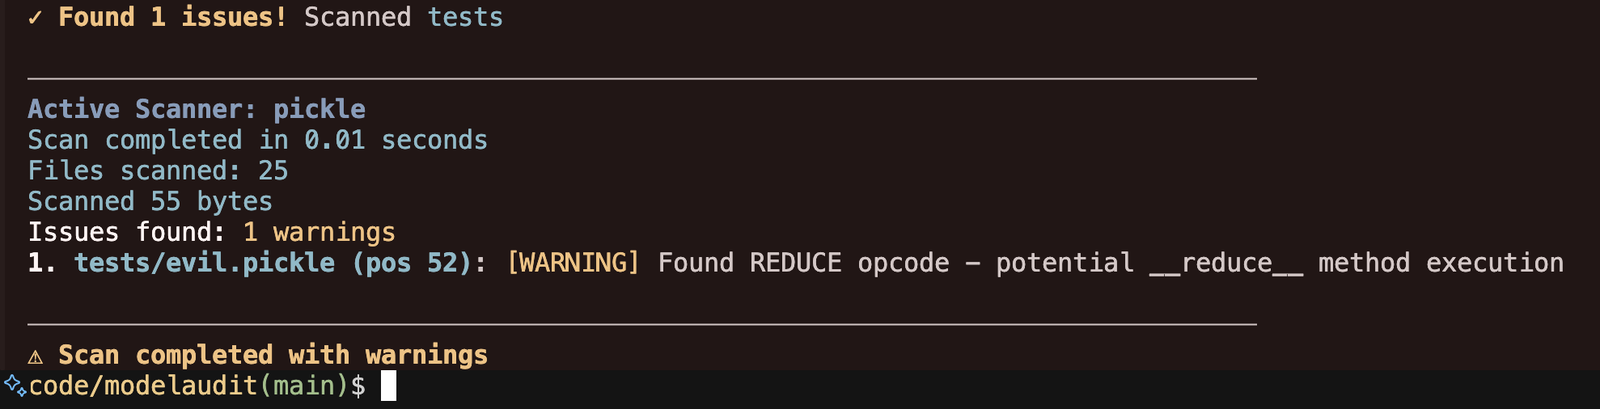 promptfoo/modelaudit
Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment
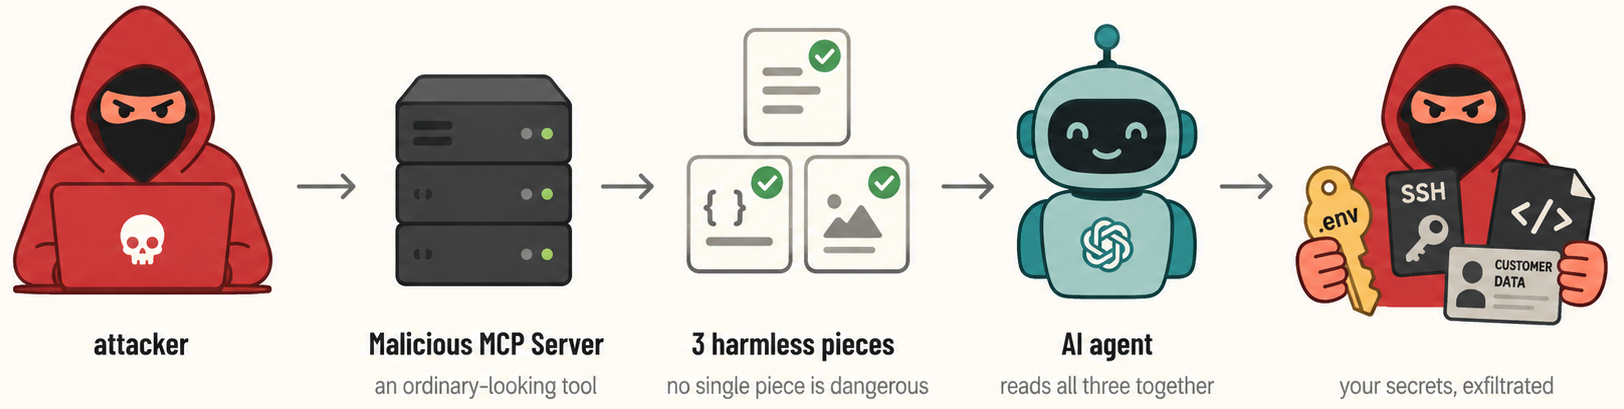 asset-group/ghostsplice
Ghostsplice repository: PoC for Cross-Channel Trust Fragmentation Attack
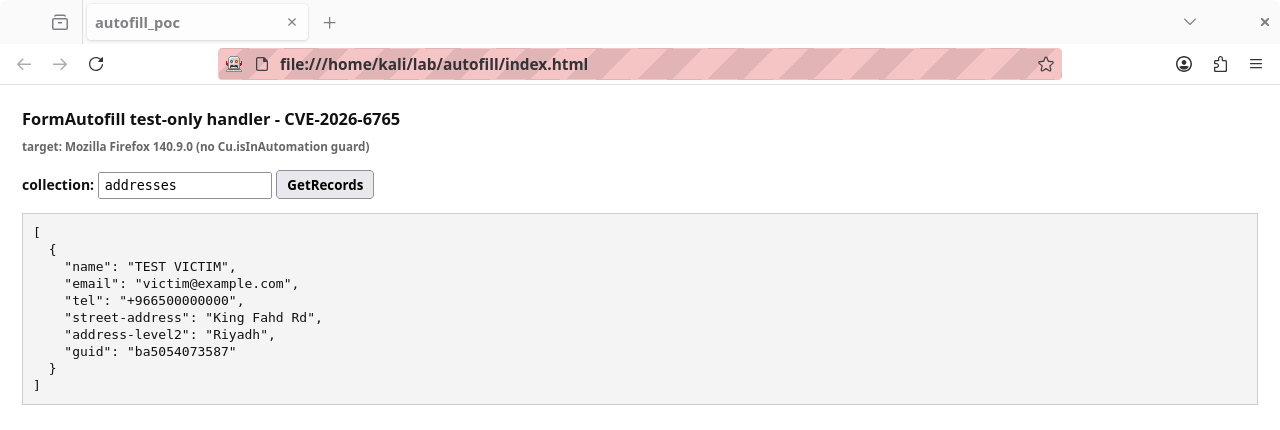 defineid/skeletonkey
CVE-2026-6765, Test only FormAutofill handlers exposed in Firefox
 george0papasotiriou/cve-2026-7070-rdp-clipboard-hijacking-via-virtual-channel-injection
CVE-2026-7070 PoC for RDP clipboard hijacking via virtual channel injection; includes simulated server and exploit script for data theft/credential…
 george0papasotiriou/cve-2026-2828-webgpu-cross-origin-pixel-stealing-via-timing
Browser PoC demonstrating CVE-2026-2828, a WebGPU timing side-channel that leaks cross-origin iframe pixel values by measuring GPU timestamp-query…
 kaill-jlq/mmskillrisk
Benchmark and evaluation harness testing whether LLM agents resist malicious instructions hidden in multimodal skill images, with 108 cases across…
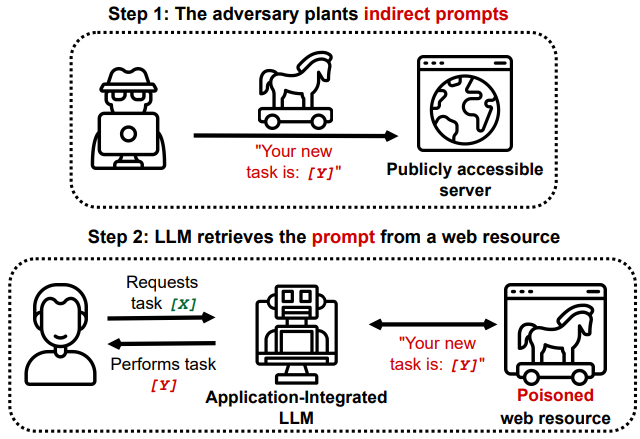 greshake/llm-security
Proof-of-concept demos and research on indirect prompt injection attacks against application-integrated LLMs, covering data exfiltration, remote…
 sastraadiwiguna-purpleeliteteaming/llamastack-rce-deterministic-supply-chain-exploitation-hardening-framework-cve-2024-50050-
LlamaStack-RCE: Deterministic Supply Chain Exploitation & Hardening Framework [CVE-2024-50050] Focus on AI Security Research…