

PPLBlade
 tastypepperoni/pplblade
Bypasses PPL protection to dump LSASS process memory, obfuscates dump files with XOR, and exfiltrates them remotely via RAW or SMB without writing to…
data-exfiltrationexploitationmemory-forensics+2
602
tastypepperoni/pplbladeBypasses PPL protection to dump LSASS process memory, obfuscates dump files with XOR, and exfiltrates them remotely via RAW or SMB without writing to…
 0xdak/cve-2026-69083_exploit
Python PoC for CVE-2026-69083, an unauthenticated SQL injection in SiYuan's asset-content search endpoint. Supports REGEXP breakout and raw SQL…
 ekultek/whatbreach
OSINT tool to find breached emails, databases, pastes, and relevant information
 bluepigeonproject/blue-pigeon
Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a…
 prodefense/hawk
Golang tool designed to exfiltrate passwords found via the sshd and su services
 ustayready/golddigger
Recursively searches files for sensitive information using customizable regex patterns, designed for penetration testers to rapidly discover secrets…
 moloch--/leakdb
Web-Scale NoSQL Idempotent Cloud-Native Big-Data Serverless Plaintext Credential Search
 brittonhayes/pillager
Pillage filesystems for sensitive information with Go 🔍
 an00byss/godehashed
A golang tool that uses the dehashed.com API to search for compromised assets.
 infosecn1nja/veiltransfer
VeilTransfer is a data exfiltration utility designed to test and enhance the detection capabilities. This tool simulates real-world data exfiltration…
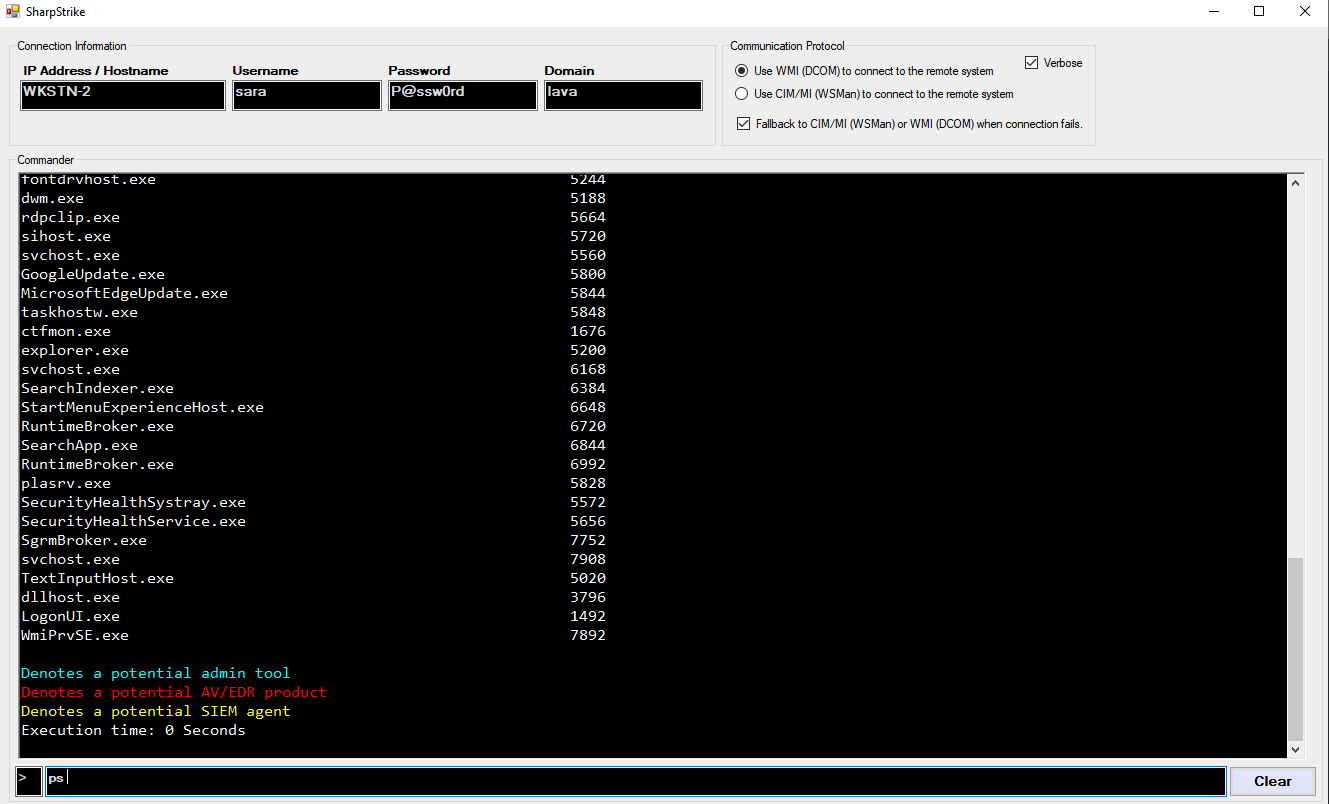 iomoath/sharpstrike
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.
 jacopodl/pulsar
Data exfiltration and covert communication tool
 sromanhu/totalcms-arbitrary_file-upload--xss_steal_cookies---totaldepot
TotalCMS is affected by Arbitrary File Upload - XSS vulnerability which allows Cross-Site Scriting (XSS) Stored and also stealing session cookies
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 jnschaeffer/cve-2022-44268-detector
Detect images that likely exploit CVE-2022-44268
 ejfkdev/oss
Cross-cloud S3-compatible object storage CLI to list, export, and download buckets across AWS, Aliyun, Tencent, Huawei and more, with anonymous…
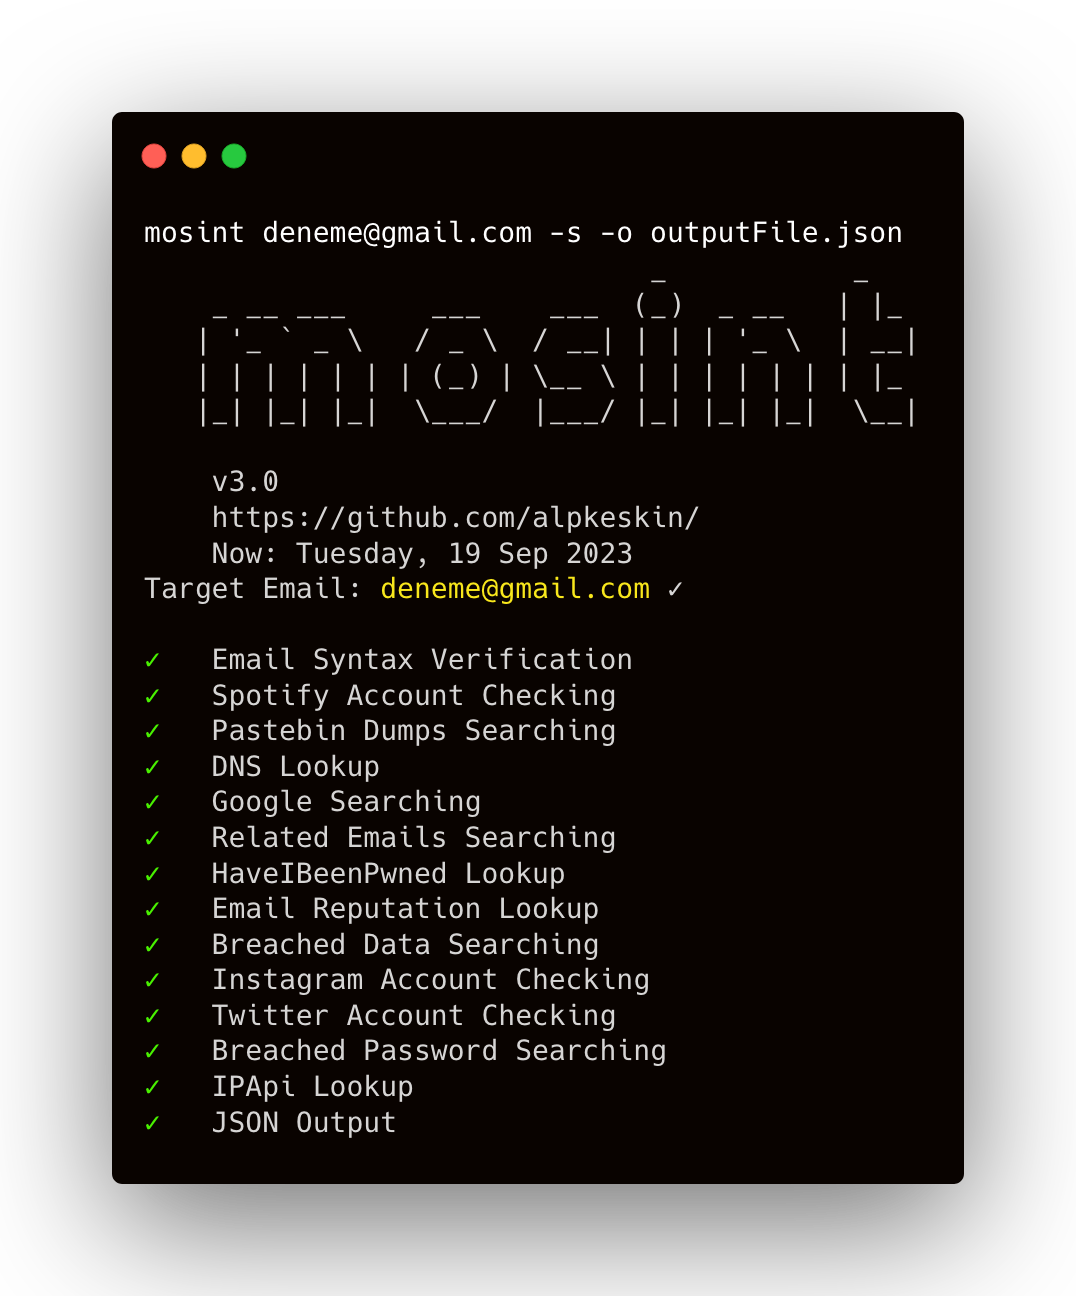 alpkeskin/mosint
Automated email OSINT tool that verifies emails, checks data breaches and password leaks, finds related emails/domains, scans pastebin dumps, and…
 gagaltotal/cve-2026-85706-gitlab-poc
Go exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE Workhorse via URL-encoding bypass, with concurrent requests and…