CVE-2026-3333-DNS-Rebinding-to-Steal-Cloud-Metadata

Python exploit for CVE-2026-3333 demonstrating DNS rebinding to access cloud metadata and steal IAM credentials through an SSRF-vulnerable web app.

Python exploit for CVE-2026-3333 demonstrating DNS rebinding to access cloud metadata and steal IAM credentials through an SSRF-vulnerable web app.

A privacy and security engineering toolkit: Discover, understand, pseudonymize, anonymize, encrypt and securely share sensitive and personal data:…

Default Detections for EDR

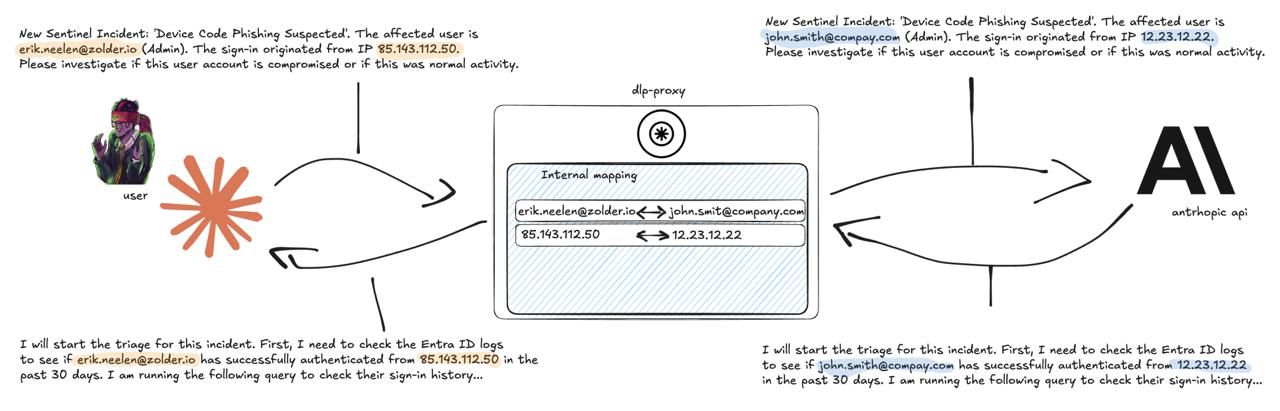
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…

An at-rest encrypted filesharing application with multiple clients who seek to share privately, without tracking.

This Proof of Concept (PoC) demonstrates an exploit for CVE-2024-42009, leveraging a cross-site scripting (XSS) vulnerability to extract emails from…

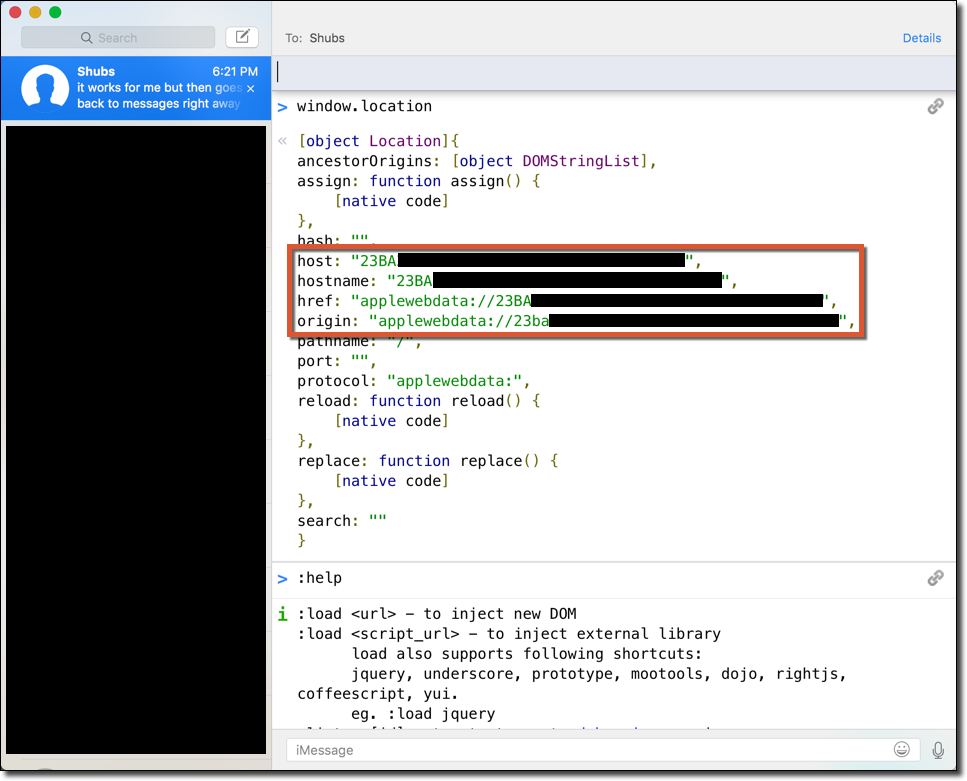
Extraction of iMessage Data via XSS