
pwnlift
 rasta-mouse/pwnlift
Easy peasy file uploads
data-exfiltrationpenetration-testingremote-access-tool+2
423 months ago
rasta-mouse/pwnliftEasy peasy file uploads
 connectedlucy/plague
Default Detections for EDR
 fleralex/enseal
Secure, ephemeral secret sharing for developers.
 legendile7/cve-2026-78122-poc
Proof-of-concept exploit for CVE-2026-78122, demonstrating container filesystem and environment variable exfiltration through docker-socket-proxy's…
 kiprotect/kodex
A privacy and security engineering toolkit: Discover, understand, pseudonymize, anonymize, encrypt and securely share sensitive and personal data:…
 gradiant/faro
FARO - Document Sensitivity Detector
 blue0x1/sqlwinds
SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit
 bande-a-bonnot/boucle-framework
Autonomous agent framework with structured memory, safety hooks, and loop management. Built by the agent that runs on it.
 incidedigital/mistica
An open source swiss army knife for arbitrary communication over application protocols
 jimywork/cromos
Cromos is a tool for downloading legitimate extensions of the Chrome Web Store and inject codes in the background of the application.
 designativedave/androrat
Remote Administration Tool for Android devices

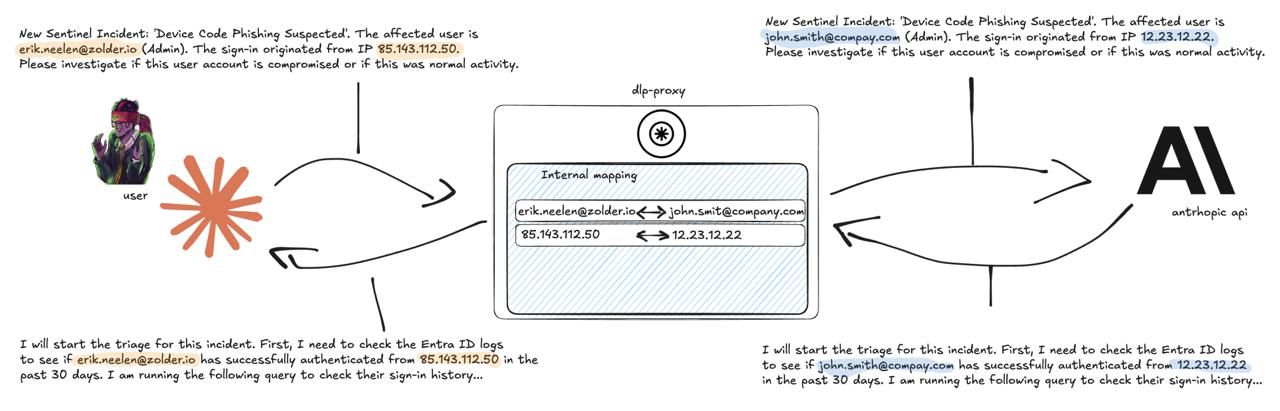 zolderio/token-proxy
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…
 bhanunamikaze/cve-2024-42009
This Proof of Concept (PoC) demonstrates an exploit for CVE-2024-42009, leveraging a cross-site scripting (XSS) vulnerability to extract emails from…
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 george0papasotiriou/cve-2026-3333-dns-rebinding-to-steal-cloud-metadata
Python exploit for CVE-2026-3333 demonstrating DNS rebinding to access cloud metadata and steal IAM credentials through an SSRF-vulnerable web app.
 george0papasotiriou/cve-2026-21015-php-filter-chain-arbitrary-file-read
PoC exploit for CVE-2026-21015 that abuses PHP filter chains to read arbitrary files through a vulnerable include() call, disclosing source and…
 george0papasotiriou/cve-2026-21004-sqlite-fts3-match-infoleak-via-query-crafting
Proof-of-concept exploit for CVE-2026-21004: uses crafted SQLite FTS3/4 MATCH prefix queries as a blind oracle to recover indexed secret data…