
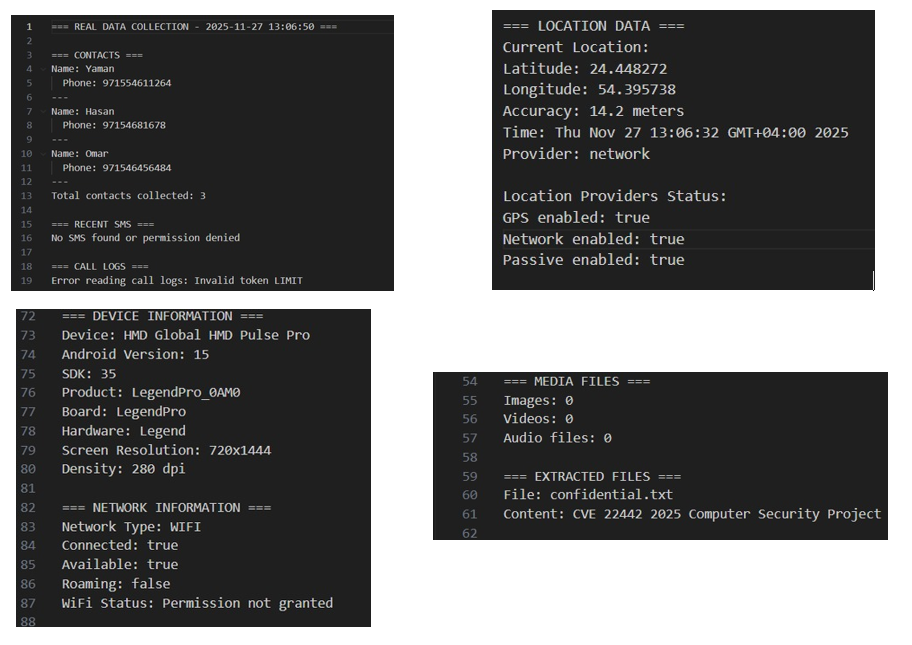
android-workprofile-exploit
 hasan-al-hussein/android-workprofile-exploit
Controlled defensive analysis of CVE-2025-22442 work-profile provisioning, policy timing, and enterprise isolation.
android-securitydata-exfiltrationeducation+5
1
hasan-al-hussein/android-workprofile-exploitControlled defensive analysis of CVE-2025-22442 work-profile provisioning, policy timing, and enterprise isolation.
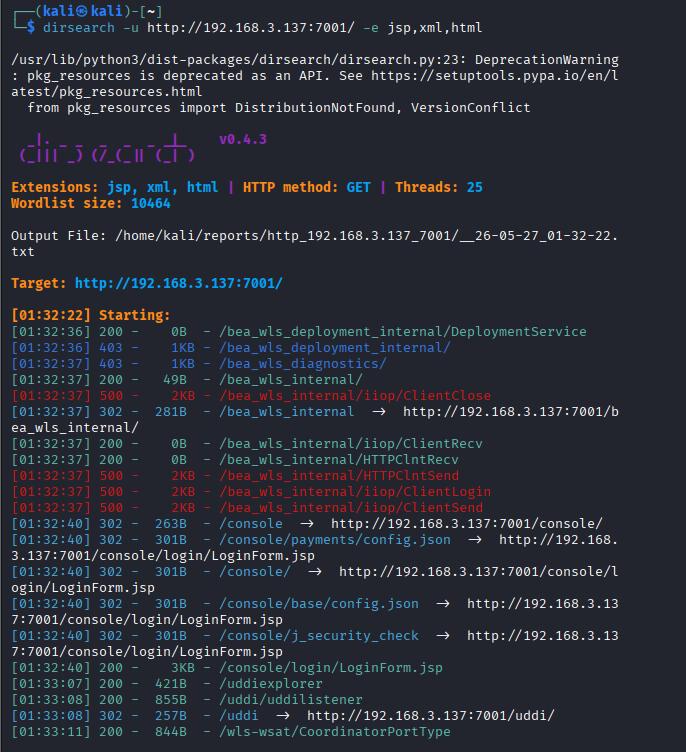 dungsocool/cve-2017-10271
Step-by-step lab guide for exploiting CVE-2017-10271 (WebLogic XMLDecoder deserialization RCE) with manual payload construction, blind RCE bypass,…
 1amunvalid/cve-2025-10951
Proof-of-concept checker for CVE-2025-10951, an unauthenticated path traversal in ml-logger, validating arbitrary file read via /glob and /stream…
 hazavvip/cve-2025-30208
Exploit scanner for CVE-2025-30208 (Vite arbitrary file read) with multi-variant bypass detection, credential harvesting, SSH key extraction, and…
 5ky9uy/glass-cage-i18-2025-24085-and-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, exploiting WebKit (CVE-2025-24201) and Core Media (CVE-2025-24085) to achieve sandbox…
 alexcyberx/cve-2025-14847_expolit
Exploit tool for CVE-2025-14847, a MongoDB memory disclosure vulnerability, enabling multi-threaded extraction of sensitive data and secrets from…
 wiliam227user/cve-2018-12633-tplink-auth-bypass
A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).
 honestcorrupt/phonepe-sensitive-data-exposure-cve-2025-5154
CVE-2025-5154: Proof-of-concept for unencrypted local storage of authentication tokens, PII, and KYC data in the PhonePe Android app, enabling…
 a1ex-var1amov/ctf-cve-2019-11043
Intentionally vulnerable PHP app with Nginx/PHP-FPM setup for reproducing CVE-2019-11043, including Docker and Kubernetes deployment,…
 julio-cfa/poc-es-file-explorer-cve-2019-6447
Bash PoC script exploiting CVE-2019-6447 in ES File Explorer to list files, photos, videos, apps, and download files from vulnerable Android devices.
 roj1py/cve-2024-47875-phpspreadsheet-xss-poc
This is a PoC/Exploit for the CVE-2024-47875 PhpSpreadsheet XSS Vuln
 michaeladamgroberman/cve-2025-10681
CVE-2025-10681: Hardcoded Azure Blob Storage Account Key — Gardyn Home Kit (ICSA-26-055-03)
 yusufdalbudak/cve-2025-32965-xrpl-js-poc
CVE Kodu: CVE-2025-32965 Zafiyet Türü: Supply Chain Attack (CWE-506: Embedded Malicious Code) Hedef: xrpl.js kütüphanesinin 4.2.1–4.2.4 ve 2.14.2…
 ifpdz/cve-2025-24104
Technical writeup of CVE-2025-24104: an iOS sandbox escape via symlink validation bypass in backup restoration, enabling arbitrary file reads outside…
 cybertechajju/cve-2025-14847_expolit
a critical memory disclosure vulnerability in MongoDB's zlib compression handling. This tool allows security researchers to extract sensitive data…
 danielossai12/aisecplus-week01-danielossai
AISec Plus Week 1 threat write-up — EchoLeak (CVE-2025-32711), zero-click indirect prompt injection in Microsoft 365 Copilot.
 scumfrog/fiberbreak
React2Shell Exploitation Tool (CVE-2025-55182)
 hexbornestudio/atlas-tj-actions-poc
PoC for CVE-2025-54416 tj-actions/branch-names command injection