
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
178 results
loki-parse preview

loki-parse

GitHubr3mrum/loki-parse

A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…
data-exfiltrationdigital-forensicsforensics+5
13
9 years ago
njRAT preview

njRAT

GitHubmwsrc/njrat

njRAT SRC Extract

command-and-controldata-exfiltrationexploitation+9
3159 years ago
R2Socks preview

R2Socks

GitHubivancabrera02/r2socks

SOCKS5 proxy tunneled through Cloudflare R2 object storage, with Python and dependency-free C++ agents relaying TCP traffic via encrypted R2 objects…
command-and-controldata-exfiltrationencryption-decryption-tools+5
381 month ago
SharpGmailC2 preview

SharpGmailC2

GitHubreveng007/sharpgmailc2

Our Friendly Gmail will act as Server and implant will exfiltrate data via smtp and will read commands from C2 (Gmail) via imap protocol
command-and-controldata-exfiltrationpost-exploitation+2
2651 year ago
secret_handshake preview

secret_handshake

GitHubjconwell/secret_handshake

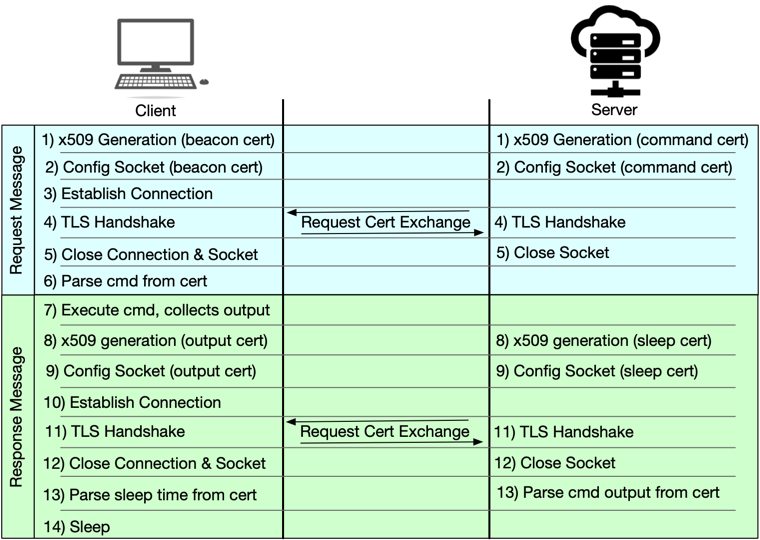
A prototype malware C2 channel using x509 certificates over mTLS
command-and-controldata-exfiltrationids-ips-evasion+1
1532 years ago
teletunnel preview

teletunnel

GitHubmhdgning131/teletunnel

Bypassing EDR's with stealthy c++ telegram Bot and Telegram itself as C2 interface !
command-and-controldata-exfiltrationids-ips-evasion+7
446 months ago
antnium preview
Archived

antnium

GitHubdobin/antnium

A C2 framework for initial access in Go

command-and-controldata-exfiltrationpayload-development+3
1994 years ago
GodGenesis preview

GodGenesis

GitHubsaumyajeetdas/godgenesis

A Python3 based C2 server to make life of red teamer a bit easier. The payload is capable to bypass all the known antiviruses and endpoints.
command-and-controldata-exfiltrationinformation-gathering+5
5332 years ago
JS-Tap preview

JS-Tap

GitHubhoodoer/js-tap

JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
command-and-controldata-exfiltrationinformation-gathering+8
4823 months ago
NorthStarC2 preview

NorthStarC2

GitHubeng1ndes/northstarc2

Web Based Command Control Framework (C2) #C2 #PostExploitation #CommandControl #RedTeam #C2Framework #PHPC2 #.NETMalware #Malware #PHPMalware #CnC…

command-and-controldata-exfiltrationinformation-gathering+6
2672 years ago
notRDP preview

notRDP

GitHubdagowda/notrdp

Havoc C2 plugin that creates a hidden Windows desktop, streams it to a browser viewer, and injects mouse/keyboard input for covert remote control.

command-and-controldata-exfiltrationimpersonation-tools+6
2349 days ago
gh0st3.6_src preview

gh0st3.6_src

GitHubigh0st/gh0st3.6_src

Remote Access Trojan (RAT) source code for learning C2 communication, payload delivery, and post-exploitation techniques in Windows environments.

command-and-controldata-exfiltrationpayload-development+3
17012 years ago
peeko preview

peeko

GitHubb3rito/peeko

peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
command-and-controldata-exfiltrationinformation-gathering+7
2331 year ago
DCVC2 preview

DCVC2

GitHub3nailsinfosec/dcvc2

Discord voice channel C2 framework for covert command and control operations. Transmits all data via RTP packets over voice channels, leaving no…
command-and-controldata-exfiltrationpayload-development+2
1311 year ago
SliverKeylogger preview

SliverKeylogger

GitHubtrustedsec/sliverkeylogger

Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…

command-and-controldata-exfiltrationpayload-development+2
1723 years ago
SharpCovertTube preview

SharpCovertTube

GitHubricardojoserf/sharpcoverttube

Youtube as C2 channel - Control Windows systems uploading QR videos to Youtube
command-and-controldata-exfiltrationeducation+4
1022 years ago
Phoenix-Framework preview

Phoenix-Framework

GitHubxm0kht4r/phoenix-framework

Post-exploitation framework that abuses trusted sites like Telegram and Discord for C2.
command-and-controldata-exfiltrationpayload-development+5
695 months ago
RedDrop preview

RedDrop

GitHubcyberbutler/reddrop

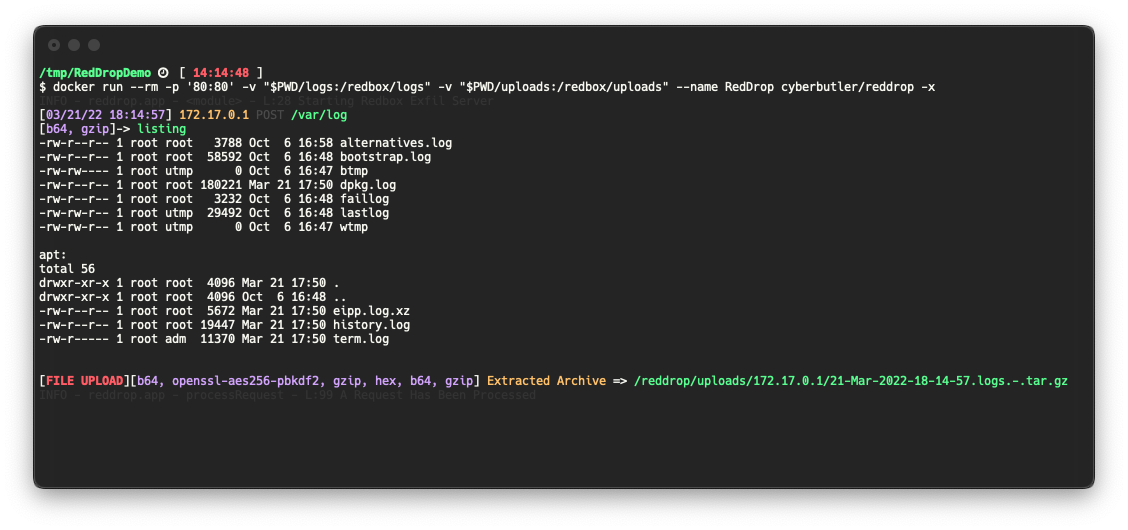
Python Flask web server for capturing, processing, and logging encoded/encrypted payloads and tar archives, designed for penetration testers and red…

command-and-controldata-exfiltrationpayload-generation+2
581 year ago
Previous12…10Next