
Sleipnir
 nccgroup/sleipnir
Tiny payload for transfer via LOKI - Provides high speed Virtual Channel two way file transfer capabilities
data-exfiltrationpayload-developmentpenetration-testing+1
27
nccgroup/sleipnirTiny payload for transfer via LOKI - Provides high speed Virtual Channel two way file transfer capabilities
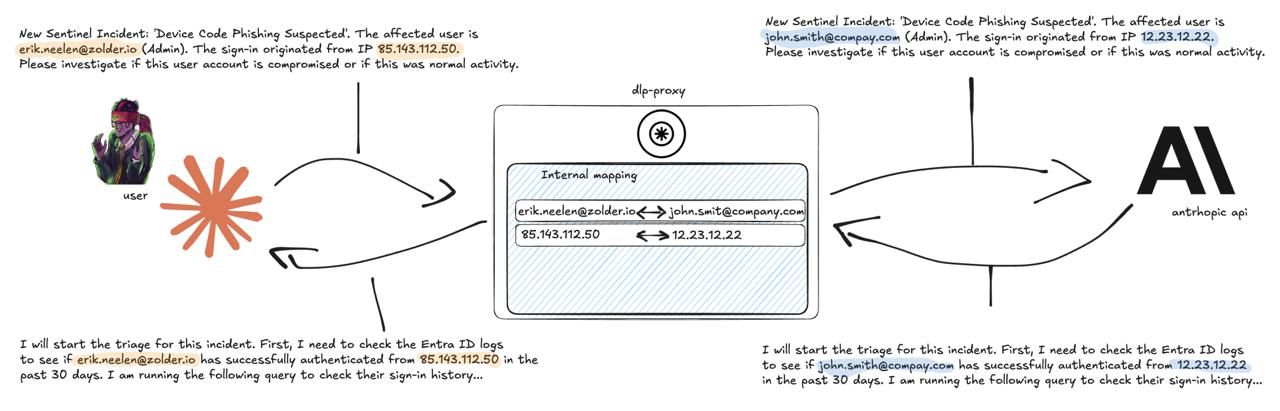 zolderio/token-proxy
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…
 pgedge/pgedge-anonymizer
An anonymizer tool for replacing PII and similar data in dev/test databases copied from production
 invicti-security/web-inf-path-trav
Tool for helping in the exploitation of path traversal vulnerabilities in Java web applications
 mhtsec/cve-2026-85706
Python PoC for CVE-2026-85706, an unauthenticated path traversal in GitLab CE/EE Repository Commits API that leaks arbitrary local files via a…
 kira2040k/redbloodc2
Node.js command-and-control server with FUD payload generation, encrypted communication, session management, and modules for data exfiltration and…
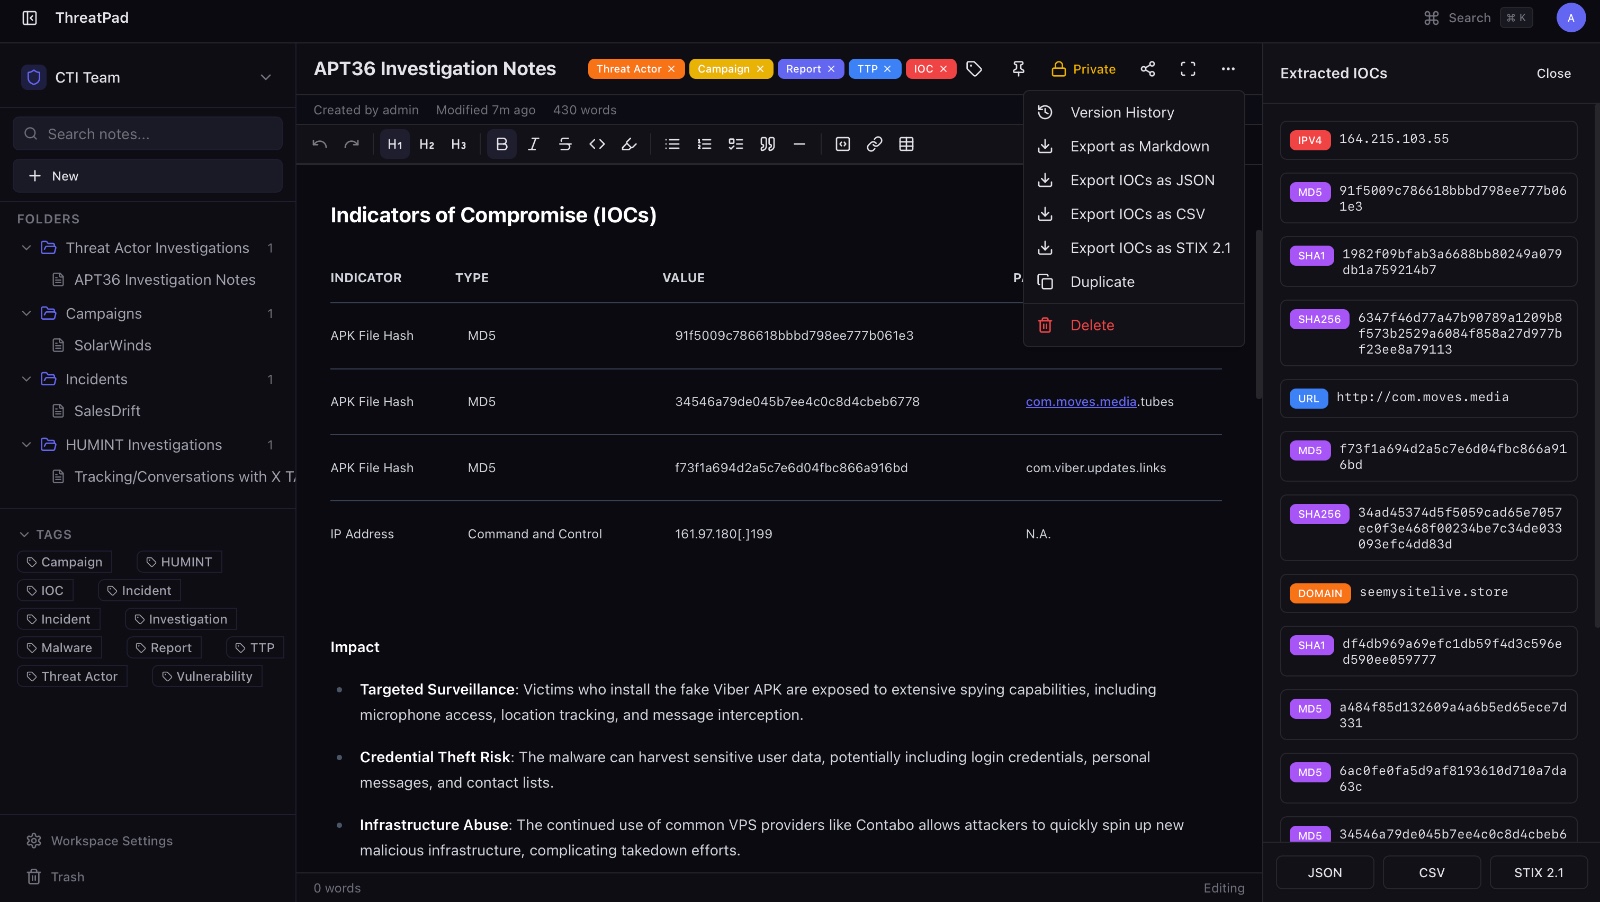 bhavikmalhotra/threatpad
Open-source collaborative note-taking platform for cybersecurity and CTI teams. IOC auto-extraction, STIX 2.1 export, real-time editing, RBAC,…
 b1ack0wl/miniupnpd_poc
Read out-of-bounds PoC for miniupnpd <= v2.1
 agentshield-ai/sigma-ai
Sigma detection rules for AI agent security monitoring
 abubakarsiddik31/zdr
Curated guide to zero-data-retention configurations for LLM APIs. Covers provider-specific ZDR endpoints, threat models, compliance mappings, and…
 taurusomar/pulsegram
Python-based keylogger with Telegram bot integration for capturing keystrokes, clipboard content, and screenshots in authorized security testing…
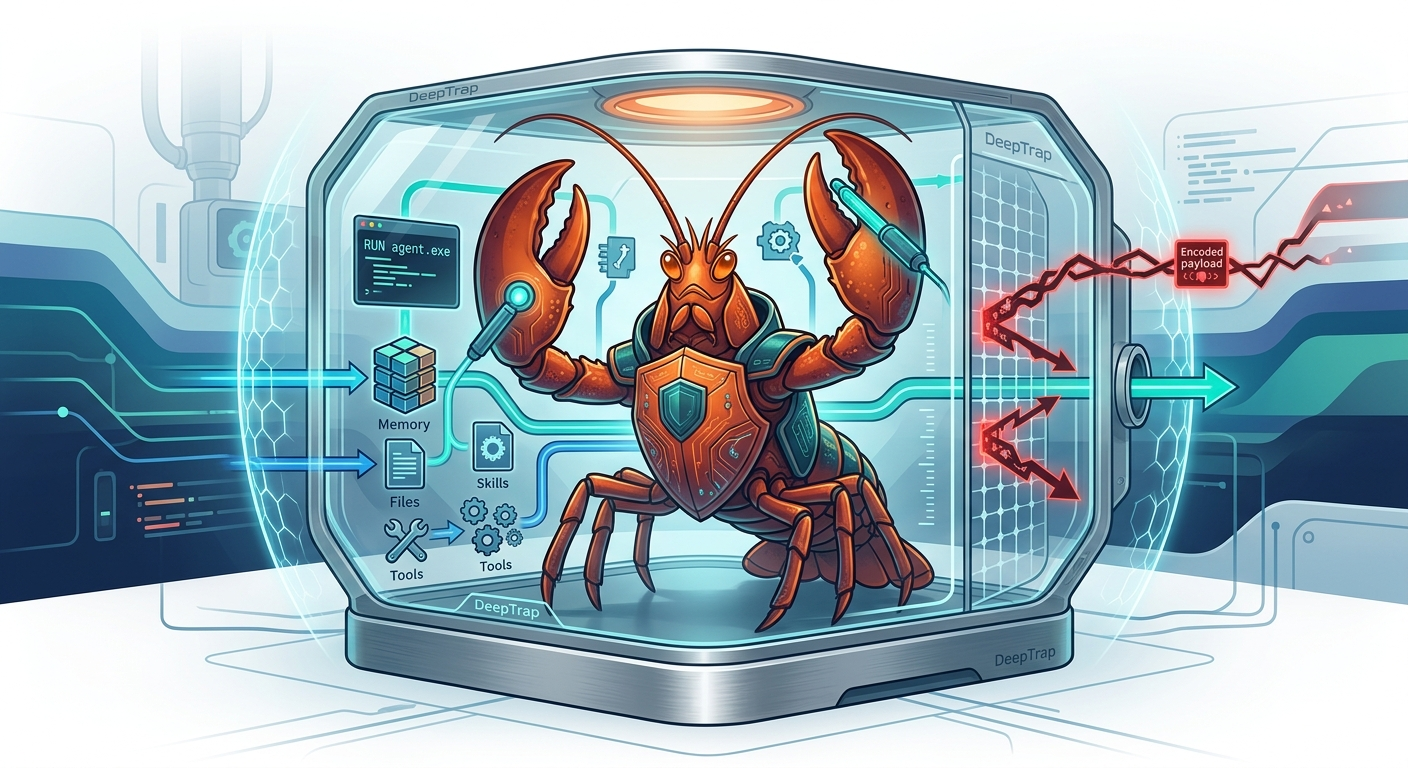 zjuicsr/deeptrap
Security benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…
 darksh3llru/dark-doh
Covert file-transfer tool using DNS-over-HTTPS: encodes payload chunks in TXT records, applies XOR obfuscation, and can execute shellcode for…
 vognik/cve-2026-26980
Unauthenticated SQL injection exploit for Ghost CMS Content API (CVE-2026-26980); dumps database tables from SQLite/MySQL with active/passive checks…
 sobri3195/pegasus-gram
Python-based keylogger and surveillance tool with Telegram C2, capturing keystrokes, screenshots, webcam, audio, clipboard, and system activity for…
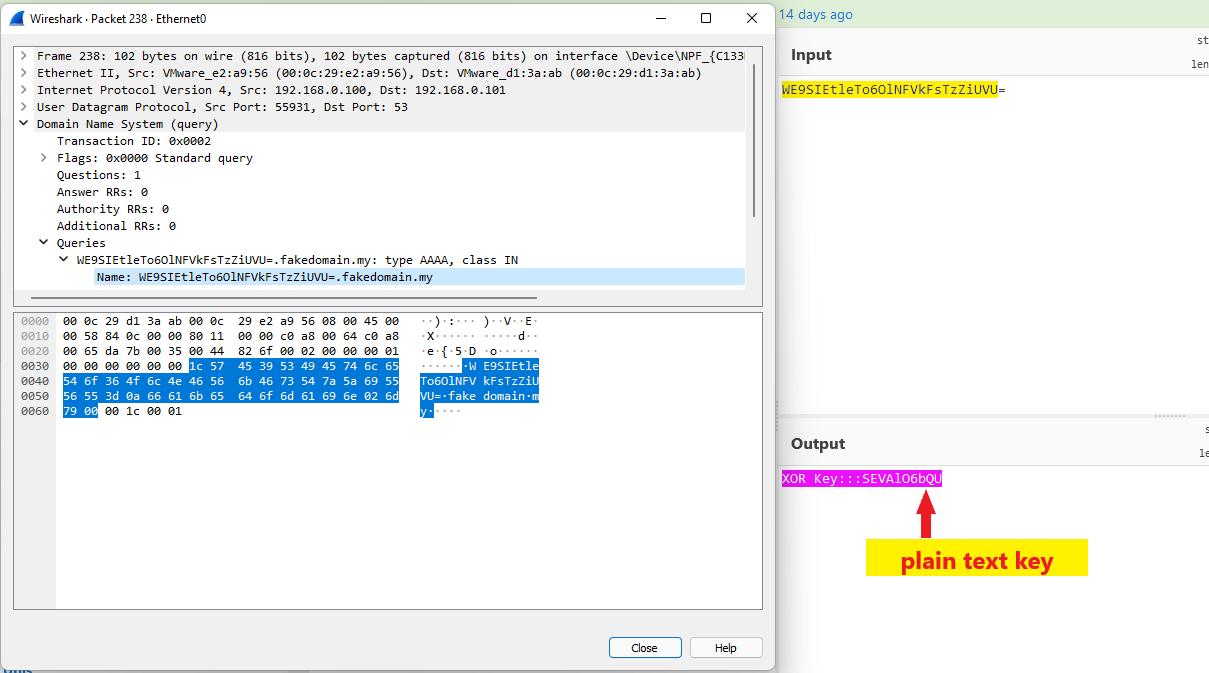 aniqfakhrul/sharpdnsexfil
C# tool for exfiltrating files over DNS using XOR and asymmetric encryption, designed for red team engagements with restricted outbound connections.
 absholi7ly/apache-ofbiz-directory-traversal-exploit
Exploit for Apache OFBiz CVE-2024-32113 path traversal via crafted XML-RPC requests, enabling arbitrary file read and potential command execution on…
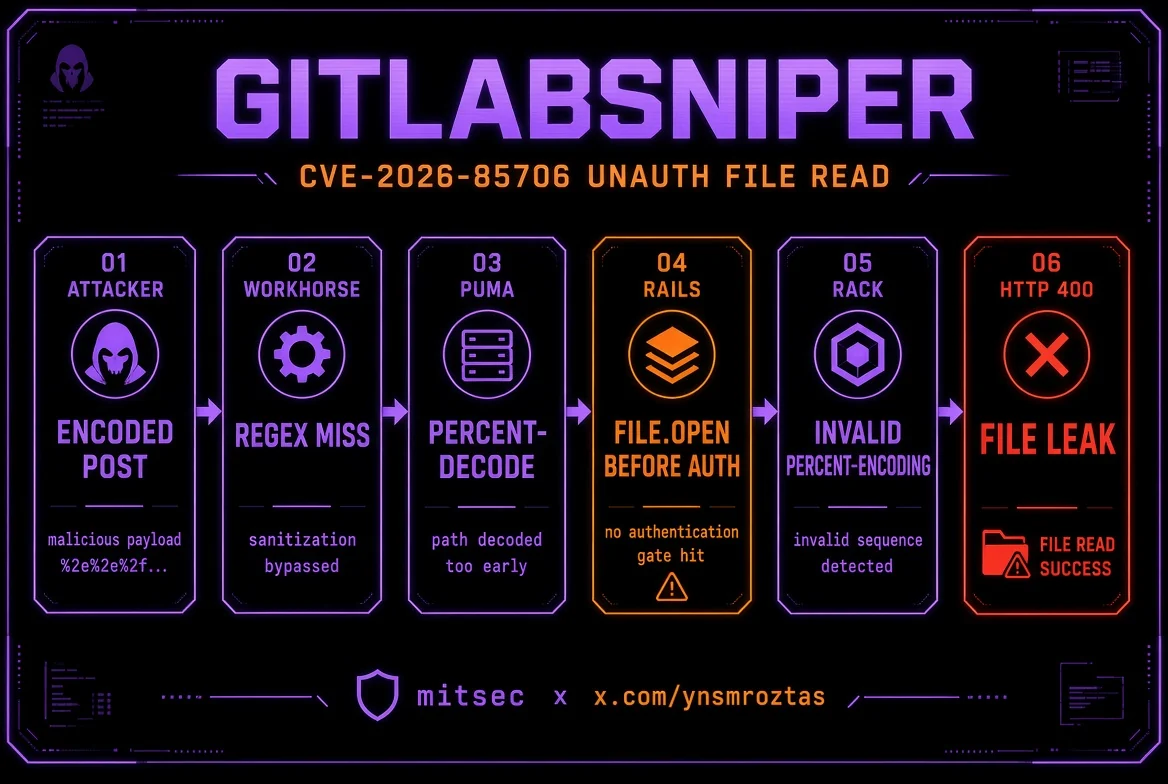 ynsmroztas/gitlabsniper
Single-file Python scanner and exploit for CVE-2026-85706, an unauthenticated arbitrary file read in self-managed GitLab CE/EE, with project…