
Phoenix-Framework
 xm0kht4r/phoenix-framework
Post-exploitation framework that abuses trusted sites like Telegram and Discord for C2.
command-and-controldata-exfiltrationpayload-development+5
xm0kht4r/phoenix-frameworkPost-exploitation framework that abuses trusted sites like Telegram and Discord for C2.
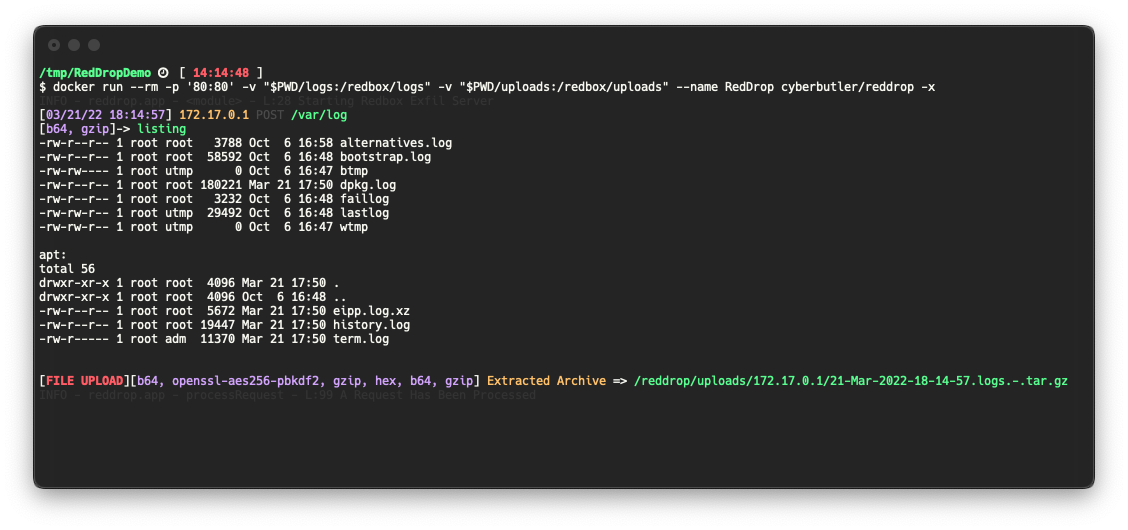 cyberbutler/reddrop
Python Flask web server for capturing, processing, and logging encoded/encrypted payloads and tar archives, designed for penetration testers and red…
 icyguider/newpowerdns
Updated version of PowerDNS by @domchell. Adds support for transfers over DNS A records and a few other useful features.
 citcheese/odbparser
OSINT tool to search, parse and dump only the open Elasticsearch and MongoDB directories that have the data you care about exposing
 mhdgning131/teletunnel
Bypassing EDR's with stealthy c++ telegram Bot and Telegram itself as C2 interface !
 ricardojoserf/covert-control
Google Drive, OneDrive and Youtube as covert-channels - Control systems remotely by uploading files to Google Drive, OneDrive, Youtube or Telegram
 wiredpulse/invoke-hivenightmare
PoC for CVE-2021-36934, which enables a standard user to be able to retrieve the SAM, Security, and Software Registry hives in Windows 10 version…
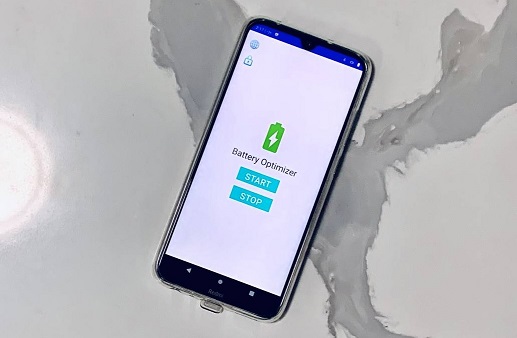 bluepigeonproject/blue-pigeon
Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a…
 ingokl/httpuploadexfil
A simple HTTP server for delivering and exfiltrating files/data during, for example, CTFs.
 jacopodl/pulsar
Data exfiltration and covert communication tool
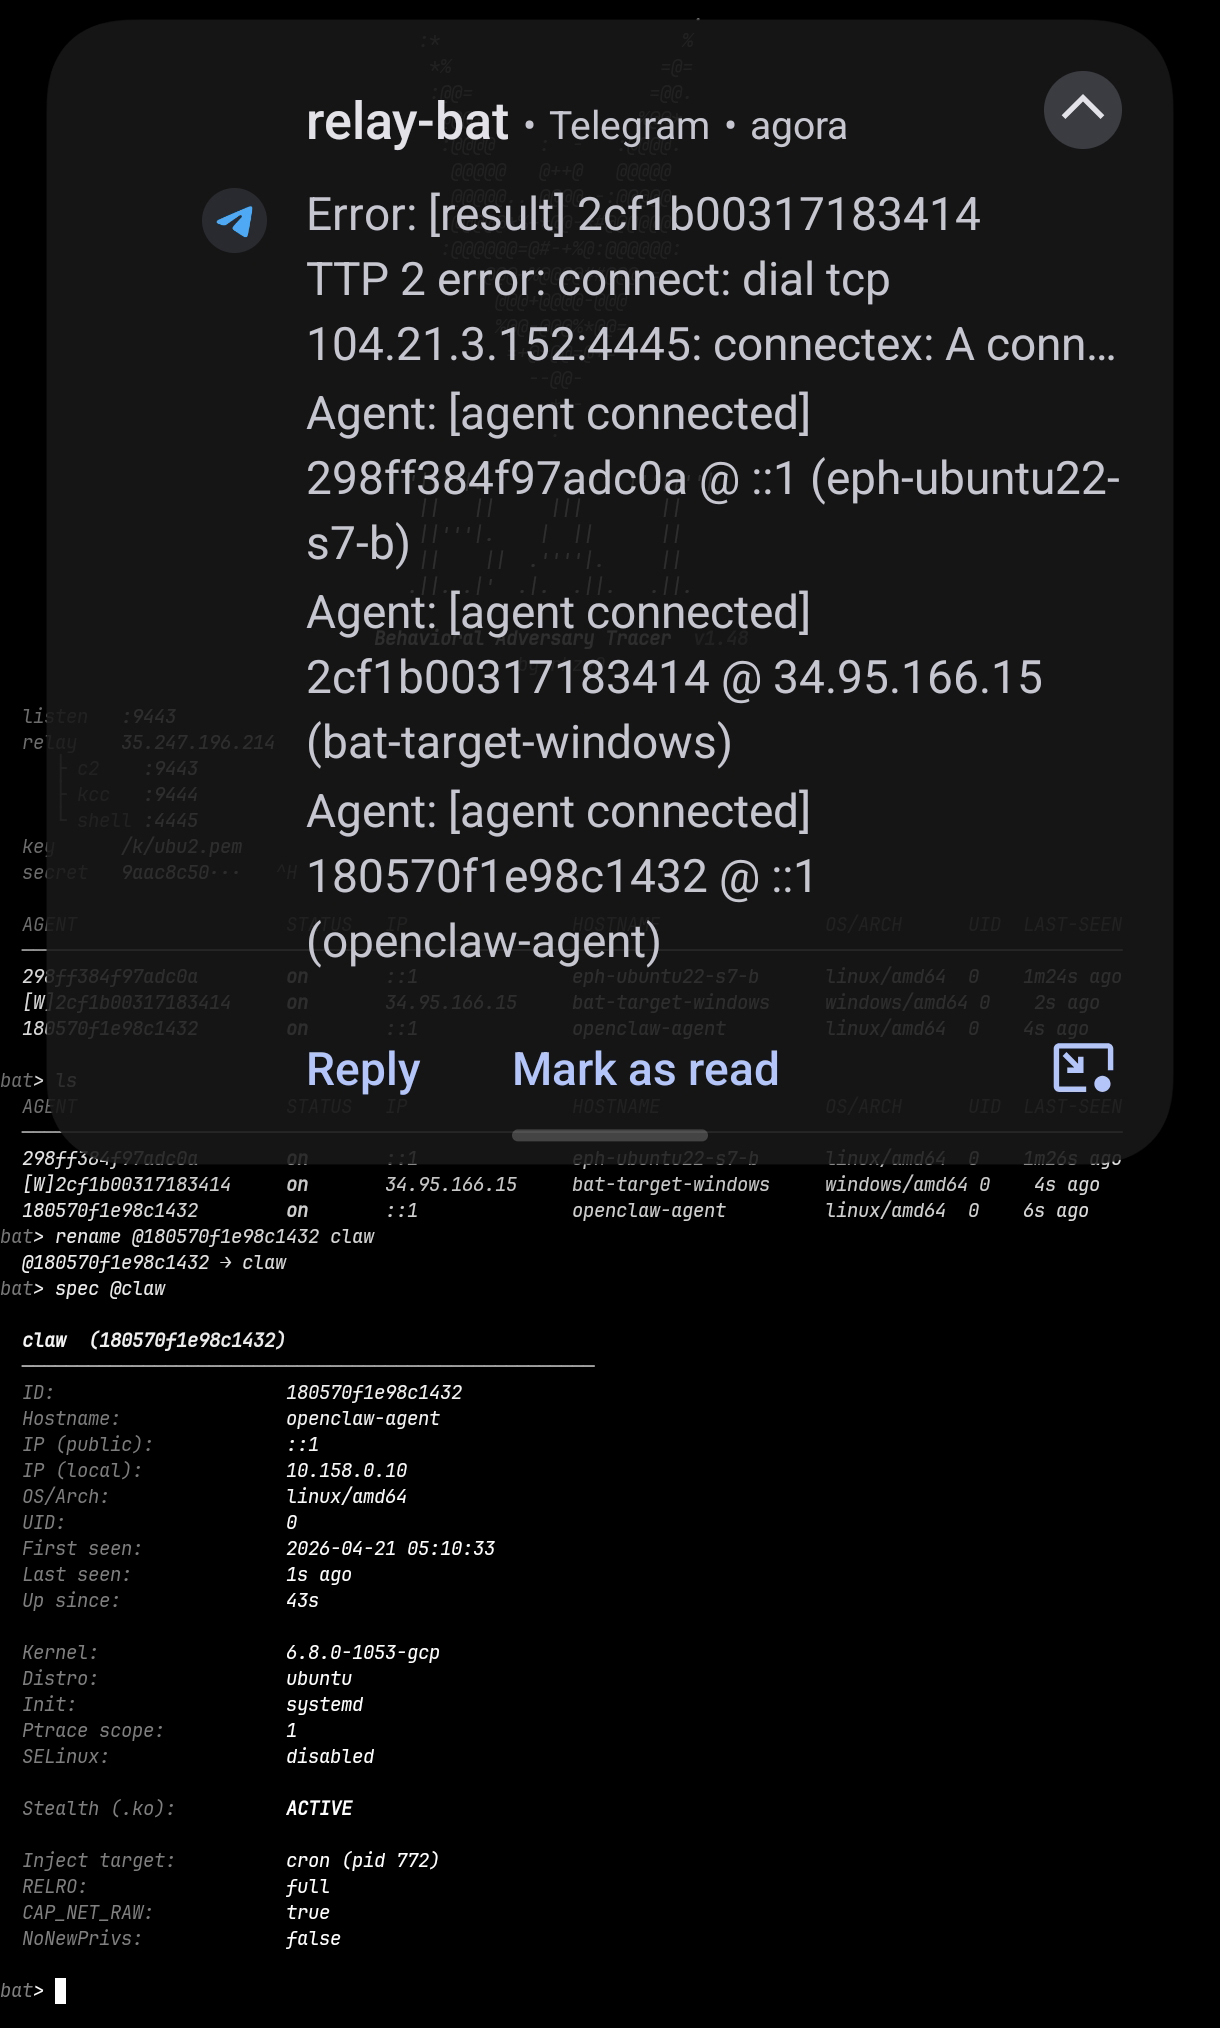 rhzv0/bat
Full-spectrum Linux adversary simulation platform with kernel-level stealth, C2 beaconing, privilege escalation, credential harvesting, lateral…
 mattiaalessi/phantom-keylogger
Phantom Keylogger is an advanced, stealth-enabled keystroke and visual intelligence gathering system.
 androvirus/blacknet
Free advanced and modern Windows botnet with a nice and secure PHP panel developed using VB.NET.
 gsoffmarket/malvinci
This simple but powerful script will introduce a new type of malware that will turn off the firewall, start an HTTP server, forward its port through…
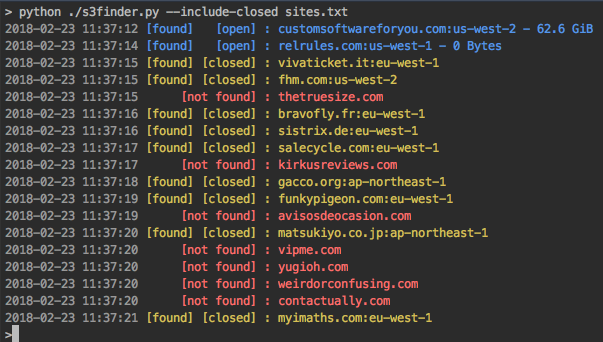 yehgdotnet/s3scanner
Scan for open S3 buckets and dump
 gryfman/dlpwn
Red Team tool for covert file exfiltration via Bluetooth audio transmission, encoding binary data into FLAC signals to bypass EDR, XDR, and DLP…
 rails/rails-forensics-cve-2026-66066
Forensic toolkit and agent skills for investigating Rails Active Storage/libvips CVE-2026-66066: detects crafted blob indicators, exposure windows,…
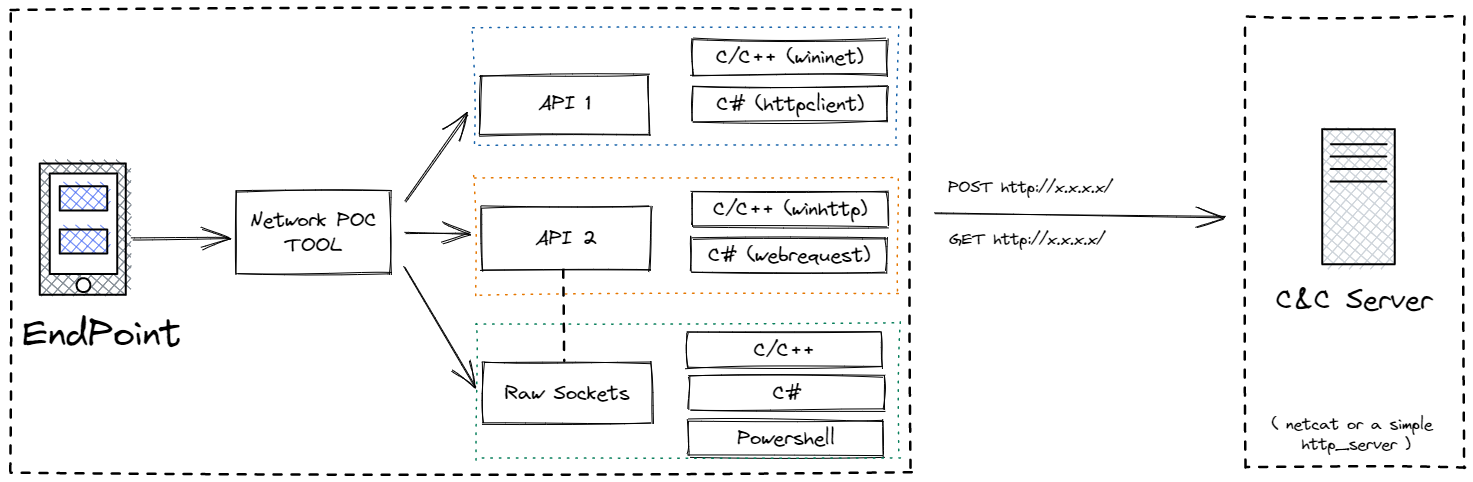 advanced-threat-research/netllix
A project created with an aim to emulate and test exfiltration of data over different network protocols.