
Phoenix-Framework
 xm0kht4r/phoenix-framework
Post-exploitation framework that abuses trusted sites like Telegram and Discord for C2.
command-and-controldata-exfiltrationpayload-development+5
69
xm0kht4r/phoenix-frameworkPost-exploitation framework that abuses trusted sites like Telegram and Discord for C2.
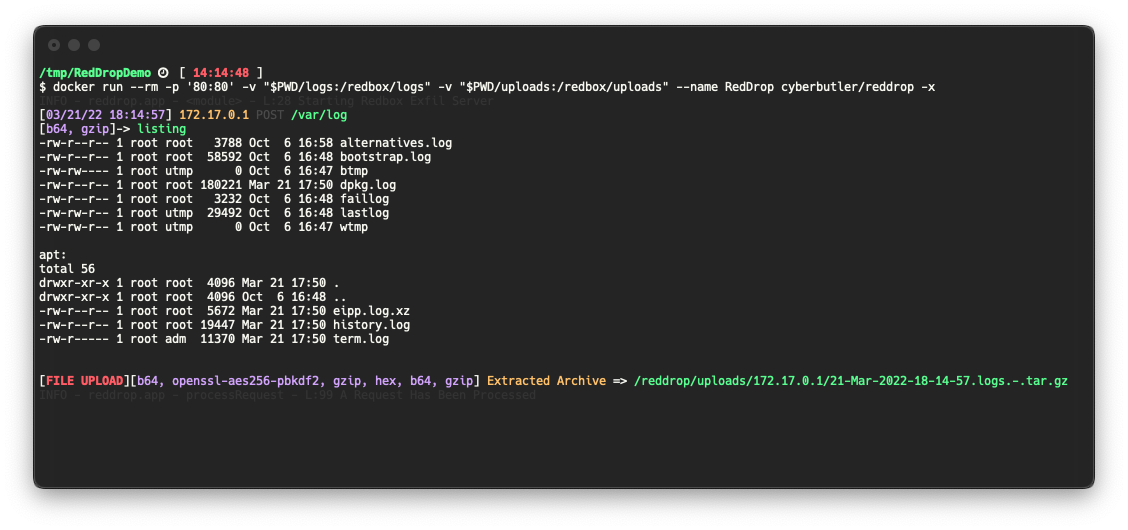 cyberbutler/reddrop
Python Flask web server for capturing, processing, and logging encoded/encrypted payloads and tar archives, designed for penetration testers and red…
 icyguider/newpowerdns
Updated version of PowerDNS by @domchell. Adds support for transfers over DNS A records and a few other useful features.
 karlvbiron/mad-cat
MAD-CAT (Meow Attack Data Corruption Automation Tool) is a comprehensive security tool designed to simulate data corruption attacks against multiple…
 wiredpulse/invoke-hivenightmare
PoC for CVE-2021-36934, which enables a standard user to be able to retrieve the SAM, Security, and Software Registry hives in Windows 10 version…
 antman1p/gdir-thief
Red Team tool for exfiltrating the target organization's Google People Directory that you have access to, via Google's API.
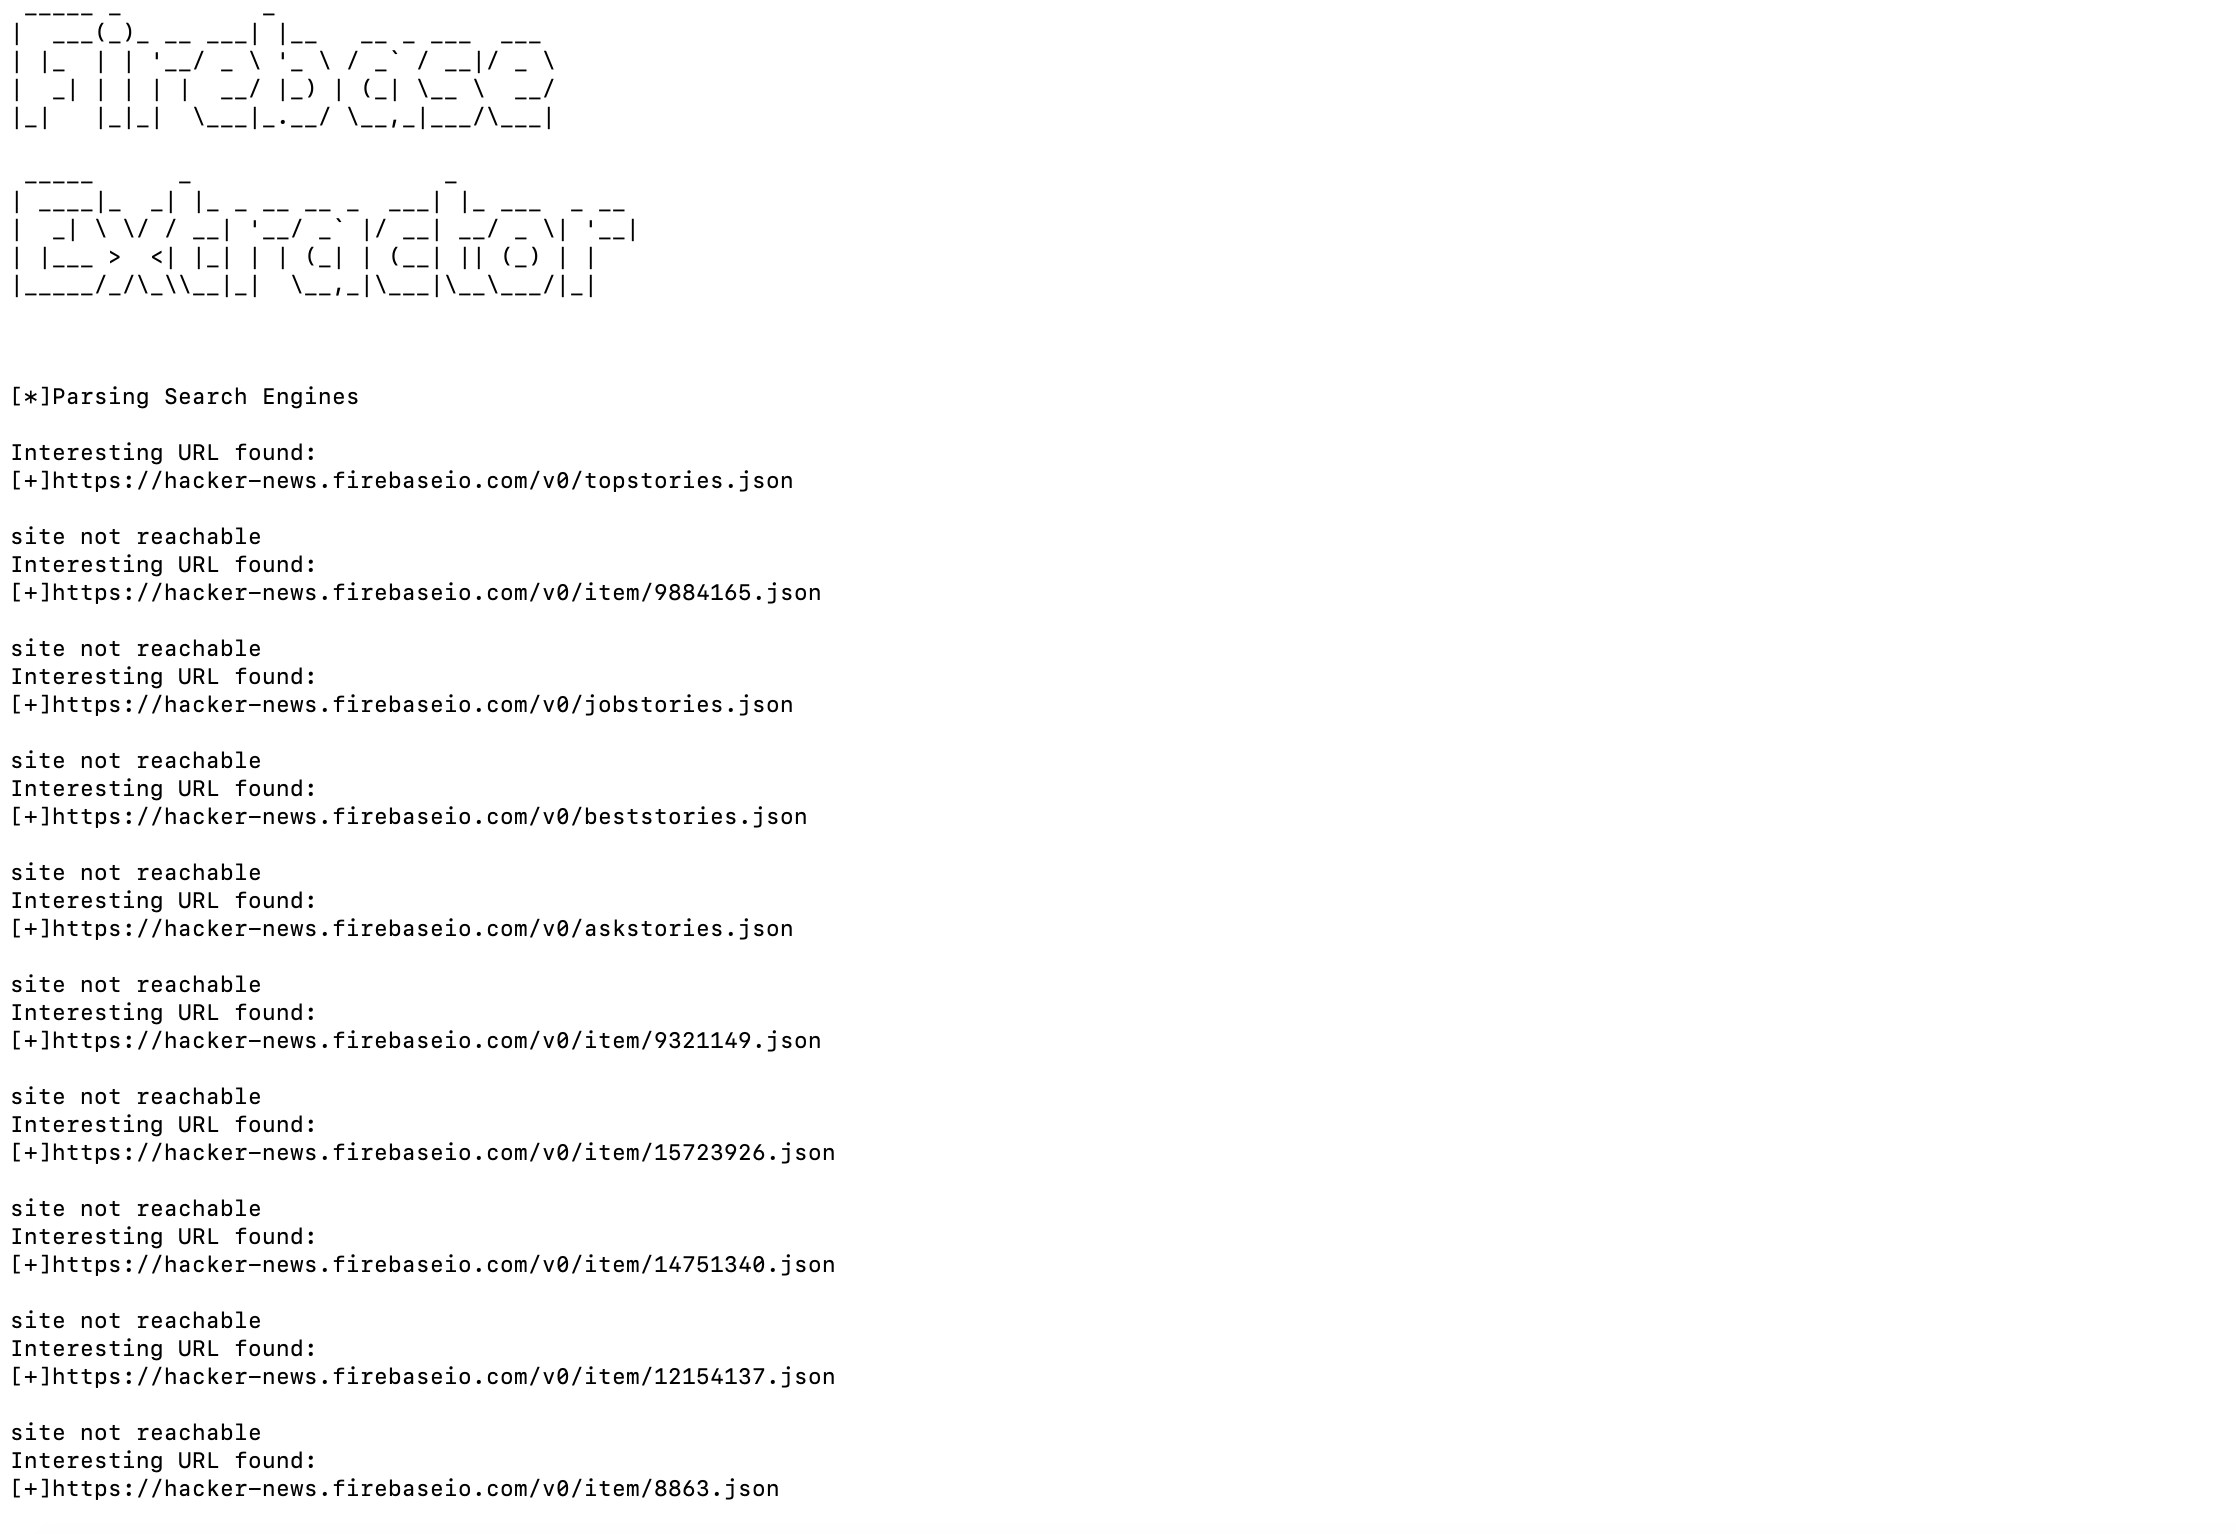 viperbluff/firebase-extractor
A tool written in python for scraping firebase data
 ingokl/httpuploadexfil
A simple HTTP server for delivering and exfiltrating files/data during, for example, CTFs.
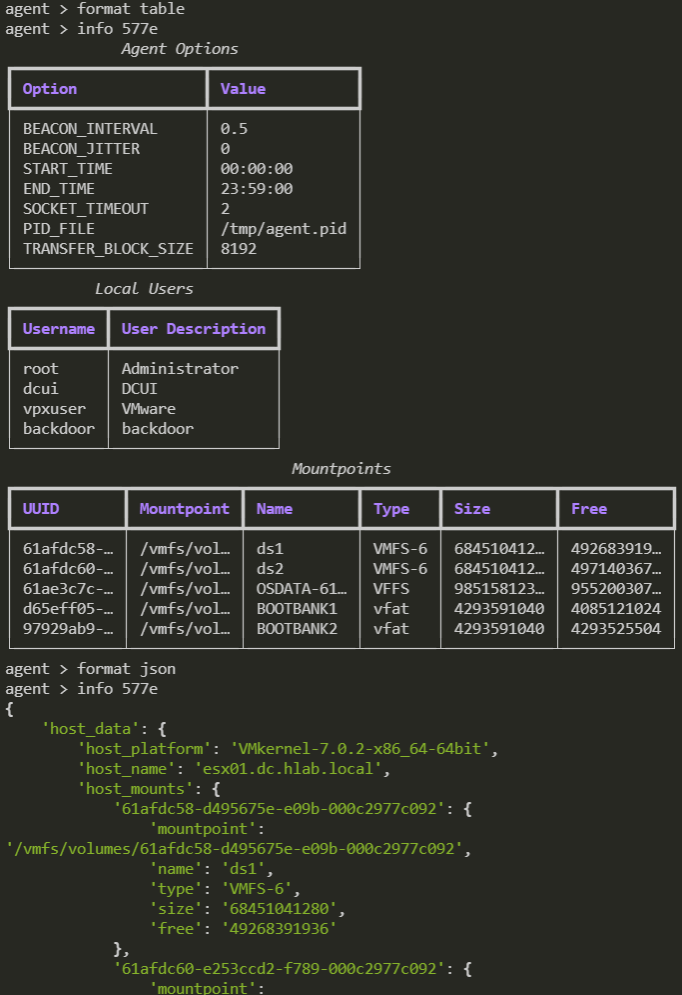 psmths/reave
WIP Post-exploitation framework tailored for hypervisors.
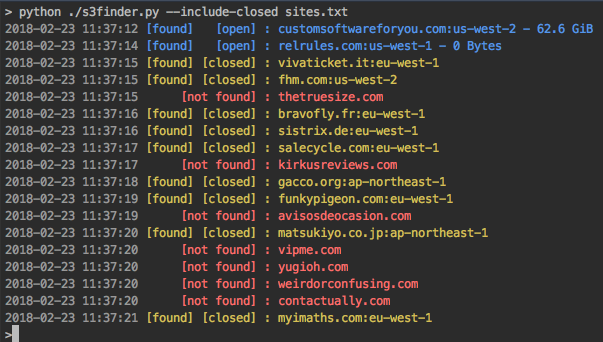 yehgdotnet/s3scanner
Scan for open S3 buckets and dump
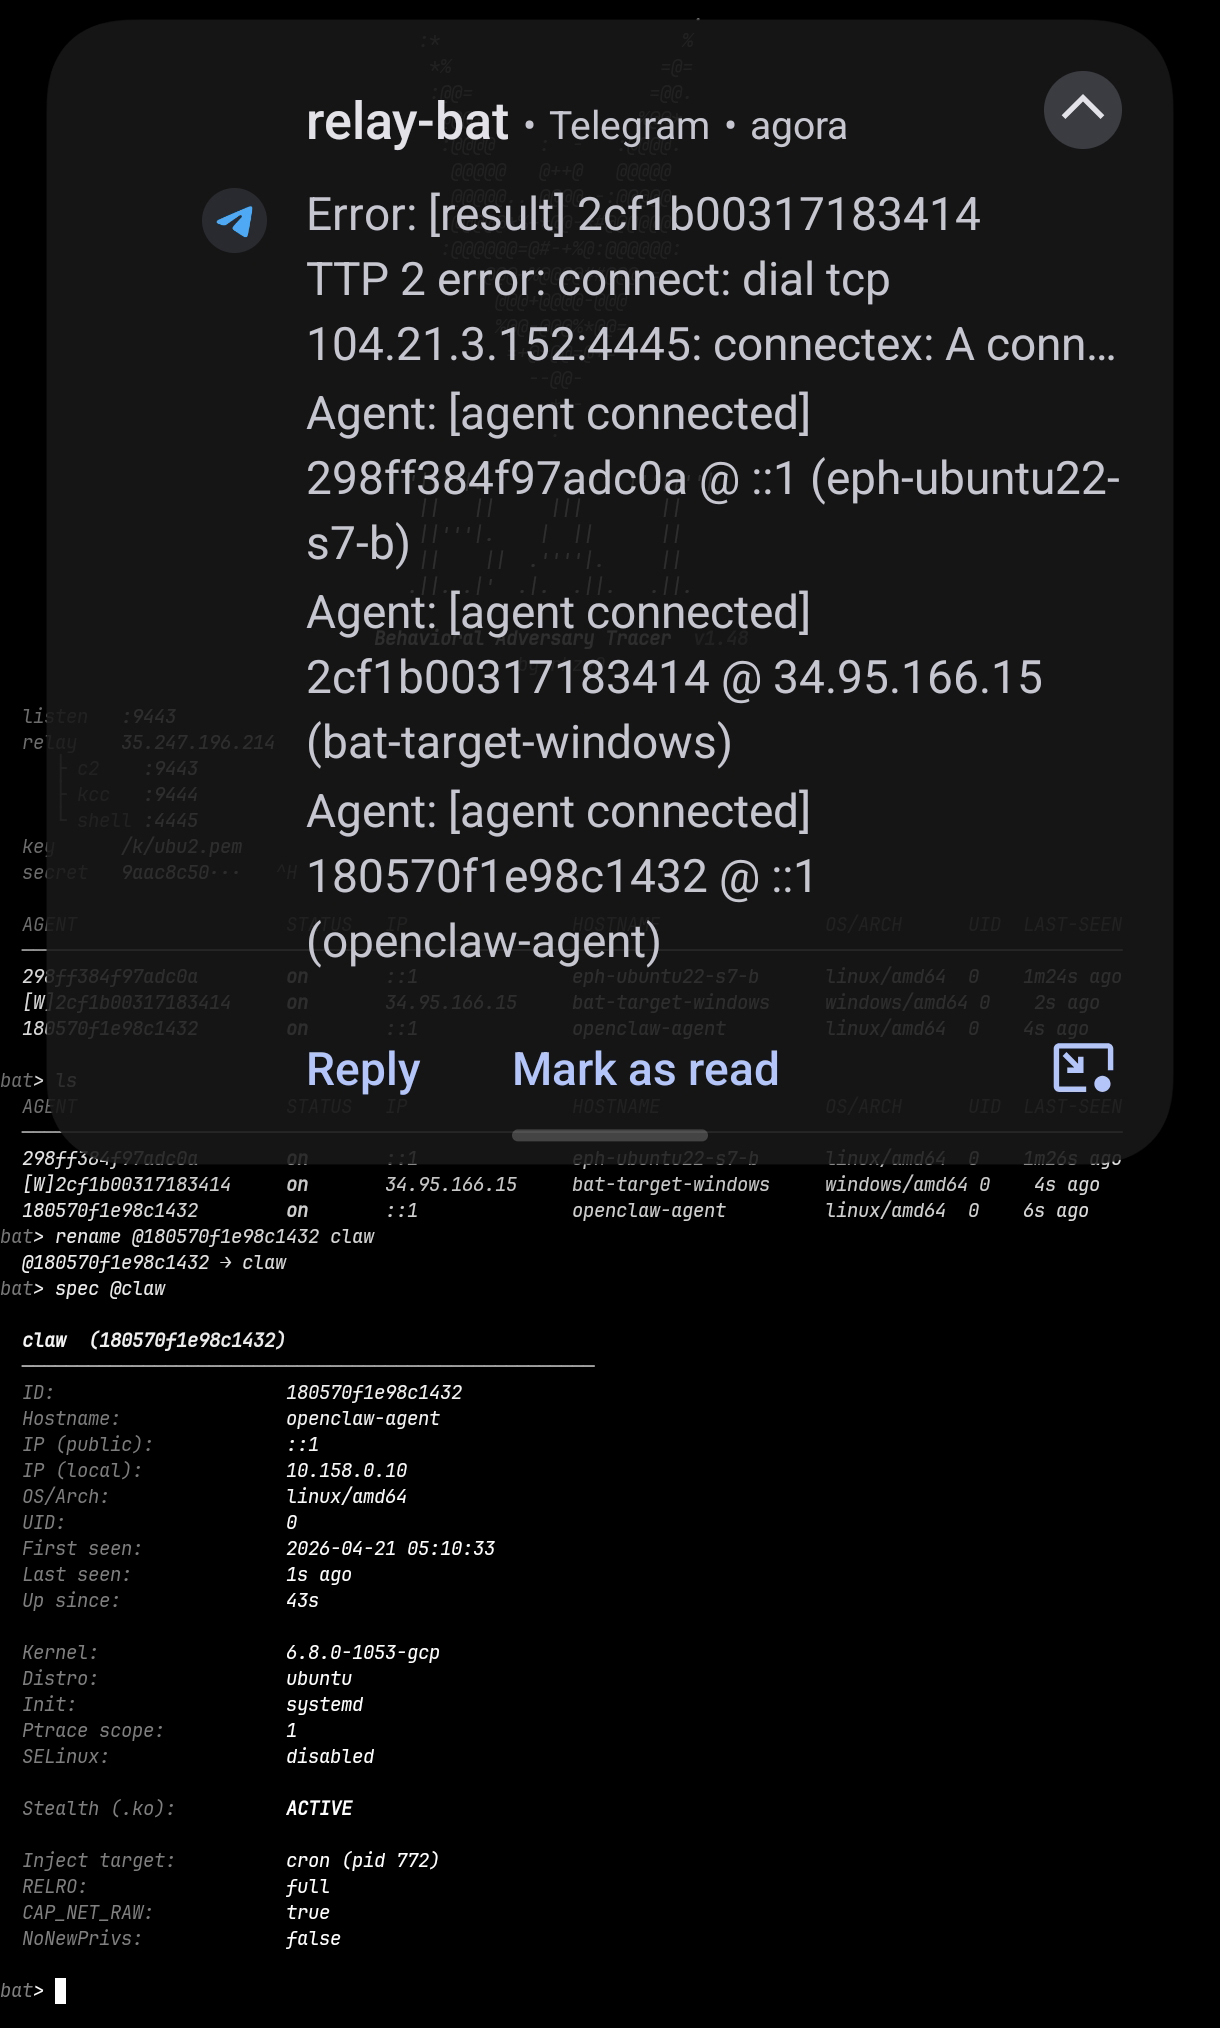 rhzv0/bat
Full-spectrum Linux adversary simulation platform with kernel-level stealth, C2 beaconing, privilege escalation, credential harvesting, lateral…
 rails/rails-forensics-cve-2026-66066
Forensic toolkit and agent skills for investigating Rails Active Storage/libvips CVE-2026-66066: detects crafted blob indicators, exposure windows,…
 momika233/cve-2022-3656
Proof-of-concept exploit for CVE-2022-3656, a Chrome/Chromium vulnerability enabling theft of sensitive files like encrypted wallets and cloud…
 6mile/gimmepatz
Personal Access Token (PAT) recon tool for bug bounty hunters, pentesters & red teams
 shieldersec/cve-2020-11579
Exploit code for CVE-2020-11579, an arbitrary file disclosure through the MySQL client in PHPKB
 gryfman/dlpwn
Red Team tool for covert file exfiltration via Bluetooth audio transmission, encoding binary data into FLAC signals to bypass EDR, XDR, and DLP…
 hacksysteam/cve-2021-45067
Exploit for Adobe Reader DC out-of-bounds read vulnerability (CVE-2021-45067) that leaks sensitive information from the sandboxed process via…
 ac3lives/kyocera-cve-2022-1026
An unauthenticated data extraction vulnerability in Kyocera printers, which allows for recovery of cleartext address book and domain joined passwords