
cve_2024_0044
 hunter24x24/cve_2024_0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
android-securitydata-exfiltrationexploitation+5
1
hunter24x24/cve_2024_0044CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 learner202649/cve-2026-35029-poc
The code for personally reproducing the corresponding vulnerability
 atici/imagemagick-cve-2022-44268-poc
A bash script for easyly exploiting ImageMagick Arbitrary File Read Vulnerability CVE-2022-44268
 wiliam227user/cve-2018-12633-tplink-auth-bypass
A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).
 iveresk/cve-2022-31749
PoC checker for CVE-2022-31749 exploiting a parameter injection vulnerability in WatchGuard SSH interface to exfiltrate hashed user passwords via FTP.
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
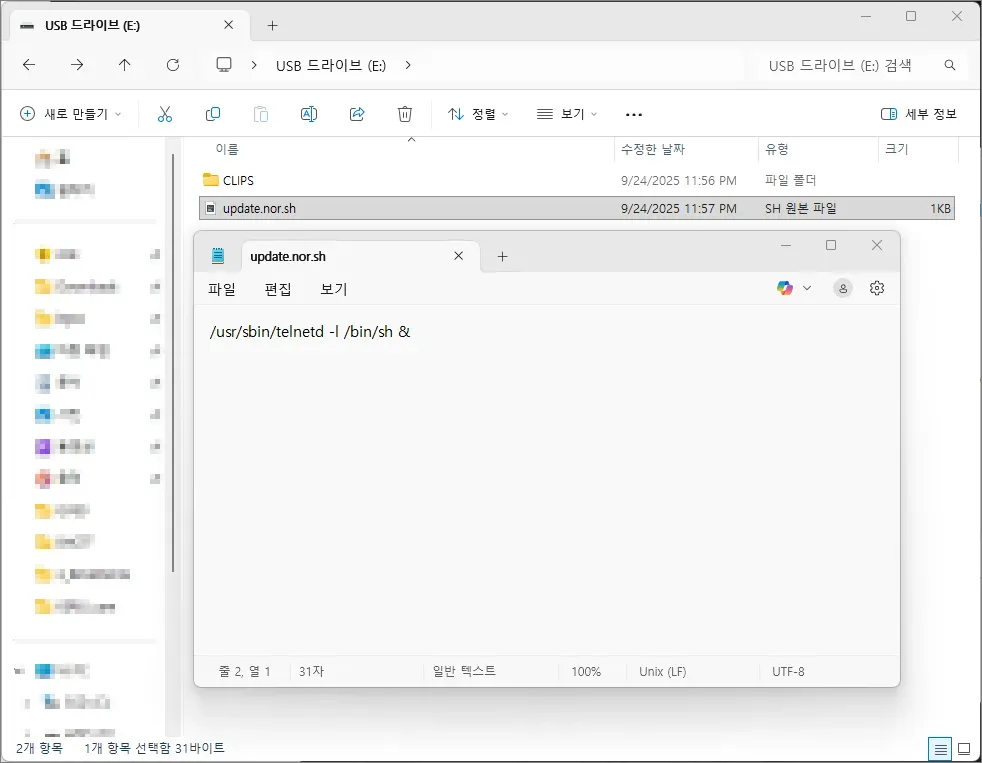 t4e-3/cve-2025-63296
KERUI K259 5MP Wi-Fi (Tuya Smart Security Camera) contains a code execution vulnerability
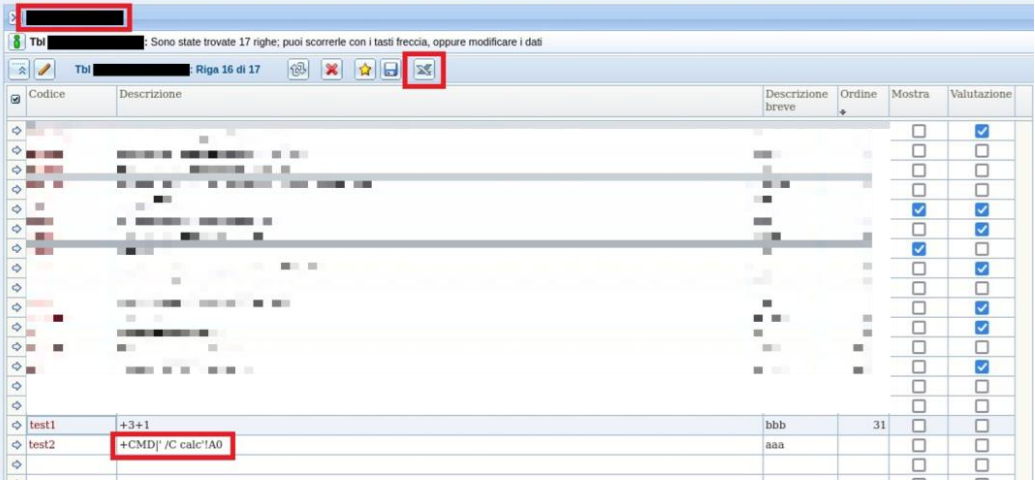 valeriocassoni/csv-injection-in-instant-developer-foundation-25.0-poc
This repository contains a Proof of Concept (PoC) for a CSV Injection (Formula Injection) vulnerability (CVE-2025-60852) affecting applications built…
 k4ran909/cve_2024_0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
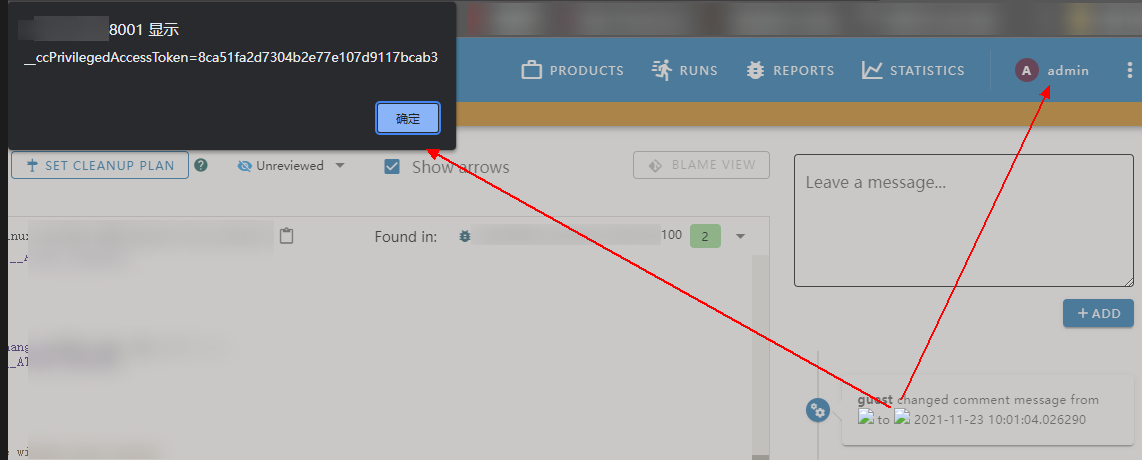 hyperkopite/cve-2021-44217
Proof-of-concept for a stored XSS vulnerability (CVE-2021-44217) in Ericsson CodeChecker's comments component, enabling cookie theft and sensitive…
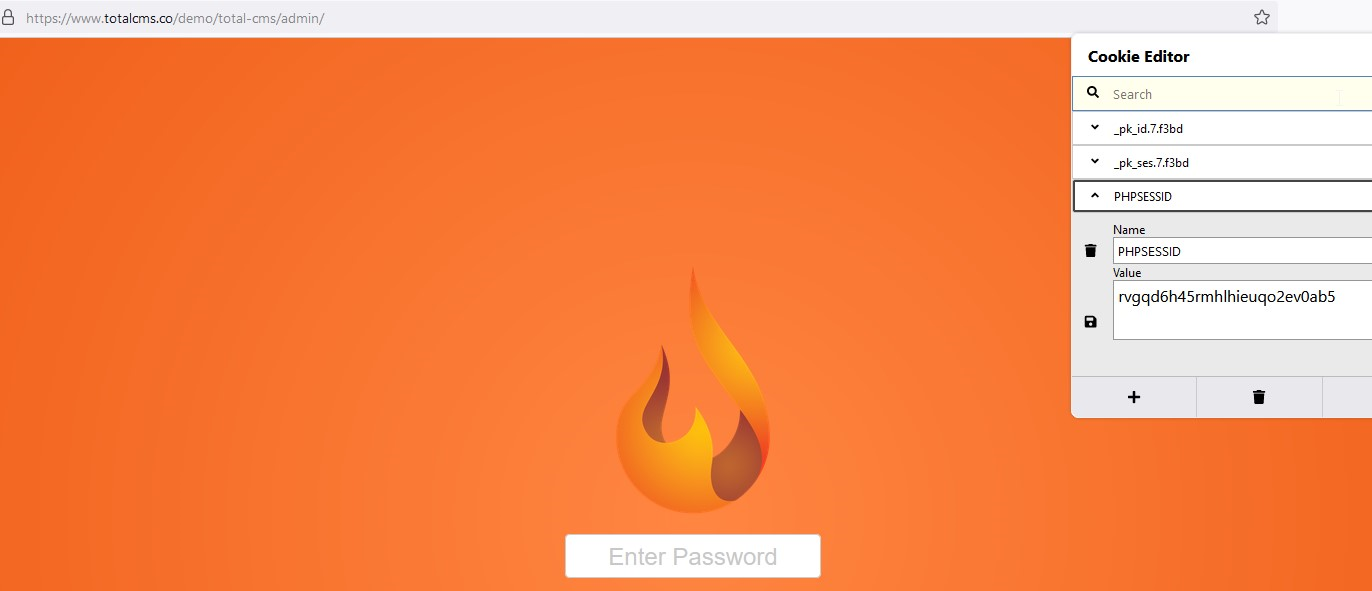 sromanhu/totalcms-arbitrary_file-upload--xss_steal_cookies---totaldepot
TotalCMS is affected by Arbitrary File Upload - XSS vulnerability which allows Cross-Site Scriting (XSS) Stored and also stealing session cookies
 mazen160/shennina
Automating Host Exploitation with AI
 ioncodes/cve-2020-16938
Bypassing NTFS permissions to read any files as unprivileged user.
 pwardle/not-a-mused
Proof-of-concept exploiting an undocumented Muse dictation endpoint setting, letting a local unprivileged process redirect dictation traffic to…
 b1ack0wl/miniupnpd_poc
Read out-of-bounds PoC for miniupnpd <= v2.1
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 mbadanoiu/cve-2024-34693
CVE-2024-34693: Server Arbitrary File Read in Apache Superset
 godylockz/cve-2023-40028
POC for CVE-2023-40028: Ghost CMS Arbitrary File Read