
CVE-2026-1357-POC
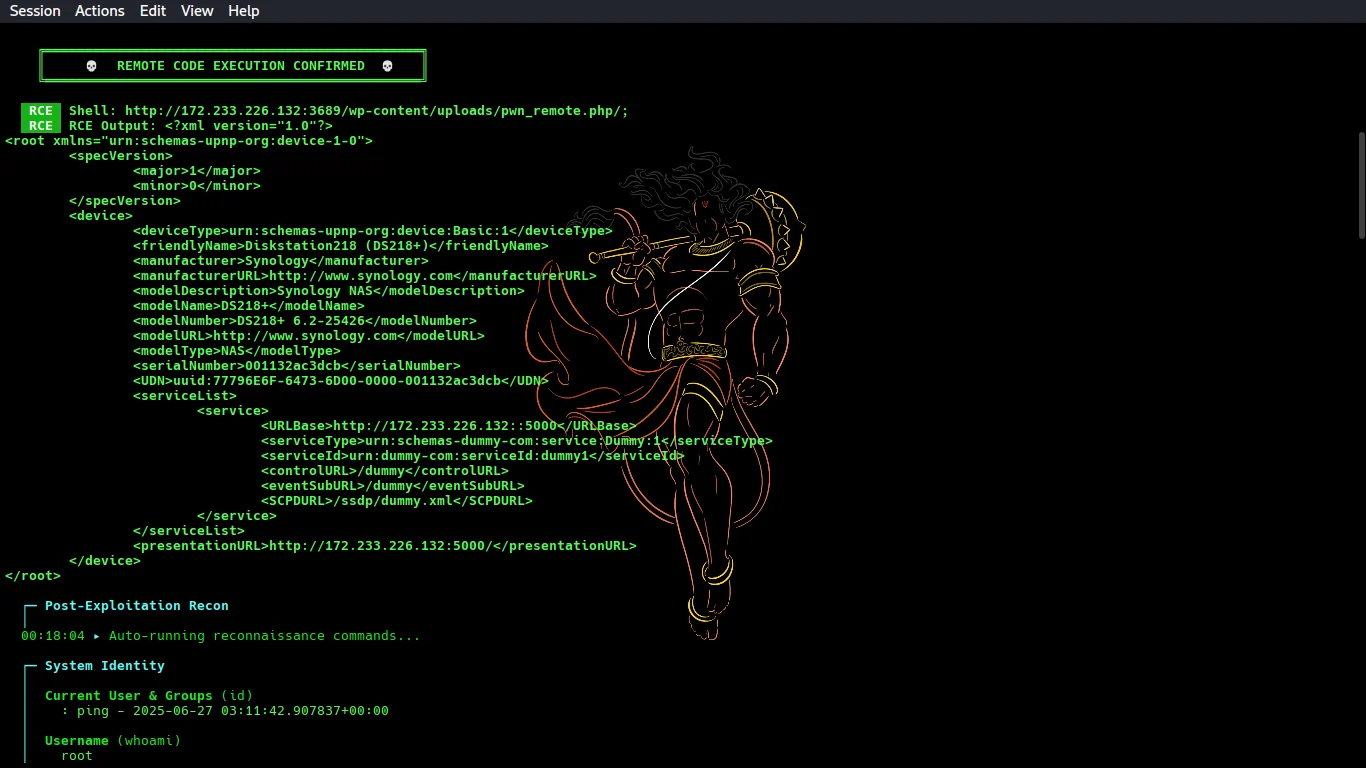
Automated exploit tool for CVE-2026-1357, an unauthenticated RCE in WPvivid Backup & Migration. Scans WordPress targets, bypasses WAF/403, uploads a…

Automated exploit tool for CVE-2026-1357, an unauthenticated RCE in WPvivid Backup & Migration. Scans WordPress targets, bypasses WAF/403, uploads a…

Exploiting CVE-2016-10277 for Secure Boot and Device Locking bypass

This is a toolkit that uses CVE-2024-31317 to extract private app data via ADB or spawn a shell with an app's UID.

Proof-of-Concept exploit for CVE-2026-15409 (SonicWall SMA 1000 RCE) via Erlang distribution over WebSocket. Achieves unauthenticated remote code…

Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.

CVE-2024-0044: uma vulnerabilidade de alta gravidade do tipo "executar como qualquer aplicativo" que afeta as versões 12 e 13 do Android

Exploiting Android Vulnerability in ES File Explorer

Proof of Concept of Libreoffice file exfiltration vulnerability in Big Blue Button

Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration

CVE-2026-60004 — Gitea/Forgejo Diffpatch Git Hook RCE. Bare clone → post-index-change hook injection. CVSS 9.8 | CWE-94 | Gitea < 1.27.1

PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…

Demonstrates a critical GraphQL batching alias-confusion SQL injection (CVE-2026-5432) with a vulnerable Node.js server and Python exploit for…

The Joomla extension PhocaCommander is vulnerable to Path Traversal in delete, copy, move actions - CVSS 6.4

POC of CVE-2026-51031 for arbitrary local file read

Source code minh họa máy chủ c2 demo kịch bản thực thi của CVE-2024-23700

CVE-2021-26837 - SQL Injection in the SearchTextbox parameter of HelpSystems/Fortra DeliverNow. Payloads, annotated requests, and evidence. Fixed in…

Python implementation/PoC for CVE-2024-40422. Exploits a critical directory traversal vulnerability in Devika v1's /api/get-browser-snapshot endpoint…

PoC for CVE-2026-53629, blind SQL injection in the GLPI history log filter