
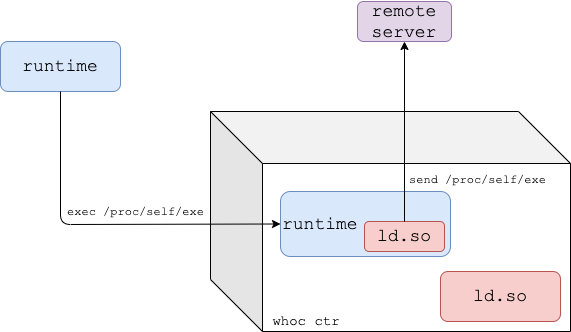
whoc
 twistlock/whoc
A container image that exfiltrates the underlying container runtime to a remote server
cloud-securitycontainer-securitydata-exfiltration+1
135
twistlock/whocA container image that exfiltrates the underlying container runtime to a remote server
 thegeekht/loki.rat
Loki.Rat is a fork of the Ares RAT, it integrates new modules, like recording , lockscreen , and locate options. Loki.Rat is a Python Remote Access…
 1d8/spybrowse
Code developed to steal certain browser config files (history, preferences, etc)
 jollheef/libreoffice-remote-arbitrary-file-disclosure
Proof of concept of LibreOffice remote arbitrary file disclosure vulnerability
 rasta-mouse/pwnlift
Easy peasy file uploads
 ingokl/httpuploadexfil
A simple HTTP server for delivering and exfiltrating files/data during, for example, CTFs.
 prodefense/hawk
Golang tool designed to exfiltrate passwords found via the sshd and su services
 krixx1337/burner-net
Zero-trust anti-forensic HTTP client. Wipes secrets. Severs traces. CPR in a Stealth Tank. 👻
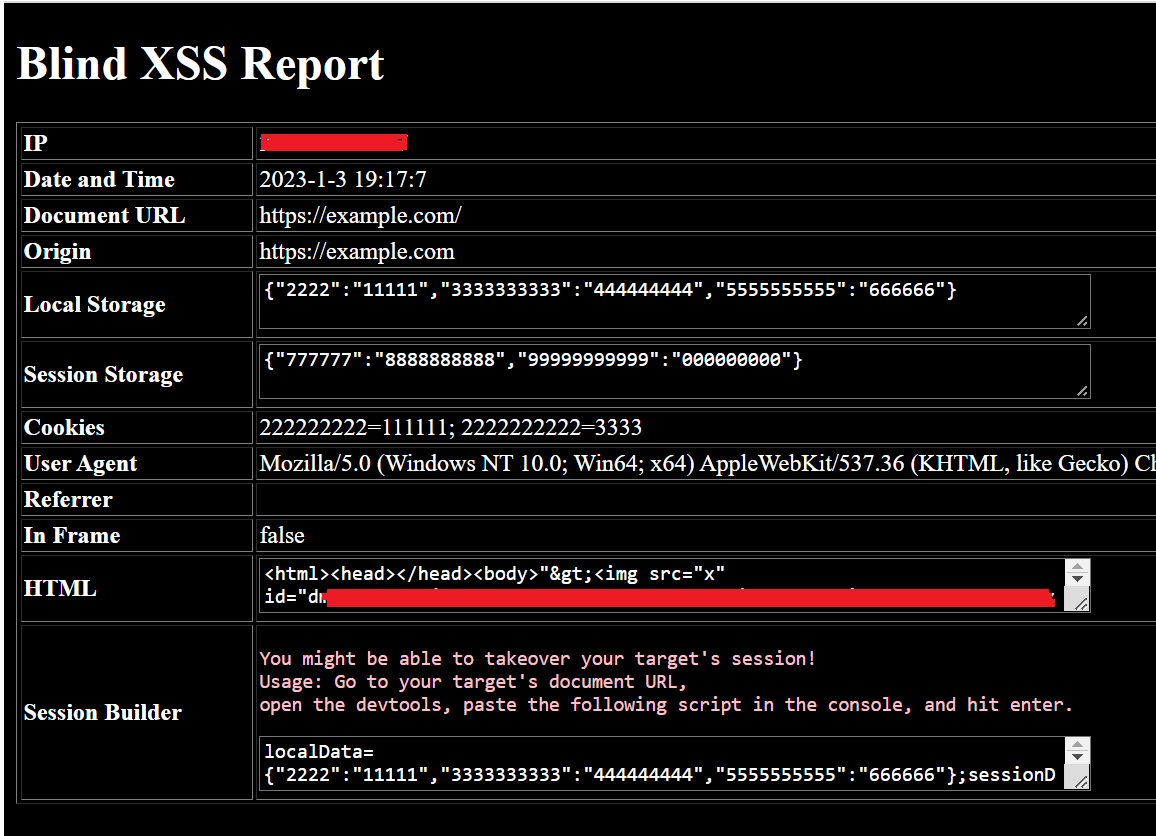 seifelsallamy/xssfire
A standalone Blind XSS Script.
 formerlab/shadow-fleet-tracker-light
Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally
 blacksnufkin/deadmanswitch
DeadManSwitch in rust with several triggers (remote local and network)
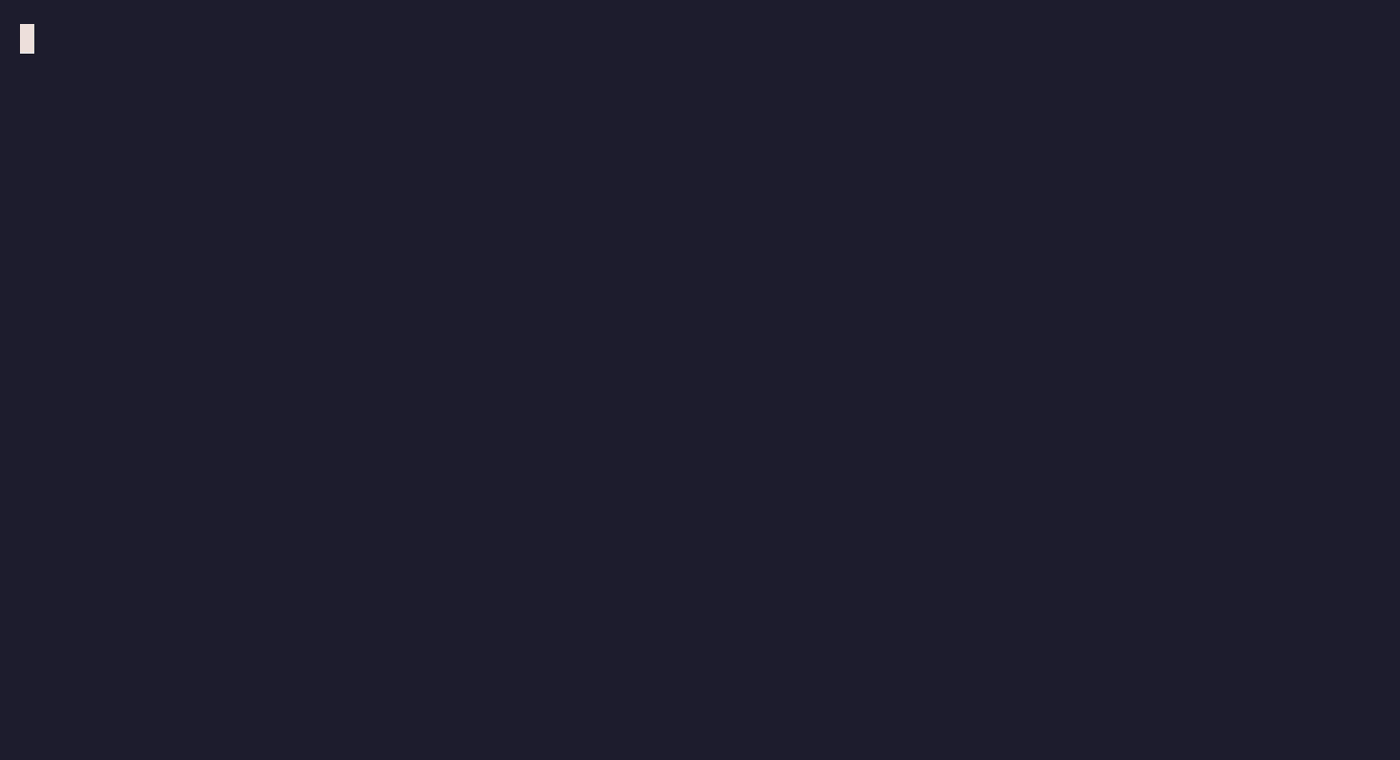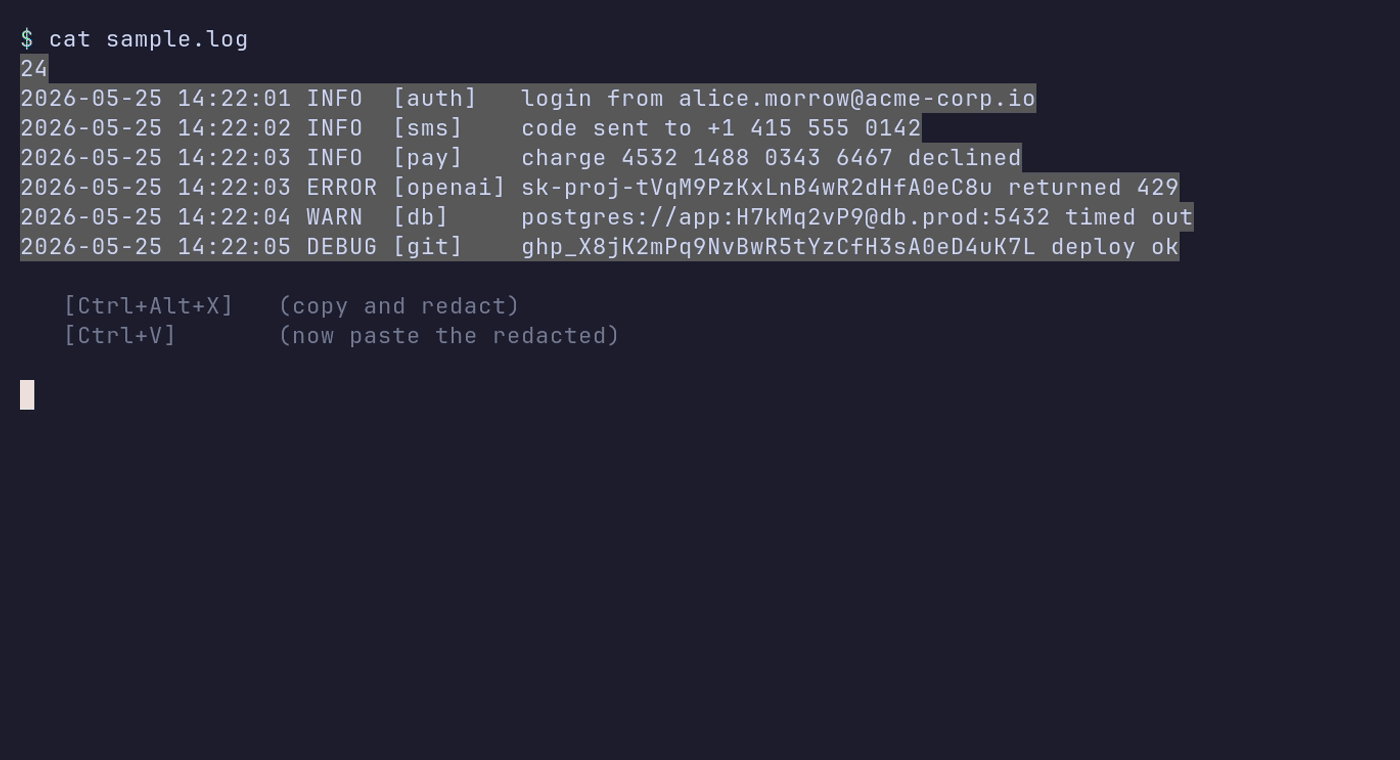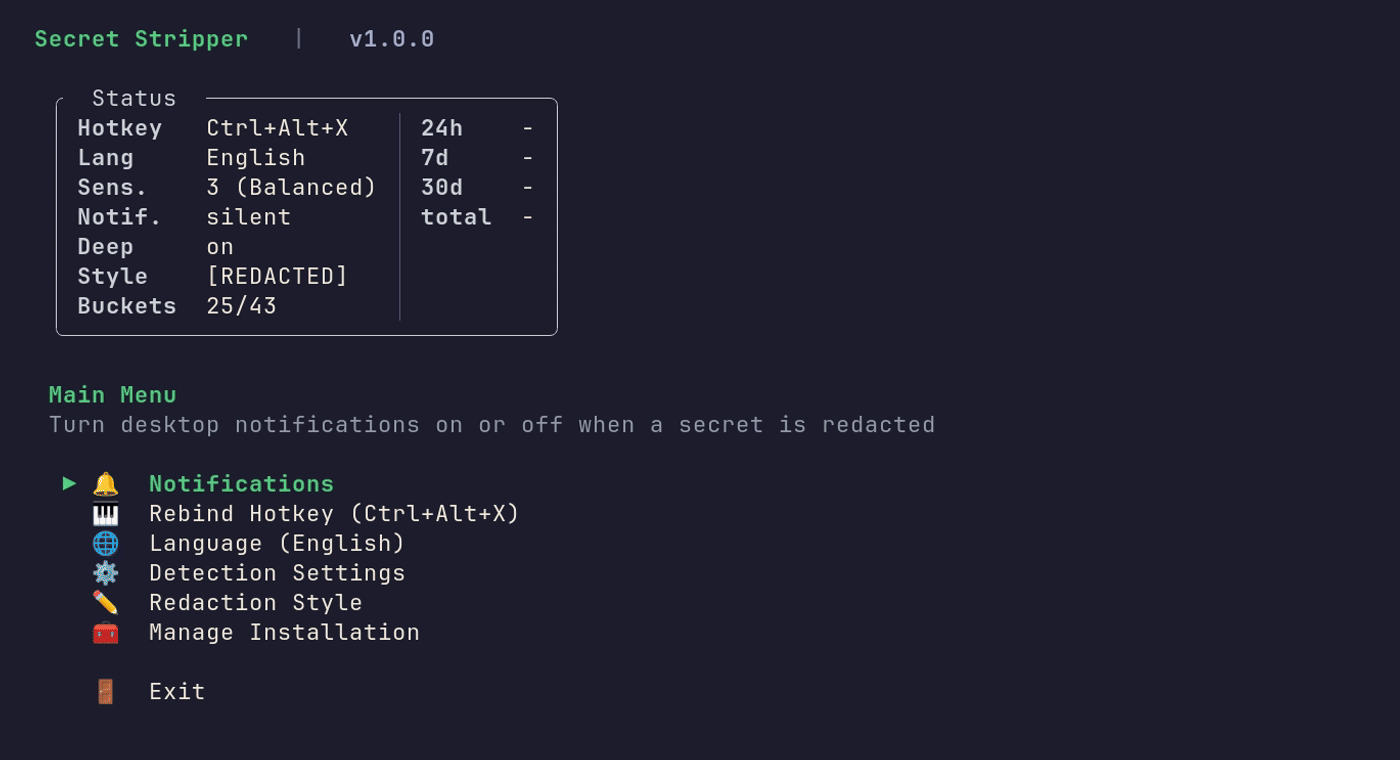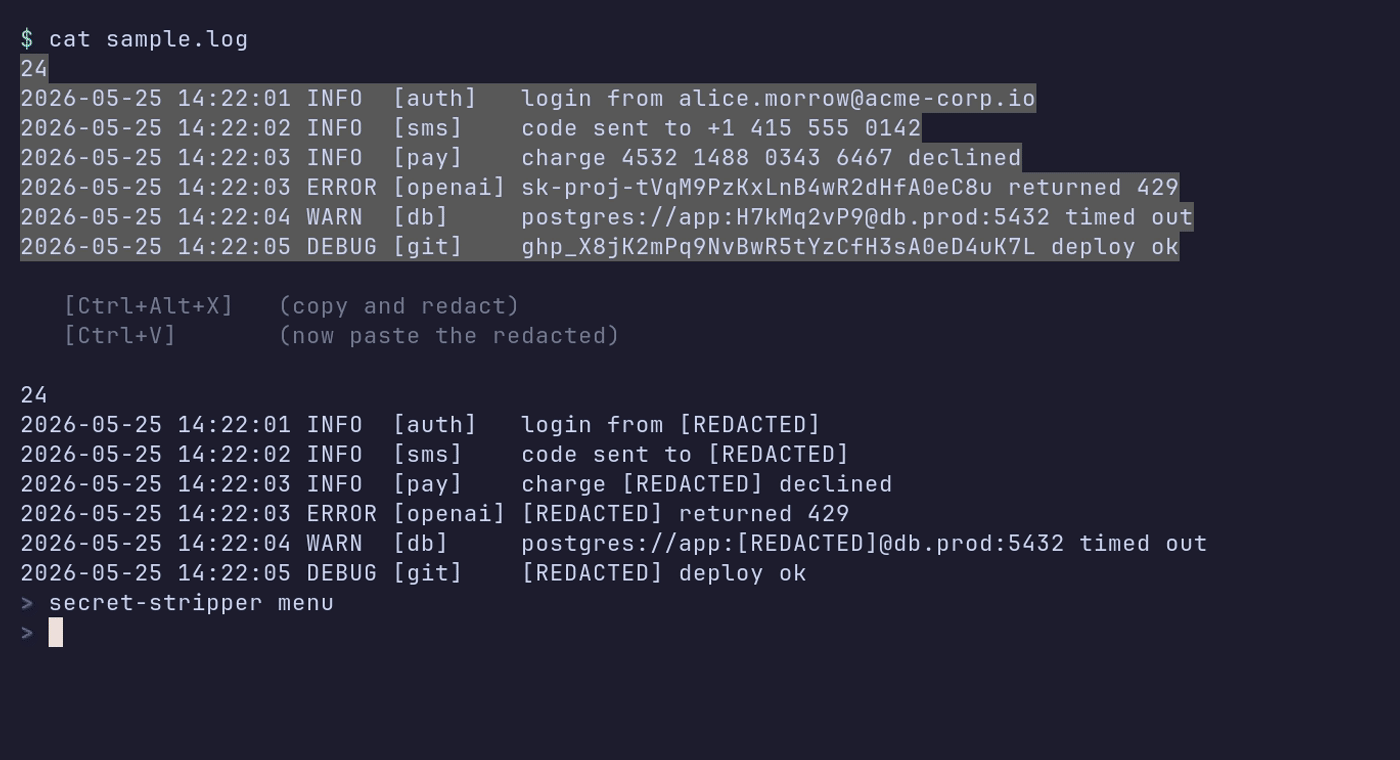 kalix127/secret-stripper
A small Rust CLI that strips secrets from your clipboard on demand.
 lucacav/steg-tools
A list of tools and material on steganography and information hiding
 gradiant/faro
FARO - Document Sensitivity Detector
 cenobyte-vincit/slot2
UEFI GRUB2 bootkit that installs a pre-boot networked implant via NVRAM boot option, chainloads a UKI, executes a dracut payload, and kexecs the…
 jgalego/hiddensteps
HiddenSteps — a local-first personal workflow intelligence platform
 b1tbreaker/cve-2025-48708
Lack of argument sanitization leading to password leakage in Ghostscript PDF versions up to 10.05.0.
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node