
drupal-jsonapi-sqli-scanner
 ridhinva/drupal-jsonapi-sqli-scanner
Scanner: CVE-2026-9082 Drupal PostgreSQL SQLi via JSON:API — Python scanner for unauthenticated SQLi leading to RCE (CISA KEV)
database-securitydata-exfiltrationexploitation+5
ridhinva/drupal-jsonapi-sqli-scannerScanner: CVE-2026-9082 Drupal PostgreSQL SQLi via JSON:API — Python scanner for unauthenticated SQLi leading to RCE (CISA KEV)
 b1tbreaker/cve-2025-48708
Lack of argument sanitization leading to password leakage in Ghostscript PDF versions up to 10.05.0.
 dakotanelson/multicat
PoC RAT using the sneaky-creeper data exfiltration library
 joshatticus/ztewaste
Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.
 crackercat/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 oscerd/cve-2026-42527
Reproducer for CVE-2026-42527 — Apache Camel permissive default ObjectInputFilter admits java.net.URL, enabling a DNS-based out-of-band side channel
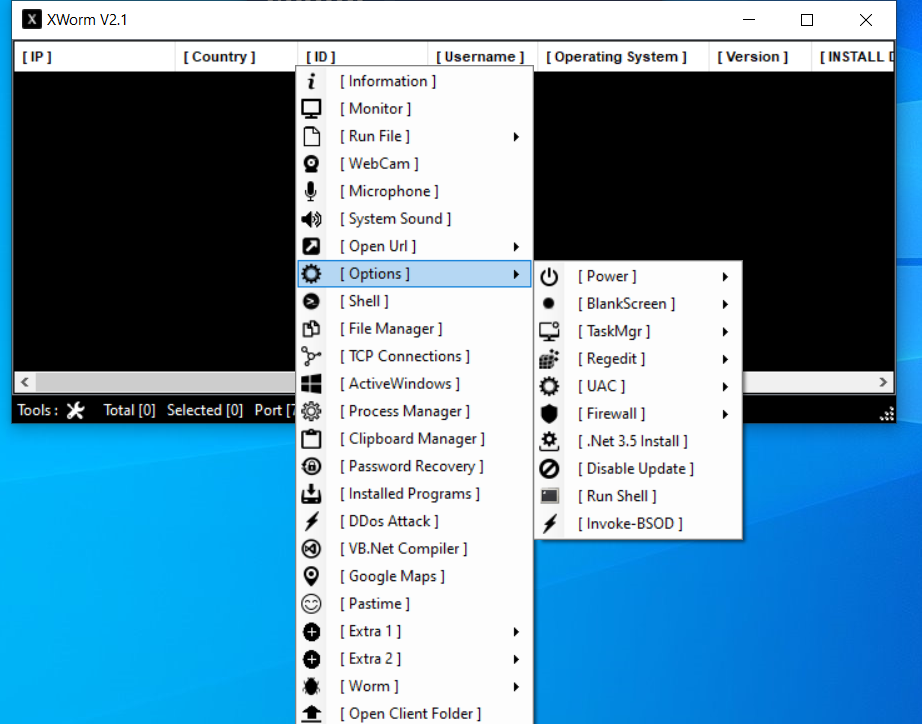
 manturever/xworm-rat
⭐️The famous XWorm RAT, version 2.1. Educational purposes only
 nhh9905/cve-2023-36802
Old CVE, but new way to leak everything.
 0xbassiouny1337/cve-2024-42009
This script exploits a stored XSS vulnerability (CVE-2024-42009) in Roundcube Webmail version 1.6.7. It injects a malicious payload into the webmail…
 george0papasotiriou/cve-2026-21004-sqlite-fts3-match-infoleak-via-query-crafting
Proof-of-concept exploit for CVE-2026-21004: uses crafted SQLite FTS3/4 MATCH prefix queries as a blind oracle to recover indexed secret data…
 inertfluid/cve-2026-54316-lab
Reproduction lab for CVE-2026-54316 (Claude Code WebFetch huggingface.co bare-hostname permission bypass / exfiltration)
 missaels235/poc-cve-2025-24104-py
Proof-of-concept Python script demonstrating iOS file exfiltration via malicious symlink in device backup restoration, targeting the…
 tadash10/exploiting-cve-2021-44228-log4shell-in-a-banking-environment
Objective: Demonstrate the exploitation of the Log4Shell vulnerability (CVE-2021-44228) within a simulated banking application environment.
 george0papasotiriou/cve-2026-2828-webgpu-cross-origin-pixel-stealing-via-timing
Browser PoC demonstrating CVE-2026-2828, a WebGPU timing side-channel that leaks cross-origin iframe pixel values by measuring GPU timestamp-query…
 0xmrma/cve-2026-5061
Consul Template validated where a symlink pointed during template evaluation, but its later dependency fetch read the original path. Retargeting the…
 biitts/cve-2026-56782-gorse-auth-bypass
CVE-2026-56782 — Gorse <0.5.10 unauthenticated DB dump/restore (admin_api_key fail-open). Lab + PoC, verified e2e.
 gmikisilva/cve-2024-33901-proofofconcept
Short program that demonstrates the vulnerability CVE-2024-33901 in KeePassXC version 2.7.7
 networkkiller/cve-2025-9223
POC CVE-2025-9223