
RingReaper
 matheuzsecurity/ringreaper
Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
adversarial-attackcommand-and-controldata-exfiltration+5
388
matheuzsecurity/ringreaperLinux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
 justicerage/ffm
Freedom Fighting Mode: open source hacking harness
 api0cradle/cve-2023-23397-poc-powershell
PowerShell script to exploit CVE-2023-23397 by sending or saving malicious Outlook calendar invitations that trigger NTLM credential leakage via the…
 gosecure/dllpasswordfilterimplant
DLL Password Filter Implant with Exfiltration Capabilities
 thatcherclough/betterbackdoor
A backdoor with a multitude of features.
 d3lb3/keefarcereborn
A standalone DLL that exports databases in cleartext once injected in the KeePass process.
 shell-company/qrexfil
This tool is a command line utility that allows you to convert any binary file into a QRcode movie. The data can then be reassembled visually…
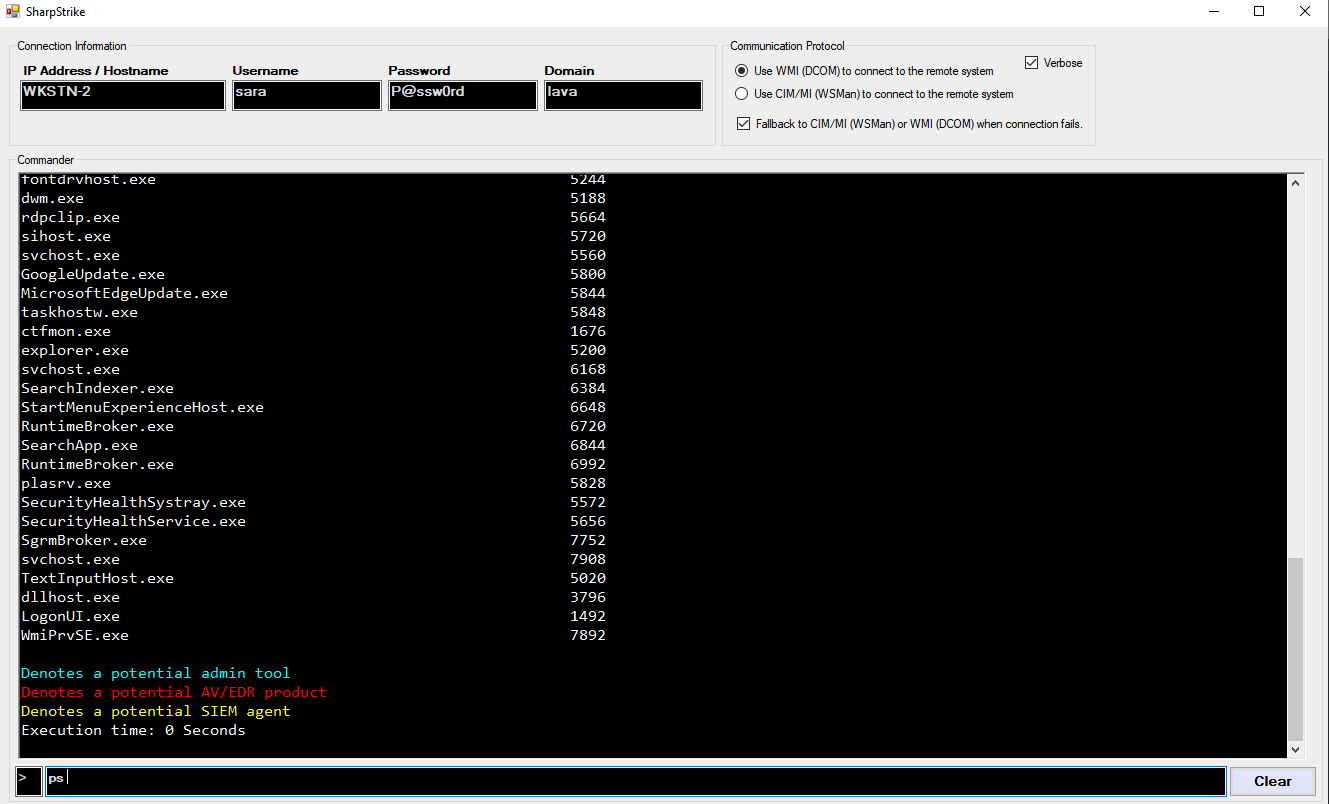 iomoath/sharpstrike
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.
 naveenrudra/rttm
Real Time Threat Monitoring Tool
 cryst4linqq/turkorat
Fully undetected grabber (grabs wallets, passwords, cookies, modifies discord client etc.)
 ioncodes/cve-2020-16938
Bypassing NTFS permissions to read any files as unprivileged user.
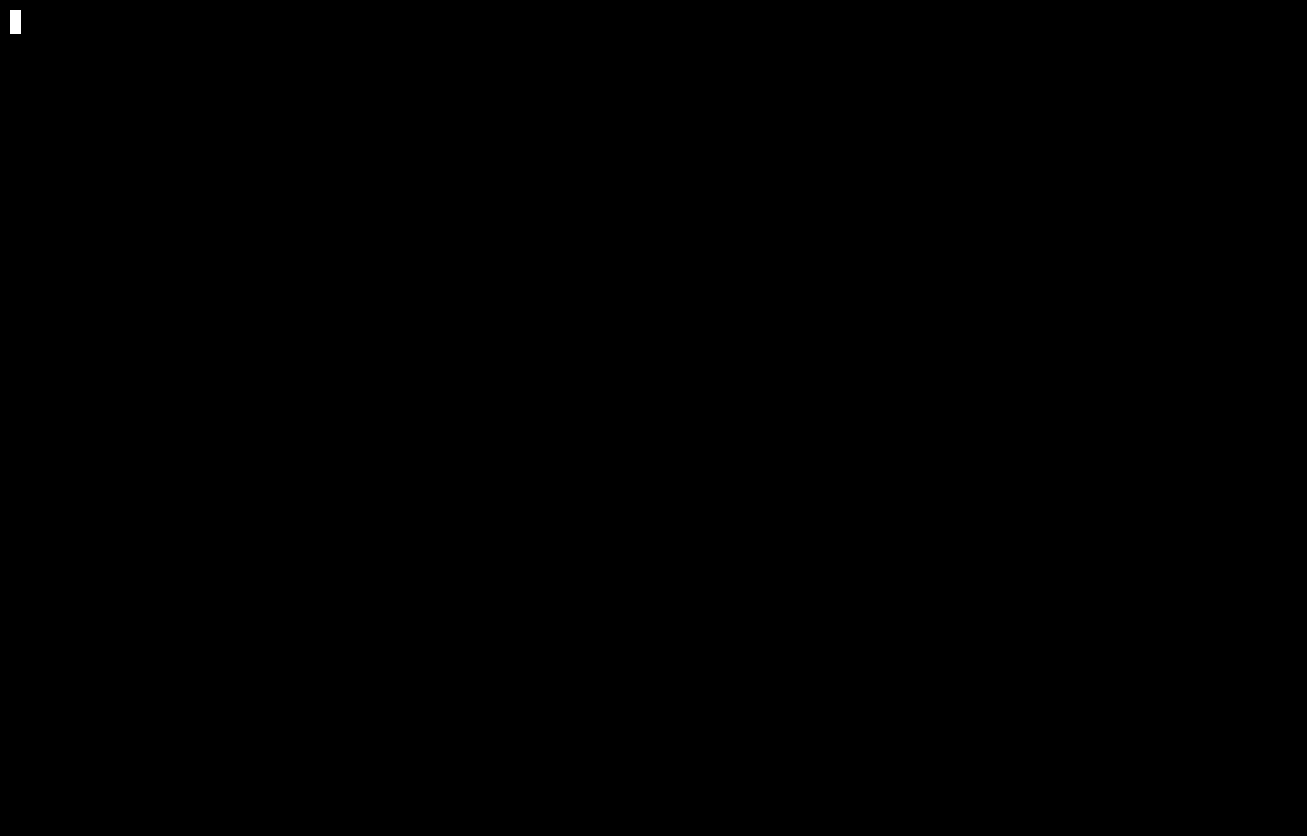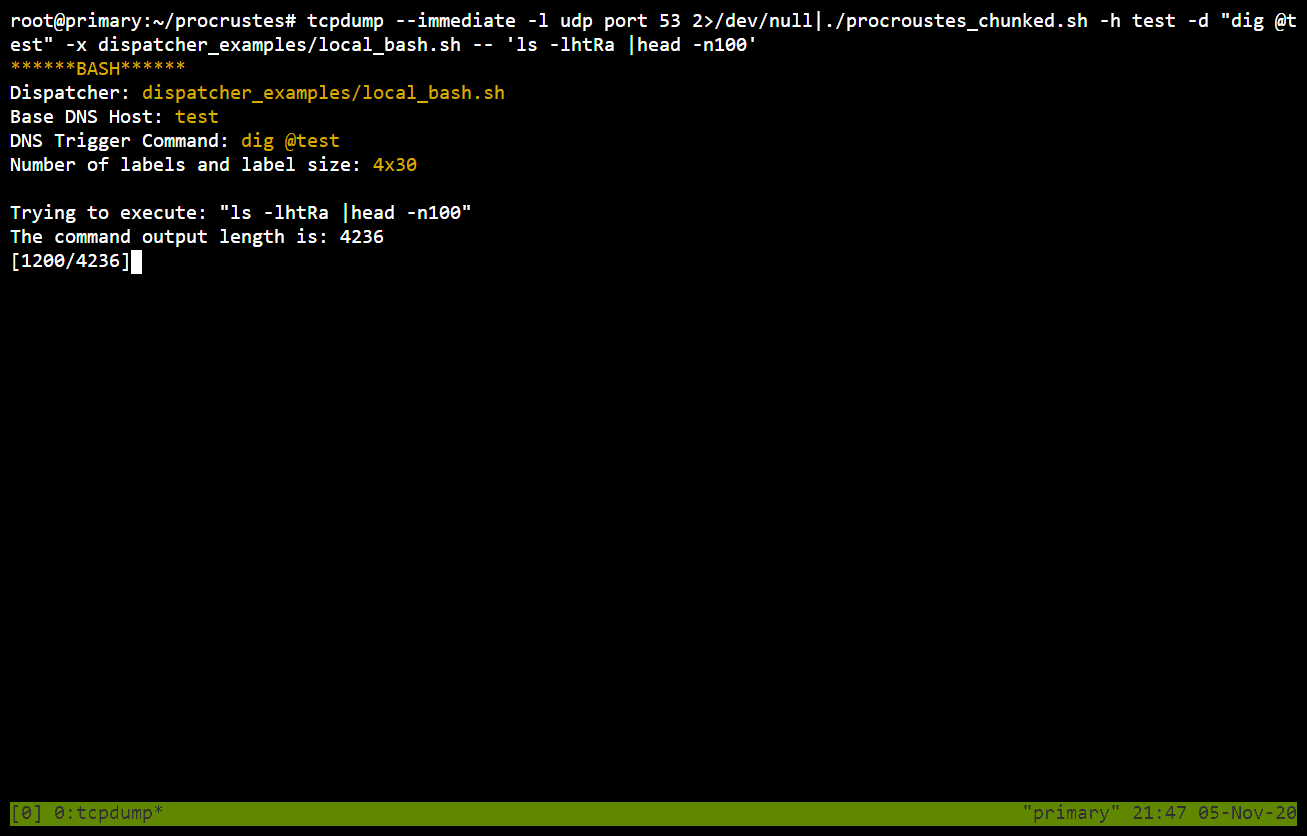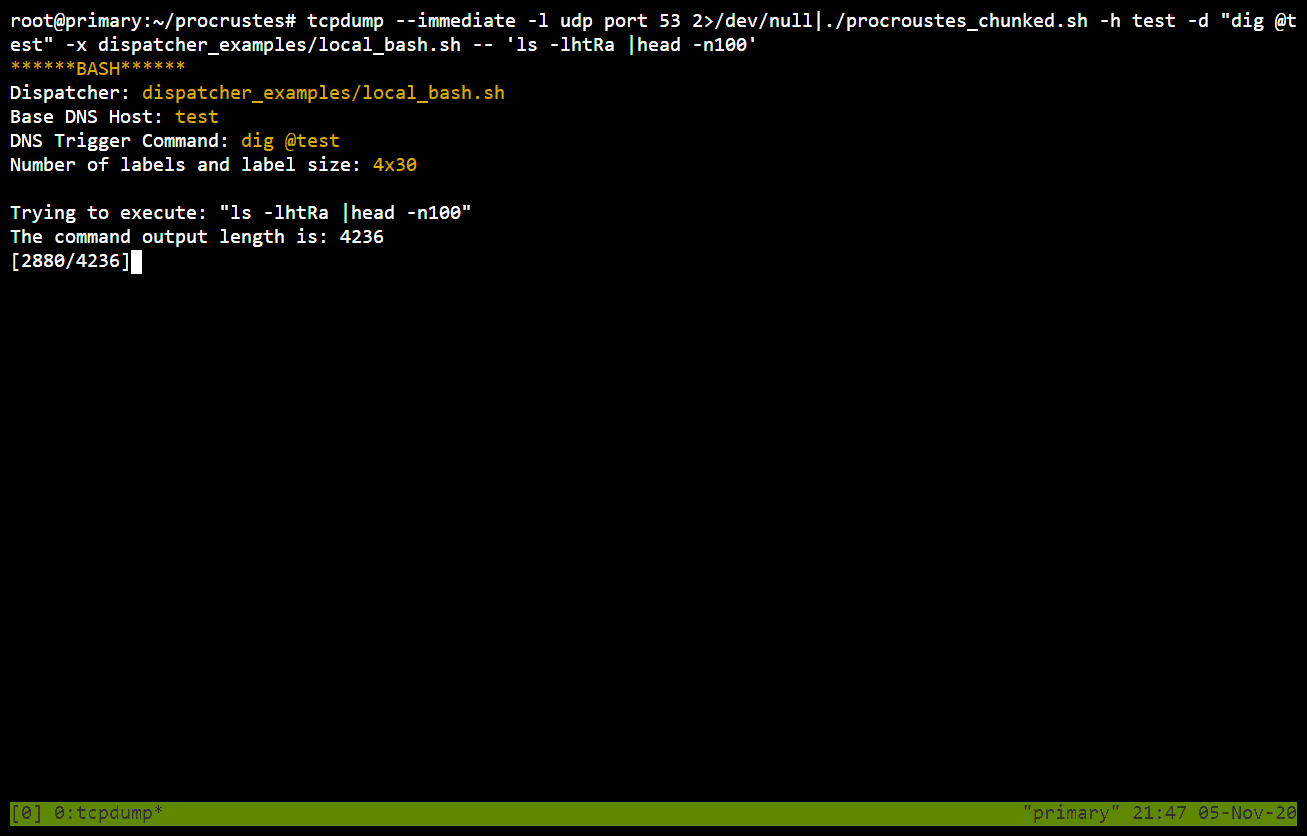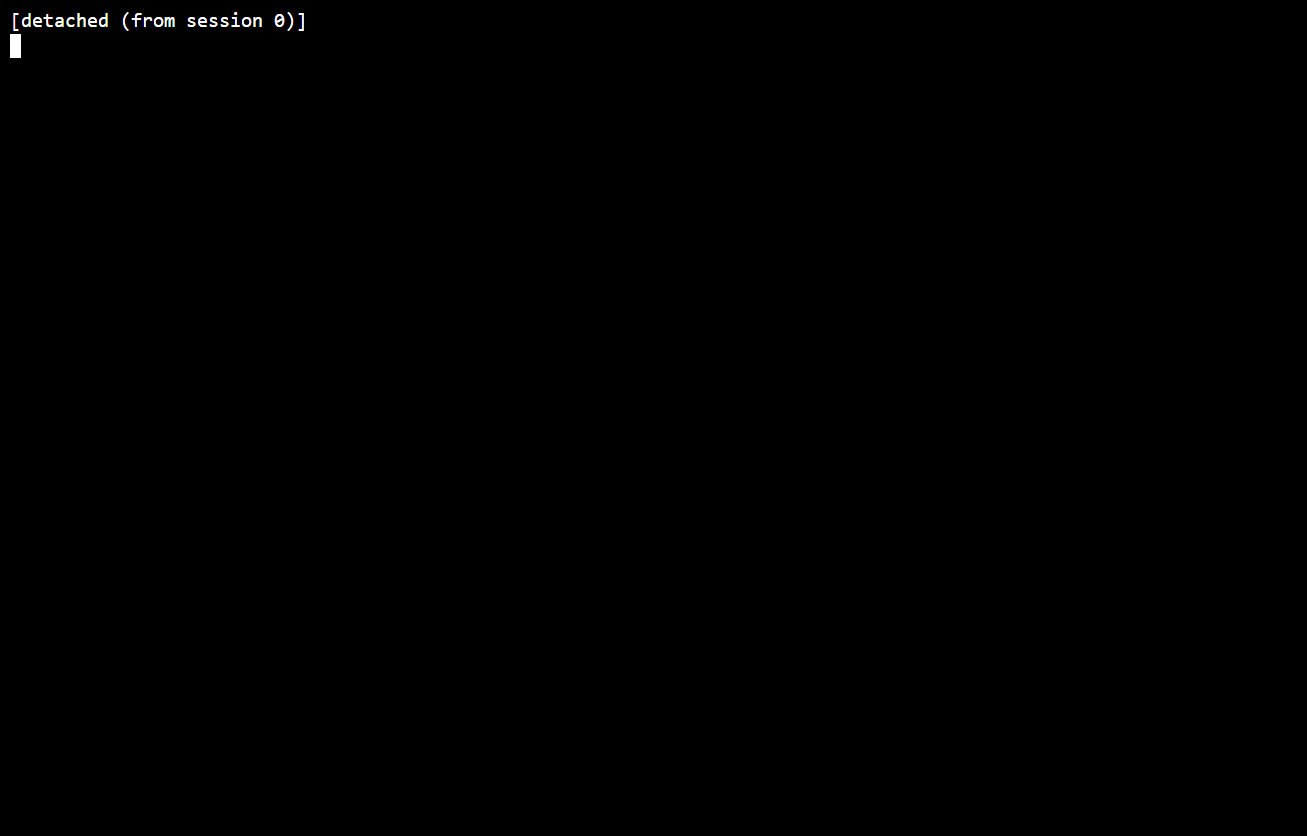 vp777/procrustes
A bash script that automates the exfiltration of data over dns in case we have blind command execution on a server with egress filtering
 zerodaylab/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
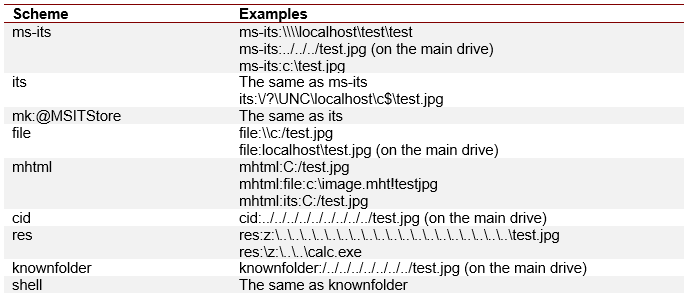 nccgroup/outlookleaktest
The Outlook HTML Leak Test Project
 wkl-sec/wmiexec
Set of python scripts which perform different ways of command execution via WMI protocol.
 internetangel/zerocrumb
Dumping App Bound Protected Credentials & Cookies Without Privileges.
 darkspacesecurity/ssh-stealer
Smart keylogging capability to steal SSH Credentials including password & Private Key