
CVE-2024-12849-Poc
 nxploited/cve-2024-12849-poc
Exploit for CVE-2024-12849, an arbitrary file read vulnerability in WordPress Error Log Viewer plugin. Downloads sensitive files via unauthenticated…
data-exfiltrationexploitationpenetration-testing+2
nxploited/cve-2024-12849-pocExploit for CVE-2024-12849, an arbitrary file read vulnerability in WordPress Error Log Viewer plugin. Downloads sensitive files via unauthenticated…
 mbadanoiu/mal-014
MAL-014: Authenticated Arbitrary File Read in VMware vCenter Server
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 samratashok/nishang
Nishang - Offensive PowerShell for red team, penetration testing and offensive security.
 jonaslejon/malicious-pdf
Generate malicious PDF test files for penetration testing, bug bounty hunting, and red teaming. Tests SSRF, XSS, XXE, NTLM credential theft, and data…
 dagrz/aws_pwn
A collection of AWS penetration testing junk
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.
 cube0x0/sharpmapexec
Windows-native penetration testing swiss army knife for lateral movement, credential access, data exfiltration, and vulnerability scanning across…
 de3vil/stealing
The SteaLinG is an open-source penetration testing framework designed for social engineering
 hazavvip/cve-2025-30208
Exploit scanner for CVE-2025-30208 (Vite arbitrary file read) with multi-variant bypass detection, credential harvesting, SSH key extraction, and…
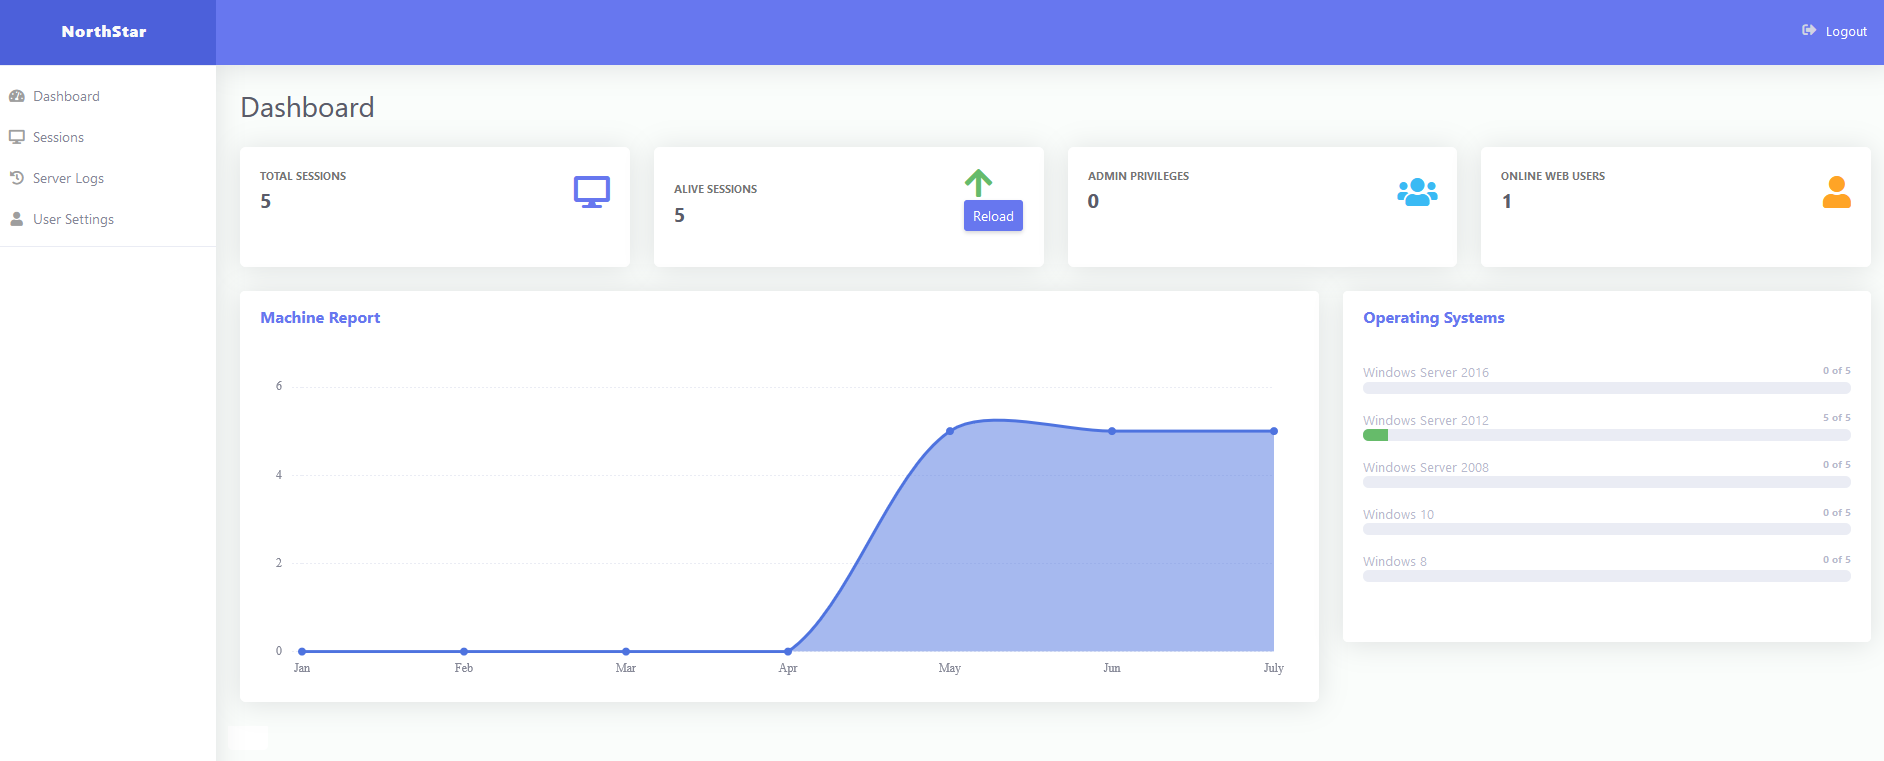 eng1ndes/northstarc2
Web Based Command Control Framework (C2) #C2 #PostExploitation #CommandControl #RedTeam #C2Framework #PHPC2 #.NETMalware #Malware #PHPMalware #CnC…

 designativedave/androrat
Remote Administration Tool for Android devices
 fs0c131y/esfileexploreropenportvuln
ES File Explorer Open Port Vulnerability - CVE-2019-6447
 mwsrc/betterandrorat
Android Remote Access Trojan
 globalpolicy/phonemonitor
A Remote Administration Tool for Android devices
 0xbinder/cve-2024-0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 huntoai/rdroid
[Android RAT] Remotely manage your android phone using PHP Interface