
CVE-2025-66516-Writeup-POC
 chasingimpact/cve-2025-66516-writeup-poc
CVE-2025-66516 working exploit, scanner, explanation.
data-exfiltrationeducationexploitation+5
11
chasingimpact/cve-2025-66516-writeup-pocCVE-2025-66516 working exploit, scanner, explanation.
 nathunandwani/cve-2020-24227
Playground Sessions - Storing User Credentials in Plaintext
 al1ex/rogue-mysql-server
Rogue-MySql-Server
 toanln-cov/cve-2026-74251
Unauthenticated SQL Injection via Attribute Filter in Phoca Cart - CVSS 9.3
 danithehack3r/cve-2024-42009-poc
CVE-2024-42009 Proof of Concept
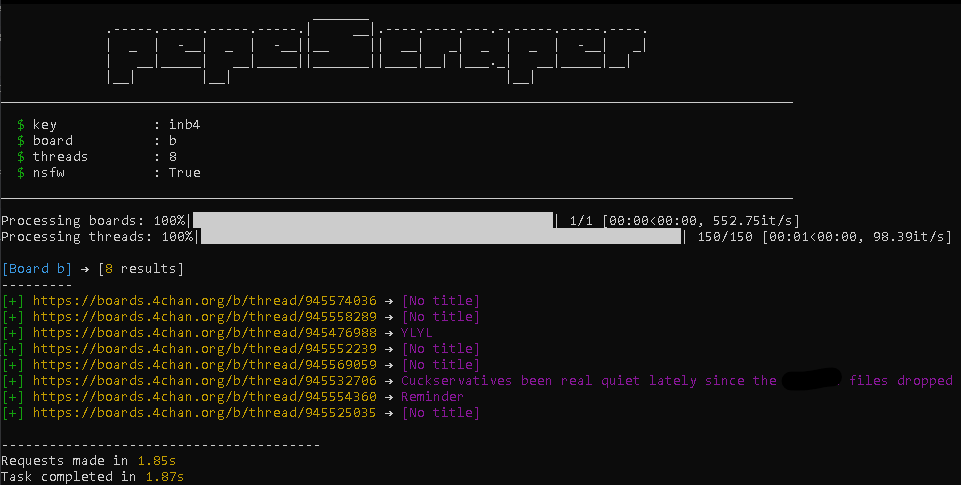 juaanreis/pepescraper
4chan content scraper
 jnschaeffer/cve-2022-44268-detector
Detect images that likely exploit CVE-2022-44268
 fleralex/enseal
Secure, ephemeral secret sharing for developers.
 007criptografia/c-cve-2024-0044
CVE-2024-0044: uma vulnerabilidade de alta gravidade do tipo "executar como qualquer aplicativo" que afeta as versões 12 e 13 do Android
 chethine/esfileexplorer-cve-2019-6447
Exploiting Android Vulnerability in ES File Explorer
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node
 george0papasotiriou/cve-2026-21002-serverless-cold-start-credential-leakage-via-reused-tmp
PoC exploit for CVE-2026-21002 serverless cold-start credential leakage, demonstrating how reused Lambda /tmp directories expose AWS secrets to other…
 tamatahyt/cve-2026-53576
Kestra Unauthenticated RCE Exploit (CVE-2026-53576)
 34zy/apt-backpack
cve-2019-11510, cve-2019-19781, cve-2020-5902, cve-2021-1497, cve-2021-20090, cve-2021-22006, cve-2021-22205, cve-2021-26084,…
 george0papasotiriou/cve-2026-11111-toctou-in-file-permission-check-before-open
Educational CVE PoC for a TOCTOU file-permission race in Flask; uses symlink replacement during the check-open window to disclose sensitive files.
 dshamany/privatesphare
An at-rest encrypted filesharing application with multiple clients who seek to share privately, without tracking.
 casp3r0x0/cve-2025-58443
FOGProject Authentication bypass CVE-2025-58443 Exploit