

nmap
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
bluetooth-securitydatabase-securitydata-exfiltration+18
13.7k
nmap/nmapHigh-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 fsecurelabs/n1qlmap
The tool exfiltrates data from Couchbase database by exploiting N1QL injection vulnerabilities.
 karlvbiron/mad-cat
MAD-CAT (Meow Attack Data Corruption Automation Tool) is a comprehensive security tool designed to simulate data corruption attacks against multiple…
 citcheese/odbparser
OSINT tool to search, parse and dump only the open Elasticsearch and MongoDB directories that have the data you care about exposing
 shieldersec/cve-2020-11579
Exploit code for CVE-2020-11579, an arbitrary file disclosure through the MySQL client in PHPKB
 cybertechajju/cve-2025-14847_expolit
a critical memory disclosure vulnerability in MongoDB's zlib compression handling. This tool allows security researchers to extract sensitive data…
 al1ex/rogue-mysql-server
Rogue-MySql-Server
 mbadanoiu/cve-2024-34693
CVE-2024-34693: Server Arbitrary File Read in Apache Superset
 george0papasotiriou/cve-2026-21004-sqlite-fts3-match-infoleak-via-query-crafting
Proof-of-concept exploit for CVE-2026-21004: uses crafted SQLite FTS3/4 MATCH prefix queries as a blind oracle to recover indexed secret data…
 proxydom/supahunter
Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…
 alexcyberx/cve-2025-14847_expolit
Exploit tool for CVE-2025-14847, a MongoDB memory disclosure vulnerability, enabling multi-threaded extraction of sensitive data and secrets from…
 casp3r0x0/cve-2025-58443
FOGProject Authentication bypass CVE-2025-58443 Exploit
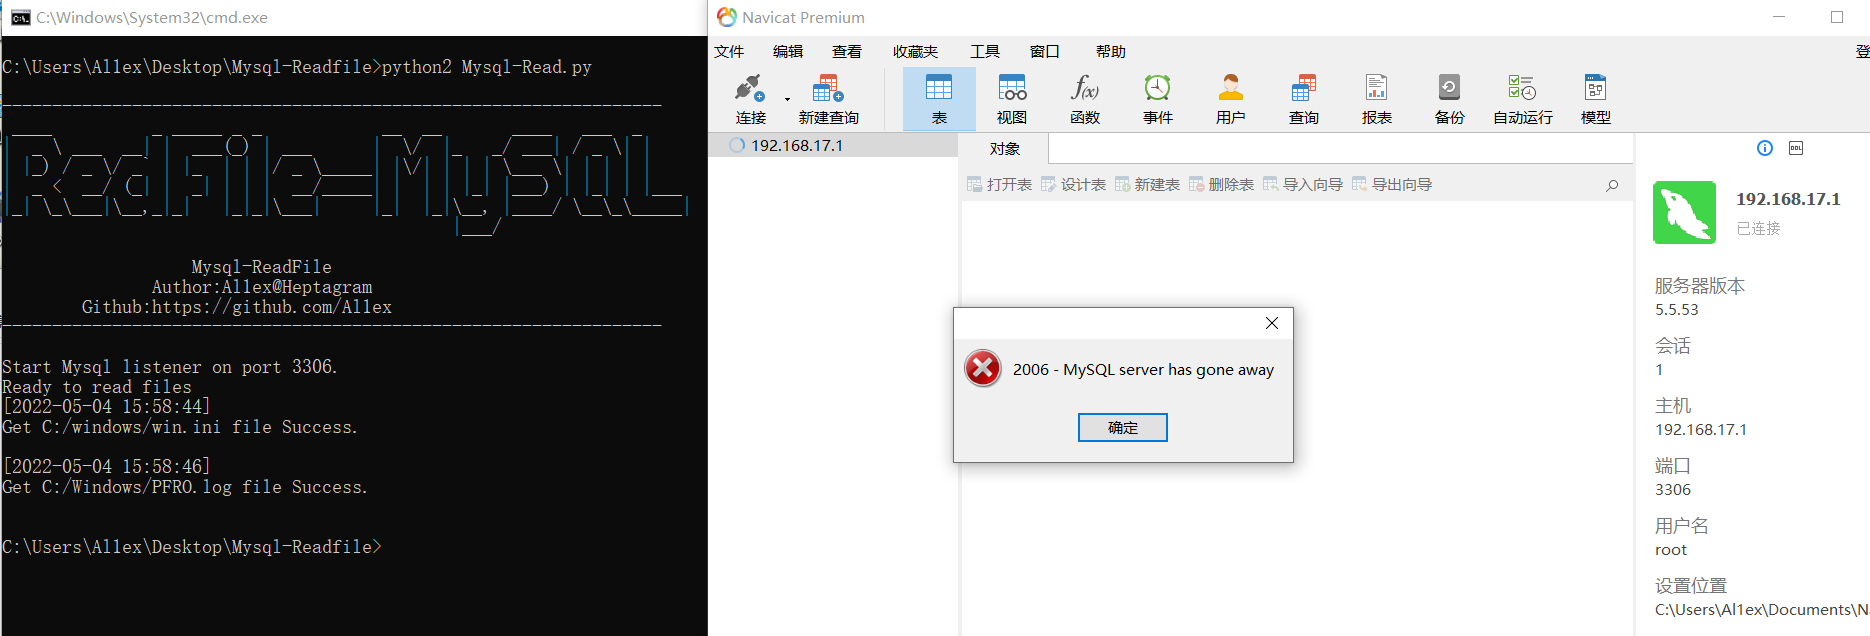
 im-hanzou/mongobleed
CVE-2025-14847 PoC exploit for MongoDB heap memory disclosure
 daturasaturated/adminer-cve-2021-43008
Adminer CVE-2021-43008 PoC
 mr-r00t11/cve-2024-34693
An input validation vulnerability in Apache Superset allows an authenticated attacker to create a MariaDB connection with local_infile enabled,…
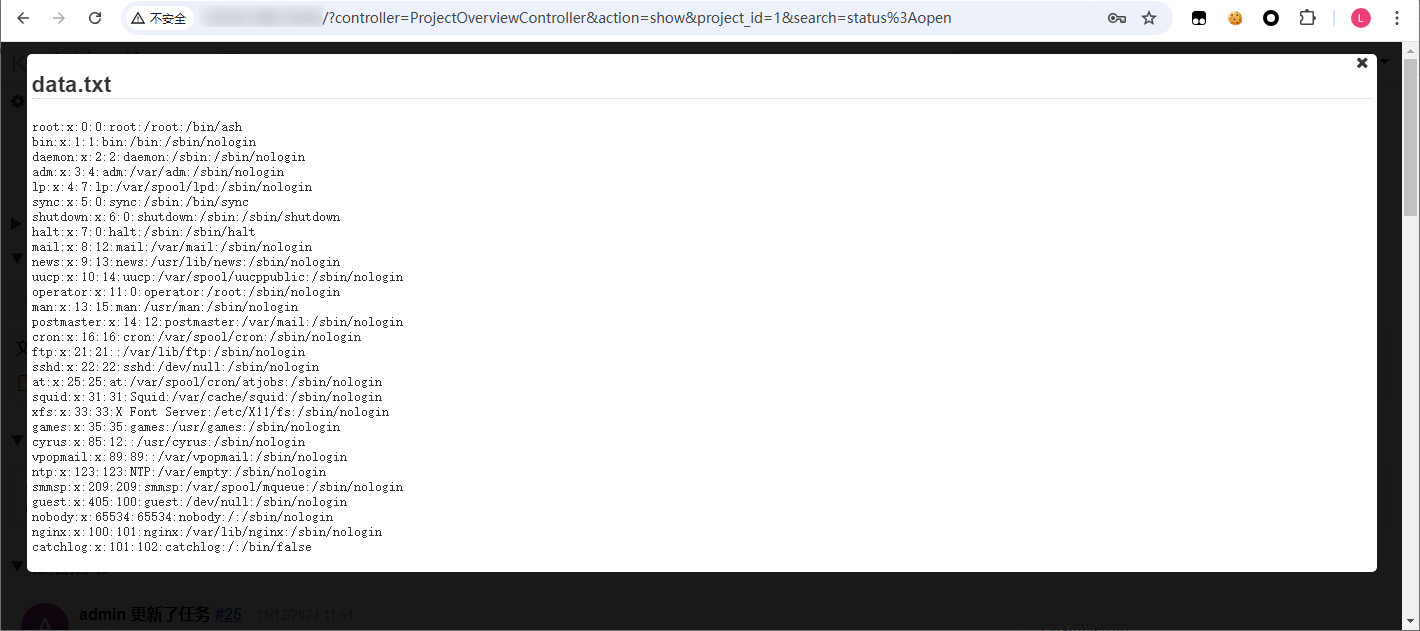 l20170217b/cve-2024-51747
Proof-of-concept exploit for CVE-2024-51747 enabling authenticated file read and deletion via SQLite database manipulation in a web application's…