
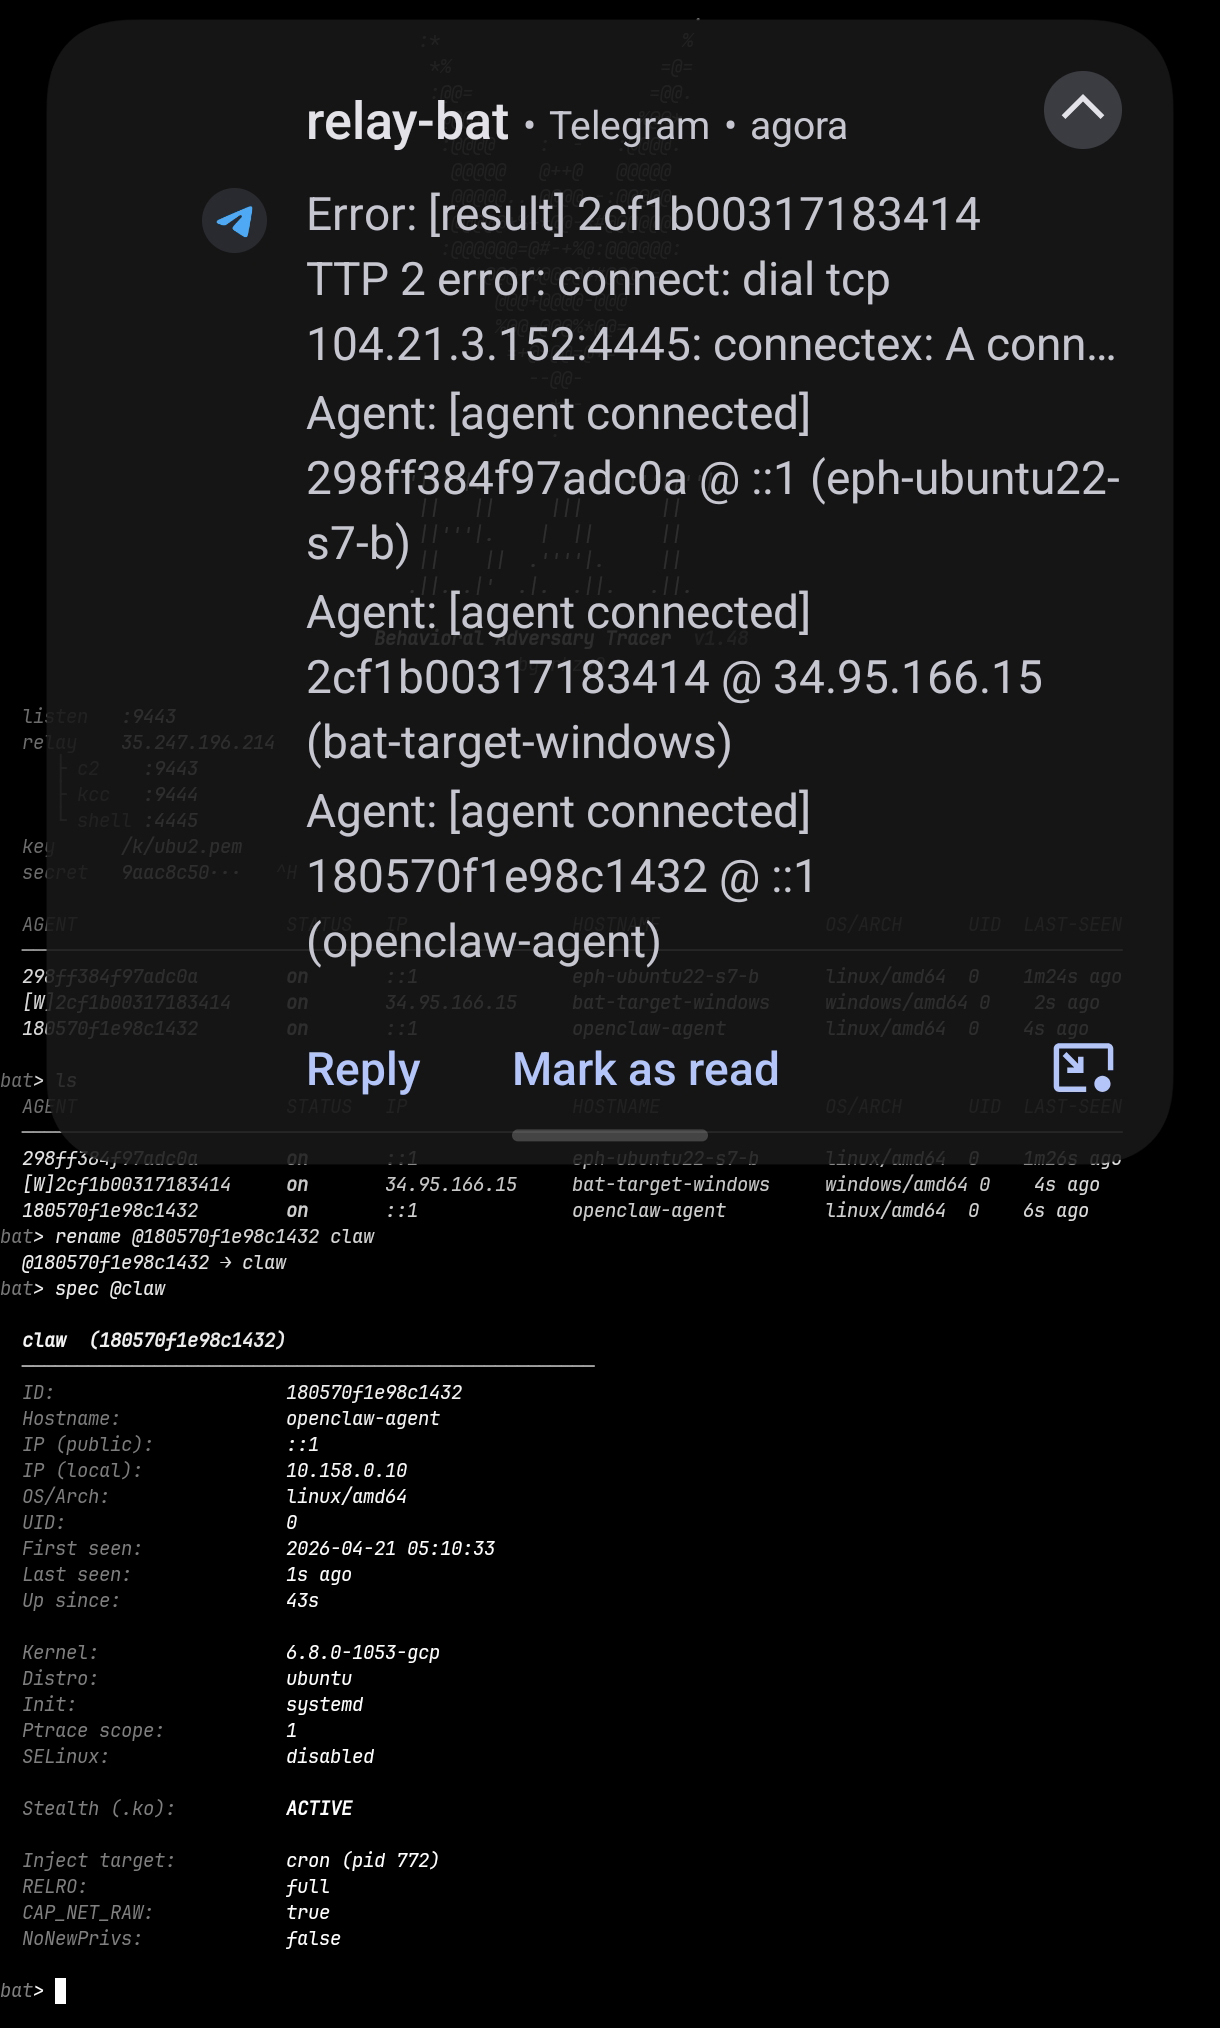
bat
 rhzv0/bat
Full-spectrum Linux adversary simulation platform with kernel-level stealth, C2 beaconing, privilege escalation, credential harvesting, lateral…
command-and-controldata-exfiltrationlateral-movement+5
375 months ago
rhzv0/batFull-spectrum Linux adversary simulation platform with kernel-level stealth, C2 beaconing, privilege escalation, credential harvesting, lateral…
 kira2040k/redbloodc2
Node.js command-and-control server with FUD payload generation, encrypted communication, session management, and modules for data exfiltration and…
 f4dee-backup/cve-2025-24071
Exploit script for CVE-2025-24071 that leaks NTLM hashes from Windows by extracting a crafted ZIP/RAR file, exploiting .library-ms file handling.…
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 moond4rk/hackbrowserdata
Extract and decrypt browser data, supporting multiple data types, runnable on various operating systems (macOS, Windows, Linux).
 wiredpulse/invoke-hivenightmare
PoC for CVE-2021-36934, which enables a standard user to be able to retrieve the SAM, Security, and Software Registry hives in Windows 10 version…
 igh0st/gh0st3.6_src
Remote Access Trojan (RAT) source code for learning C2 communication, payload delivery, and post-exploitation techniques in Windows environments.
 3nailsinfosec/dcvc2
Discord voice channel C2 framework for covert command and control operations. Transmits all data via RTP packets over voice channels, leaving no…
 rails/rails-forensics-cve-2026-66066
Forensic toolkit and agent skills for investigating Rails Active Storage/libvips CVE-2026-66066: detects crafted blob indicators, exposure windows,…
 dragon56yt/revshell
A comprehensive educational repository demonstrating the evolution of a Windows reverse shell implant, from a simple proof‑of‑concept (v1.0) to a…
 dagowda/notrdp
Havoc C2 plugin that creates a hidden Windows desktop, streams it to a browser viewer, and injects mouse/keyboard input for covert remote control.
 threatexpert/gonc
Netcat with automated NAT traversal, secure P2P, and advanced features for shell access, file transfer, and network proxying.
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 jimywork/cromos
Cromos is a tool for downloading legitimate extensions of the Chrome Web Store and inject codes in the background of the application.
 p0dalirius/dumpsmbshare
A python script to dump files and folders remotely from a Windows SMB share.
 maldevel/dicerosbicornis
A fully featured Windows backdoor that uses email as a C&C server
 toxy4ny/bl00dym4ry
Educational trojan simulator for cybersecurity training, simulating phishing attacks with social engineering, system reconnaissance, anti-sandbox…
 zveriu/cve-2009-0229-poc
PoC for CVE-2009-0229 "Print Spooler Read File Vulnerability" LPE AFR (related to CVE-2020-1048)