
woo
 randomrobbiebf/woo
Exploit woocommerce SQLI and grab user and password hash
data-exfiltrationexploitationinformation-gathering+3
2
randomrobbiebf/wooExploit woocommerce SQLI and grab user and password hash
 nxploited/cve-2025-7401
Premium Age Verification / Restriction for WordPress <= 3.0.2 - Unauthenticated Arbitrary File Read and Write
 cerberusmrxi/cve-2025-55182-advanced-react-server-components-rce-exploit
Advanced React Server Components RCE scanner for CVE-2025-55182. Features: multi-stage fingerprinting, vulnerability verification, DNS exfiltration,…
 darabium/cve-2024-28987
**CVE-2024-28987** is a critical vulnerability in SolarWinds Web Help Desk (WHD) that allows remote attackers to access sensitive ticket information…
 huseyn0vs/cve-2026-16540-simplyscheduleappointments
CVE-2026-16540 — Simply Schedule Appointments < 1.6.12.6 Unauthenticated Appointment Data Disclosure and Mass Deletion
 themehackers/cve-2026-22804
This repository contains a Proof of Concept (PoC) exploit for the Stored Cross-Site Scripting (XSS) vulnerability in Termix, which can lead to Local…
 smarttfoxx/cve-2025-65321
Language Sloth Sloth Bot 1.0 is vulnerable to Directory Traversal in the gif() and png() functions. The functions build file paths using unsanitized…
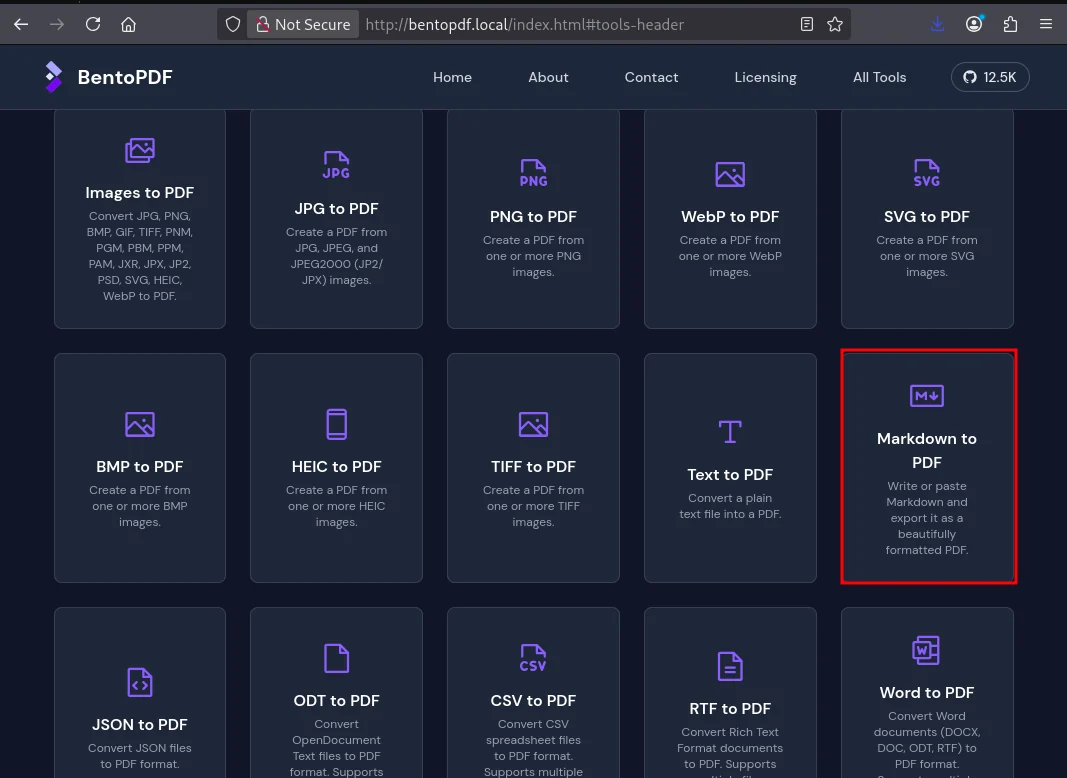 astaruf/cve-2026-41653
Proof-of-concept exploit for CVE-2026-41653, a stored XSS in BentoPDF that enables silent file exfiltration and WASM supply-chain hijacking.
 efeanilarslan/cve-2026-42167-exploit
Python exploit for CVE-2026-42167 (ProFTPD mod_sql). Features automated file scanning and timing-based blind data exfiltration.
 davidrxchester/cve-2026-5530
Proof-of-concept exploit for CVE-2026-5530, an SSRF in Ollama's Pull/Push API, enabling internal endpoint enumeration and full response exfiltration…
 jfriedli/cve-2025-12137
Proof-of-concept exploit for CVE-2025-12137 demonstrating local file disclosure via a WordPress plugin's REST API importer endpoint. Includes…
 ysaxon/tftplunder
Info and exploit for CVE-2023-29930: blind file read/write in Genesys TFTP provisioning server configuration
 xalfie/fortigate-belsen-leak-dump-cve-2022-40684-
Extracts passwords from Fortinet VPN leak dumps associated with CVE-2022-40684, processing subfolders for vpn-passwords.txt and outputting cleaned…
 nicetop1027/cve-2026-discord
Critical vulnerability report detailing zero-day Remote Debugging Port exposure in Discord macOS client leading to account takeover, spyware, worm…
 audiopump/cve-2025-66723
CVE-2025-66723: inMusic Brands Engine DJ >=3.0.0 through <4.3.4 exposes local and network files to external parties
 azhariramadhan/cve-2026-39047
Printer exploitation framework for security testing via raw port 9100, featuring PCL payload delivery, DoS bombing, C2 QR codes, phishing QR codes,…
 hazavvip/cve-2025-30208
Exploit scanner for CVE-2025-30208 (Vite arbitrary file read) with multi-variant bypass detection, credential harvesting, SSH key extraction, and…
 jet-pentest/cve-2021-27187
Proof-of-concept for CVE-2021-27187: cleartext credential storage in FX Aggregator terminal client login.sav file, enabling local credential theft…