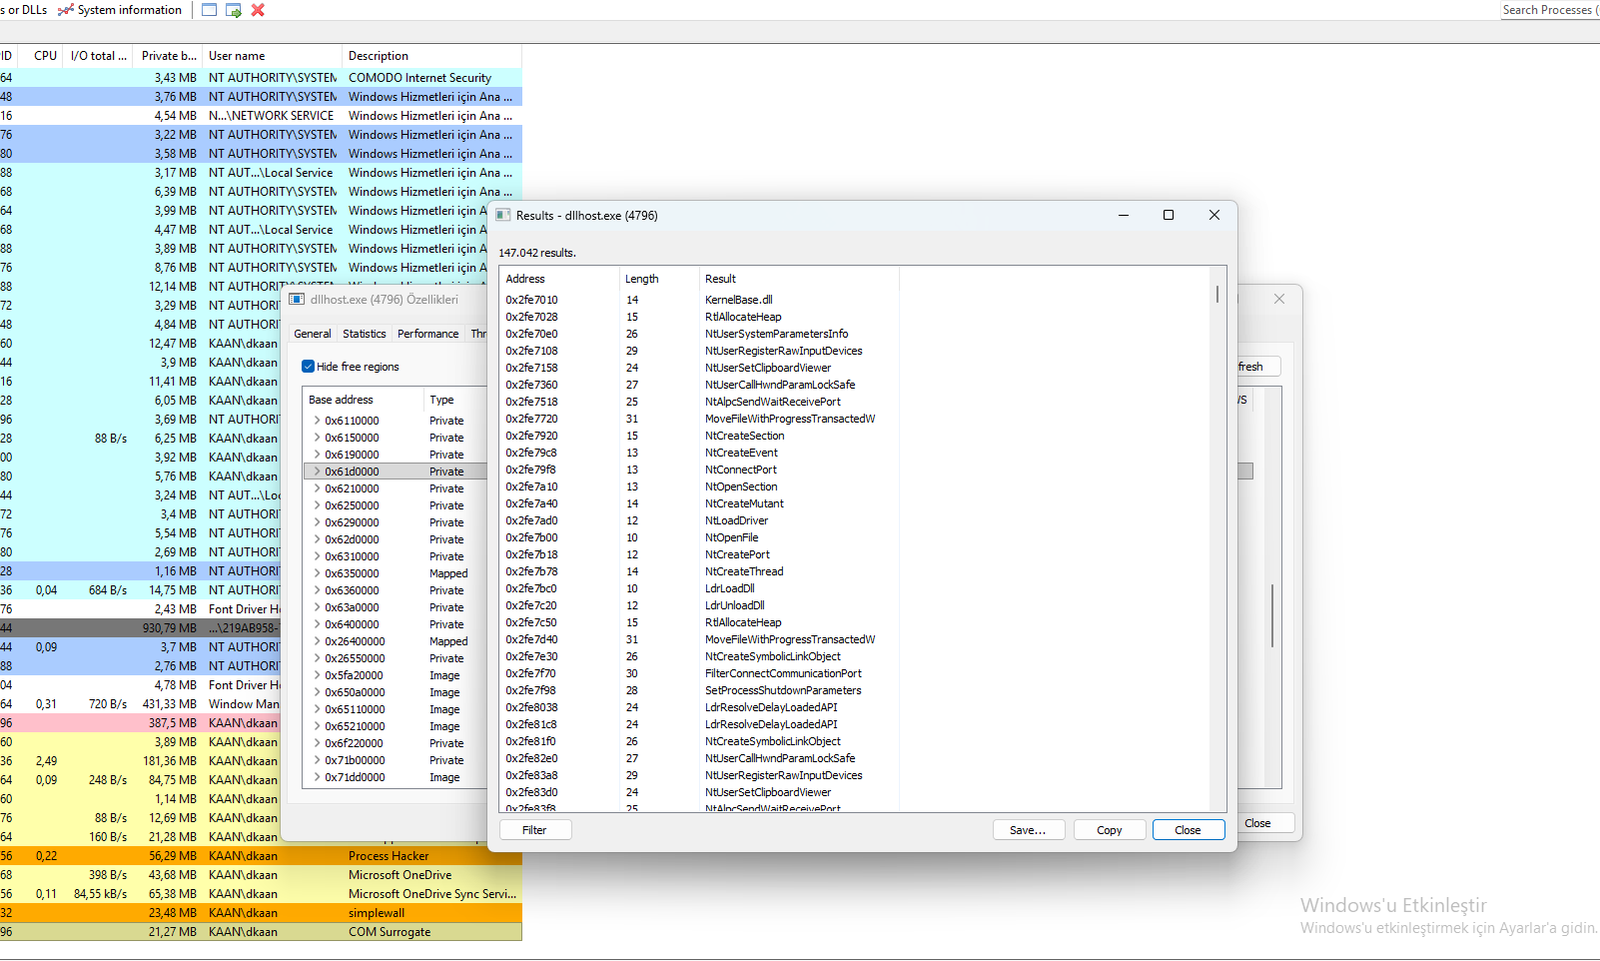
Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis

In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

Dump cookies and credentials directly from Chrome/Edge process memory

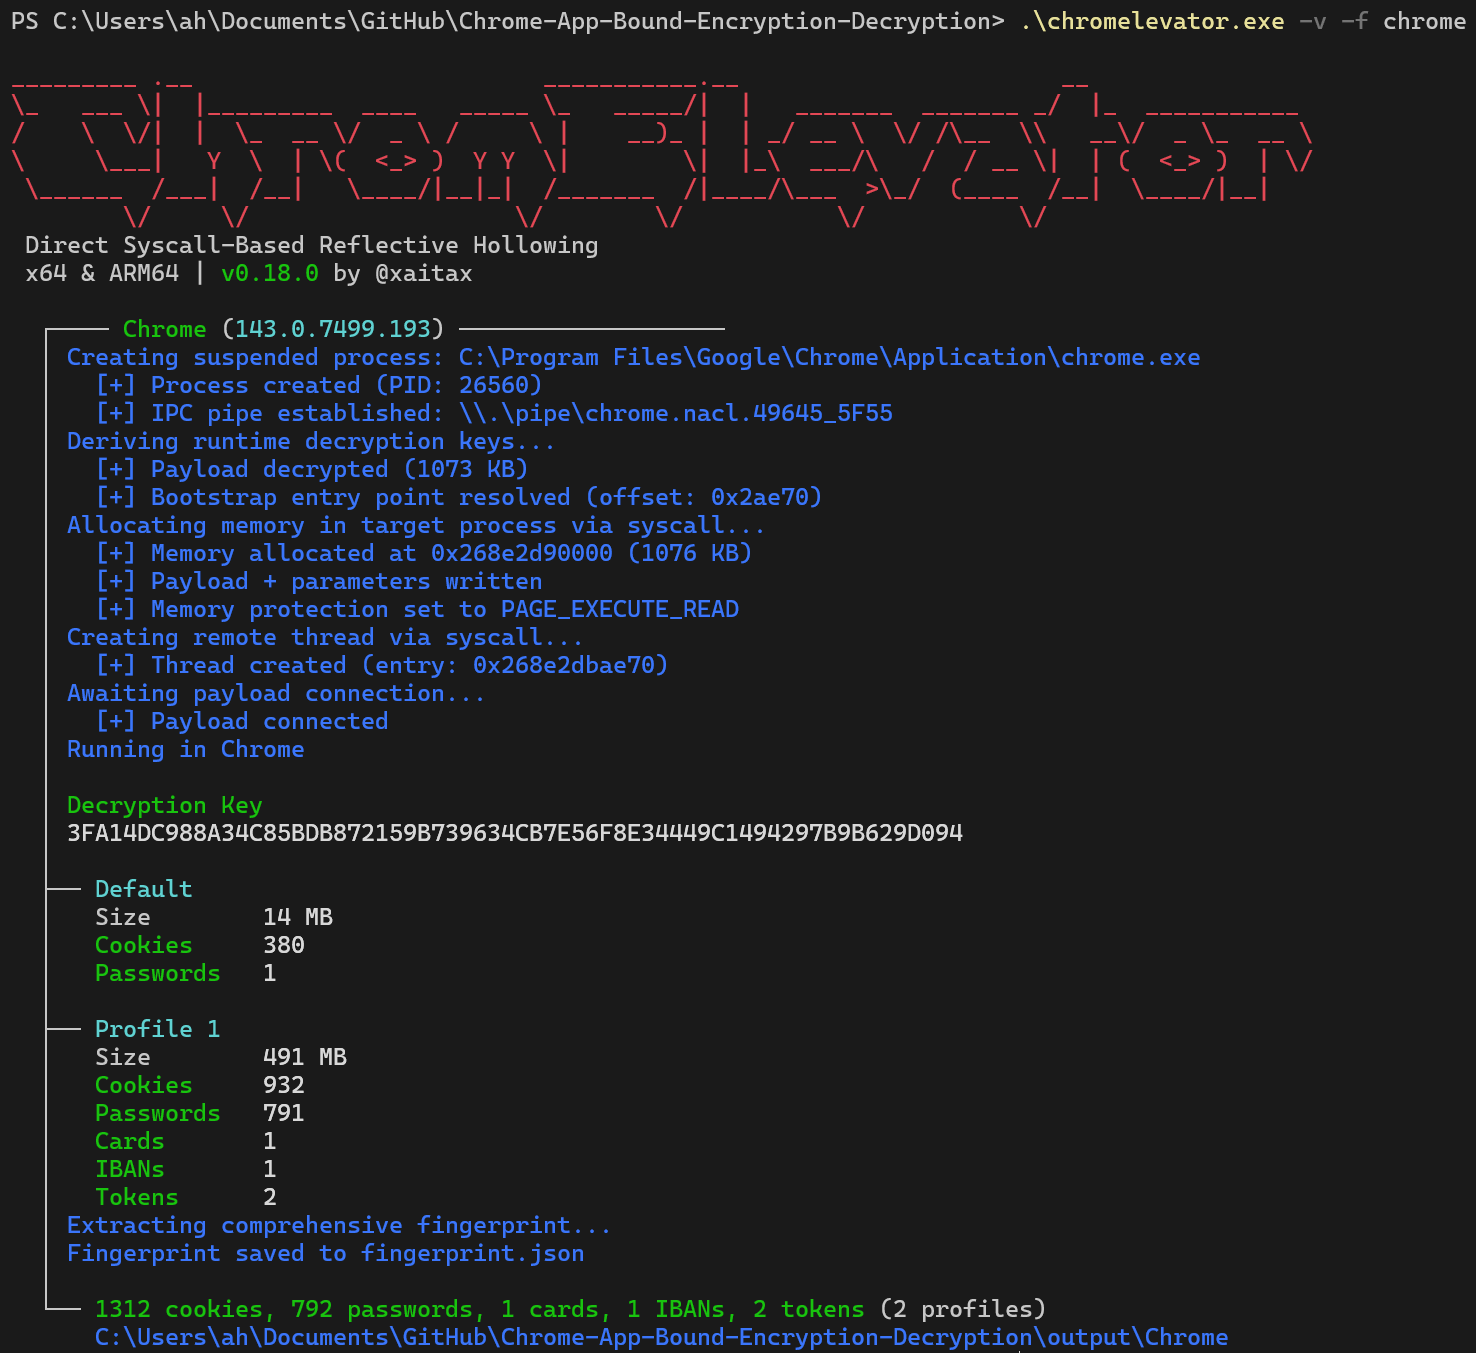
Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…

CitrixBleed2 poc

My experiments in weaponizing Nim (https://nim-lang.org/)

High speed/Low cost CommonCrawl RegExp in Node.js

Exploit for Adobe Reader DC out-of-bounds read vulnerability (CVE-2021-45067) that leaks sensitive information from the sandboxed process via…

Simple Process Dumper using DMA over a PCIe FPGA device

Physmem2profit can be used to create a minidump of a target hosts' LSASS process by analysing physical memory remotely

Solitude is a privacy analysis tool that enables anyone to conduct their own privacy investigations. Whether a curious novice or a more advanced…

LeakScraper is an efficient set of tools to process and visualize huge text files containing credentials. Theses tools are designed to help…

Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.