
darknet-mcp-server
 badchars/darknet-mcp-server
66-tool MCP server for dark web intelligence — breach data, ransomware tracking, Tor .onion access, malware analysis, blockchain intel, exploit…
ai-securitydata-exfiltrationinformation-gathering+8
412
badchars/darknet-mcp-server66-tool MCP server for dark web intelligence — breach data, ransomware tracking, Tor .onion access, malware analysis, blockchain intel, exploit…
 kaitokidc500/cve-2024-23700-c2-server
Source code minh họa máy chủ c2 demo kịch bản thực thi của CVE-2024-23700
 0xterror/cve-2023-22047-oracle-peoplesoft-lfi
CVE-2023-22047 is a critical unauthenticated Local File Inclusion (LFI) vulnerability in Oracle PeopleSoft Enterprise PeopleTools. This exploit…
 cerberusmrxi/cve-2025-55182-advanced-react-server-components-rce-exploit
Advanced React Server Components RCE scanner for CVE-2025-55182. Features: multi-stage fingerprinting, vulnerability verification, DNS exfiltration,…
 doany1/cve-2026-24849
Proof-of-concept exploit for CVE-2026-24849, an authenticated path-traversal arbitrary file read in OpenEMR's EtherFax module. Reads server files…
 hazavvip/cve-2025-30208
Exploit scanner for CVE-2025-30208 (Vite arbitrary file read) with multi-variant bypass detection, credential harvesting, SSH key extraction, and…
 jricramc/aigate
AI Prompt Secret Scanner: local proxy and Claude Code hook that blocks secrets before they reach AI APIs
 jfriedli/cve-2025-12137
Proof-of-concept exploit for CVE-2025-12137 demonstrating local file disclosure via a WordPress plugin's REST API importer endpoint. Includes…
 audiopump/cve-2025-66723
CVE-2025-66723: inMusic Brands Engine DJ >=3.0.0 through <4.3.4 exposes local and network files to external parties
 scumfrog/fiberbreak
React2Shell Exploitation Tool (CVE-2025-55182)
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 stonelinks/react-cve-2025-55182
Analysis of malware found on a server compromised via CVE-2025-55182, including obfuscated dropper, C2 communication, persistence mechanisms, and…
 aseemyash/krle
CVE-2025-55182 & CVE-2025-66478 proof of concepts
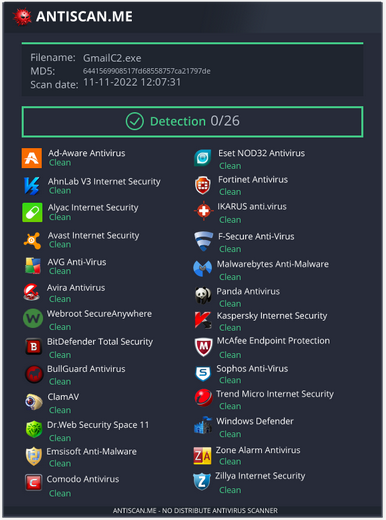 reveng007/sharpgmailc2
Our Friendly Gmail will act as Server and implant will exfiltrate data via smtp and will read commands from C2 (Gmail) via imap protocol
 bbo513/cve-2023-7231
PoC and Disclosure for CVE-2023-7231 – Memcached Gopher RCE chain
 mbadanoiu/cve-2024-34693
CVE-2024-34693: Server Arbitrary File Read in Apache Superset
 saumyajeetdas/godgenesis
A Python3 based C2 server to make life of red teamer a bit easier. The payload is capable to bypass all the known antiviruses and endpoints.