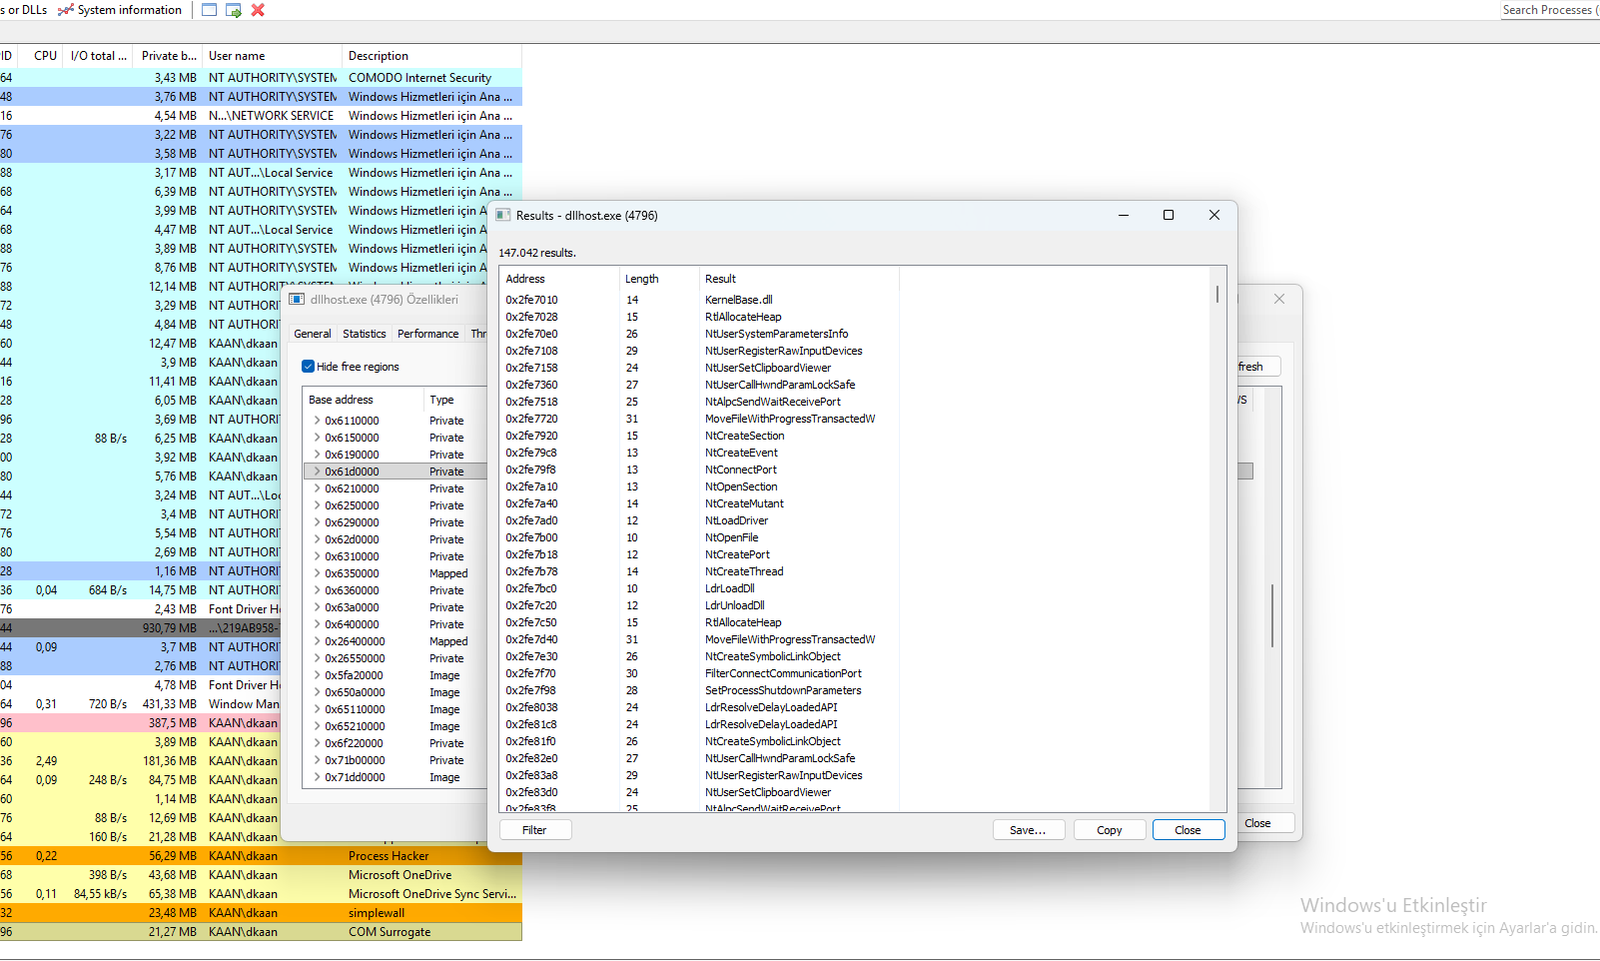
Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis

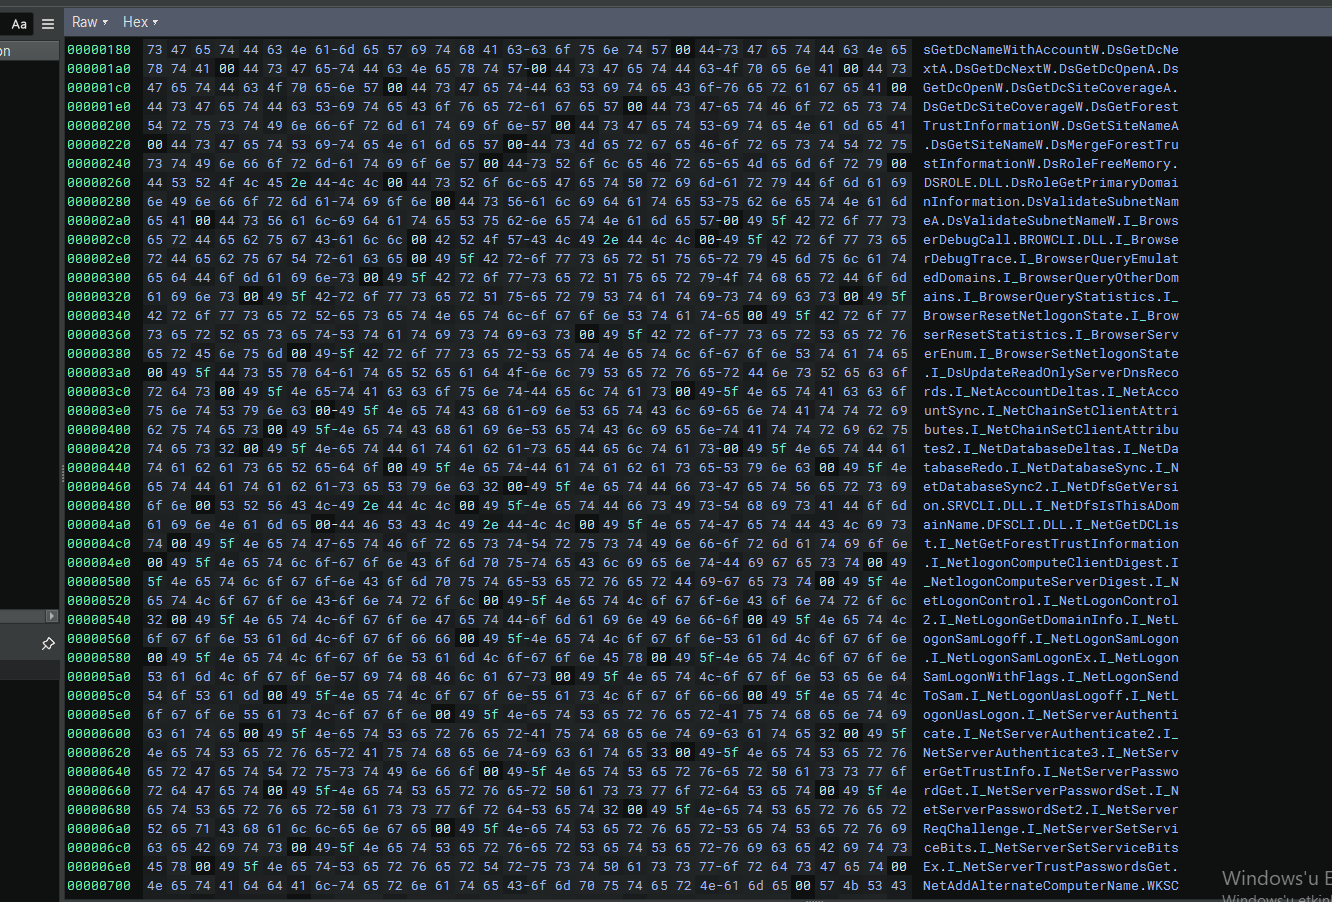
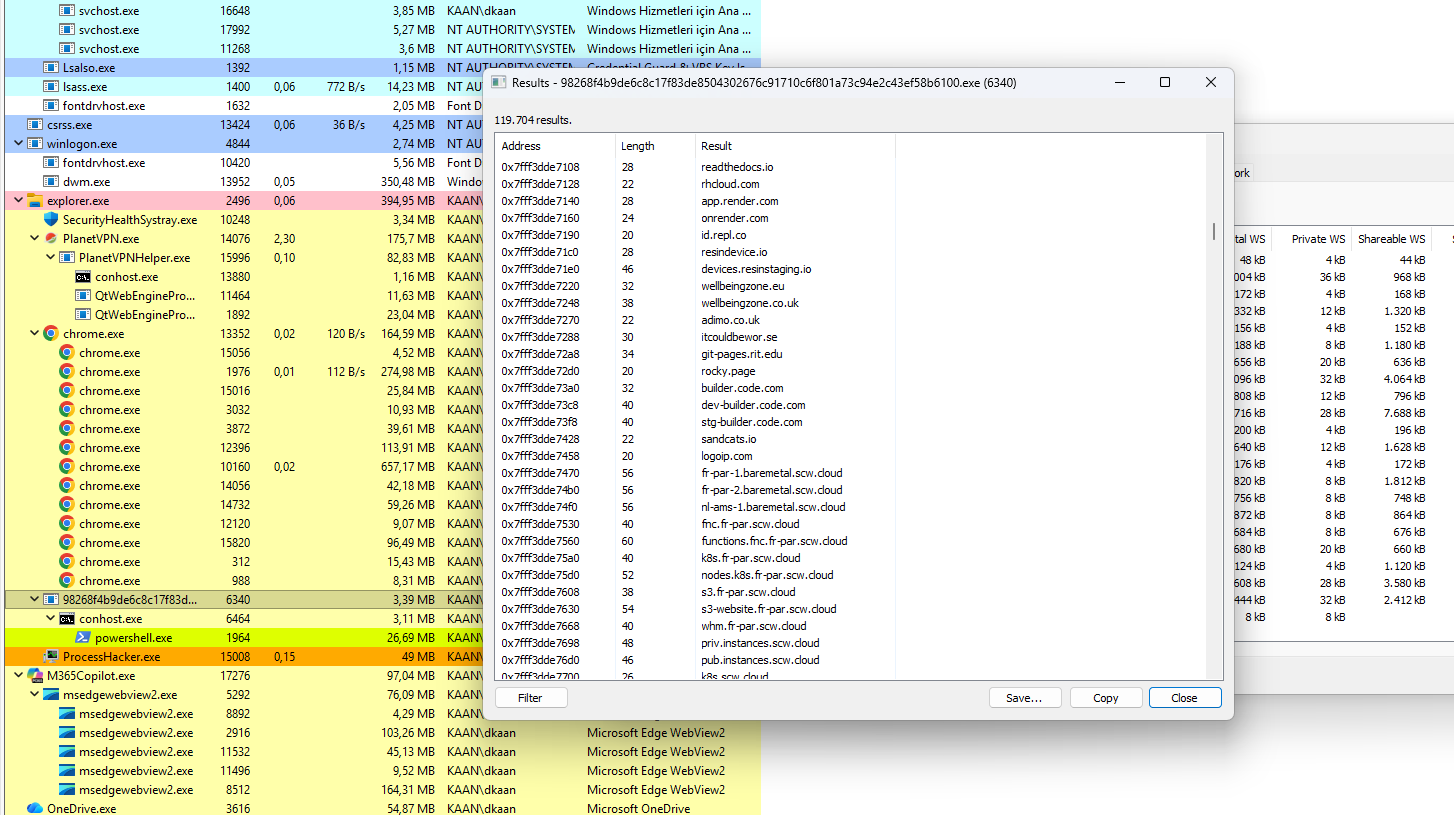
In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

Source code minh họa máy chủ c2 demo kịch bản thực thi của CVE-2024-23700

Reverse engineering analysis of AcrStealer, a sophisticated info-stealer that uses custom protocols, browser credential theft, and payload…

Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…

Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, exploiting WebKit (CVE-2025-24201) and Core Media (CVE-2025-24085) to achieve sandbox…

This is a SMS And Call Bomber For Linux And Termux

OWASP iGoat - A Learning Tool for iOS App Pentesting and Security by Swaroop Yermalkar

A Remote Administration Tool for Android devices

ES File Explorer Open Port Vulnerability - CVE-2019-6447

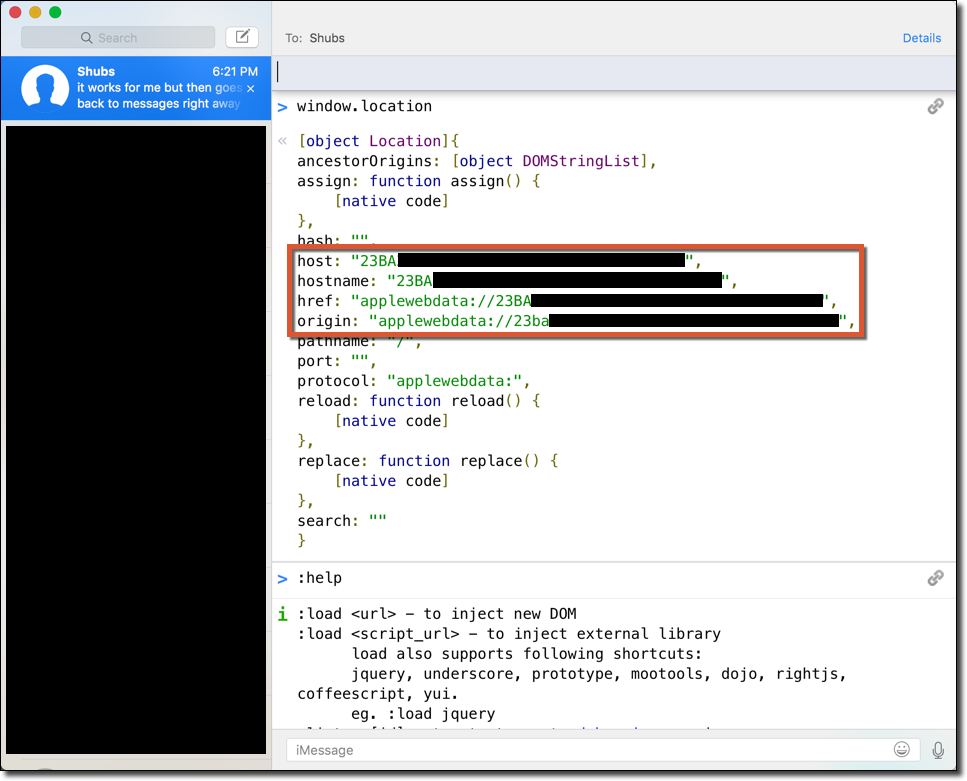
Extraction of iMessage Data via XSS