
CVE-2026-86259
 uziii2208/cve-2026-86259
OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass
api-securitycloud-securitydata-exfiltration+6
uziii2208/cve-2026-86259OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass
 george0papasotiriou/cve-2026-21015-php-filter-chain-arbitrary-file-read
PoC exploit for CVE-2026-21015 that abuses PHP filter chains to read arbitrary files through a vulnerable include() call, disclosing source and…
 george0papasotiriou/cve-2026-3333-dns-rebinding-to-steal-cloud-metadata
Python exploit for CVE-2026-3333 demonstrating DNS rebinding to access cloud metadata and steal IAM credentials through an SSRF-vulnerable web app.
 dshamany/privatesphare
An at-rest encrypted filesharing application with multiple clients who seek to share privately, without tracking.
 rasta-mouse/pwnlift
Easy peasy file uploads
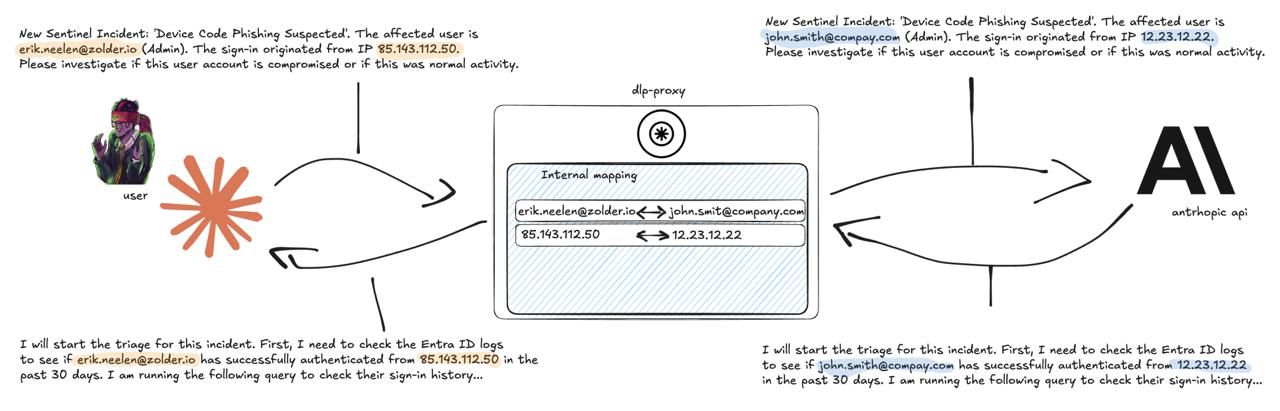 zolderio/token-proxy
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…
 bhanunamikaze/cve-2024-42009
This Proof of Concept (PoC) demonstrates an exploit for CVE-2024-42009, leveraging a cross-site scripting (XSS) vulnerability to extract emails from…
 kiprotect/kodex
A privacy and security engineering toolkit: Discover, understand, pseudonymize, anonymize, encrypt and securely share sensitive and personal data:…
 tadash10/exploiting-cve-2021-44228-log4shell-in-a-banking-environment
Objective: Demonstrate the exploitation of the Log4Shell vulnerability (CVE-2021-44228) within a simulated banking application environment.
 connectedlucy/plague
Default Detections for EDR
 kevthehermit/pastehunter
Scanning pastebin with yara rules
 incidedigital/mistica
An open source swiss army knife for arbitrary communication over application protocols
 jimywork/cromos
Cromos is a tool for downloading legitimate extensions of the Chrome Web Store and inject codes in the background of the application.
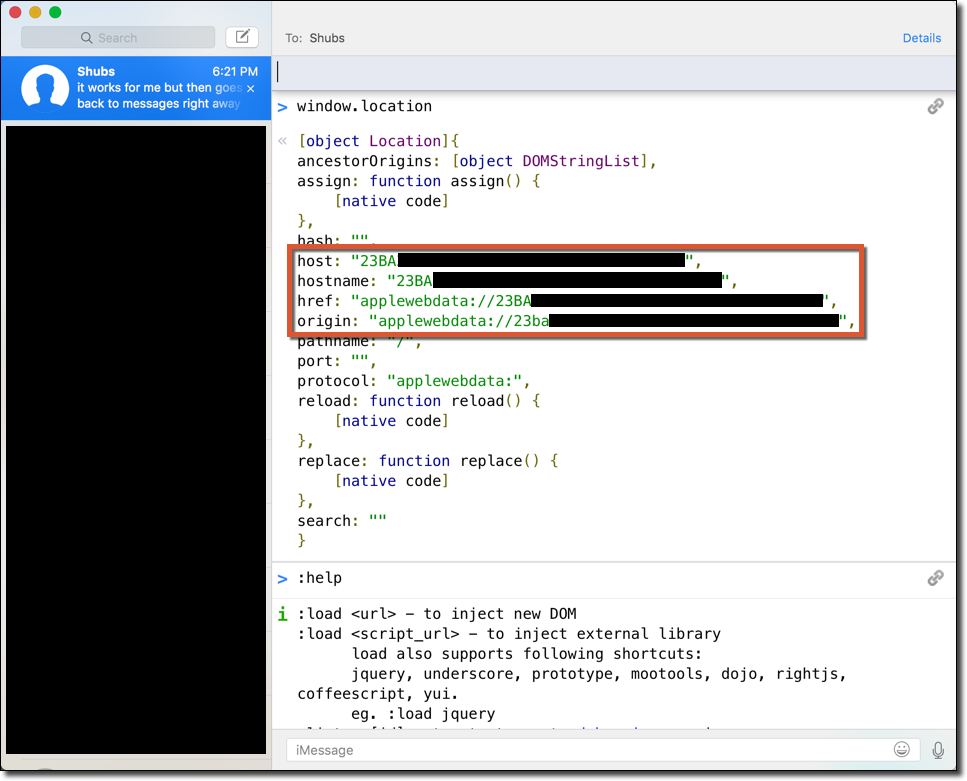 moloch--/cve-2016-1764
Extraction of iMessage Data via XSS
 s3bap3/pmp-exploit
Password Manager Pro Exploit