
CVE-2026-86259
 uziii2208/cve-2026-86259
OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass
api-securitycloud-securitydata-exfiltration+6
uziii2208/cve-2026-86259OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass
 legendile7/cve-2026-78122-poc
Proof-of-concept exploit for CVE-2026-78122, demonstrating container filesystem and environment variable exfiltration through docker-socket-proxy's…
 connectedlucy/plague
Default Detections for EDR
 george0papasotiriou/cve-2026-21004-sqlite-fts3-match-infoleak-via-query-crafting
Proof-of-concept exploit for CVE-2026-21004: uses crafted SQLite FTS3/4 MATCH prefix queries as a blind oracle to recover indexed secret data…
 george0papasotiriou/cve-2026-3333-dns-rebinding-to-steal-cloud-metadata
Python exploit for CVE-2026-3333 demonstrating DNS rebinding to access cloud metadata and steal IAM credentials through an SSRF-vulnerable web app.
 blue0x1/sqlwinds
SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit
 blacksnufkin/deadmanswitch
DeadManSwitch in rust with several triggers (remote local and network)
 designativedave/androrat
Remote Administration Tool for Android devices
 mwsrc/betterandrorat
Android Remote Access Trojan

 gradiant/faro
FARO - Document Sensitivity Detector
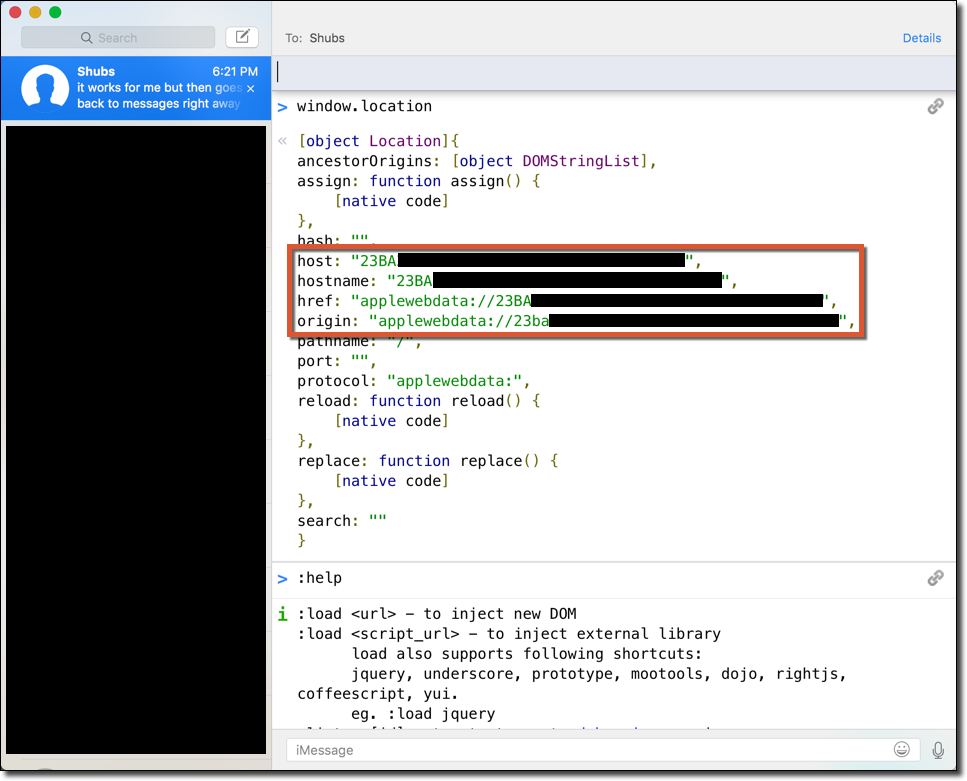 moloch--/cve-2016-1764
Extraction of iMessage Data via XSS
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 bande-a-bonnot/boucle-framework
Autonomous agent framework with structured memory, safety hooks, and loop management. Built by the agent that runs on it.
 fleralex/enseal
Secure, ephemeral secret sharing for developers.
 bhanunamikaze/cve-2024-42009
This Proof of Concept (PoC) demonstrates an exploit for CVE-2024-42009, leveraging a cross-site scripting (XSS) vulnerability to extract emails from…
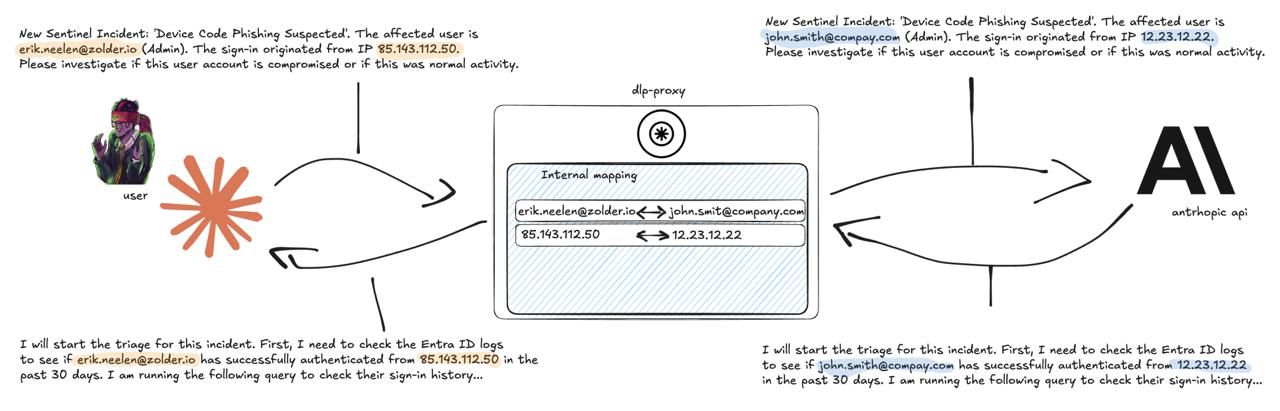 zolderio/token-proxy
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…
 dshamany/privatesphare
An at-rest encrypted filesharing application with multiple clients who seek to share privately, without tracking.