

XXERipper
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
api-security-testingdata-exfiltrationexploitation+9
kamalx06/xxeripperBlack-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 gagaltotal/cve-2026-85706-gitlab-poc
Go exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE Workhorse via URL-encoding bypass, with concurrent requests and…
 efeanilarslan/cve-2026-42167-exploit
Python exploit for CVE-2026-42167 (ProFTPD mod_sql). Features automated file scanning and timing-based blind data exfiltration.
 davidrxchester/cve-2026-7020
POC for CVE-2026-7720 - Ollama tensor digest path traversal
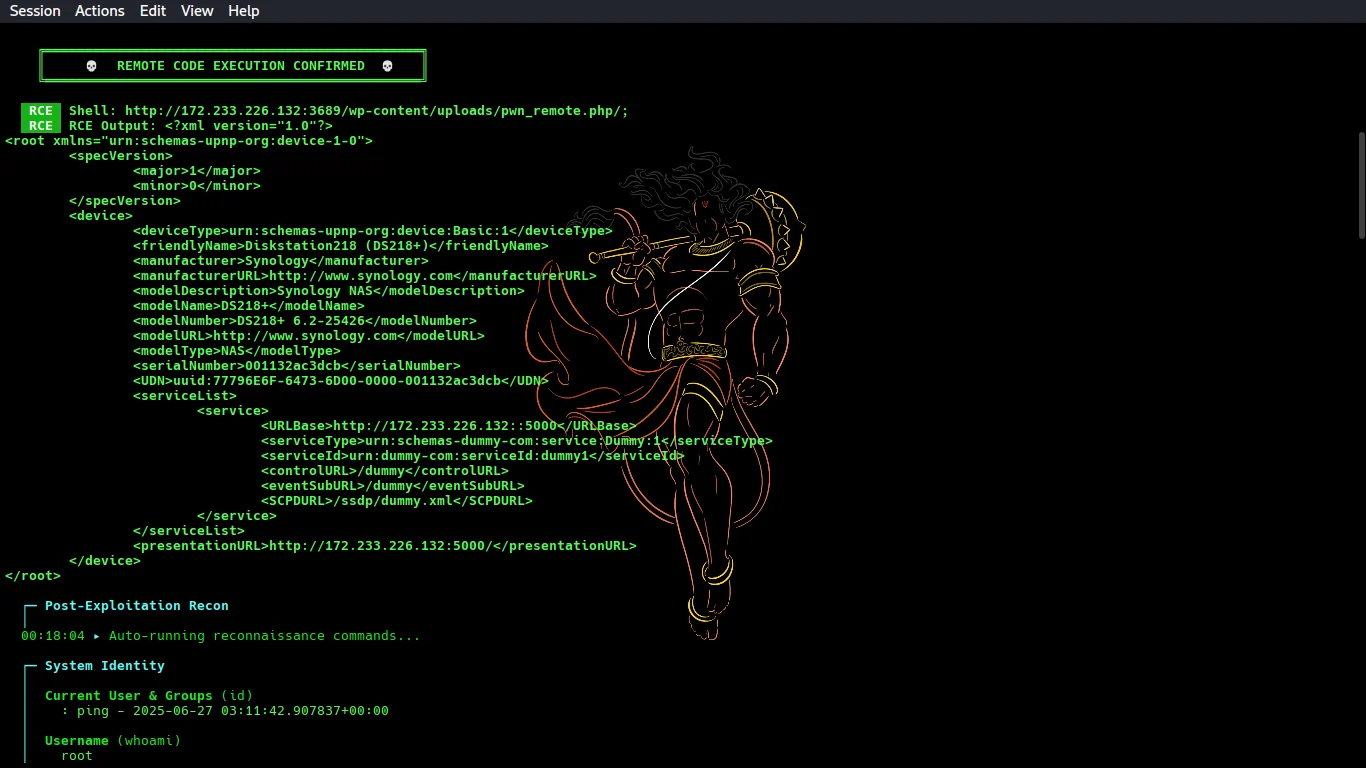 cybertechajju/cve-2026-1357-poc
Automated exploit tool for CVE-2026-1357, an unauthenticated RCE in WPvivid Backup & Migration. Scans WordPress targets, bypasses WAF/403, uploads a…
 azhariramadhan/cve-2026-39047
Printer exploitation framework for security testing via raw port 9100, featuring PCL payload delivery, DoS bombing, C2 QR codes, phishing QR codes,…
 acheong08/cve-2026-65400
Apple MacOS Screen Sharing Arbitrary File read/write -> RCE
 yarrick/iodine
Tunnel IPv4 data through DNS servers to bypass firewall restrictions and provide covert network access for penetration testing.
 daemoncibsec/flar3ad
POC of CVE-2026-51031 for arbitrary local file read
 ch4120n/cve-2026-15409
Proof-of-Concept exploit for CVE-2026-15409 (SonicWall SMA 1000 RCE) via Erlang distribution over WebSocket. Achieves unauthenticated remote code…
 toanln-cov/cve-2026-66493
The Joomla extension PhocaCommander is vulnerable to Path Traversal in delete, copy, move actions - CVSS 6.4
 invicti-security/web-inf-path-trav
Tool for helping in the exploitation of path traversal vulnerabilities in Java web applications
 moniik/poc_salesforce_lightning
Academic purposes only. Attack against Salesforce lightning with guest privilege.
 absholi7ly/apache-ofbiz-directory-traversal-exploit
Exploit for Apache OFBiz CVE-2024-32113 path traversal via crafted XML-RPC requests, enabling arbitrary file read and potential command execution on…
 sunynov/cve-2026-39363
方便实用的CVE-2026-39363利用工具
 shinthink/cve-2026-60004
CVE-2026-60004 — Gitea/Forgejo Diffpatch Git Hook RCE. Bare clone → post-index-change hook injection. CVSS 9.8 | CWE-94 | Gitea < 1.27.1
 pentestpartners/ptp-rat
Exfiltrate data over screen interfaces