

CVE-2026-74251
 toanln-cov/cve-2026-74251
Unauthenticated SQL Injection via Attribute Filter in Phoca Cart - CVSS 9.3
database-securitydata-exfiltrationexploitation+3
toanln-cov/cve-2026-74251Unauthenticated SQL Injection via Attribute Filter in Phoca Cart - CVSS 9.3
 nxploited/cve-2024-7135
Proof-of-concept exploit for authenticated arbitrary file read via directory traversal in WordPress Tainacan plugin (CVE-2024-7135).
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node
 ioncodes/cve-2020-16938
Bypassing NTFS permissions to read any files as unprivileged user.
 udyz/cve-2025-53770-exploit
Exploit for CVE-2025-53770, a SharePoint ViewState deserialization vulnerability, enabling remote code execution via crafted payloads.
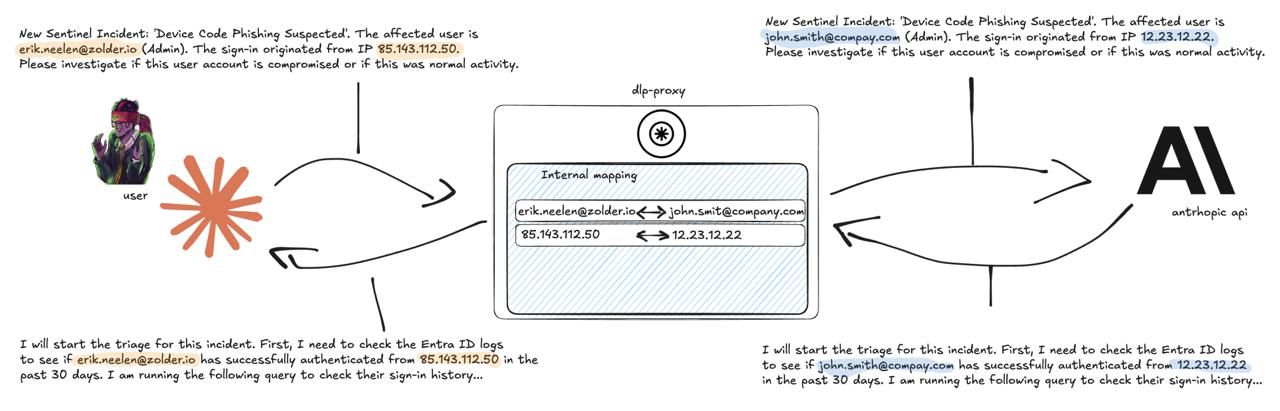 zolderio/token-proxy
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.
 mthbernardes/leakmanager
A tool to help you manage your leaks
 magic-wormhole/magic-wormhole
get things from one computer to another, safely
 limerboy/adamantium-thief
:key: (THIS CODE IS OUTDATED FOR NEW CHROME VERSIONS) Decrypt chromium based browsers passwords, cookies, credit cards, history, bookmarks, autofill.…
 aydinnyunus/keylogger
Get Keyboard,Mouse,ScreenShot,Microphone Inputs from Target Computer and Send to your Mail.
 aydinnyunus/wifipassword-stealer
Get All Registered Wifi Passwords from Target Computer.
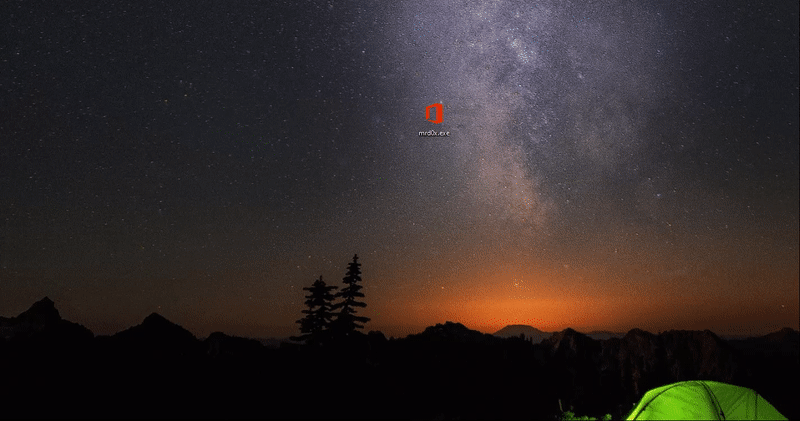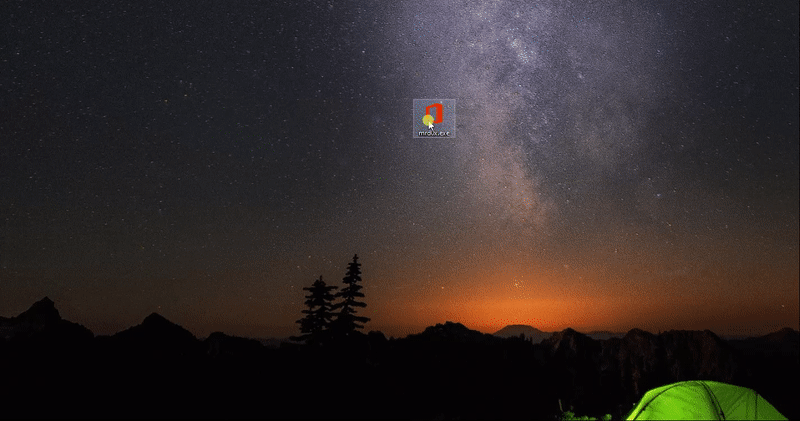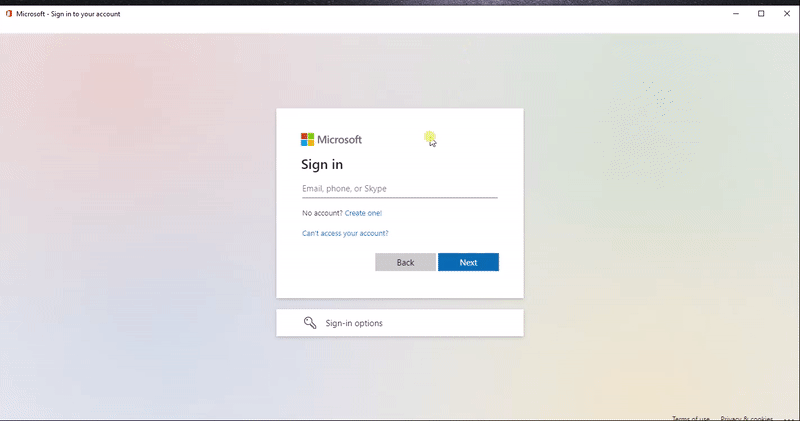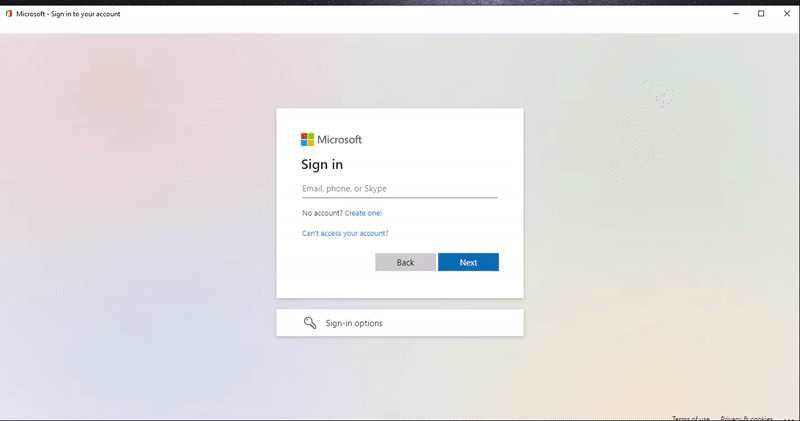 mrd0x/webview2-cookie-stealer
Injects JavaScript keylogger into WebView2 pages to capture keystrokes and exfiltrate cookies from Microsoft authentication sessions via HTTP GET…
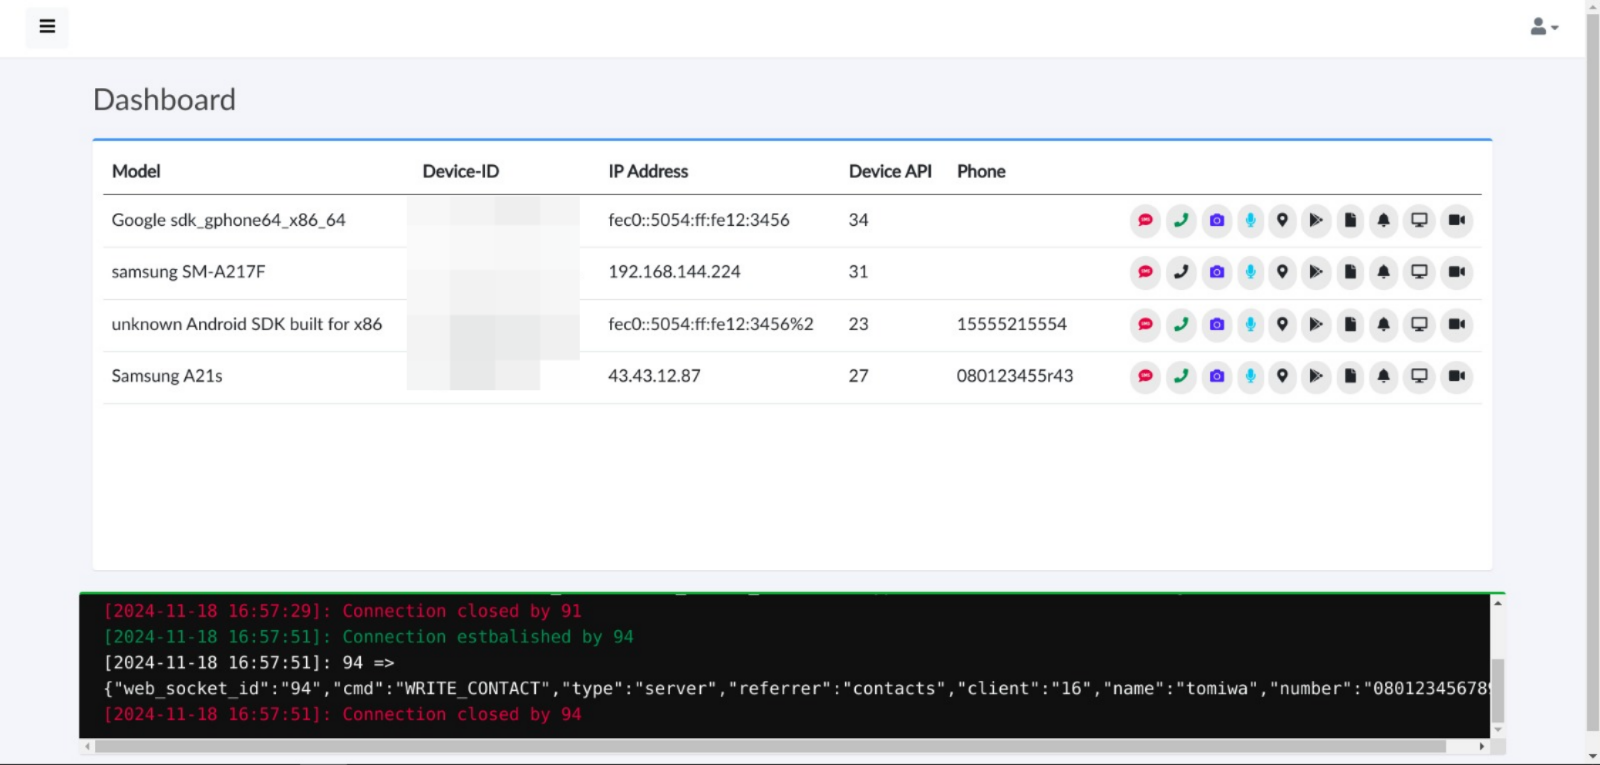 tomiwa-ot/moukthar
Android remote administration tool